
Consensus-OSINT
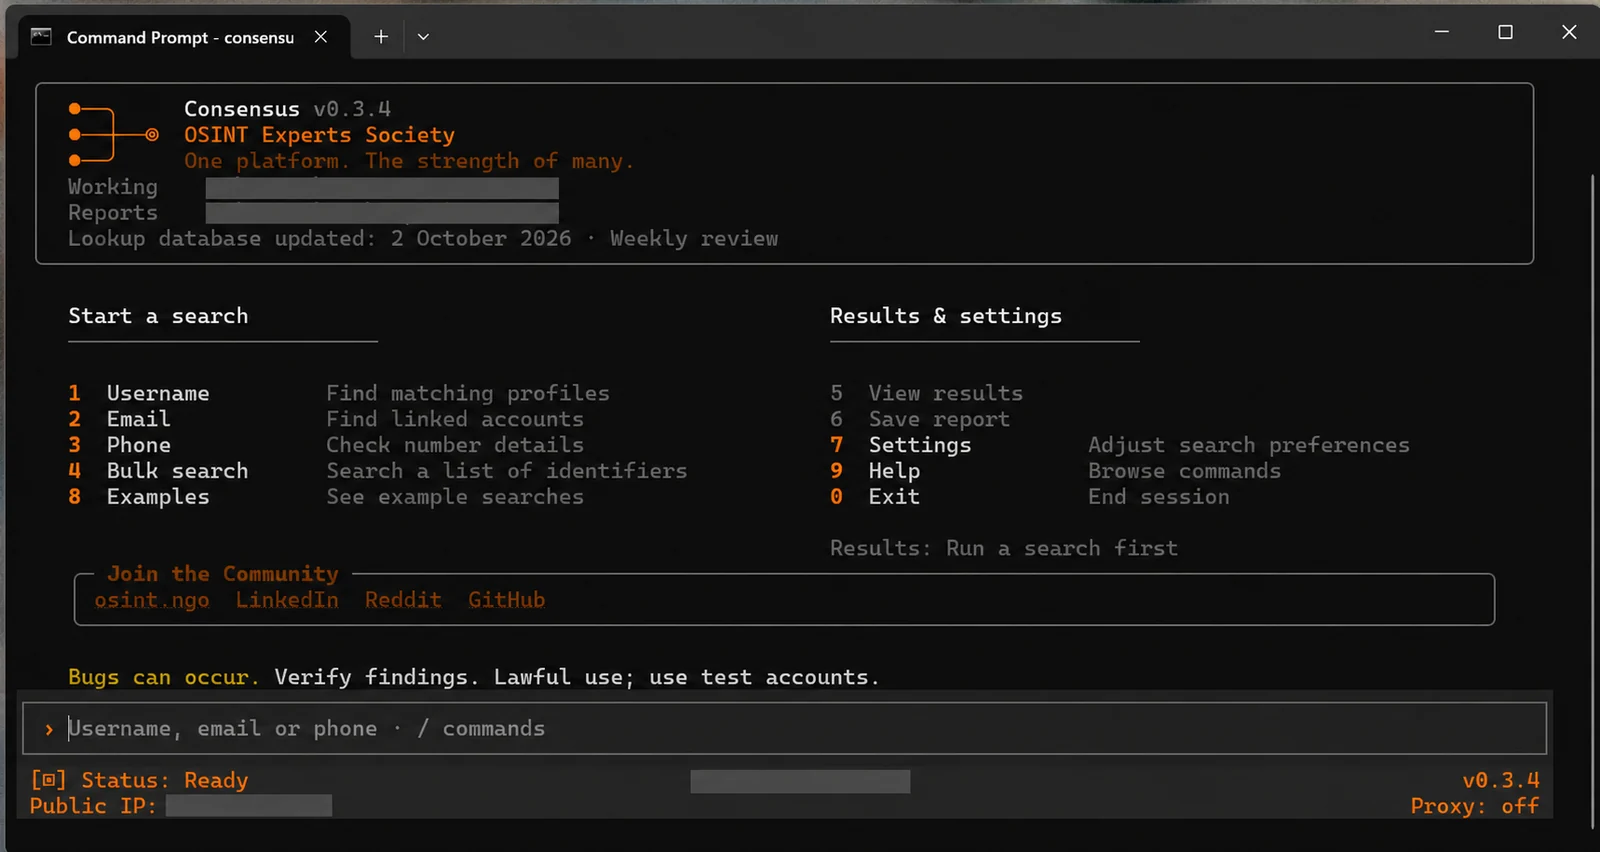
🔎 Username, email & phone OSINT — 9,700+ lookup checks from 19 projects, with profile enrichment, bulk searches, evidence graphs and expert-reviewed…

🔎 Username, email & phone OSINT — 9,700+ lookup checks from 19 projects, with profile enrichment, bulk searches, evidence graphs and expert-reviewed…

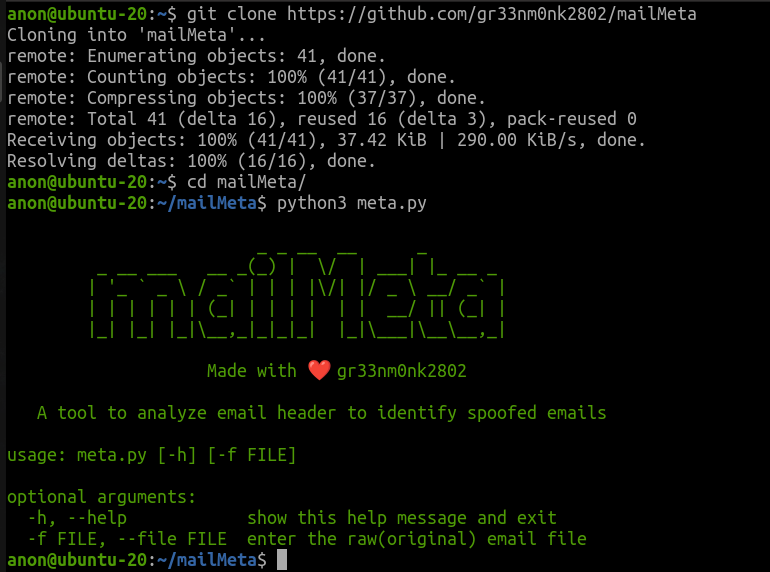
An forensics tool to help aid in the investigation of spoofed emails based off the email headers.

Open-source security monitoring platform for threat hunting, intrusion detection, log management, incident response, and endpoint visibility with…

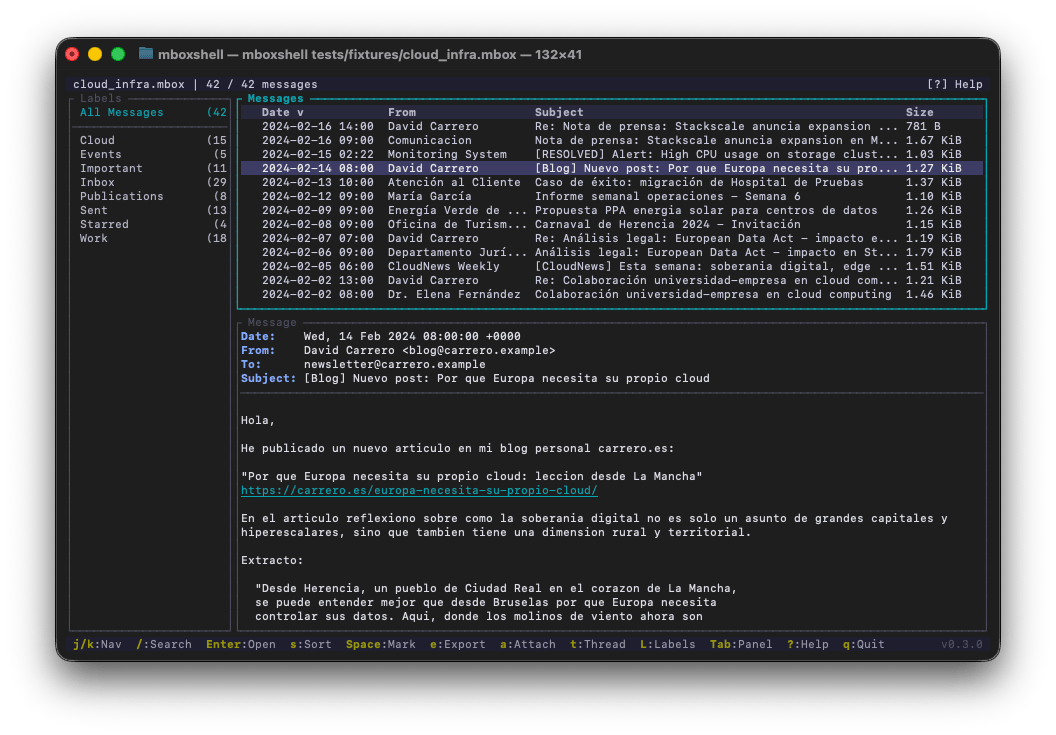
mboxShell. Fast terminal viewer for MBOX files of any size. Open, search and export emails from Gmail Takeout backups (50GB+) without loading them…

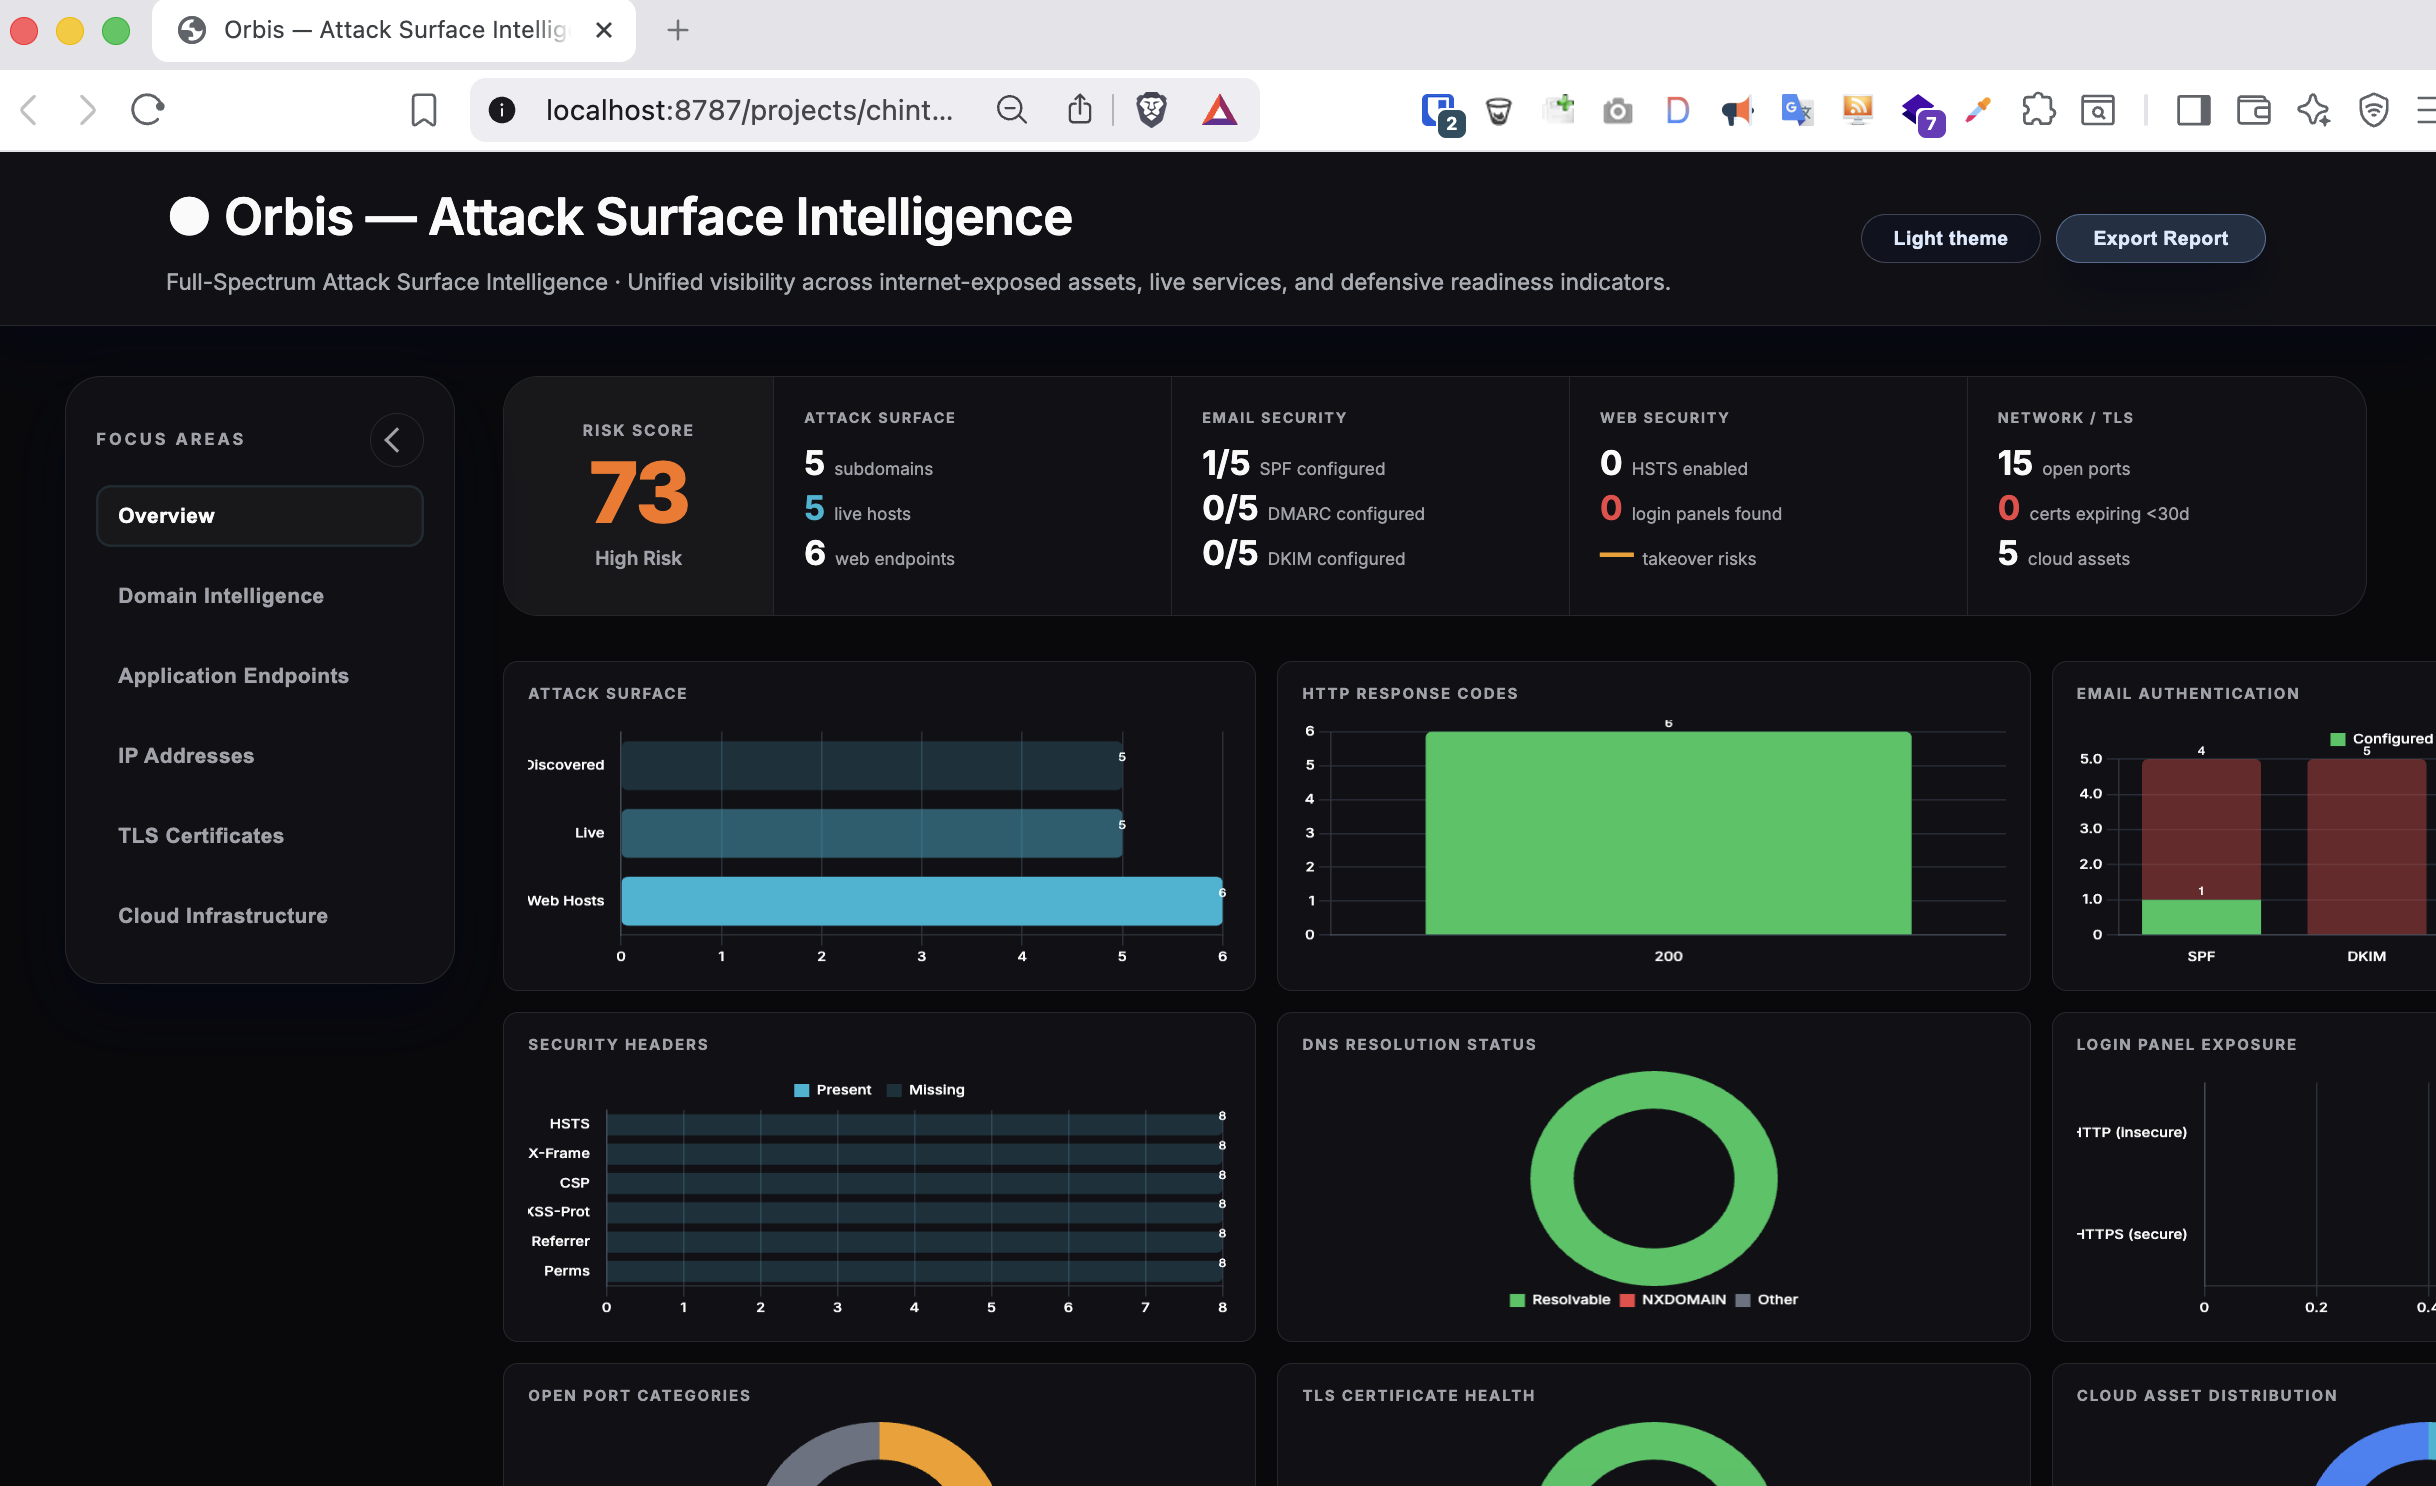
Orbis is an full spectrum automated external attack surface intelligent toolkit.

Real-time cloud-native runtime security agent for Linux that monitors syscalls and container/Kubernetes metadata to detect anomalous behavior and…

Shell-based vulnerability scanner for CVE-2026-45185 (Dead.Letter) in Exim MTA. Detects use-after-free in GnuTLS builds, checks version, TLS library,…

Most Powerful Send Fake Mail Using Any Mail I'd undetectable

Instructions for installing a vulnerable version of Exim and its expluatation

A temporary email right from your terminal written in POSIX sh

SQL powered operating system instrumentation, monitoring, and analytics.

Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…

Spam filtering and email processing framework with regex rules, statistical analysis, custom Lua plugins, and external blocklists for MTA integration.

A tool to abuse Exchange services

Deploy a phishing infrastructure on the fly.

Identify public-facing Microsoft Exchange servers and determine their software versions

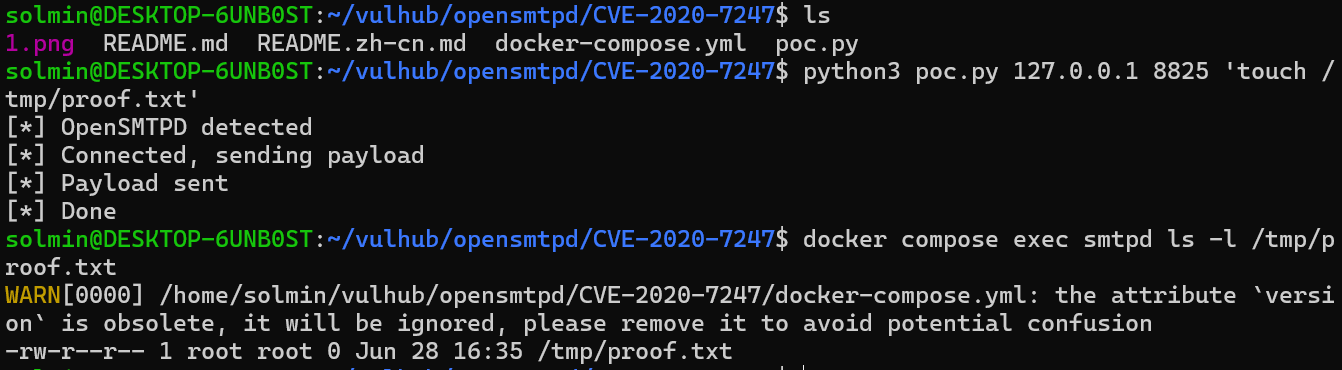
Docker-based lab demonstrating CVE-2020-7247 remote code execution in OpenSMTPD 6.6.1p1 with a Python PoC for educational security testing.

Um estudo de caso do CVE-2024-21413. Usado como parâmetro a sala do TryHackMe Moniker Link (CVE-2024-21413). Feito edições com claude code no exploit.