
CVE-2026-73570
 hainhc/cve-2026-73570
Proof-of-concept exploit for CVE-2026-73570, an unauthenticated OS command injection in Zimbra Collaboration Suite via zimbra-snmp log injection,…
email-securityexploitationincident-response+3
hainhc/cve-2026-73570Proof-of-concept exploit for CVE-2026-73570, an unauthenticated OS command injection in Zimbra Collaboration Suite via zimbra-snmp log injection,…
 thoropass-public/area51
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 fathanahhidayati/https-github.com-xaitax-cve-2024-21413-microsoft-outlook-remote-code-execution-vulnerability
Proof-of-concept exploit for CVE-2024-21413, a Microsoft Outlook remote code execution vulnerability. Demonstrates NTLM credential leakage and RCE…
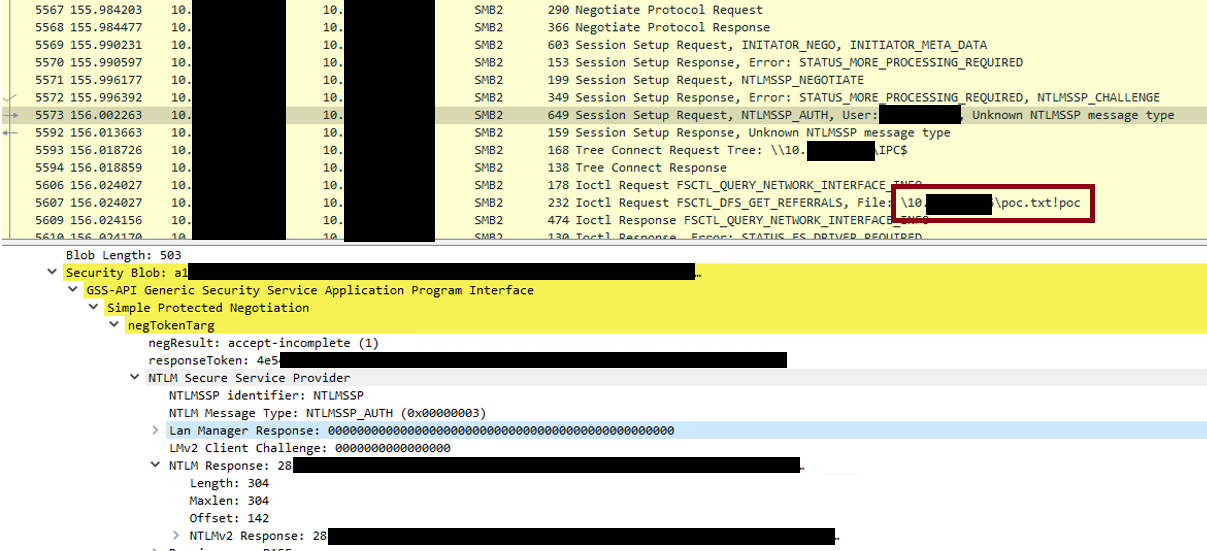 xaitax/cve-2024-21413-microsoft-outlook-remote-code-execution-vulnerability
Microsoft-Outlook-Remote-Code-Execution-Vulnerability
 jishino567/cve-2026-73570
Python PoC for CVE-2026-73570, an SMTP command injection in Zimbra. Sends malformed RCPT TO payloads to trigger shell command execution via…
 danithehack3r/cve-2024-42009-poc
CVE-2024-42009 Proof of Concept
 srvaccount/cve-2021-26855-poc
PoC exploit code for CVE-2021-26855
 mr-xn/cve-2021-26855-d
Python tool to exploit CVE-2021-26855 (ProxyLogon) for downloading Exchange mailbox emails via EWS, supporting user enumeration and bulk target…
 bailongwang1/cve-2020-0688
PHP CLI script that scans single hosts or IP ranges to detect Exchange servers vulnerable to CVE-2020-0688 by checking installed cumulative updates.
 hevnsnt/cvengine
AI-first external attack surface assessment with continuous discovery, evidence-based vulnerability validation, and developer-agent MCP integration.
 d0rb/cve-2024-21378
This repository contains an exploit for targeting Microsoft Outlook through Exchange Online, leveraging a vulnerability to execute arbitrary code via…
 wyatu/cve-2018-8581
CVE-2018-8581 | Microsoft Exchange Server Elevation of Privilege Vulnerability
 abraxas/cakephp-smtp-crlf
CakePHP 5.4.2 - High - Remote - Header injection - SmtpTransport lone LF leftover of GHSA-2qh5
 romain-deperne/cve-2026-34975
Proof-of-concept and technical analysis of CRLF email header injection in Plunk's raw MIME construction, demonstrating Bcc injection and other…
 millad7/sogo_web_mail-vulnerability-cve-2025-50340
Insecure Direct Object Reference (IDOR vulnerability) in SOGo Webmail Allows a user to send emails on behalf of another user.
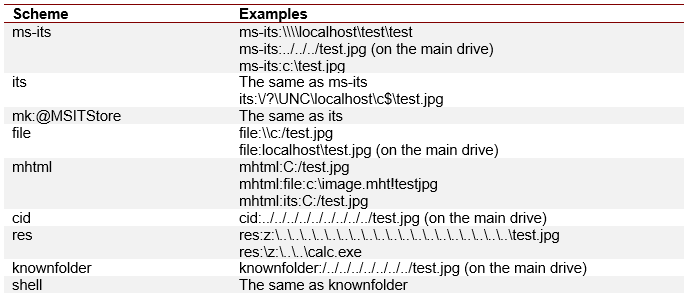 nccgroup/outlookleaktest
The Outlook HTML Leak Test Project
 natasaka/cve-2025-30349
Horde IMP (through 6.2.27) vulnerability – obfuscation via HTML encoding – XSS payload
 0neb1n/cve-2020-16947
Proof-of-concept exploit for CVE-2020-16947, a Microsoft Outlook RCE triggered by malformed HTML content leading to a heap buffer overflow and remote…