
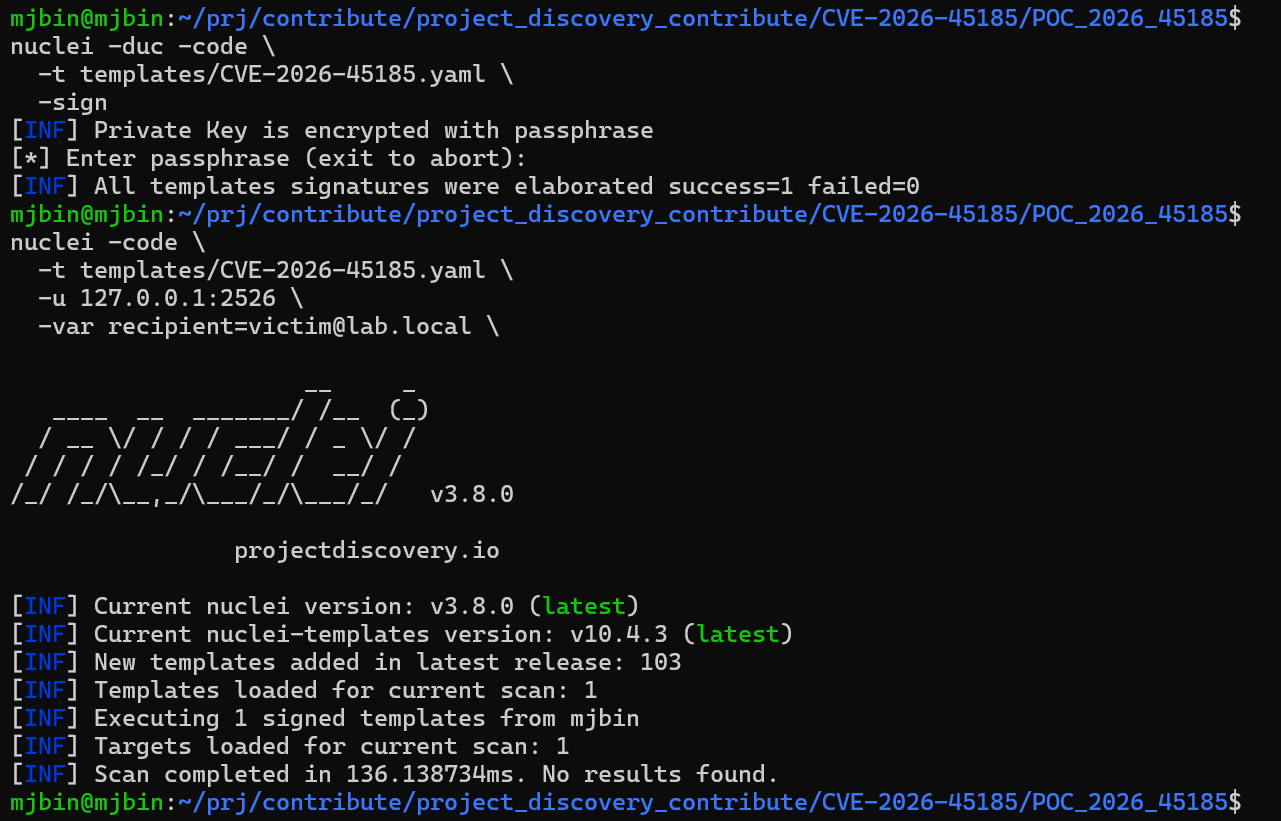
POC_CVE-2026-45185
 mj-bin/poc_cve-2026-45185
POC_CVE-2026-45185 for nuclei-templates
educationemail-securityexploitation+3
mj-bin/poc_cve-2026-45185POC_CVE-2026-45185 for nuclei-templates
 viniciusfariasdev/cve-2024-21413-outlook-monikerlink-lab
Educational lab and PoC demonstrating CVE-2024-21413 Outlook Moniker Link attack to leak netNTLMv2 hashes via crafted HTML email.
 mqkgithub/moniker-link-cve-2024-21413
Step-by-step walkthrough of exploiting CVE-2024-21413 in Microsoft Outlook to bypass Protected View and leak NTLM credentials via Moniker Links,…
 duy-31/cve-2024-21413
Microsoft Outlook Information Disclosure Vulnerability (leak password hash) - Expect Script POC
 darsigovrustam/cve-2019-10149
Instructions for installing a vulnerable version of Exim and its expluatation
 ahmetkarakayaoffical/cve-2024-21413-microsoft-outlook-remote-code-execution-vulnerability
Bu betik, Microsoft Outlook'ta keşfedilen ve CVSS değeri 9.8 olan önemli bir güvenlik açığı olan CVE-2024-21413 için bir kavram kanıtı (PoC)…
 alicangnll/cve-2023-23397
CVE-2023-23397 - Microsoft Outlook Vulnerability
 0xblackash/cve-2026-73570
Advisory and detection guidance for CVE-2026-73570, an unauthenticated OS command injection in Zimbra SNMP notification processing leading to remote…
 h1ssbl1tz/blind-trust-cve-2024-21413-research
A security research tool for simulating targeted phishing campaigns using CVE-2024-21413 (Moniker Link).
 abc1230940/soc336-windows-ole-zero-click-rce-exploitation-detected-cve-2025-21298
SOC336 - Windows OLE Zero-Click RCE Exploitation Detected (CVE-2025-21298) Walkthrough
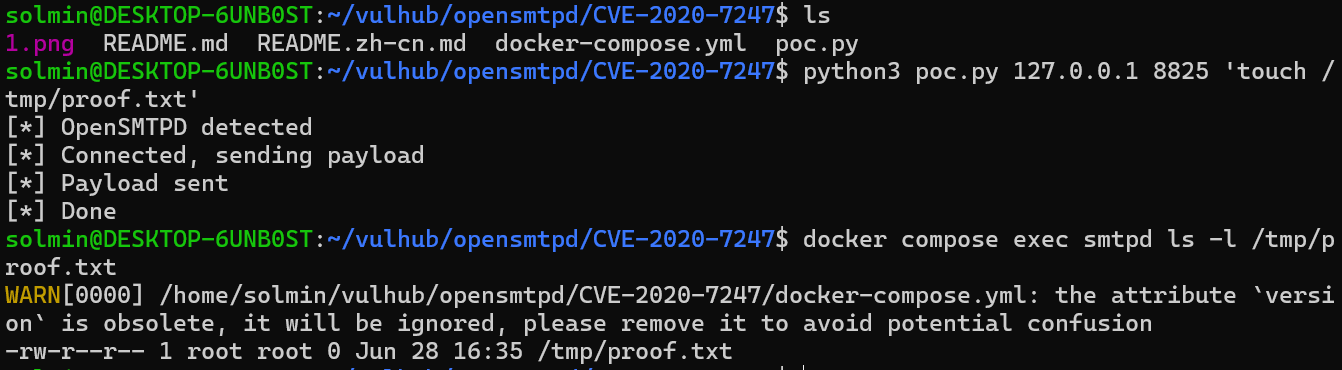 solmin111/opensmtpd-cve-2020-7247-
Docker-based lab demonstrating CVE-2020-7247 remote code execution in OpenSMTPD 6.6.1p1 with a Python PoC for educational security testing.
 eylommaayan/thm---cve-2024-21413-moniker-link-microsoft-outlook-
ב־13 בפברואר 2024 פרסמה Microsoft חולשת אבטחה חמורה ב־Microsoft Outlook, אשר קיבלה את הזיהוי CVE-2024-21413, ומוכרת בשם Moniker Link Vulnerability. …
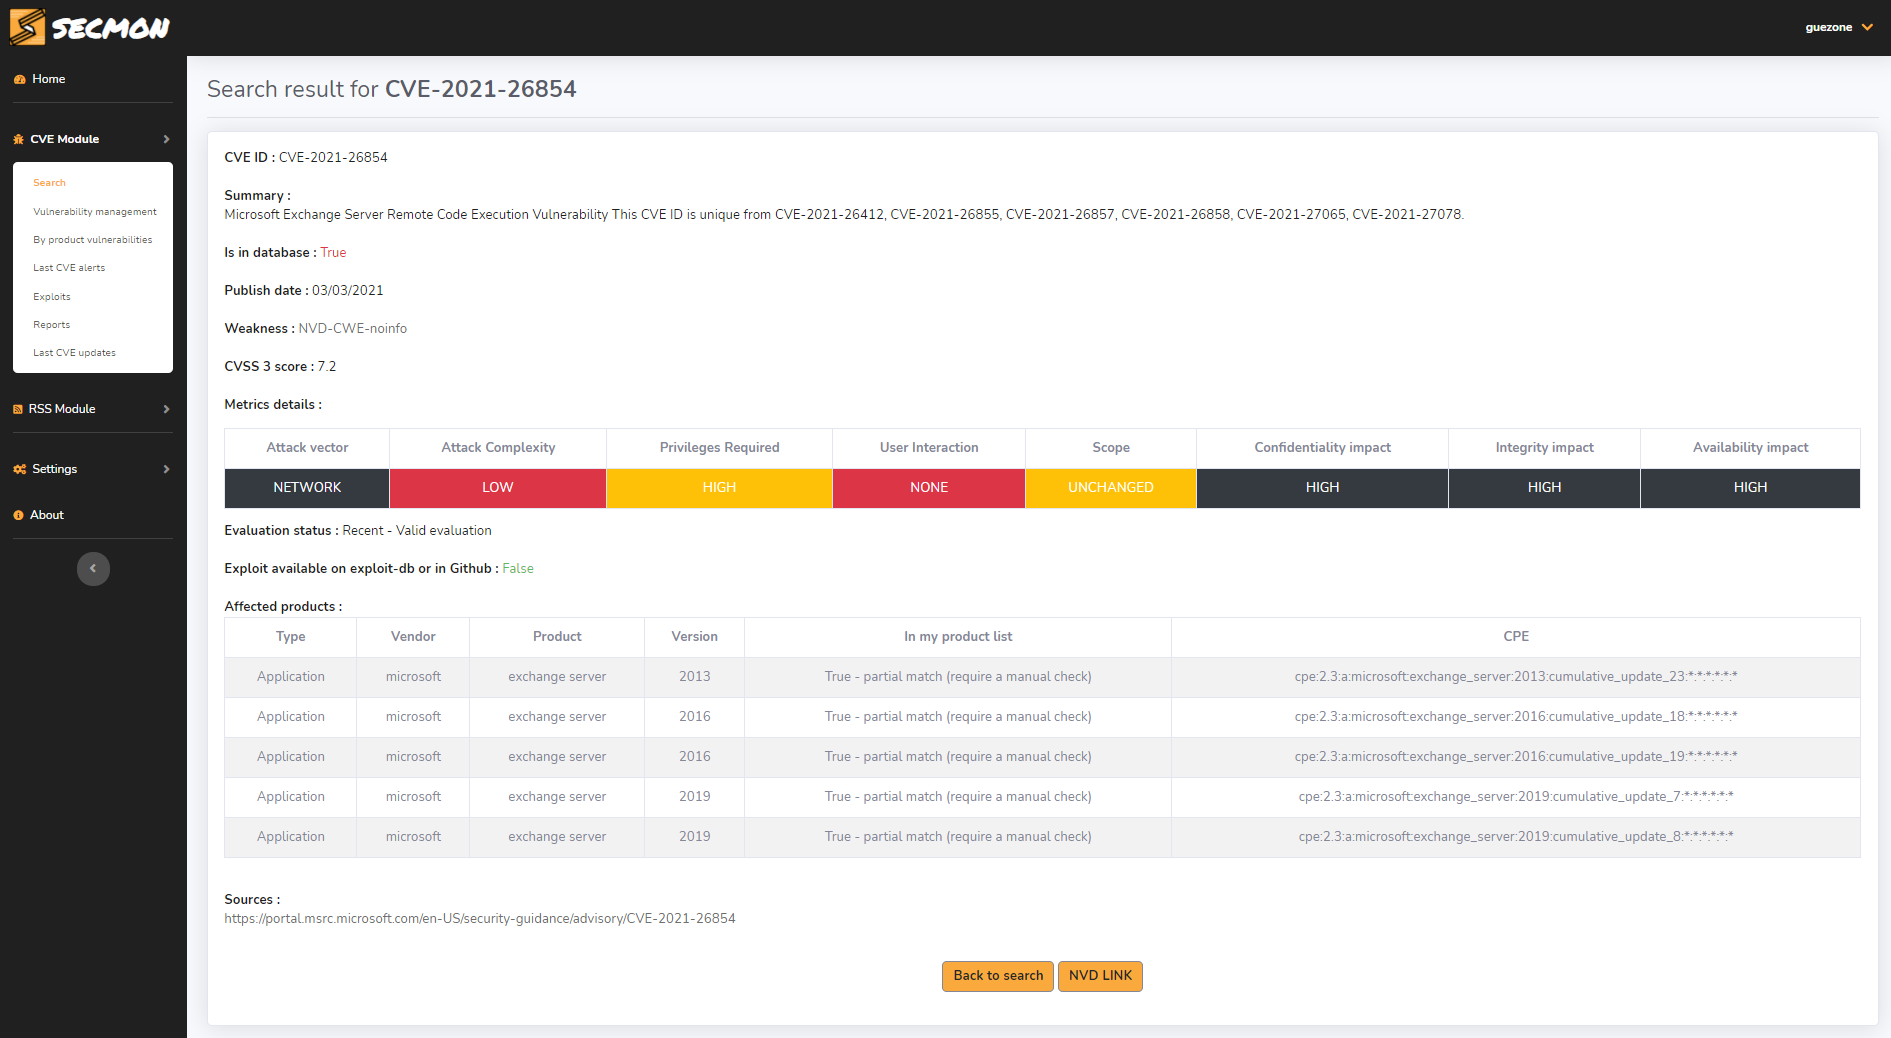 alb-uss/secmon
SECMON is a web-based tool for the automation of infosec watching and vulnerability management with a web interface.
 quickbreach/exchangerelayx
An NTLM relay tool to the EWS endpoint for on-premise exchange servers. Provides an OWA for hackers.
 trackflaw/cve-2023-23397
Simple PoC of the CVE-2023-23397 vulnerability with the payload sent by email.
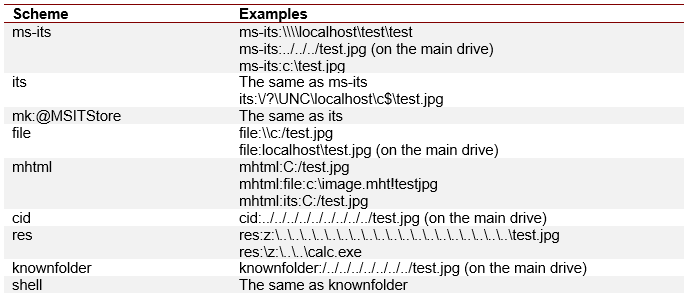 nccgroup/outlookleaktest
The Outlook HTML Leak Test Project
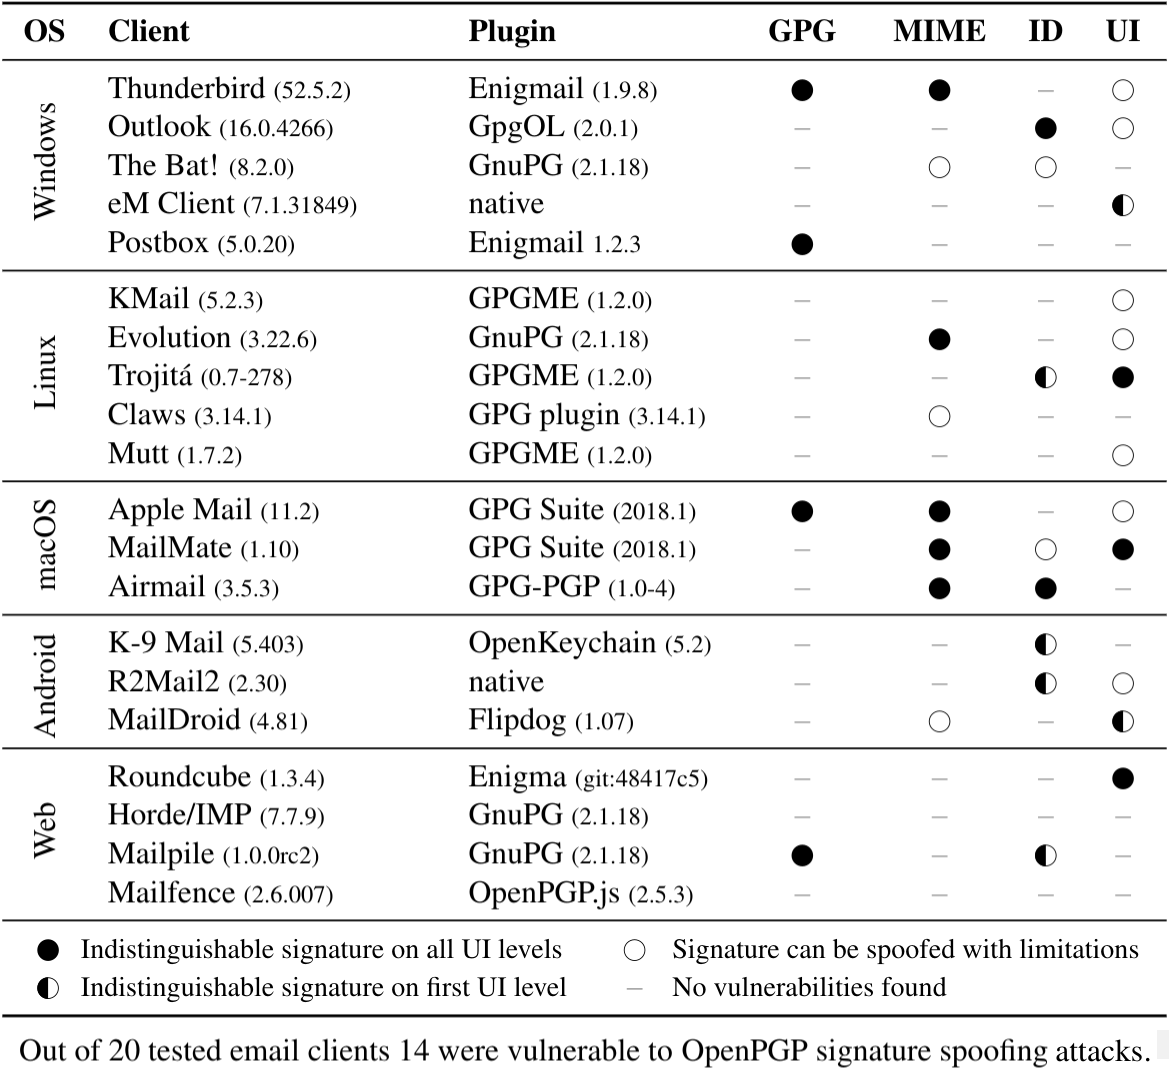 rub-nds/johnny-you-are-fired
Artifacts for the USENIX publication.
 grn-bogo/cve-2023-23397
Python script to create a message with the vulenrability properties set