
tryhackme-moniker-link
 yfelipecruvinel/tryhackme-moniker-link
Documentation of my hands-on lab Moniker Link (CVE-2024-21413) completed on TryHackMe.
educationemail-securityexploitation+3
yfelipecruvinel/tryhackme-moniker-linkDocumentation of my hands-on lab Moniker Link (CVE-2024-21413) completed on TryHackMe.
 p4x1s/cve-2023-23397-poc
CVE-2023-23397漏洞的简单PoC,有效载荷通过电子邮件发送。
 natasaka/cve-2025-30349
Horde IMP (through 6.2.27) vulnerability – obfuscation via HTML encoding – XSS payload
 theunknownsoul/cve-2023-23397-pow
Proof of Work of CVE-2023-23397 for vulnerable Microsoft Outlook client application.
 abc1230940/soc336-windows-ole-zero-click-rce-exploitation-detected-cve-2025-21298
SOC336 - Windows OLE Zero-Click RCE Exploitation Detected (CVE-2025-21298) Walkthrough
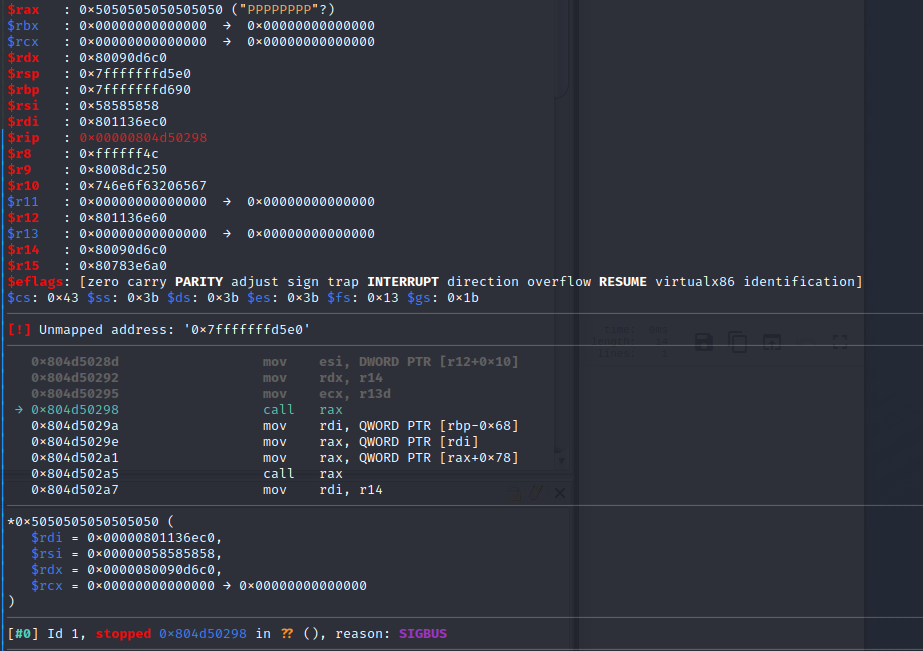 ly1g3/cisco-cve-2023-31488
Cisco Email Security Appliance: Email to zero-click RCE as root - Remote Code Execution/Memory Corruption/ROP-chain
 c-g-creator/letsdefend-soc336-windows-ole-zero-click-rce-exploitation-detected-cve-2025-21298
LetsDefend SOC336 case study on CVE-2025-21298
 derrickschoen/laravel-framework
Fork of laravel/framework 10.50.2 with CVE-2026-48019 (CRLF injection in default email rule) backported into ValidatesAttributes::validateEmail.…
 0xblackash/cve-2026-28289
CVE-2026-28289
 phaedrik/cve-2023-23397-poc
Two POCs I created for the CVE-2023-23397 Outlook NTLM vulnerability, to be used internally.
 networksecure/cve-2020-14066
Proof-of-concept exploit for CVE-2020-14066 targeting insecure permissions in Icewarp Email Server 12.3.0.1, enabling privilege escalation or…
 j0eyv/cve-2023-23397
Proof-of-concept exploit for CVE-2023-23397, an Outlook/Exchange privilege escalation vulnerability that triggers NTLM credential theft via a…
 eylommaayan/thm---cve-2024-21413-moniker-link-microsoft-outlook-
ב־13 בפברואר 2024 פרסמה Microsoft חולשת אבטחה חמורה ב־Microsoft Outlook, אשר קיבלה את הזיהוי CVE-2024-21413, ומוכרת בשם Moniker Link Vulnerability. …
 saykino/cve-2025-54320
Proof-of-concept for CVE-2025-54320: an email bombing vulnerability in Ascertia SigningHub's Invite User API due to missing rate limiting, allowing…
 saykino/cve-2026-31283
Documentation of CVE-2026-31283: an email bombing vulnerability in Totara LMS's forgot password API due to missing rate limiting, allowing…
 materaj2/cve-2026-45185-detection-script
These detection scripts are property of the SECPlayground Platform. Two safe detection scripts. Neither drives the close_notify-mid-BDAT trigger, so…
 millad7/sogo_web_mail-vulnerability-cve-2025-50340
Insecure Direct Object Reference (IDOR vulnerability) in SOGo Webmail Allows a user to send emails on behalf of another user.
 ozzi-/zimbra-cve-2017-8802-hotifx
Security hotfix for CVE-2017-8802