
CVEngine
 hevnsnt/cvengine
AI-first external attack surface assessment with continuous discovery, evidence-based vulnerability validation, and developer-agent MCP integration.
ai-securityemail-securityinformation-gathering+8
567
hevnsnt/cvengineAI-first external attack surface assessment with continuous discovery, evidence-based vulnerability validation, and developer-agent MCP integration.
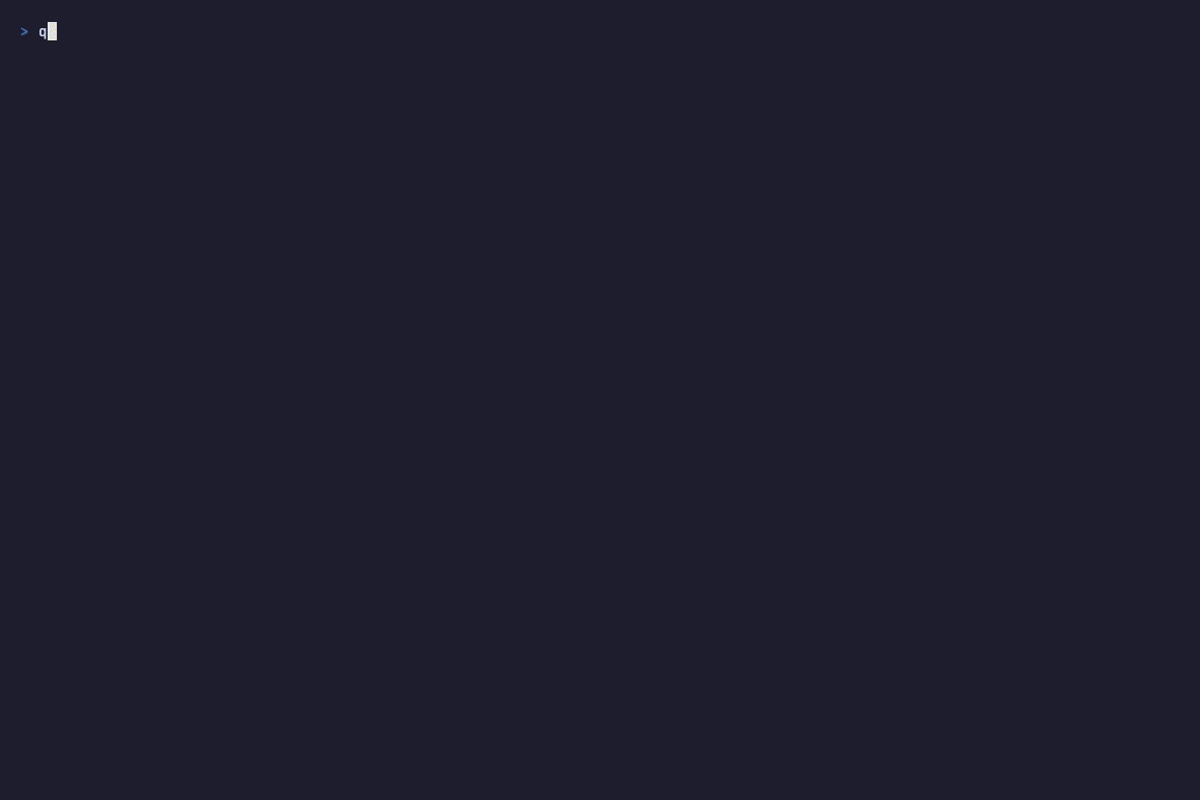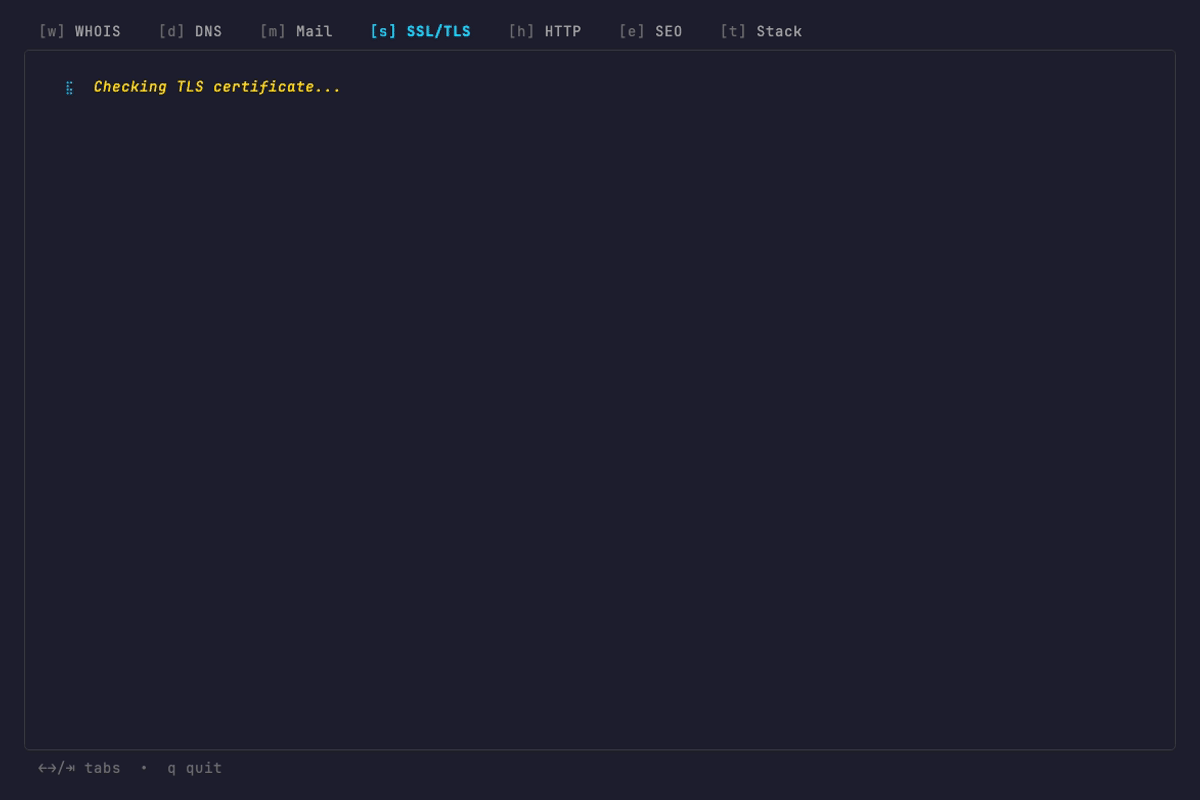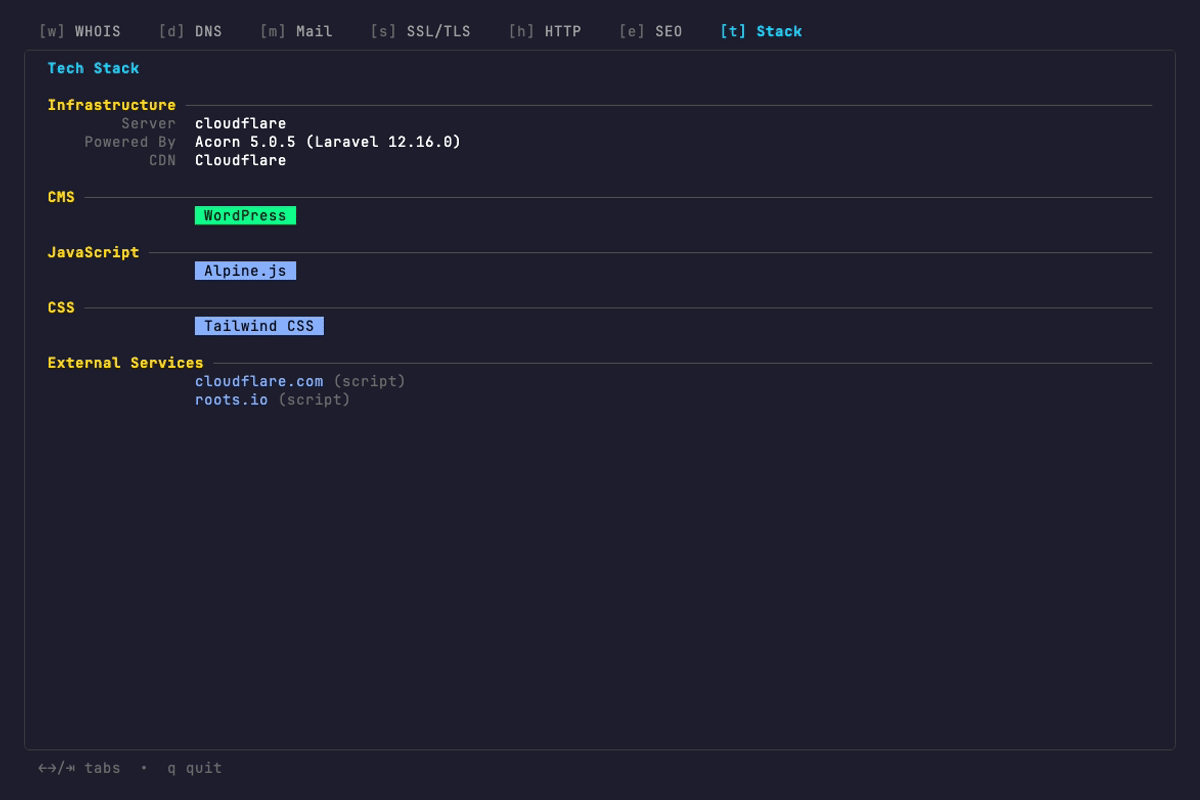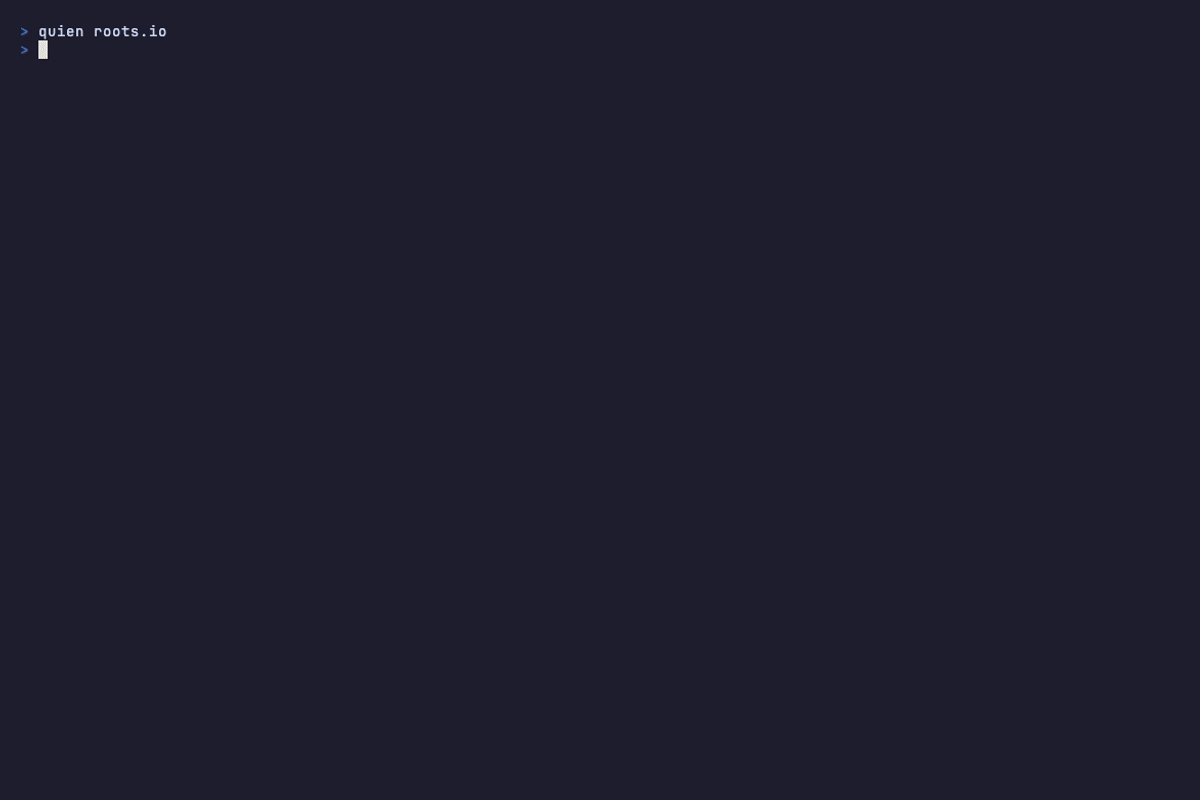 retlehs/quien
A better whois and domain intelligence toolkit
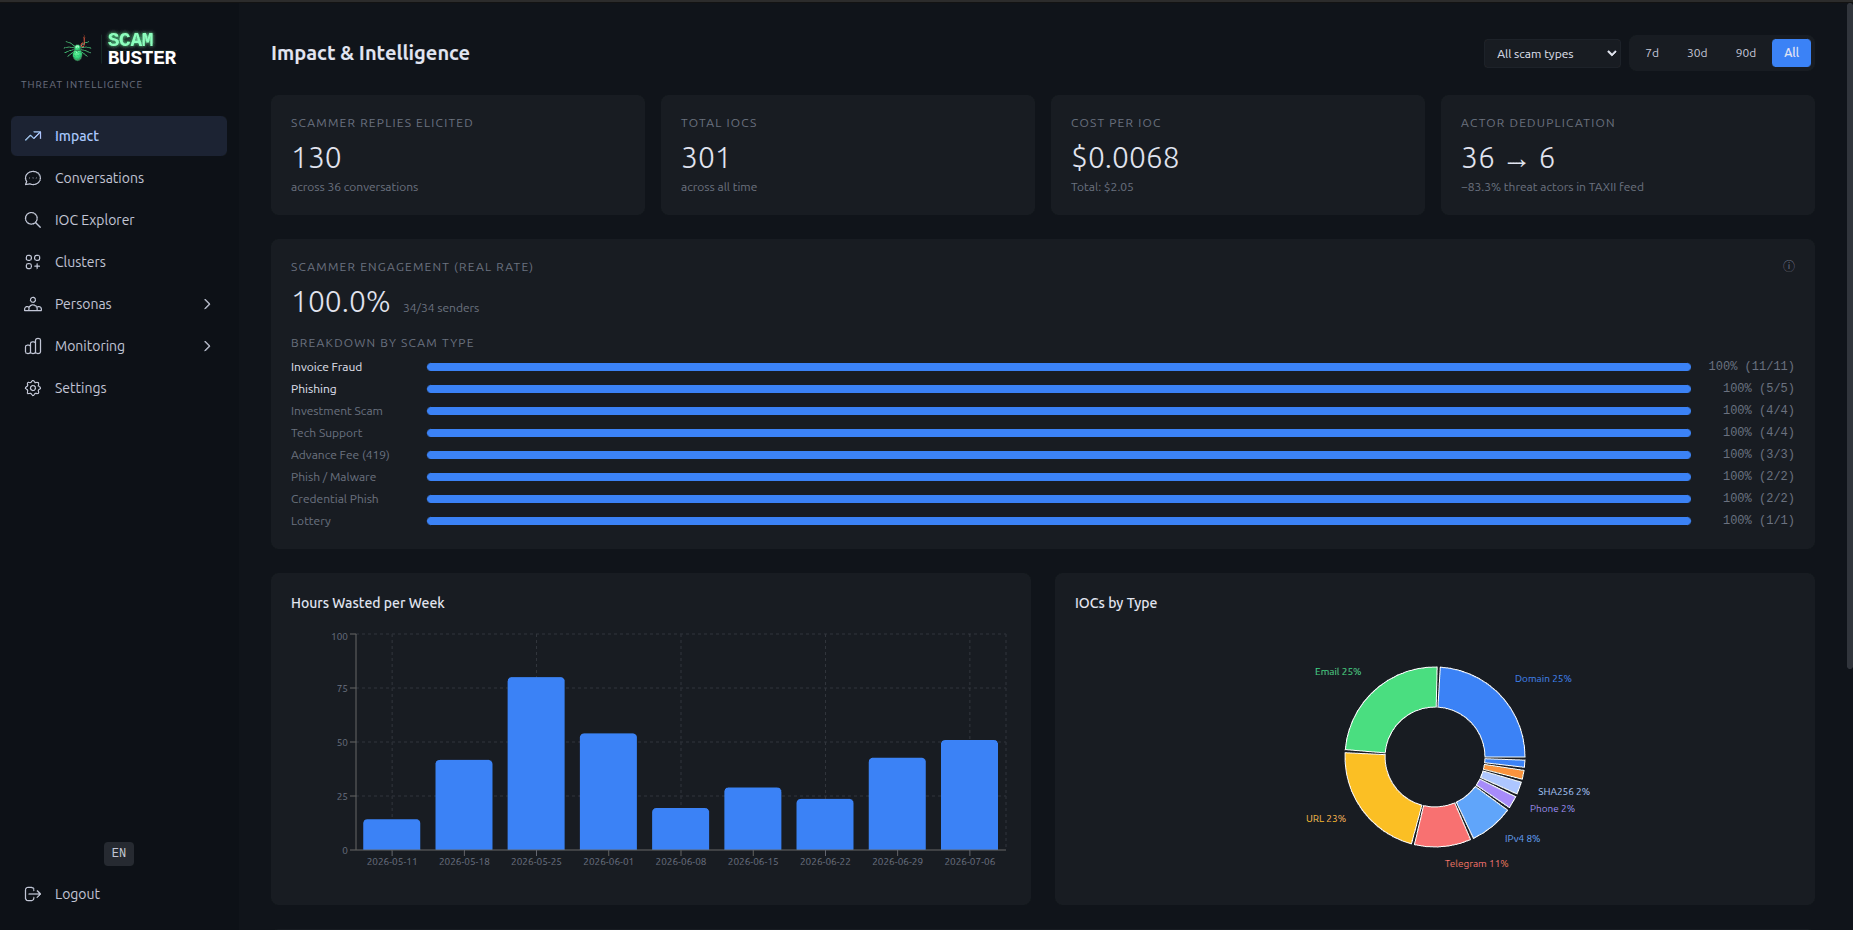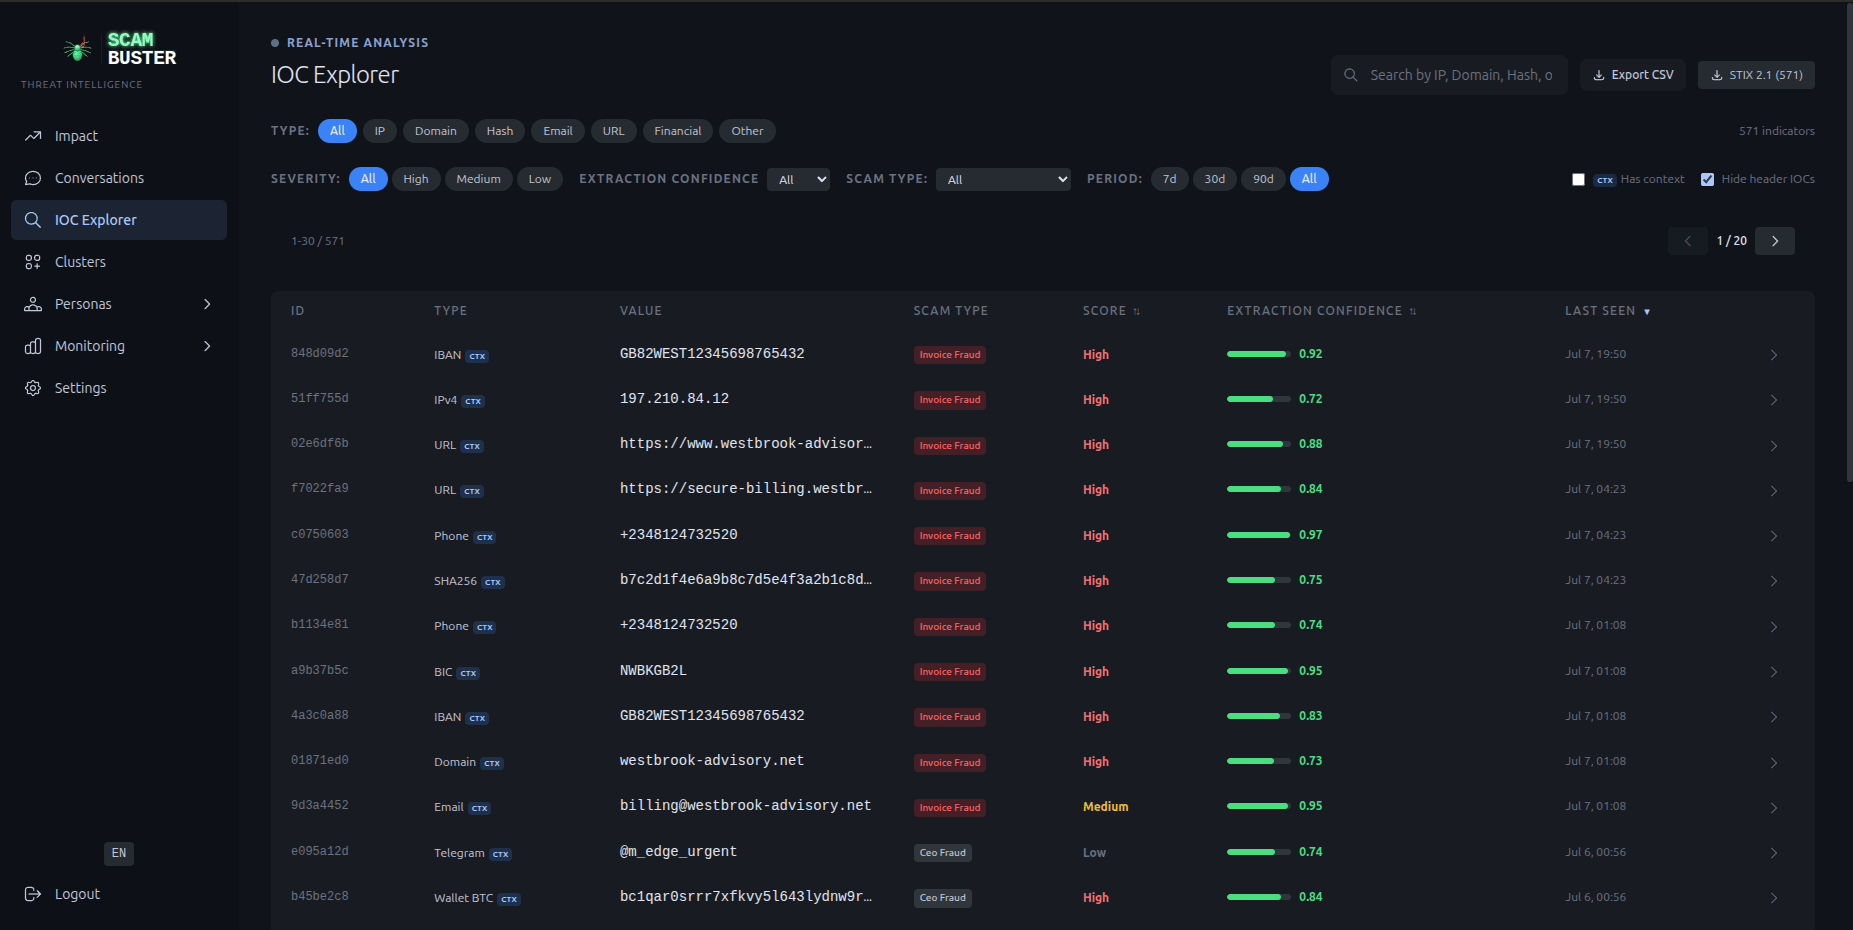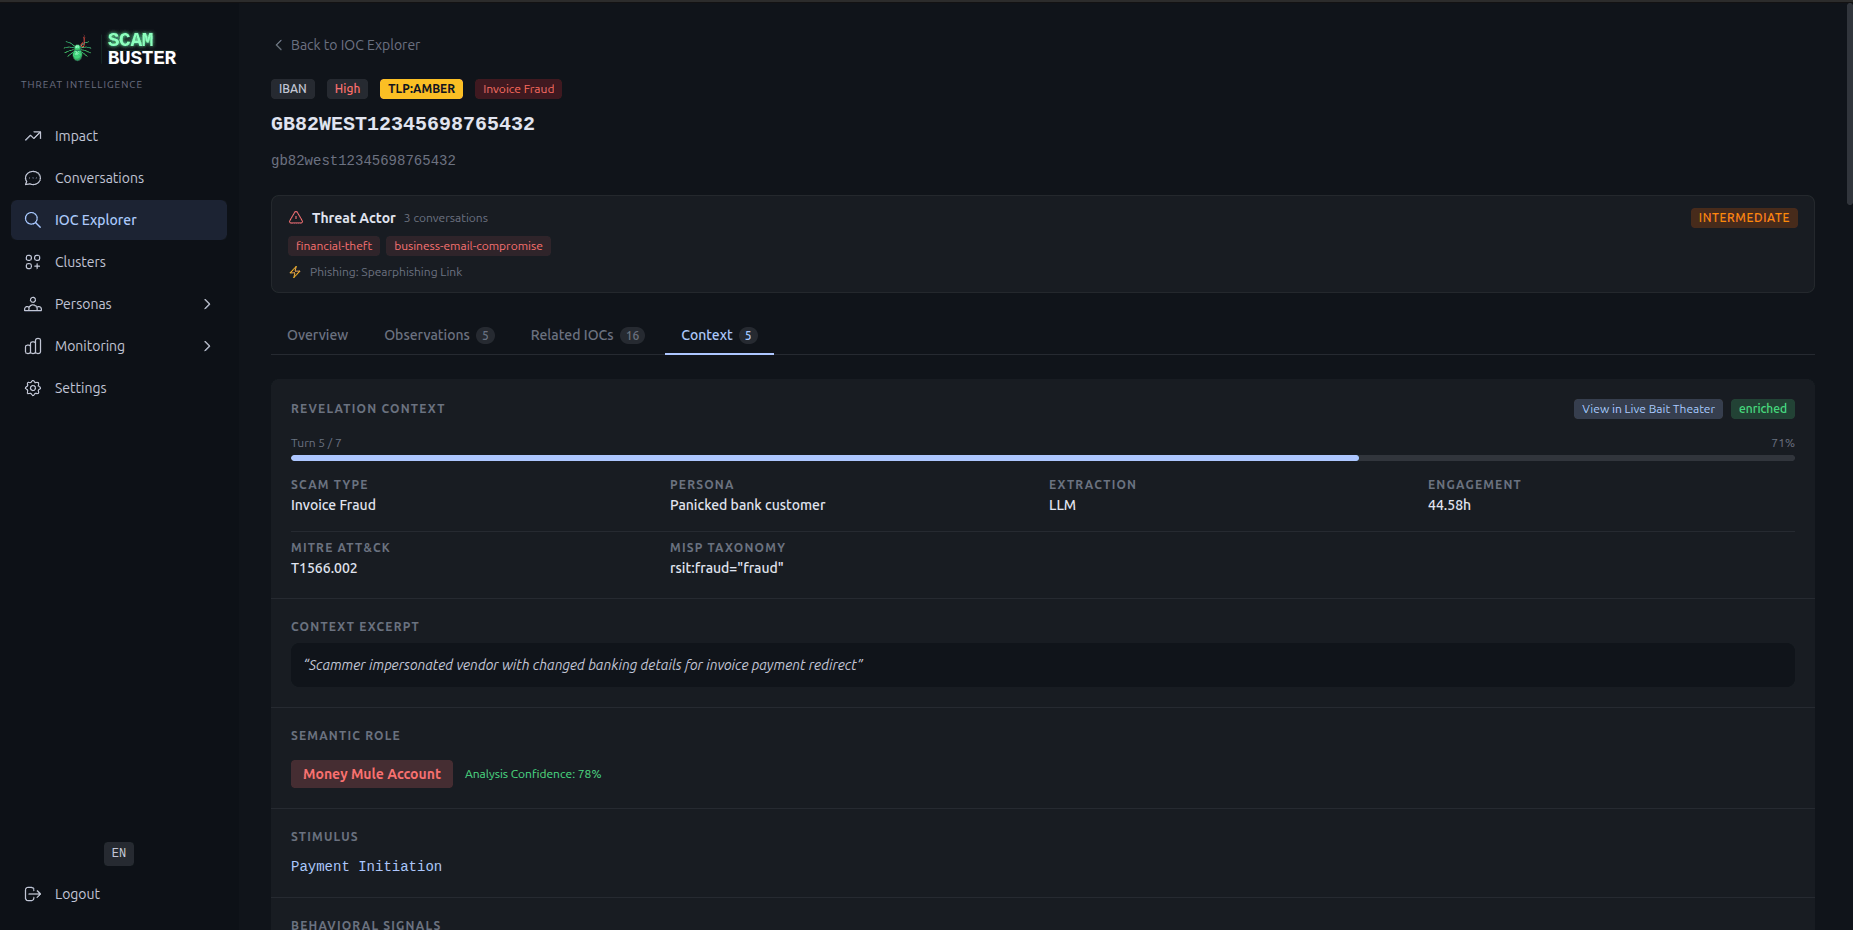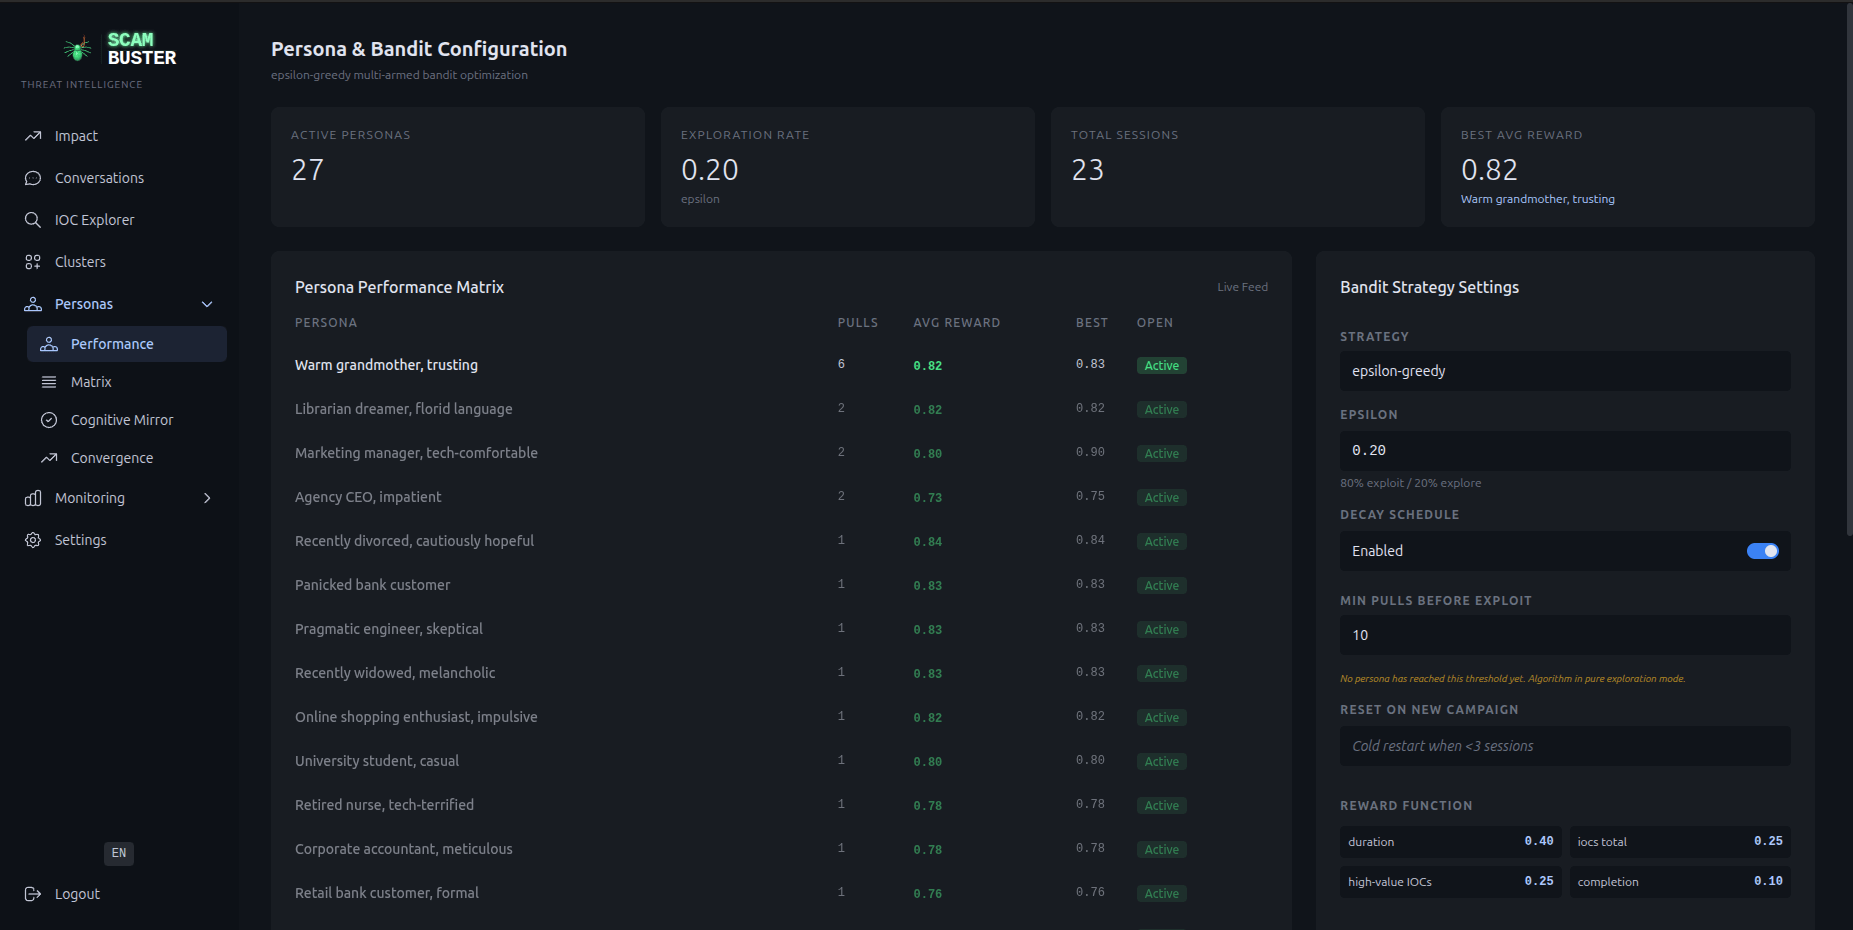 laugiov/scambuster
Defensive engagement & threat intelligence research laboratory. Converts inbound scam emails into actionable IOCs through controlled, policy-driven…
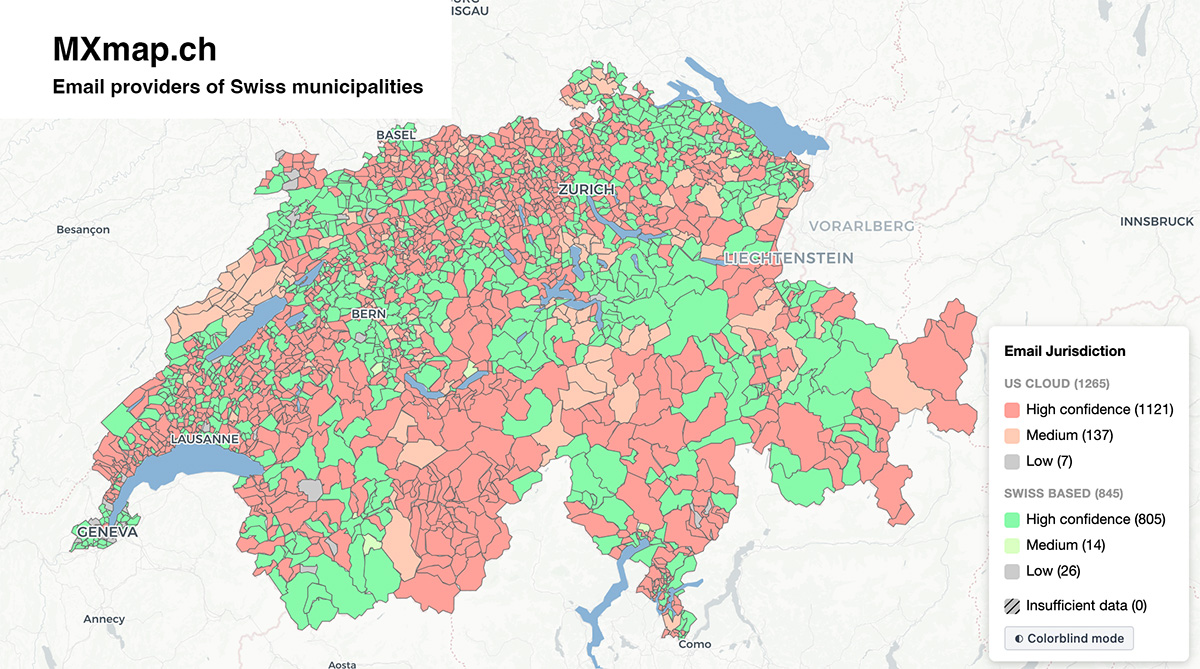 davidhuser/mxmap
Automated pipeline that resolves Swiss municipality domains, scrapes websites for email addresses, and classifies email providers via MX, SPF, DKIM,…
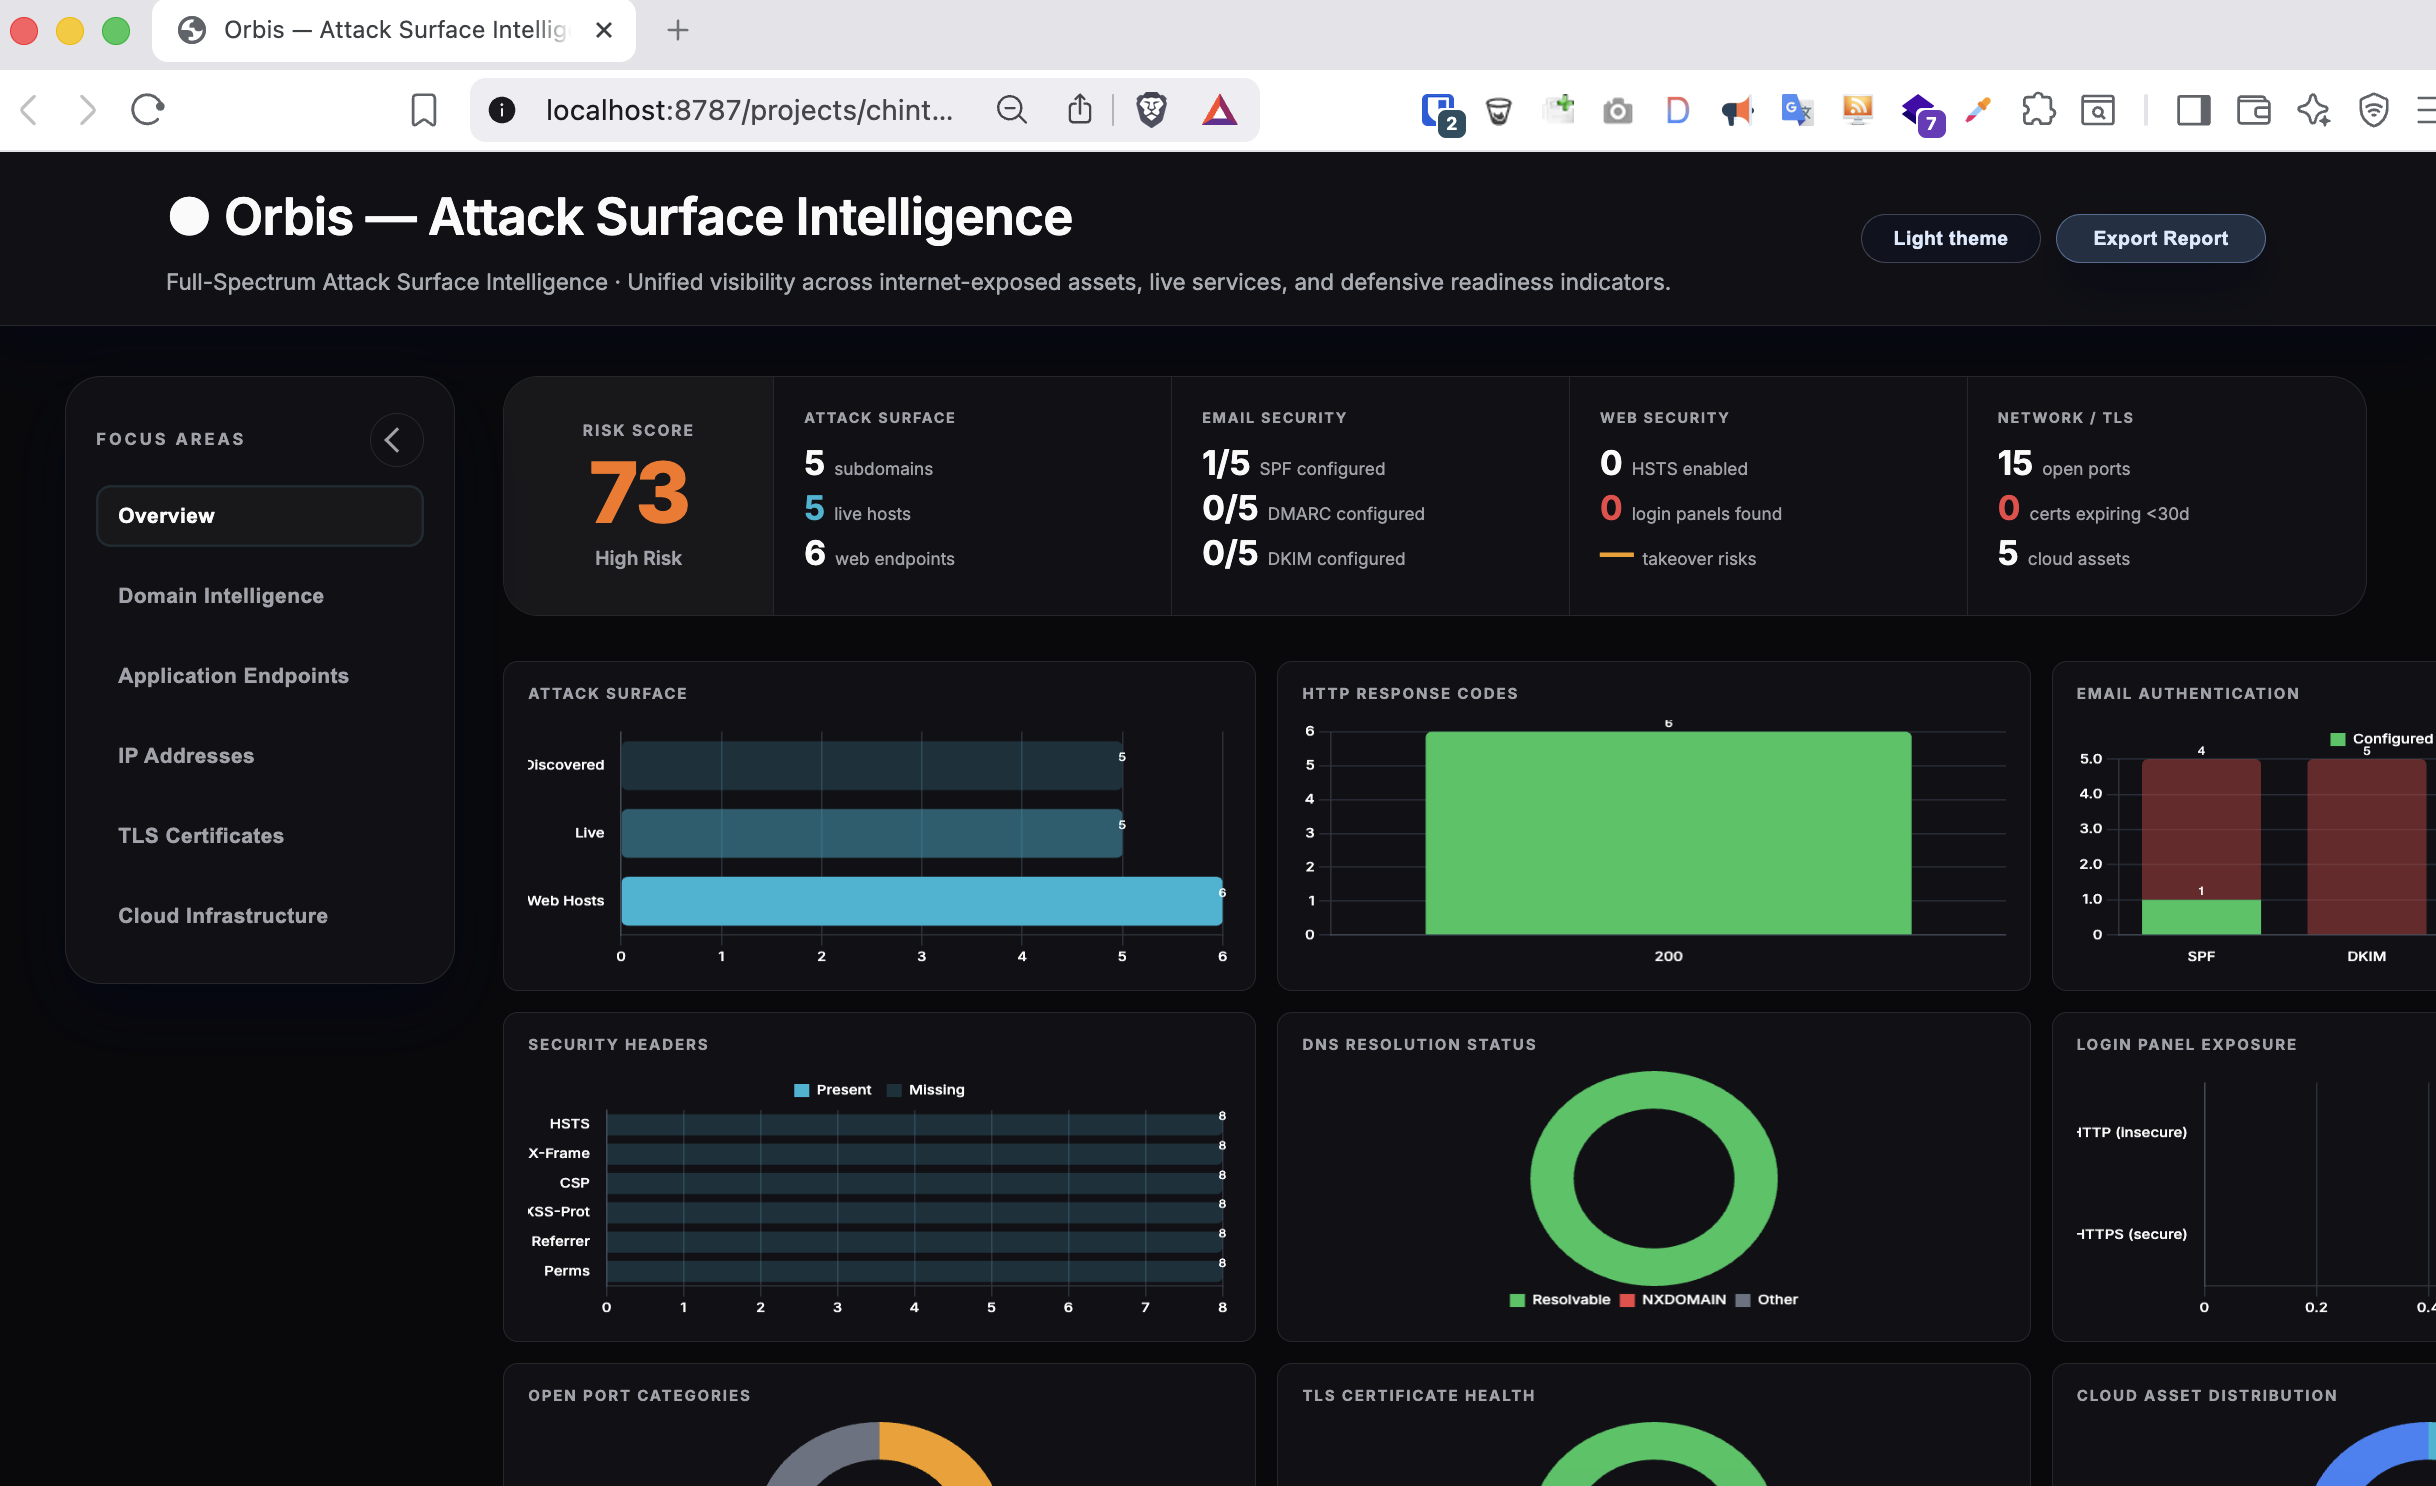 iamthefrogy/frogy2.0
Orbis is an full spectrum automated external attack surface intelligent toolkit.
 randomaccess3/awesome-bec
Repository of attack and defensive information for Business Email Compromise investigations
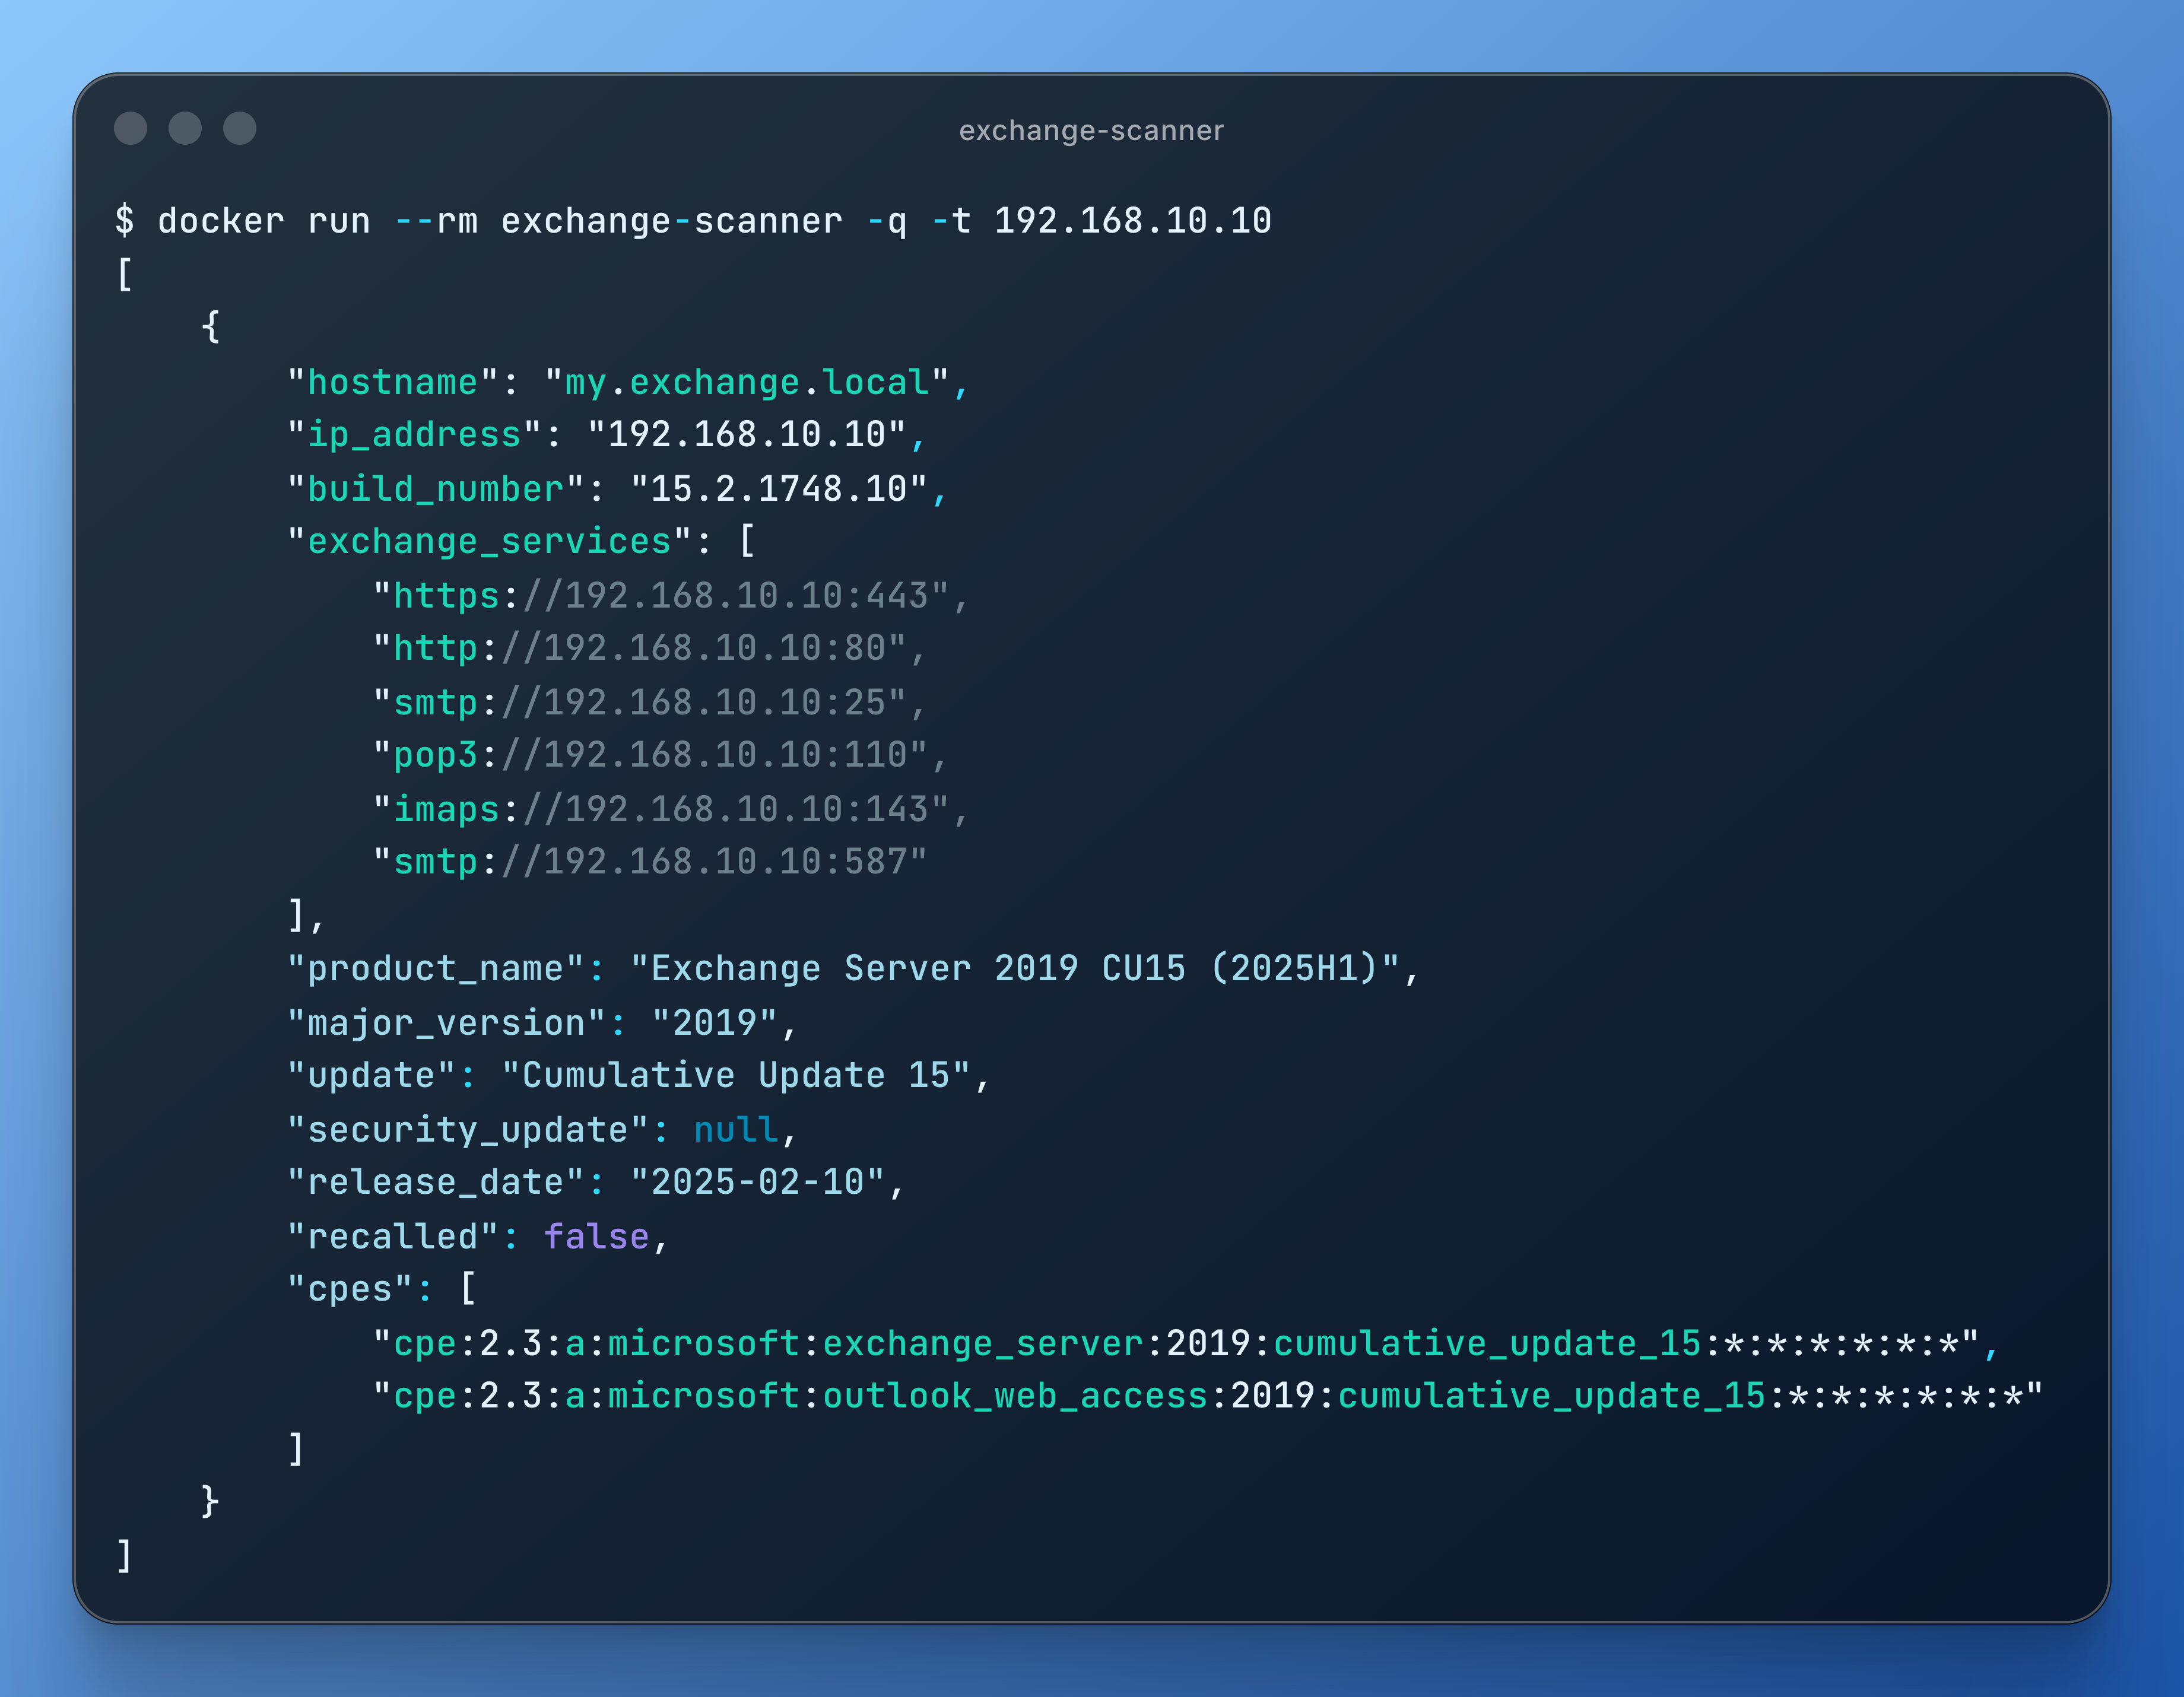 bishopfox/exchange-scanner
Identify public-facing Microsoft Exchange servers and determine their software versions
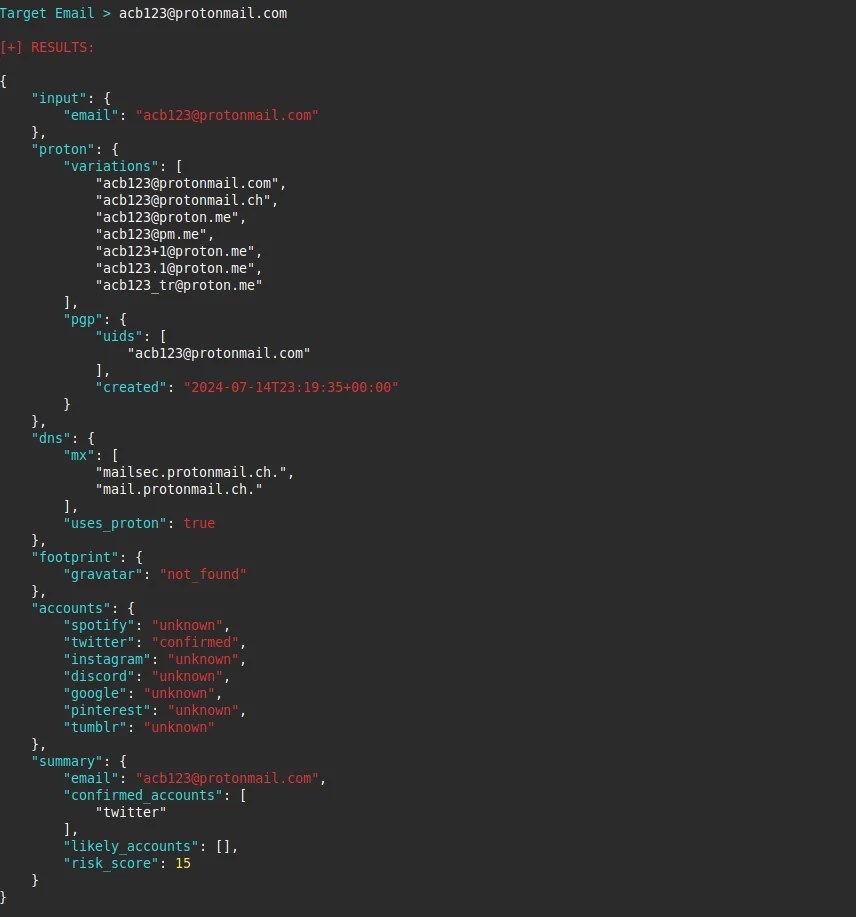 emrekybs/protonscope
Lightweight Python OSINT tool that analyzes email addresses to extract intelligence and digital footprint data, with a focus on ProtonMail…
 mr-r3b00t/crime-mapper
A tool for mapping cyber crime
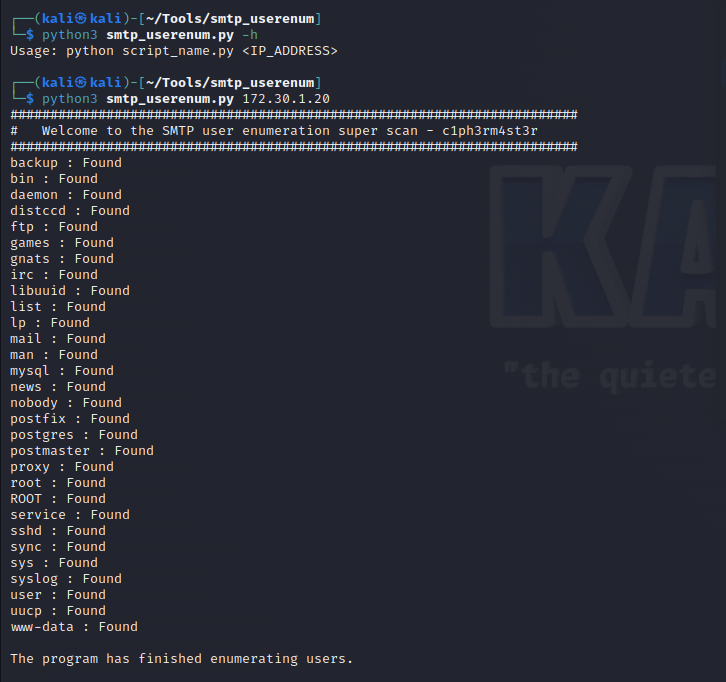 h3x0v3rl0rd/smtp_userenum
Python script for enumerating SMTP users by leveraging VRFY and EXPN commands to identify valid email accounts on a target mail server.
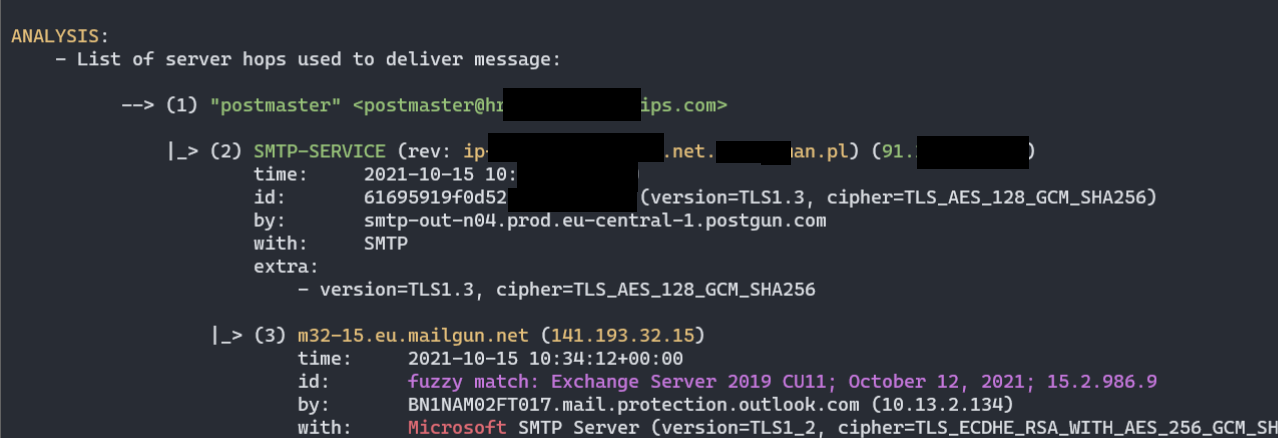 mgeeky/decode-spam-headers
A script that helps you understand why your E-Mail ended up in Spam
 pixelbubble/pastemonitor
Scrape Pastebin API to collect daily pastes, setup a wordlist and be alerted by email when you have a match.
 damianofalcioni/ip-biter
IP-Biter: The Hacker-friendly E-Mail (but not only) Tracking Framework
 black-scorp10/email-vulnerability-checker
Automated SPF and DMARC configuration checker that identifies email spoofing vulnerabilities across single or bulk domains using DNS lookups.
 sensepost/ruler
A tool to abuse Exchange services
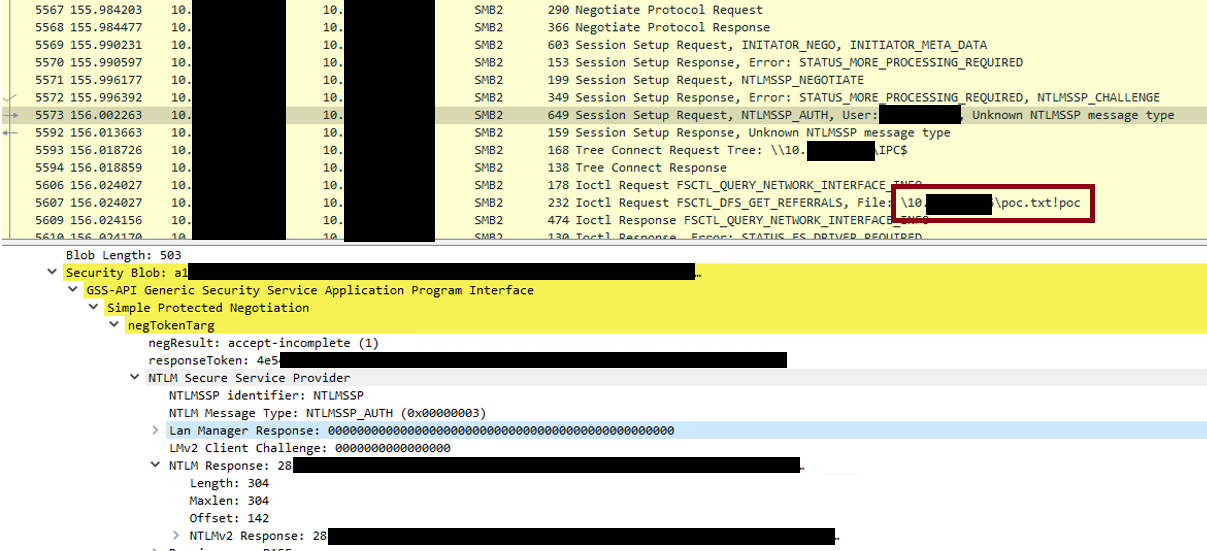 xaitax/cve-2024-21413-microsoft-outlook-remote-code-execution-vulnerability
Microsoft-Outlook-Remote-Code-Execution-Vulnerability
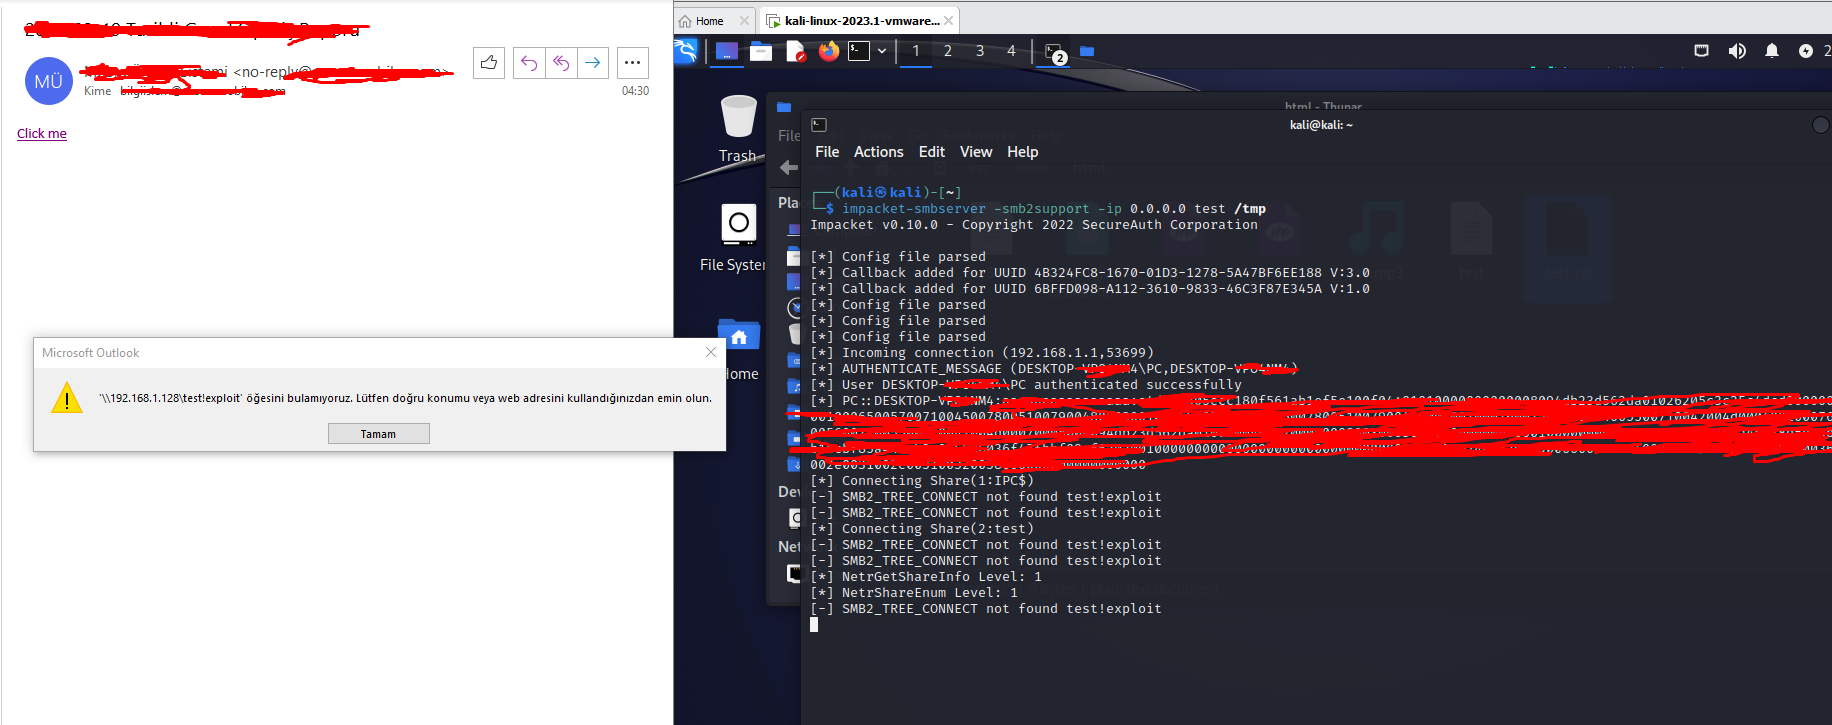 mseymend/cve-2024-21413
CVE-2024-21413 Açığını Kullanarak Giriş Bilgilerini Alma
 duy-31/cve-2024-21413
Microsoft Outlook Information Disclosure Vulnerability (leak password hash) - Expect Script POC