
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
44 results
cakephp-smtp-crlf preview

cakephp-smtp-crlf

GitHubabraxas/cakephp-smtp-crlf

CakePHP 5.4.2 - High - Remote - Header injection - SmtpTransport lone LF leftover of GHSA-2qh5

email-securityexploitationpenetration-testing+4
2 days ago
CVEngine preview

CVEngine

GitHubhevnsnt/cvengine

AI-first external attack surface assessment with continuous discovery, evidence-based vulnerability validation, and developer-agent MCP integration.
ai-securityemail-securityinformation-gathering+8
3724 days ago
CVE-2026-76461 preview

CVE-2026-76461

GitHub0xblackash/cve-2026-76461

Research repository for CVE-2026-76461, a critical SQL injection in Cisco Secure Email Gateway leading to root RCE, with detection rules, mitigation…

educationemail-securityexploitation+7
21 month ago
area51 preview

area51

GitHubthoropass-public/area51

The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
api-security-testingcloud-securityemail-security+4
71 month ago
CVE-2026-73570 preview

CVE-2026-73570

GitHubhainhc/cve-2026-73570

Proof-of-concept exploit for CVE-2026-73570, an unauthenticated OS command injection in Zimbra Collaboration Suite via zimbra-snmp log injection,…
email-securityexploitationincident-response+3
1 month ago
CVE-2026-34975 preview

CVE-2026-34975

GitHubromain-deperne/cve-2026-34975

Proof-of-concept and technical analysis of CRLF email header injection in Plunk's raw MIME construction, demonstrating Bcc injection and other…
email-securityexploitationpapers-research+2
1 month ago
CVE-2026-73570 preview

CVE-2026-73570

GitHubbiutrap/cve-2026-73570

Proof-of-concept exploit for CVE-2026-73570, demonstrating SMTP command injection via crafted RCPT TO header to trigger service status changes.
email-securityexploitationvulnerability-analysis+1
1 month ago
CVE-2026-73570 preview

CVE-2026-73570

GitHubhorkimhab/cve-2026-73570

Proof-of-concept exploit for an actively exploited Zimbra Collaboration Suite vulnerability, designed for authorized penetration testing and…
educationemail-securityexploitation+3
52 months ago
CVE-2026-73570 preview

CVE-2026-73570

GitHubjishino567/cve-2026-73570

Python PoC for CVE-2026-73570, an SMTP command injection in Zimbra. Sends malformed RCPT TO payloads to trigger shell command execution via…
email-securityexploitationpenetration-testing+3
42 months ago
css-the-bomb-inside-your-inbox preview

css-the-bomb-inside-your-inbox

GitHubportswigger/css-the-bomb-inside-your-inbox

All the materials for Gareth Heyes' Black Hat talk: CSS: the bomb inside your inbox.
ai-securitycurated-resourcesdata-exfiltration+7
432 months ago
CVE-2026-54433 preview

CVE-2026-54433

GitHubaramosf/cve-2026-54433

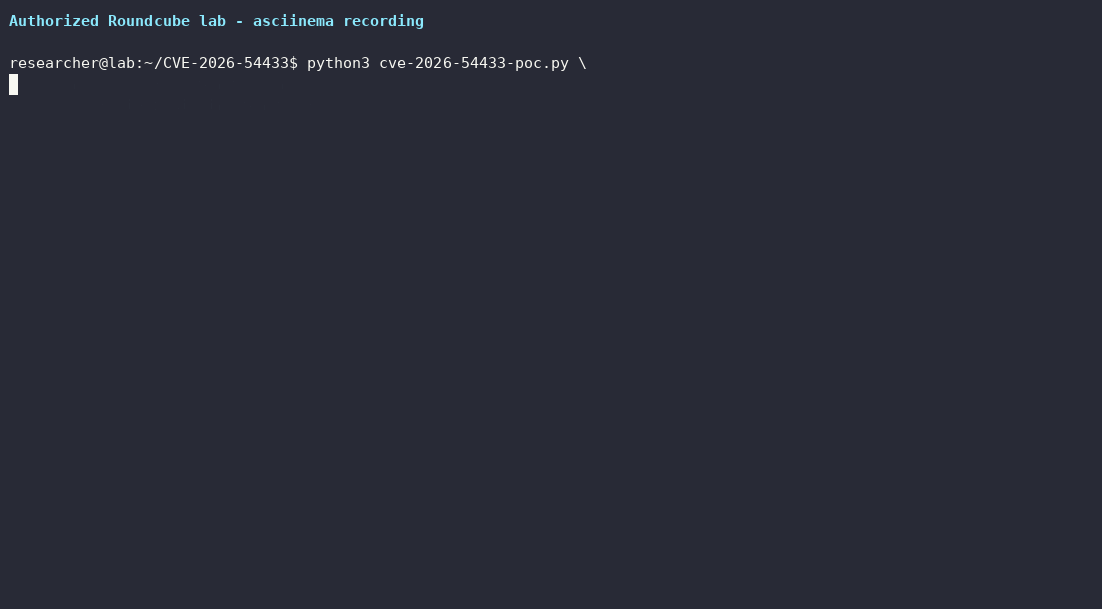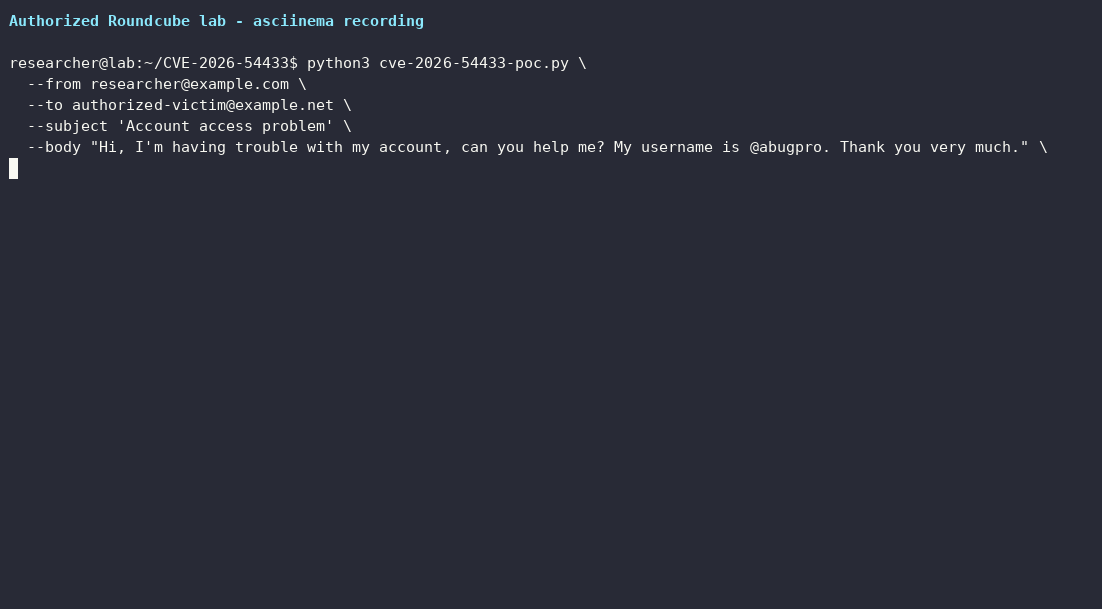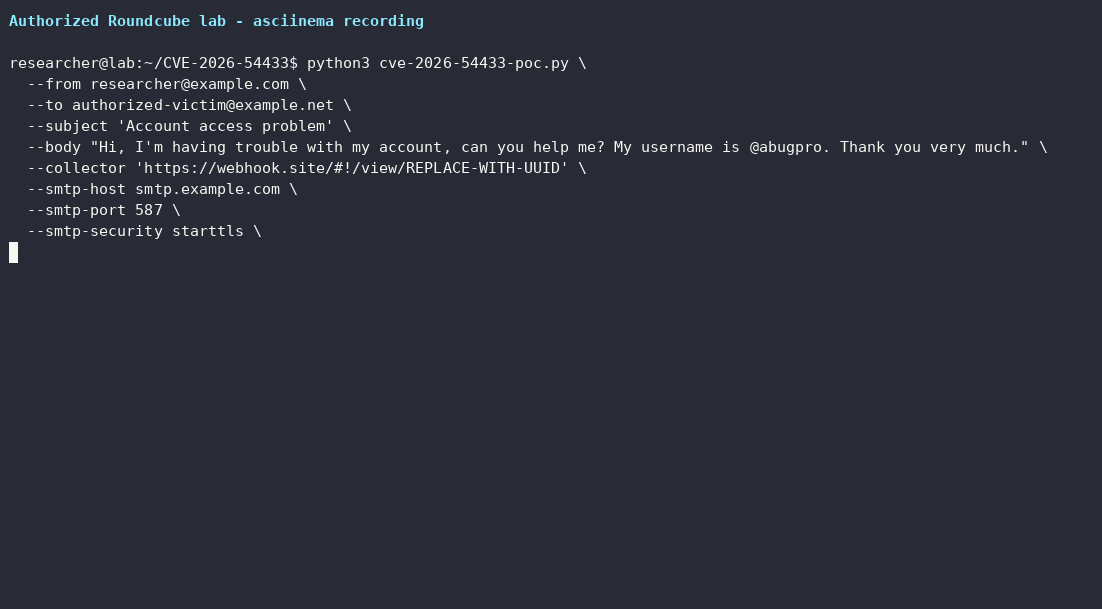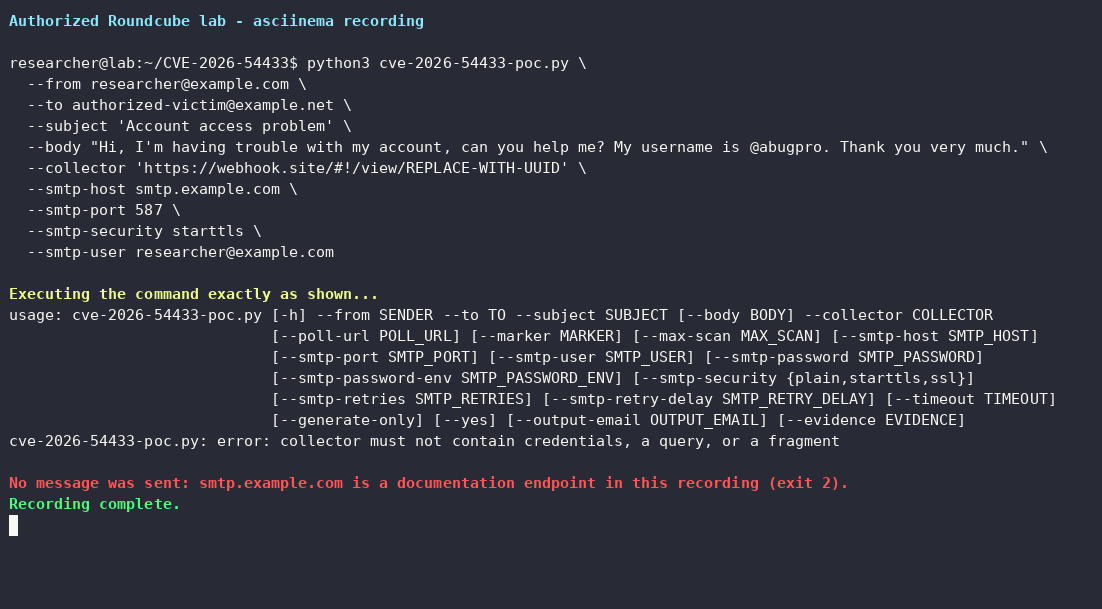
Configurable Python PoC for CVE-2026-54433, a stored XSS in Roundcube's plain-text email renderer. Generates crafted .eml, sends via SMTP, and…
data-exfiltrationemail-securityexploitation+6
2 months ago
Ashwesker-CVE-2025-68645 preview

Ashwesker-CVE-2025-68645

GitHubashwesker/ashwesker-cve-2025-68645

POC BLH Magelang CSIRT 2026 by babyrootkid
email-securityexploitationvulnerability-analysis+2
2 months ago
CVE-2026-11113-SMTP-Header-Injection-in-Contact-Form preview

CVE-2026-11113-SMTP-Header-Injection-in-Contact-Form

GitHubgeorge0papasotiriou/cve-2026-11113-smtp-header-injection-in-contact-form

Proof-of-concept exploit for CVE-2026-11113, demonstrating SMTP header injection in a Flask contact form via unsanitized email input; includes…
educationemail-securityexploitation+4
2 months ago
CVE-2026-28289 preview

CVE-2026-28289

GitHub0xblackash/cve-2026-28289

CVE-2026-28289
email-securityexploitationpayload-development+3
17 months ago
CVE-2026-25916-Roundcube-Webmail-DOM-based-XSS-Exploit-via-SVG-href-Attribute preview

CVE-2026-25916-Roundcube-Webmail-DOM-based-XSS-Exploit-via-SVG-href-Attribute

GitHubmbanyamer/cve-2026-25916-roundcube-webmail-dom-based-xss-exploit-via-svg-href-attribute

Python exploit for Roundcube Webmail DOM-based XSS (CVE-2026-25916) via SVG href attributes, enabling session hijacking and data exfiltration through…

email-securityexploitationpayload-generation+3
38 months ago
splitting-the-email-atom preview

splitting-the-email-atom

GitHubportswigger/splitting-the-email-atom

Research materials and tooling for exploiting email address parser discrepancies to bypass access controls, including fuzzers, Hackvertor tags, CSS…
ctfeducationemail-security+7
10011 months ago
SOGo_web_mail-vulnerability-CVE-2025-50340 preview

SOGo_web_mail-vulnerability-CVE-2025-50340

GitHubmillad7/sogo_web_mail-vulnerability-cve-2025-50340

Insecure Direct Object Reference (IDOR vulnerability) in SOGo Webmail Allows a user to send emails on behalf of another user.
email-securityimpersonation-toolspenetration-testing+3
1 year ago
CVE-2024-21413 preview

CVE-2024-21413

GitHubthemehackers/cve-2024-21413

CVE-2024-21413 | Microsoft Outlook Remote Code Execution Vulnerability PoC

email-securityexploitationpayload-generation+3
251 year ago
Previous123Next