
cakephp-smtp-crlf
 abraxas/cakephp-smtp-crlf
CakePHP 5.4.2 - High - Remote - Header injection - SmtpTransport lone LF leftover of GHSA-2qh5
email-securityexploitationpenetration-testing+4
abraxas/cakephp-smtp-crlfCakePHP 5.4.2 - High - Remote - Header injection - SmtpTransport lone LF leftover of GHSA-2qh5
 thoropass-public/area51
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 hainhc/cve-2026-73570
Proof-of-concept exploit for CVE-2026-73570, an unauthenticated OS command injection in Zimbra Collaboration Suite via zimbra-snmp log injection,…
 mr-un1k0d3r/redteamscripts
Collection of offensive red team scripts including process termination, SPF bypass for phishing, password spraying, and ColdFusion password…
 jishino567/cve-2026-73570
Python PoC for CVE-2026-73570, an SMTP command injection in Zimbra. Sends malformed RCPT TO payloads to trigger shell command execution via…
 biutrap/cve-2026-73570
Proof-of-concept exploit for CVE-2026-73570, demonstrating SMTP command injection via crafted RCPT TO header to trigger service status changes.
 horkimhab/cve-2026-73570
Proof-of-concept exploit for an actively exploited Zimbra Collaboration Suite vulnerability, designed for authorized penetration testing and…
 ashwesker/ashwesker-cve-2025-68645
POC BLH Magelang CSIRT 2026 by babyrootkid
 0xblackash/cve-2026-28289
CVE-2026-28289
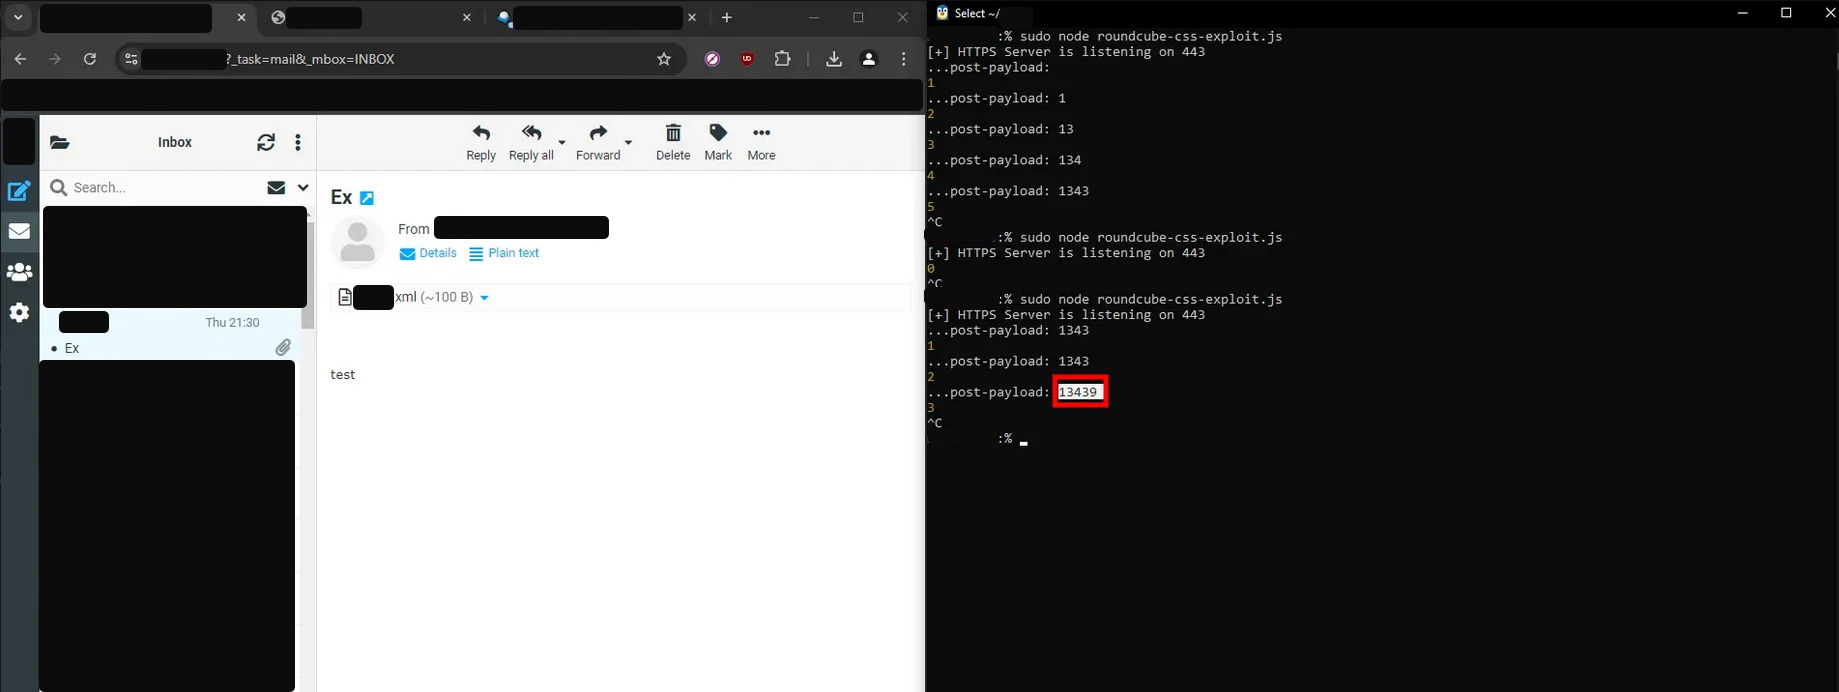 victoni/roundcube-cve-2024-42008-and-cve-2024-42010-poc
POC for Roundcube vulnerabilities CVE-2024-42008 and CVE-2024-42010
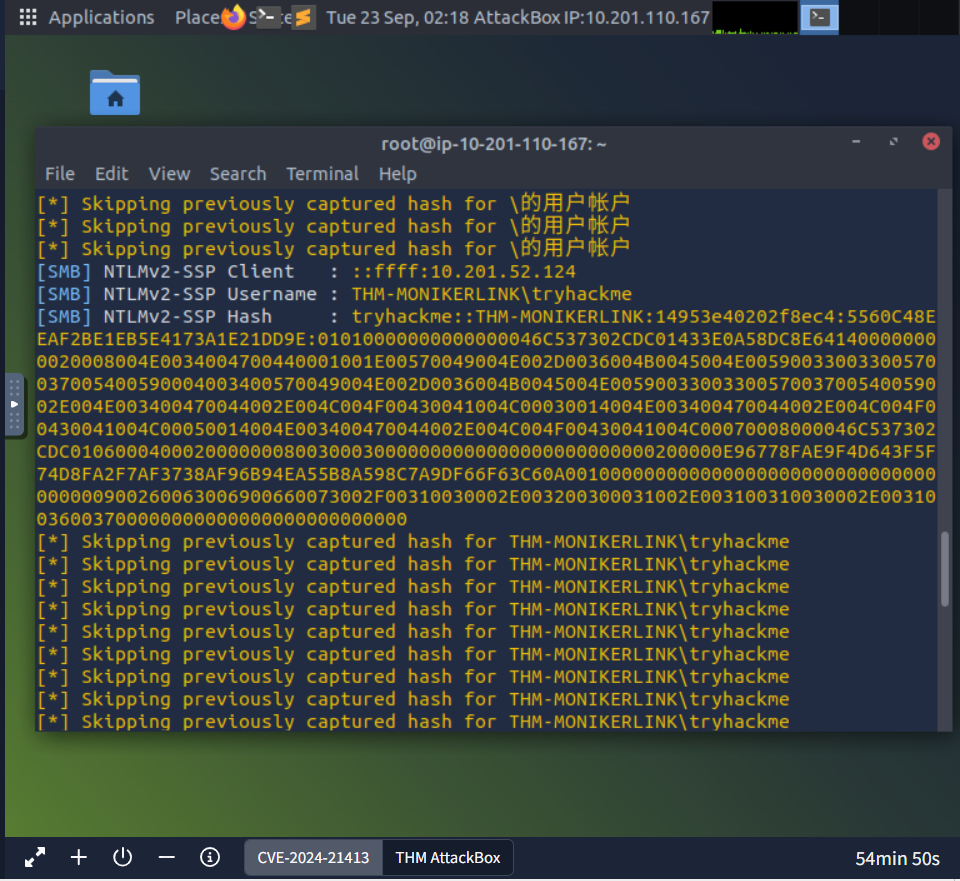 yass2400012/email-exploit-moniker-link-cve-2024-21413-
Proof-of-concept exploit for CVE-2024-21413 using Moniker Link in HTML email to trigger SMB connection and capture netNTLMv2 hashes via Responder.…
 materaj2/cve-2026-45185-detection-script
These detection scripts are property of the SECPlayground Platform. Two safe detection scripts. Neither drives the close_notify-mid-BDAT trigger, so…
 rxerium/cve-2024-39929
Detection method for Exim vulnerability CVE-2024-39929
 sqrtzeroknowledge/cve-2023-23397_exploit_0day
Exploit for the CVE-2023-23397
 jacquesquail/cve-2023-23397
Proof-of-concept exploit for CVE-2023-23397, a Microsoft Outlook privilege escalation vulnerability. Sends a crafted email with a malicious UNC path…