prompt-injection-email-samples

Open .eml test set for evaluating how email security controls and AI mailbox assistants handle indirect prompt injection across disclosure,…

Open .eml test set for evaluating how email security controls and AI mailbox assistants handle indirect prompt injection across disclosure,…

Deploy a phishing infrastructure on the fly.

Open-source interactive security awareness training library with 130+ SCORM exercises covering phishing, vishing, BEC, MFA fatigue, and OWASP AI/LLM…

A curated portfolio showcasing my SOC investigations, threat hunting projects, DFIR labs, detection engineering, technical blogs, and cybersecurity…

Self-contained Python PoC for Dovecot SQL authentication bypass: logs in as any user without the real password and enumerates usernames on vulnerable…

Documentation of my hands-on lab Moniker Link (CVE-2024-21413) completed on TryHackMe.

Lab write-up analyzing CVE-2024-21413 Outlook Moniker Link exploitation, NetNTLMv2 credential leakage via SMB, detection with YARA/Wireshark, and…

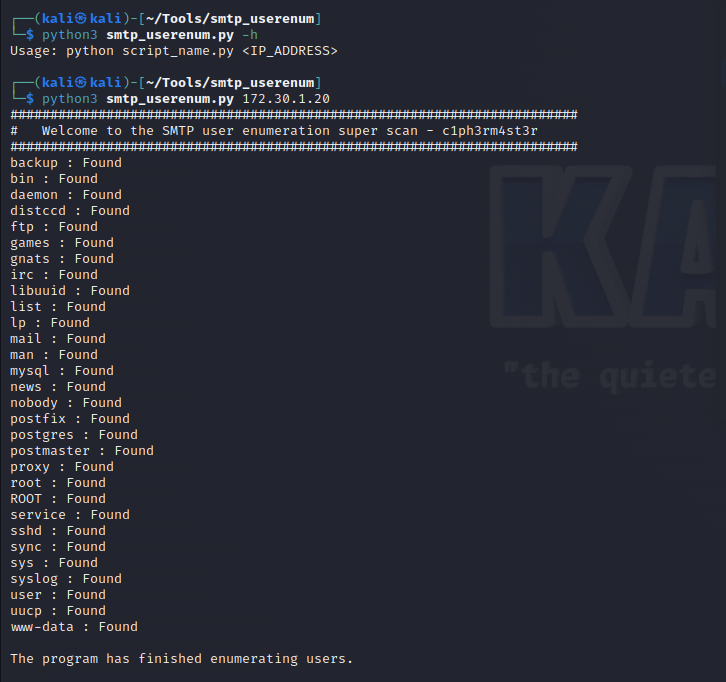
Python script for enumerating SMTP users by leveraging VRFY and EXPN commands to identify valid email accounts on a target mail server.

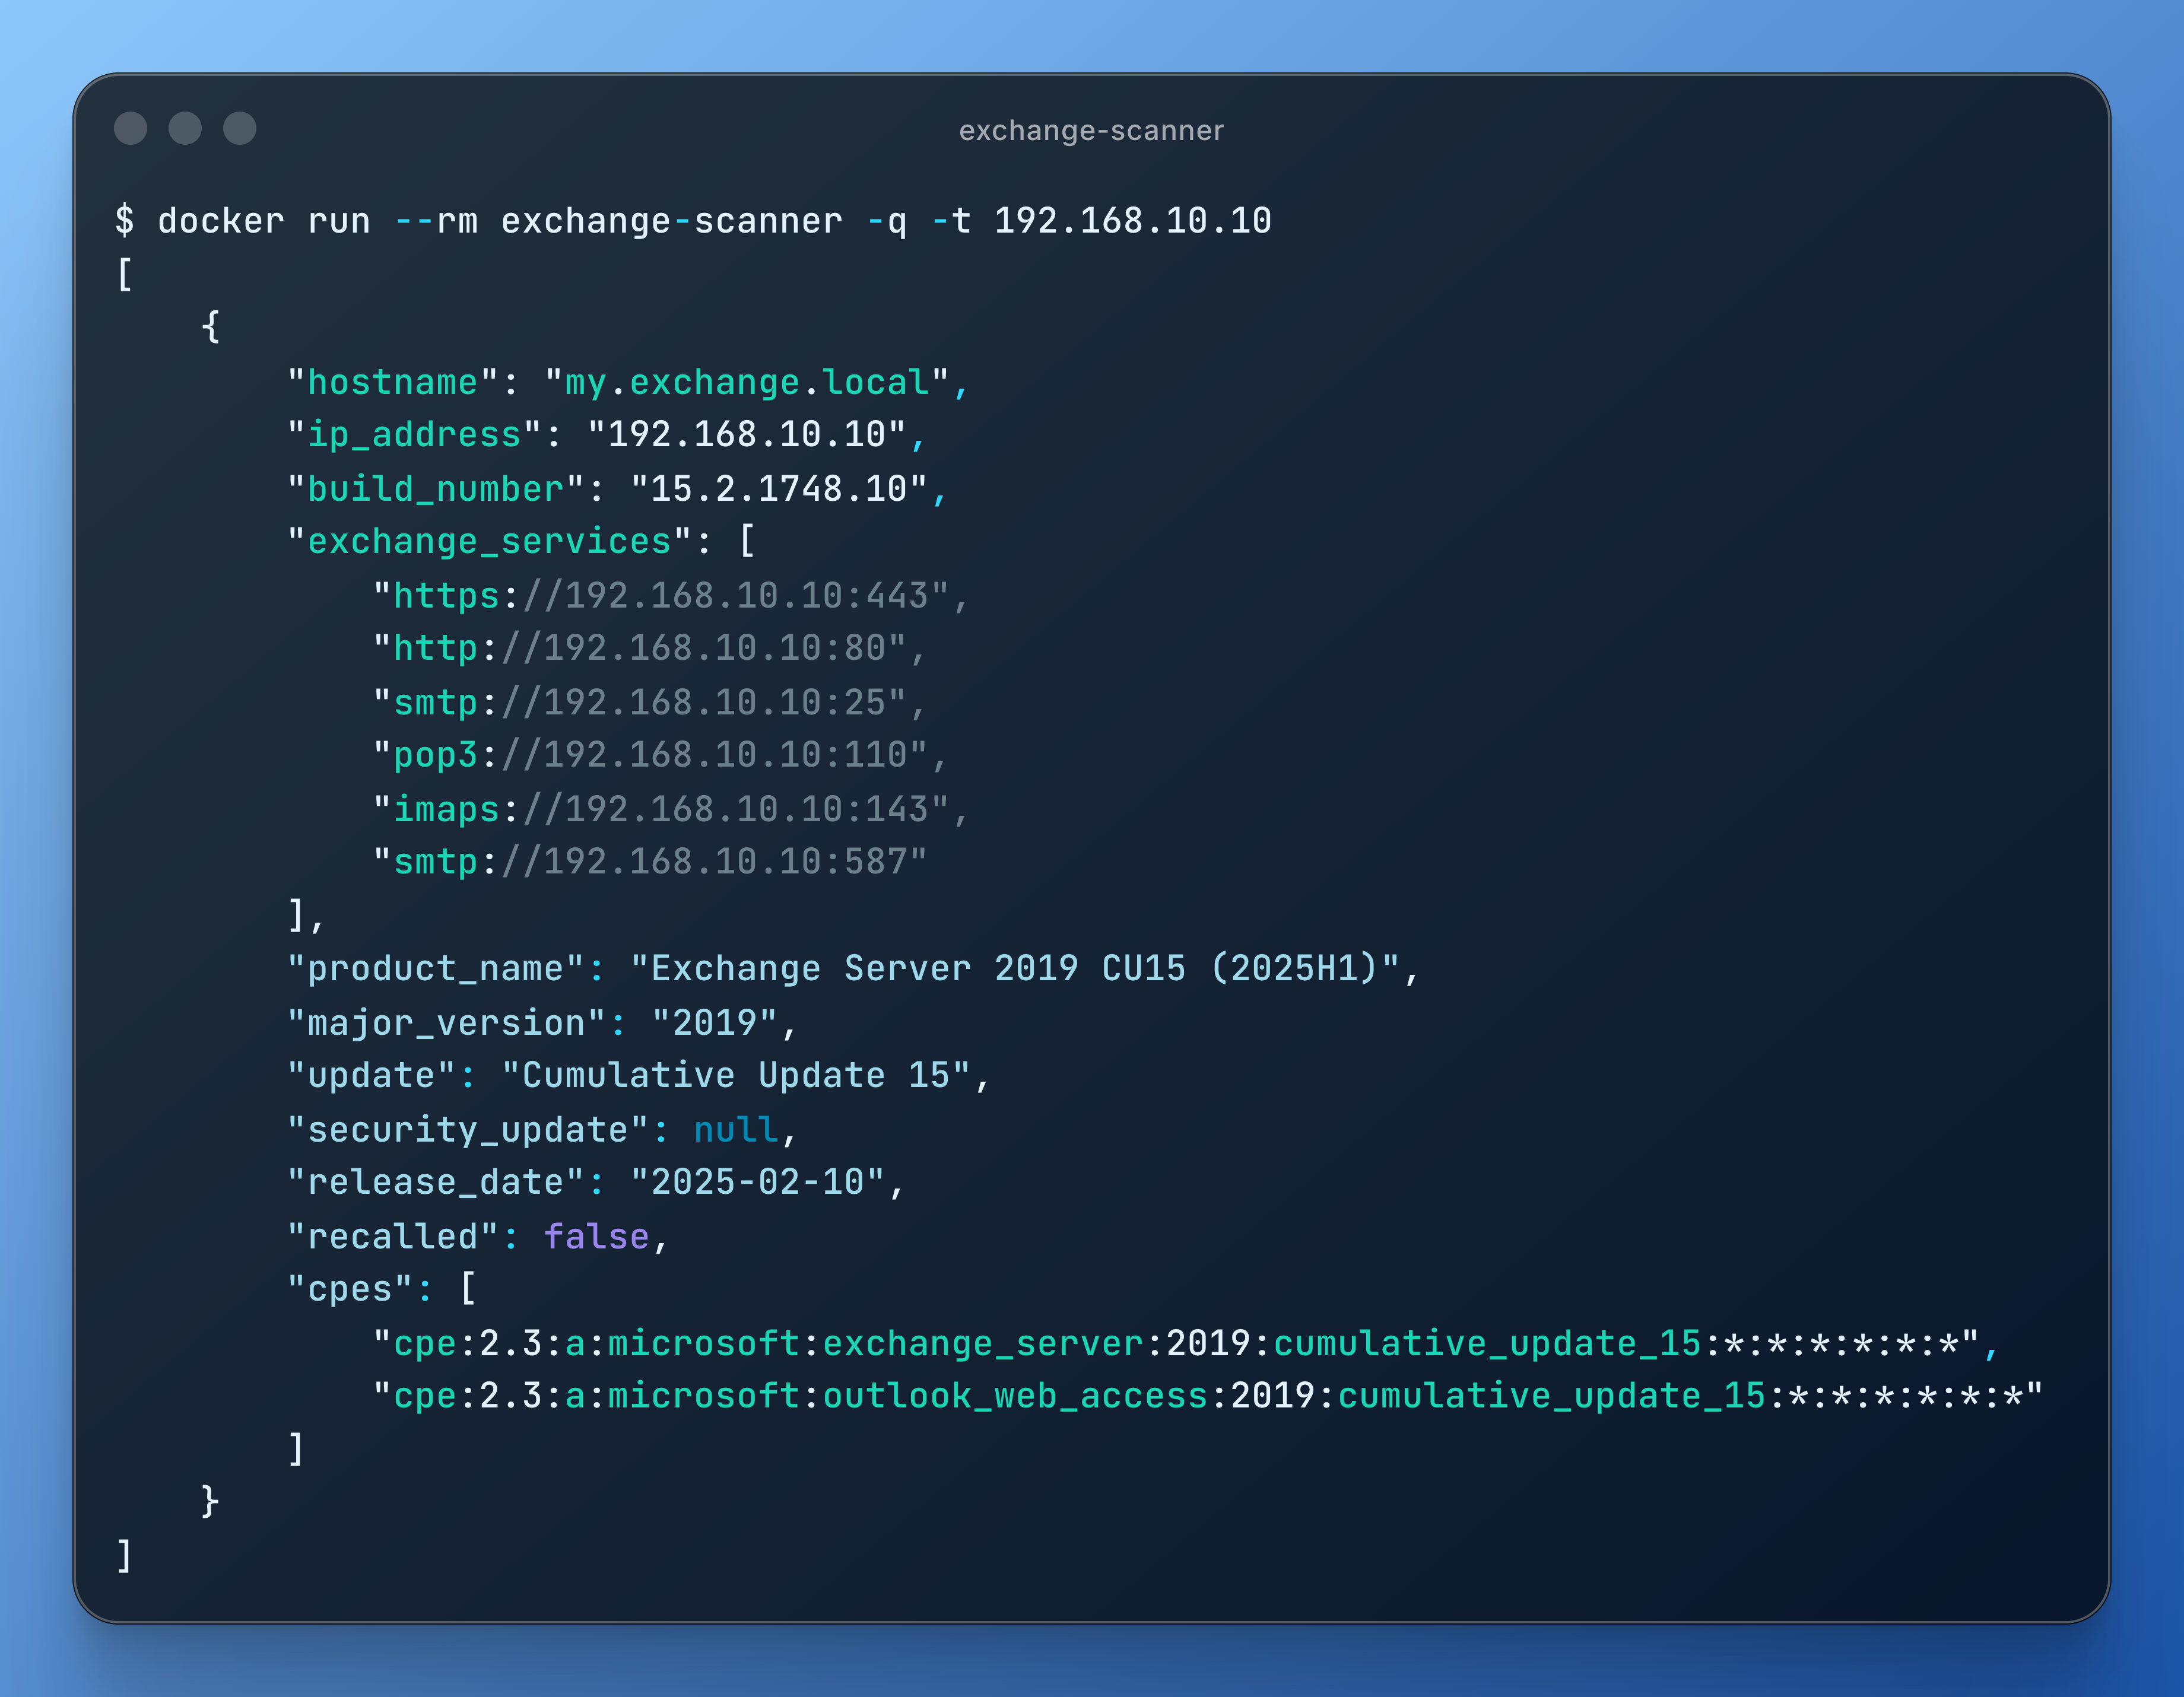
Identify public-facing Microsoft Exchange servers and determine their software versions

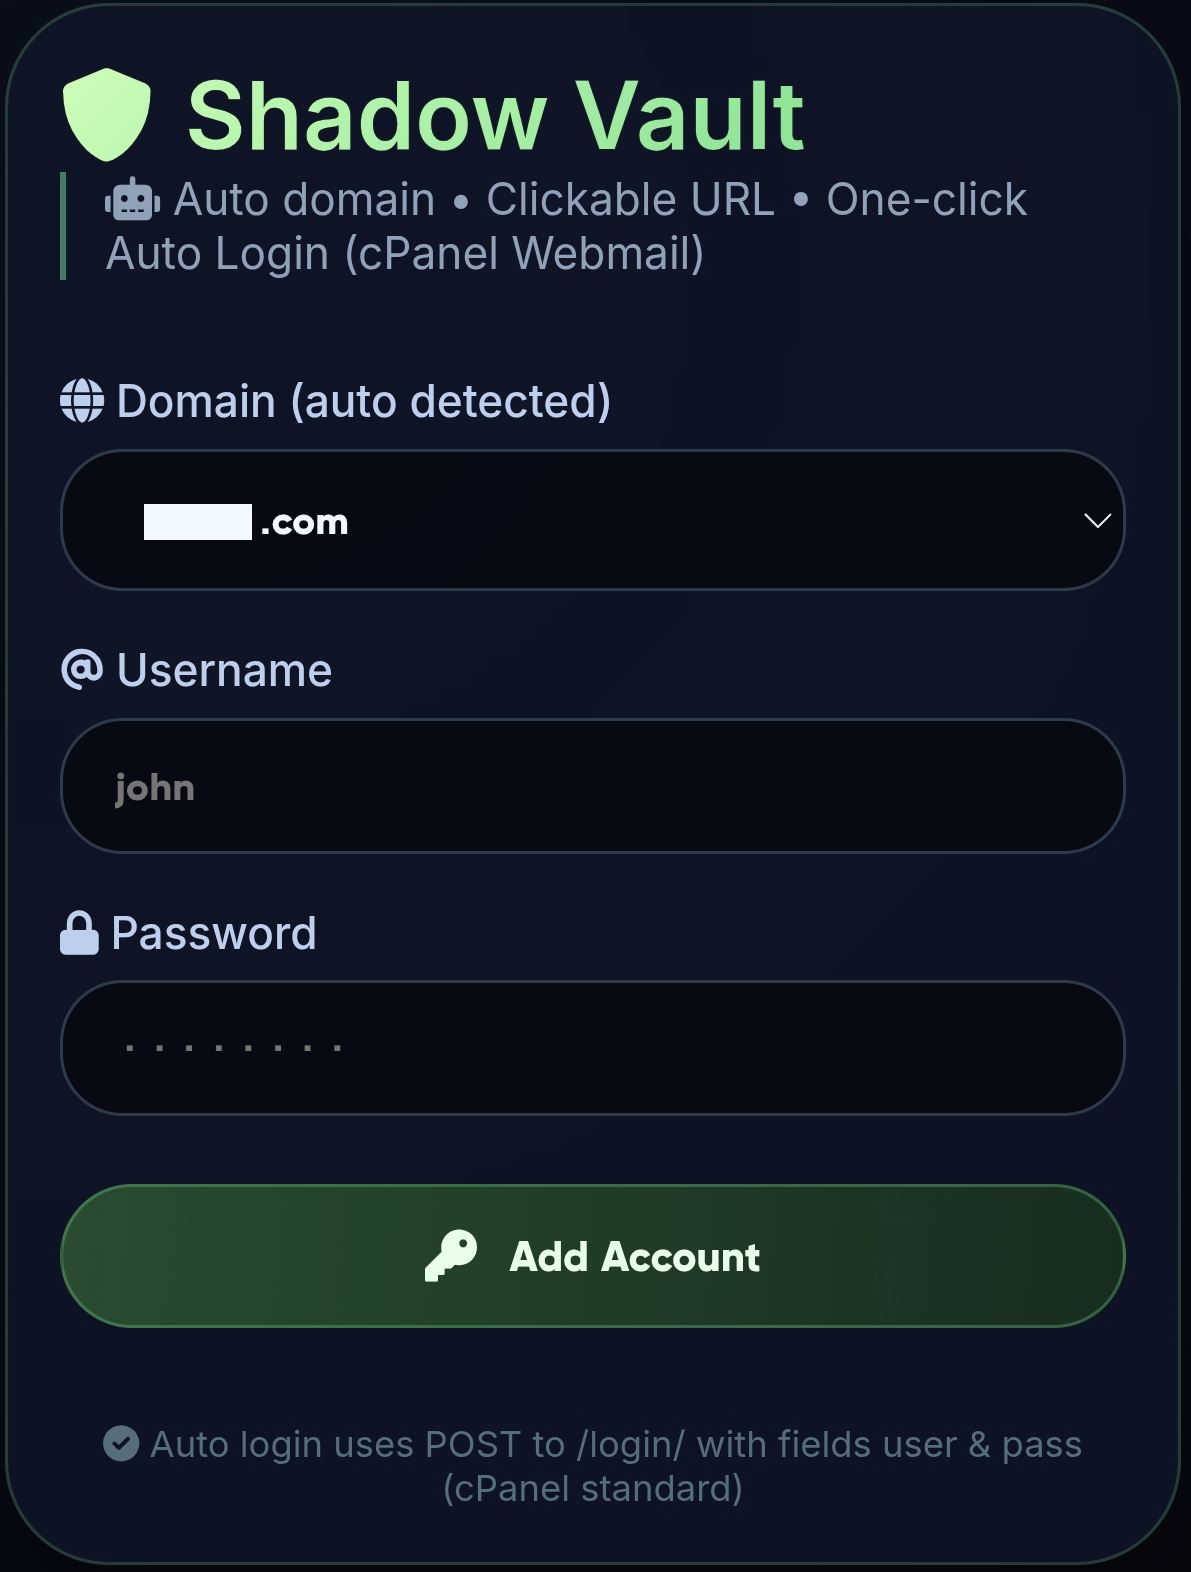
Shadow Vault – Add shadow users with SHA-512 hash, auto aging match, multiple write fallbacks.

amavis is a high-performance email content filter framework written in Perl.

Documentation of CVE-2026-31283: an email bombing vulnerability in Totara LMS's forgot password API due to missing rate limiting, allowing…

Insecure Direct Object Reference (IDOR vulnerability) in SOGo Webmail Allows a user to send emails on behalf of another user.

Python exploit for CVE-2024-21413, a Microsoft Outlook remote code execution vulnerability. Sends a crafted email via SMTP to trigger code execution…

An automated attack chain based on CVE-2022-30190, 163 email backdoor, and image steganography.

Educational exploit for CVE-2024-21413 (Moniker Link) demonstrating Outlook RCE and NTLM credential leak via crafted hyperlinks, with detection and…

Instructions for installing a vulnerable version of Exim and its expluatation

Python 3 proof-of-concept for CVE-2023-51764 SMTP smuggling vulnerability, enabling email spoofing via crafted SMTP sessions.