

opencti
 opencti-platform/opencti
Open Cyber Threat Intelligence Platform
curated-resourceseducationemail-security+6
opencti-platform/openctiOpen Cyber Threat Intelligence Platform
 security-onion-solutions/securityonion
Open-source security monitoring platform for threat hunting, intrusion detection, log management, incident response, and endpoint visibility with…
 ransomleak/training-security-awareness
Open-source interactive security awareness training library with 130+ SCORM exercises covering phishing, vishing, BEC, MFA fatigue, and OWASP AI/LLM…
 portswigger/splitting-the-email-atom
Research materials and tooling for exploiting email address parser discrepancies to bypass access controls, including fuzzers, Hackvertor tags, CSS…
 lissy93/awesome-privacy
🦄 A curated list of privacy & security-focused software and services
 all3xj/fixing-google-secops-detections
Tuning and refactoring Google Chronicle Curated Detections to eliminate alert fatigue and fix logic gaps/bugs.
 danithehack3r/cve-2024-42009-poc
CVE-2024-42009 Proof of Concept
 yfelipecruvinel/tryhackme-moniker-link
Documentation of my hands-on lab Moniker Link (CVE-2024-21413) completed on TryHackMe.
 chenjj/espoofer
An email spoofing testing tool that aims to bypass SPF/DKIM/DMARC and forge DKIM signatures.🍻
 mj-bin/poc_cve-2026-45185
POC_CVE-2026-45185 for nuclei-templates
 an0nud4y/evilginx-phishing-infra-setup
Evilginx Phishing Infrastructure Setup Guide - Securing Evilginx and Gophish Infrastructure, Removing IOCs, Phishing TTPs
 dev-lu/osint_toolkit
Open source platform for cyber security analysts with many features for threat intelligence and detection engineering.
 abc1230940/soc336-windows-ole-zero-click-rce-exploitation-detected-cve-2025-21298
SOC336 - Windows OLE Zero-Click RCE Exploitation Detected (CVE-2025-21298) Walkthrough
 saykino/cve-2026-31283
Documentation of CVE-2026-31283: an email bombing vulnerability in Totara LMS's forgot password API due to missing rate limiting, allowing…
 trustedsec/reel
Phishing simulation and awareness framework for node-based campaigns, credential capture, SMTP delivery, CAPTCHA, and optional browser credential…
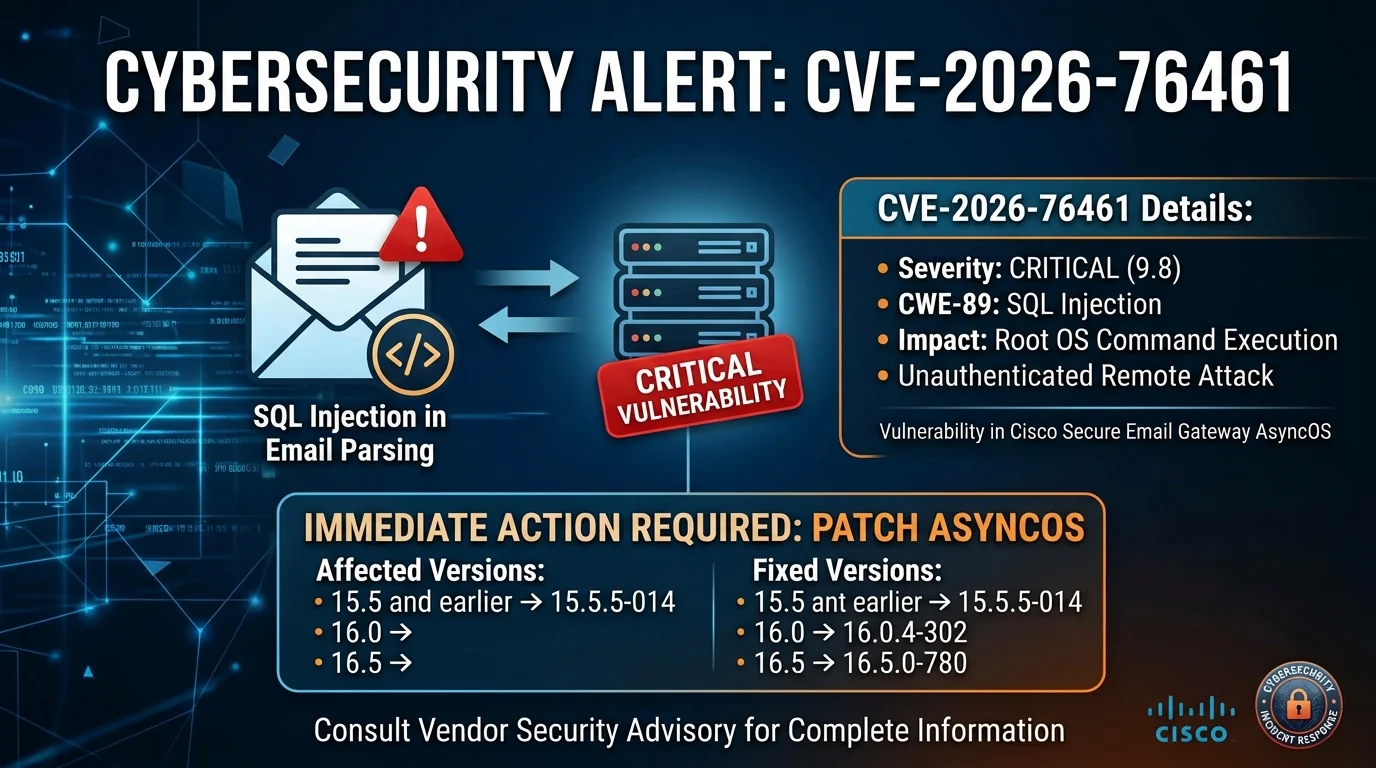 0xblackash/cve-2026-76461
Research repository for CVE-2026-76461, a critical SQL injection in Cisco Secure Email Gateway leading to root RCE, with detection rules, mitigation…
 michael-david-fry/cve-2024-39929
POC to test CVE-2024-39929 against EXIM mail servers
 0xblackash/cve-2026-73570
Advisory and detection guidance for CVE-2026-73570, an unauthenticated OS command injection in Zimbra SNMP notification processing leading to remote…