

wazuh
 wazuh/wazuh
Open-source XDR and SIEM platform for threat detection, log analysis, file integrity monitoring, vulnerability assessment, and compliance management…
anomaly-detectionanti-botcloud-security+12
16.5k1 day ago
wazuh/wazuhOpen-source XDR and SIEM platform for threat detection, log analysis, file integrity monitoring, vulnerability assessment, and compliance management…
 misp/misp
MISP (core software) - Open Source Threat Intelligence and Sharing Platform
 zeek/zeek
Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.
 stamparm/maltrail
Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
 oisf/suricata
Open-source network IDS/IPS/NSM engine for real-time traffic inspection, intrusion detection and prevention, protocol analysis, and rule-based threat…
 security-onion-solutions/securityonion
Open-source security monitoring platform for threat hunting, intrusion detection, log management, incident response, and endpoint visibility with…
 neo23x0/loki
IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…
 falcosecurity/falco
Real-time cloud-native runtime security agent for Linux that monitors syscalls and container/Kubernetes metadata to detect anomalous behavior and…
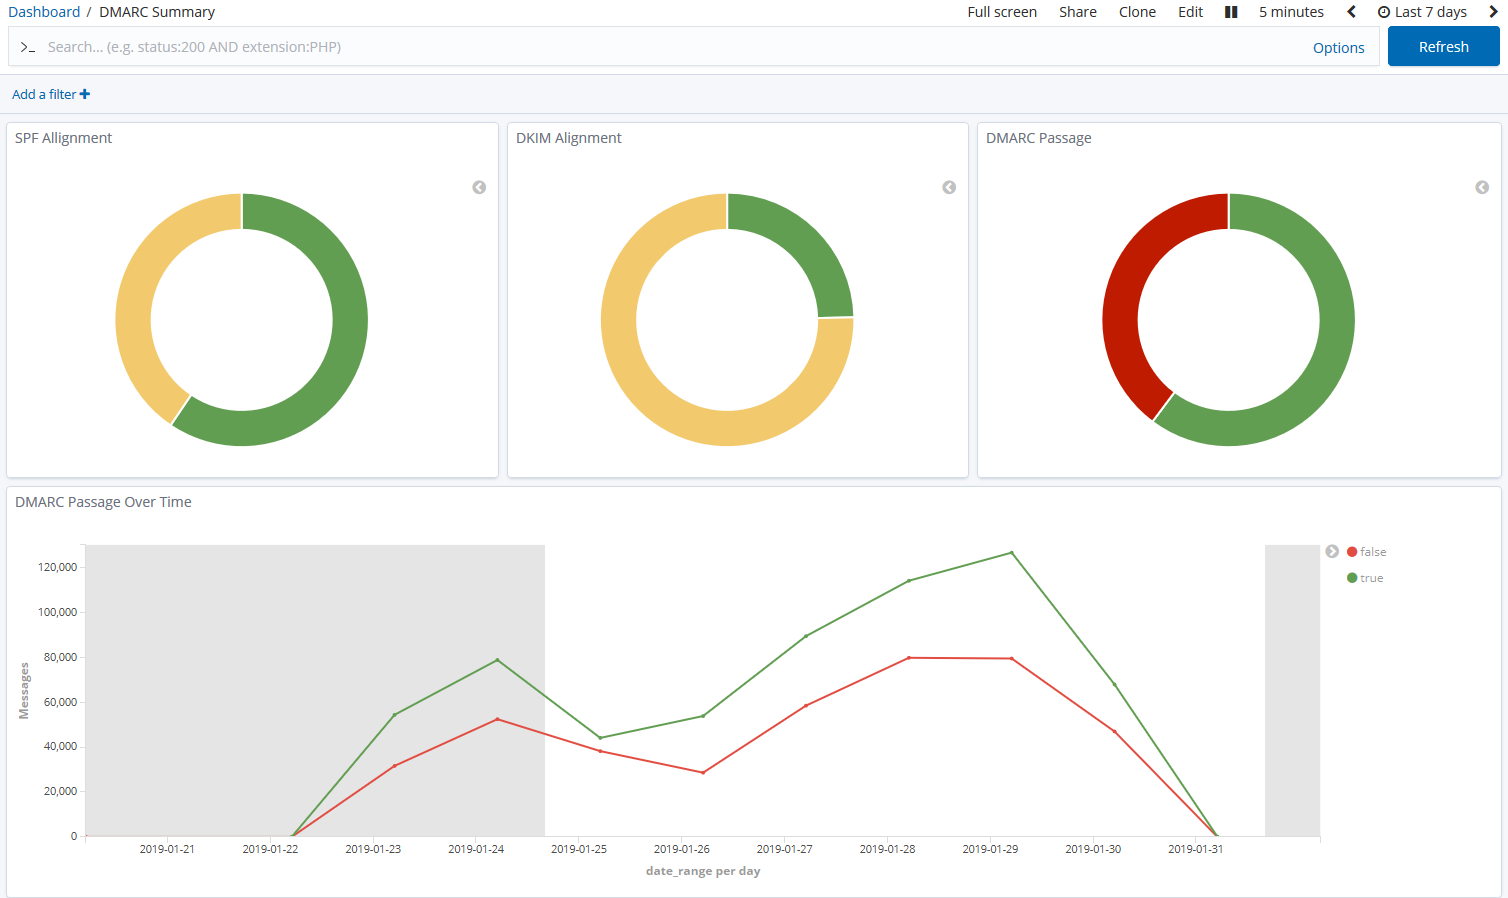 domainaware/parsedmarc
A Python package and CLI for parsing aggregate and forensic DMARC reports
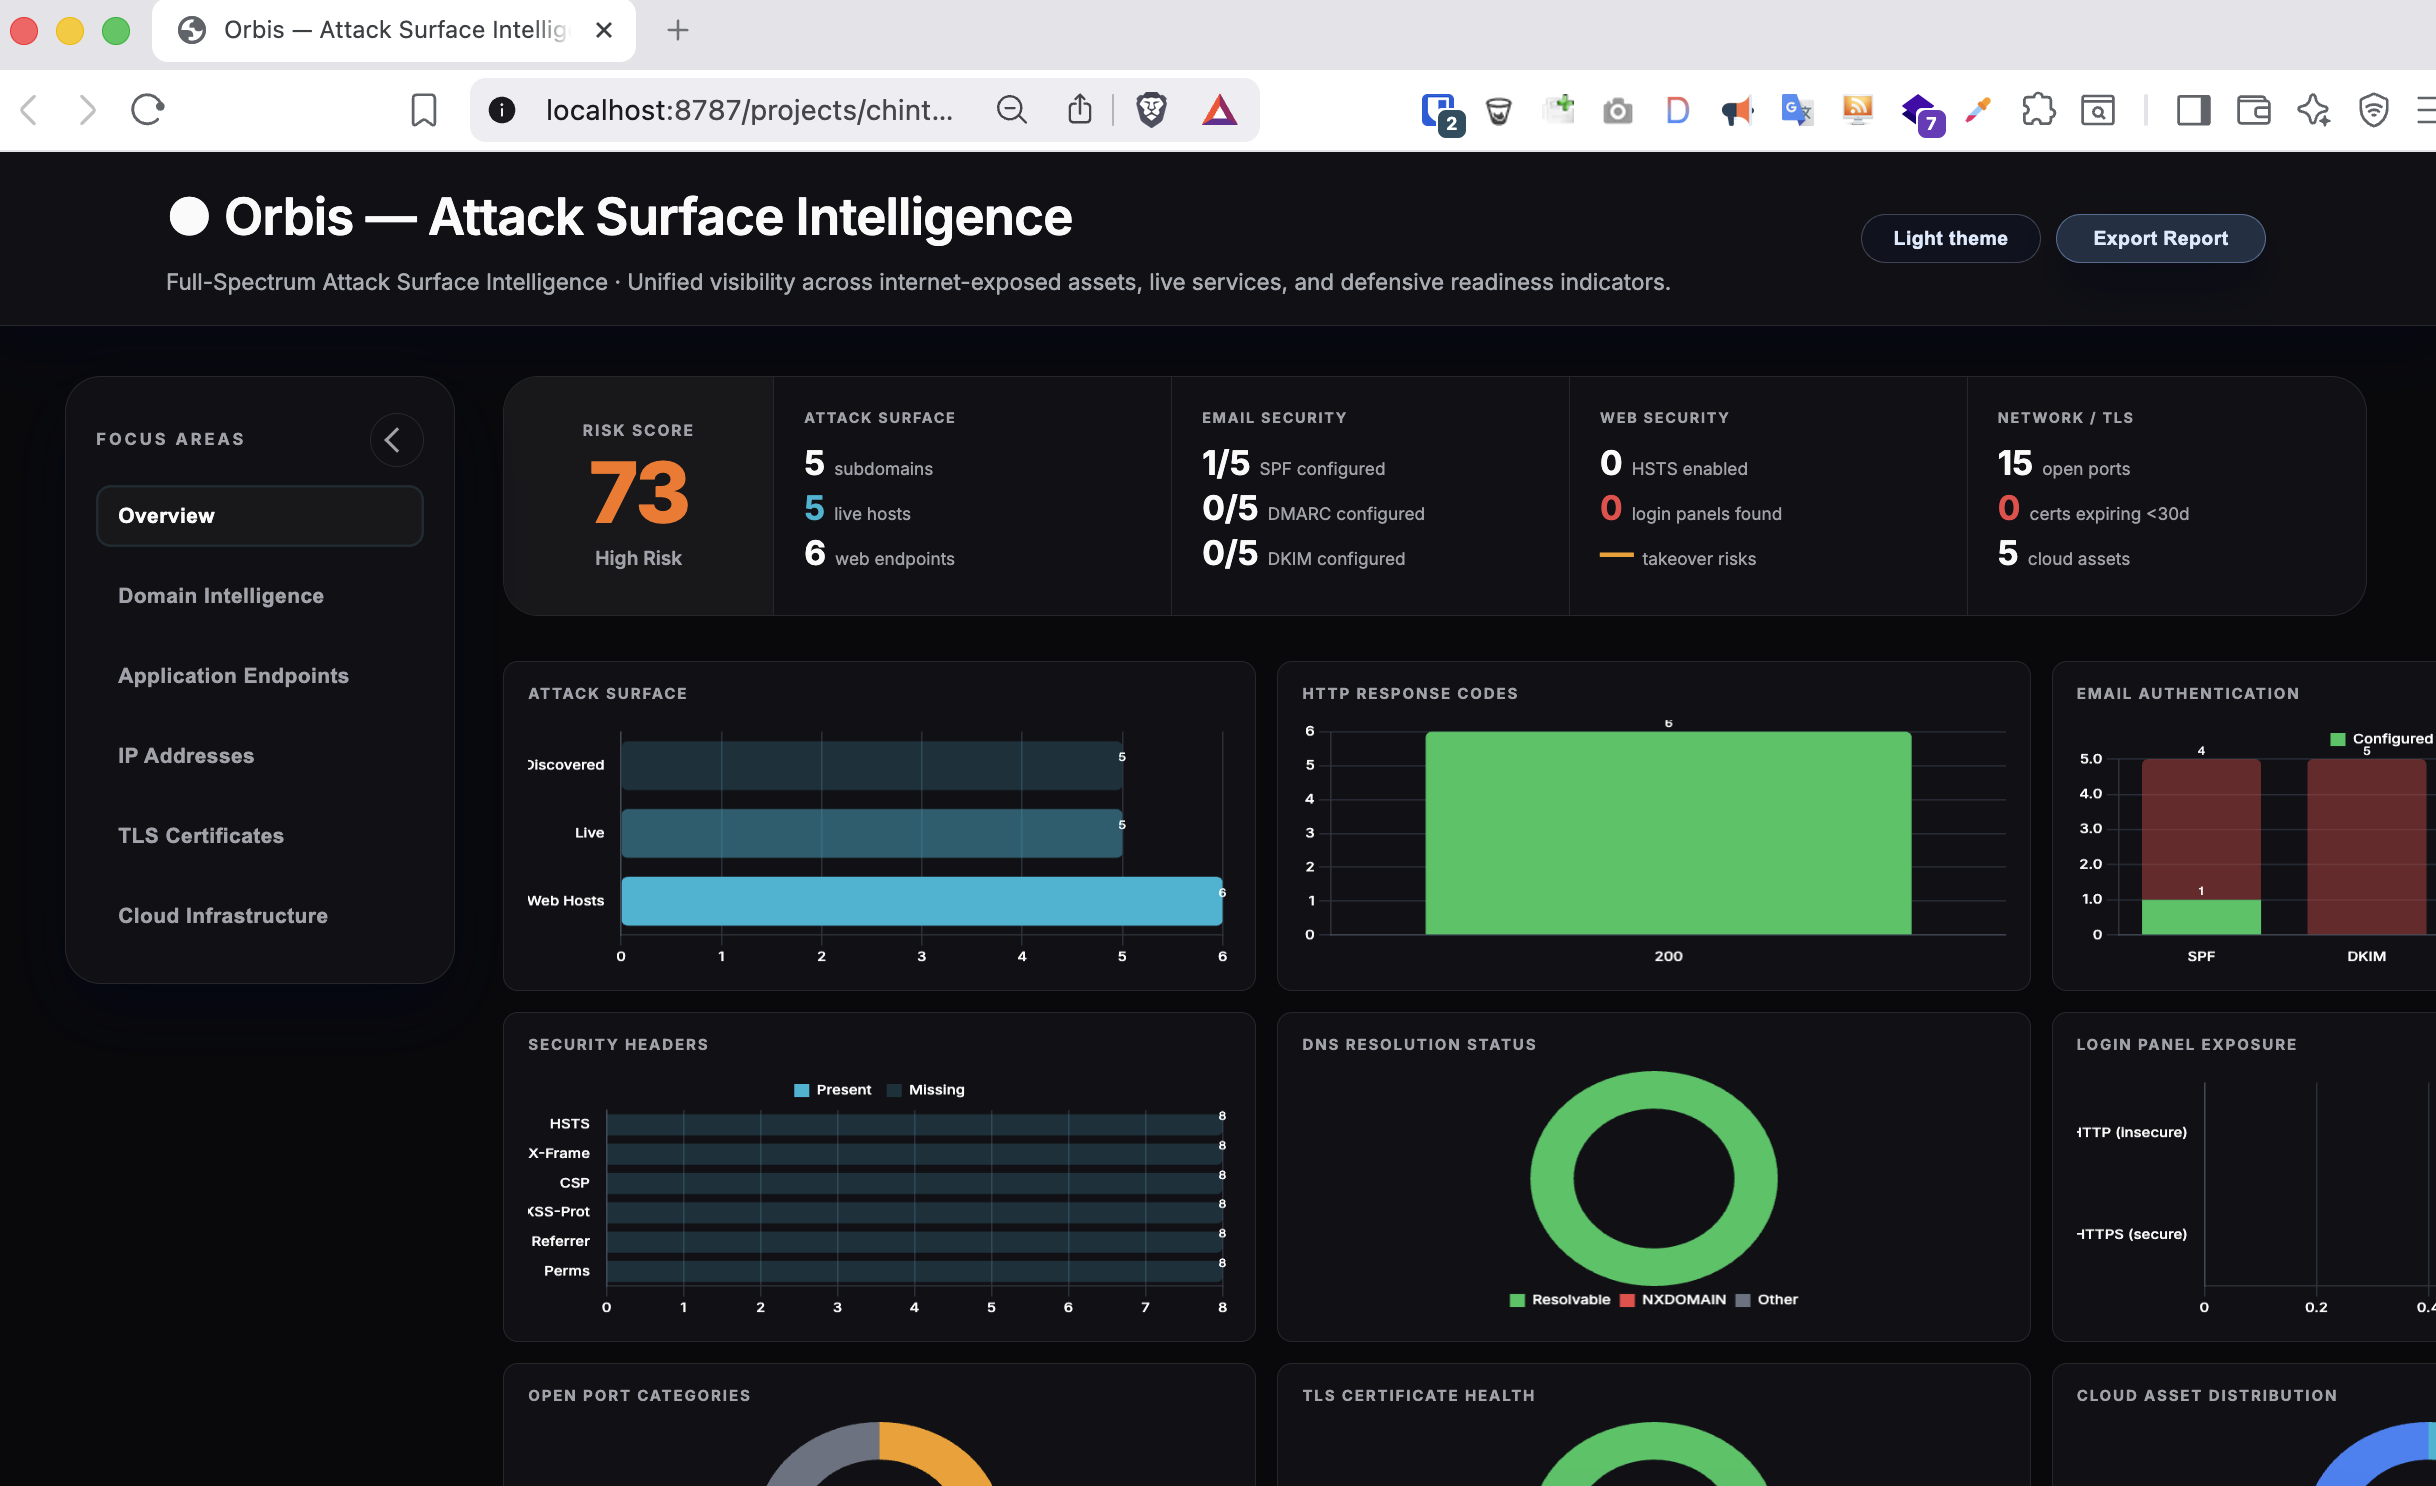 iamthefrogy/frogy2.0
Orbis is an full spectrum automated external attack surface intelligent toolkit.

 lissy93/awesome-privacy
🦄 A curated list of privacy & security-focused software and services
 joda32/yowie
Finds the SaaS services an organisation subscribes to, using only externally observable data. Built for shadow IT discovery.
 logisek/azureadenumeration
Microsoft Entra ID (Azure AD) Unauthenticated Enumeration
 osquery/osquery
SQL powered operating system instrumentation, monitoring, and analytics.
 v4d1/spoofthatmail
Bash script to check if a domain or list of domains can be spoofed based in DMARC records
 synacktiv/aadoutsider-py
Python3 rewrite of AsOutsider features of AADInternals
 all3xj/fixing-google-secops-detections
Tuning and refactoring Google Chronicle Curated Detections to eliminate alert fatigue and fix logic gaps/bugs.