

area51
 thoropass-public/area51
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
api-security-testingcloud-securityemail-security+4
7
thoropass-public/area51The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 jishino567/cve-2026-73570
Python PoC for CVE-2026-73570, an SMTP command injection in Zimbra. Sends malformed RCPT TO payloads to trigger shell command execution via…
 raikia/fiercephish
FiercePhish is a full-fledged phishing framework to manage all phishing engagements. It allows you to track separate phishing campaigns, schedule…
 qsecure-labs/overlord
Python-based CLI for automated red team infrastructure deployment on AWS and Digital Ocean, with modular support for C2, email servers, HTTP…
 0nyx-my7h/cve-2025-43920
PoC and technical write-up for CVE-2025-43920, a remote command injection in GNU Mailman 2.1.39's external archiver allowing unauthenticated code…
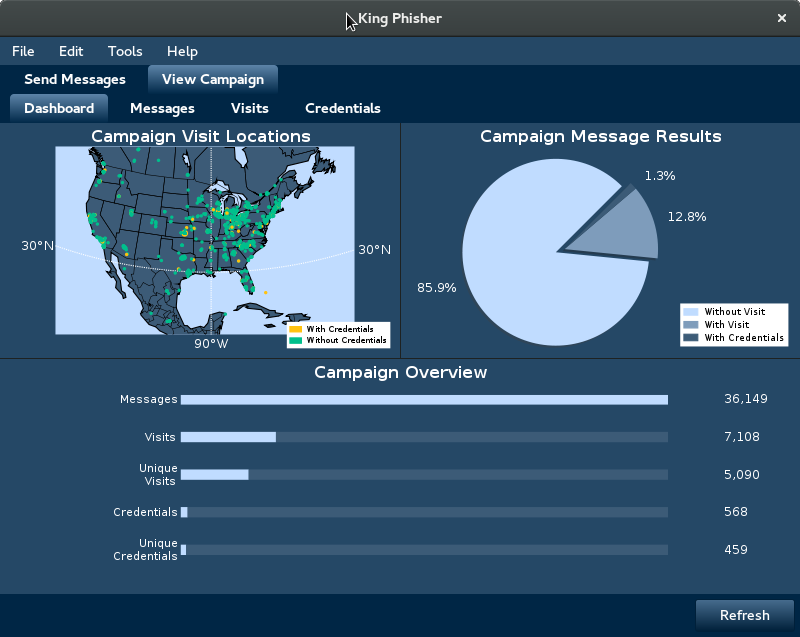 crimsonforge-io/king-phisher
Simulate realistic phishing campaigns with credential harvesting, email tracking, and landing page cloning for security awareness training and…
 hainhc/cve-2026-73570
Proof-of-concept exploit for CVE-2026-73570, an unauthenticated OS command injection in Zimbra Collaboration Suite via zimbra-snmp log injection,…
 rxerium/cve-2024-39929
Detection method for Exim vulnerability CVE-2024-39929
 biutrap/cve-2026-73570
Proof-of-concept exploit for CVE-2026-73570, demonstrating SMTP command injection via crafted RCPT TO header to trigger service status changes.
 mattkeeley/spoofy
Bulk domain spoofability checker using authoritative SPF and DMARC record analysis with custom, real-world tested spoof logic and optional DKIM…
 bl4ckmamb4/openrelaymagic
Tool to find SMTP servers vulnerable to open relay
 0xblackash/cve-2026-28289
CVE-2026-28289
 eeenvik1/cve-2023-51764
Proof-of-concept exploit for CVE-2023-51764 SMTP smuggling vulnerability in Postfix, enabling email spoofing and message injection via crafted SMTP…
 jb-selfcompany/tyr
True P2P Email on top of Yggdrasil Network for Android
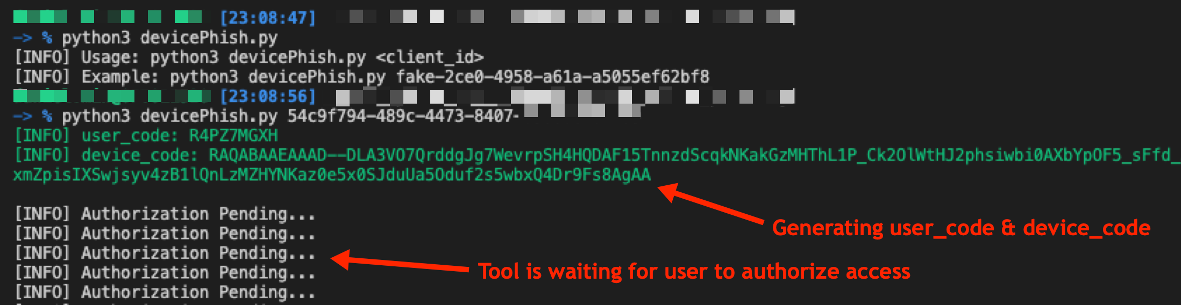 optiv/microsoft365_devicephish
A proof-of-concept script to conduct a phishing attack abusing Microsoft 365 OAuth Authorization Flow
 horkimhab/cve-2026-73570
Proof-of-concept exploit for an actively exploited Zimbra Collaboration Suite vulnerability, designed for authorized penetration testing and…
 materaj2/cve-2026-45185-detection-script
These detection scripts are property of the SECPlayground Platform. Two safe detection scripts. Neither drives the close_notify-mid-BDAT trigger, so…