
Consensus-OSINT
🔎 Username, email & phone OSINT — 9,700+ lookup checks from 19 projects, with profile enrichment, bulk searches, evidence graphs and expert-reviewed…

🔎 Username, email & phone OSINT — 9,700+ lookup checks from 19 projects, with profile enrichment, bulk searches, evidence graphs and expert-reviewed…

IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…

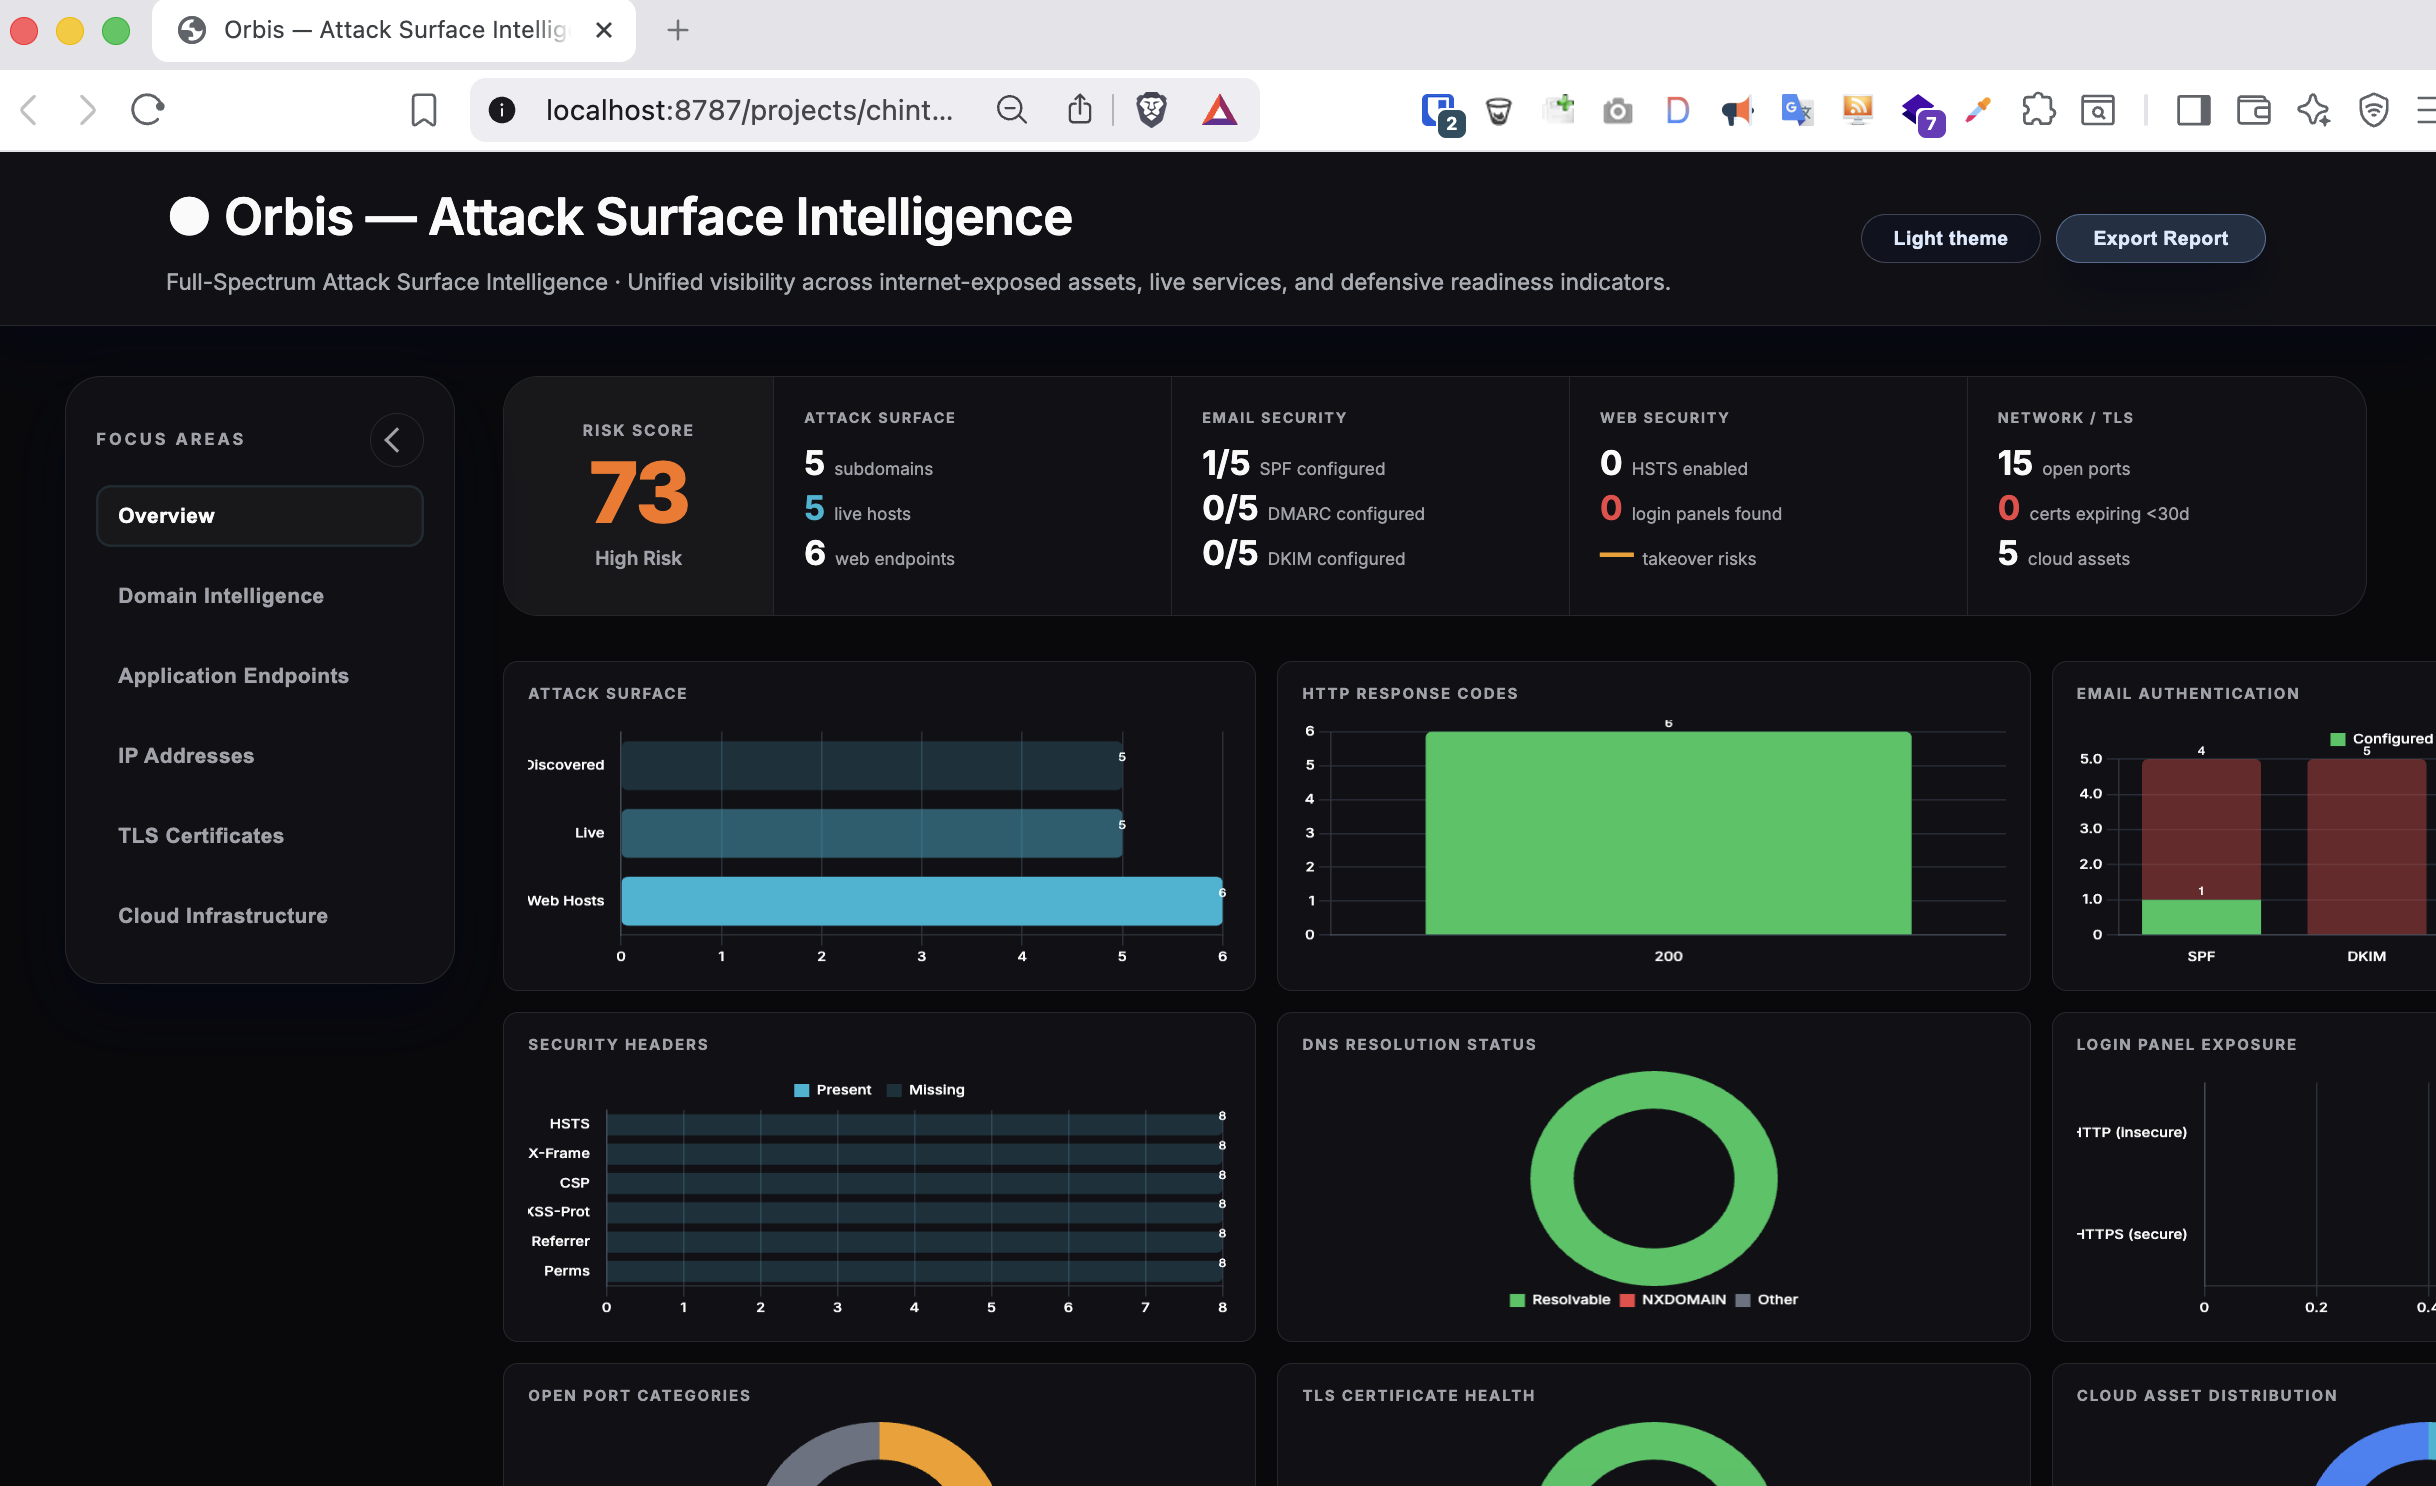
Orbis is an full spectrum automated external attack surface intelligent toolkit.

🦄 A curated list of privacy & security-focused software and services

SQL powered operating system instrumentation, monitoring, and analytics.

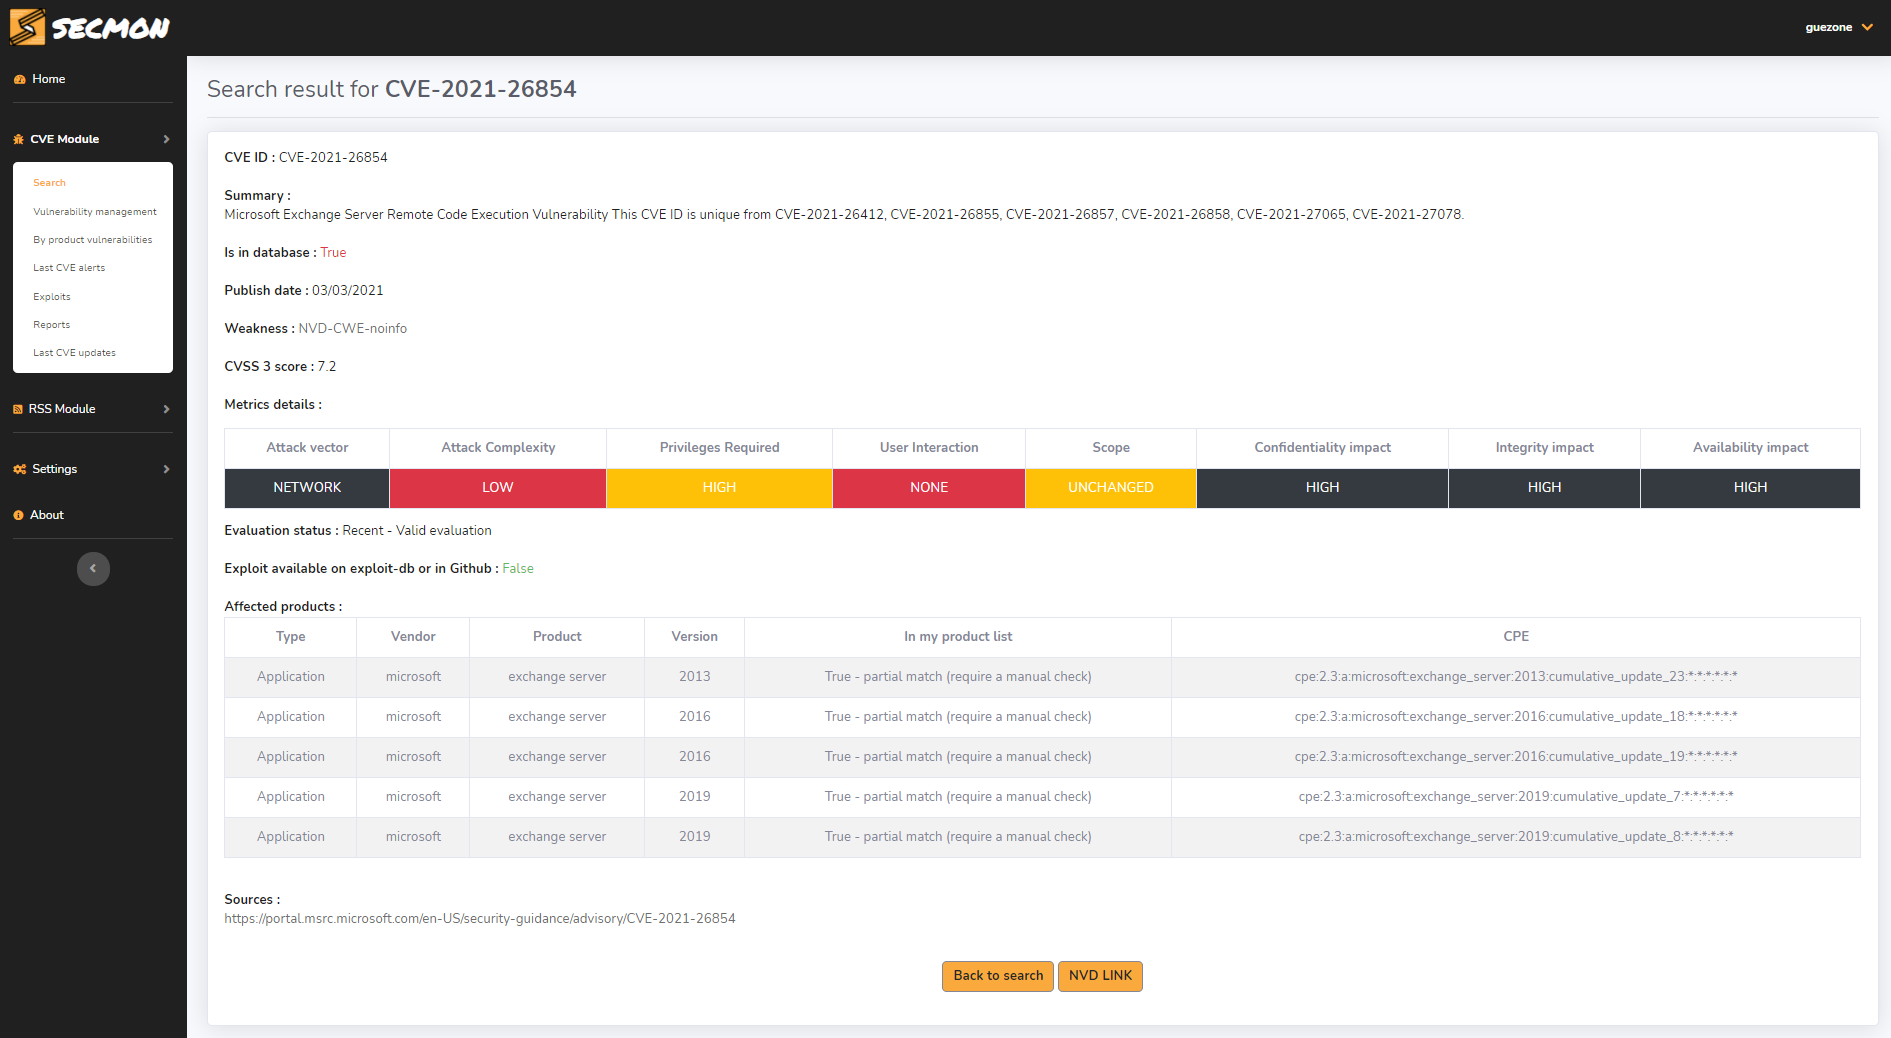
SECMON is a web-based tool for the automation of infosec watching and vulnerability management with a web interface.

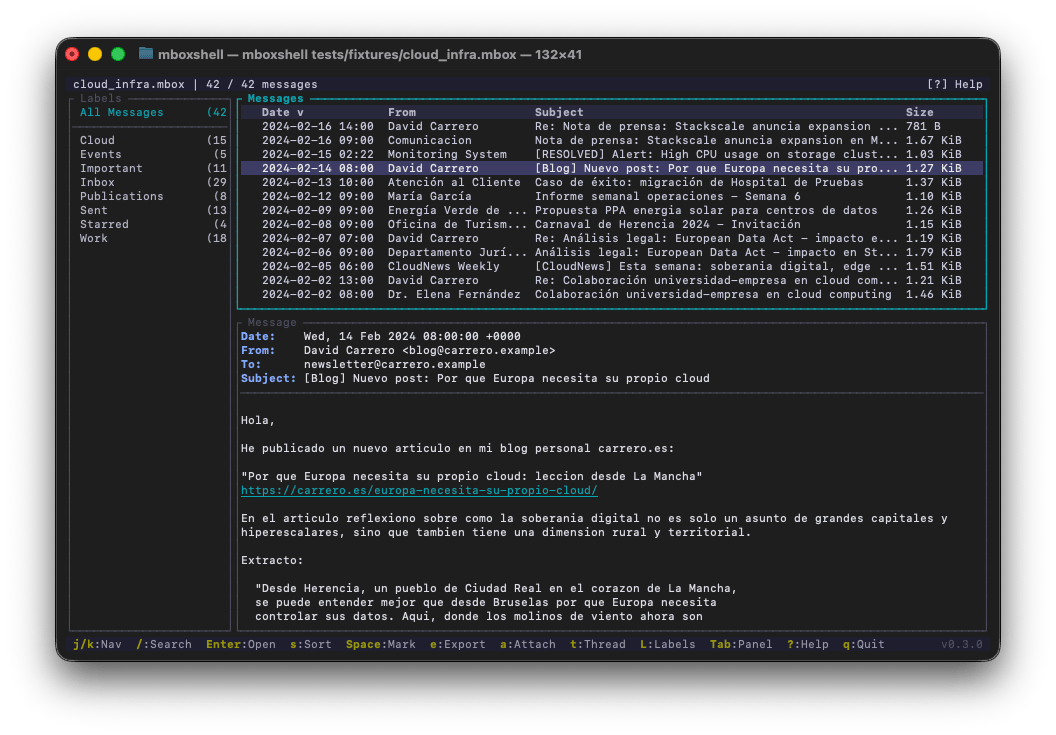
mboxShell. Fast terminal viewer for MBOX files of any size. Open, search and export emails from Gmail Takeout backups (50GB+) without loading them…

SOC336 - Windows OLE Zero-Click RCE Exploitation Detected (CVE-2025-21298) Walkthrough

A curated portfolio showcasing my SOC investigations, threat hunting projects, DFIR labs, detection engineering, technical blogs, and cybersecurity…

A tool to abuse Exchange services

PowerShell script to exploit CVE-2023-23397 by sending or saving malicious Outlook calendar invitations that trigger NTLM credential leakage via the…

Collection of offensive red team scripts including process termination, SPF bypass for phishing, password spraying, and ColdFusion password…

Purple team project exploiting CVE-2023-23397 Outlook NTLM leak with phishing delivery, plus Sigma/Wazuh detections mapped to MITRE ATT&CK for the…

PowerShell-based detection and remediation toolkit for CVE-2025-32711 (EchoLeak), a critical zero-click AI command injection vulnerability in…

LetsDefend SOC336 case study on CVE-2025-21298

Um estudo de caso do CVE-2024-21413. Usado como parâmetro a sala do TryHackMe Moniker Link (CVE-2024-21413). Feito edições com claude code no exploit.

An automated attack chain based on CVE-2022-30190, 163 email backdoor, and image steganography.

Two POCs I created for the CVE-2023-23397 Outlook NTLM vulnerability, to be used internally.