
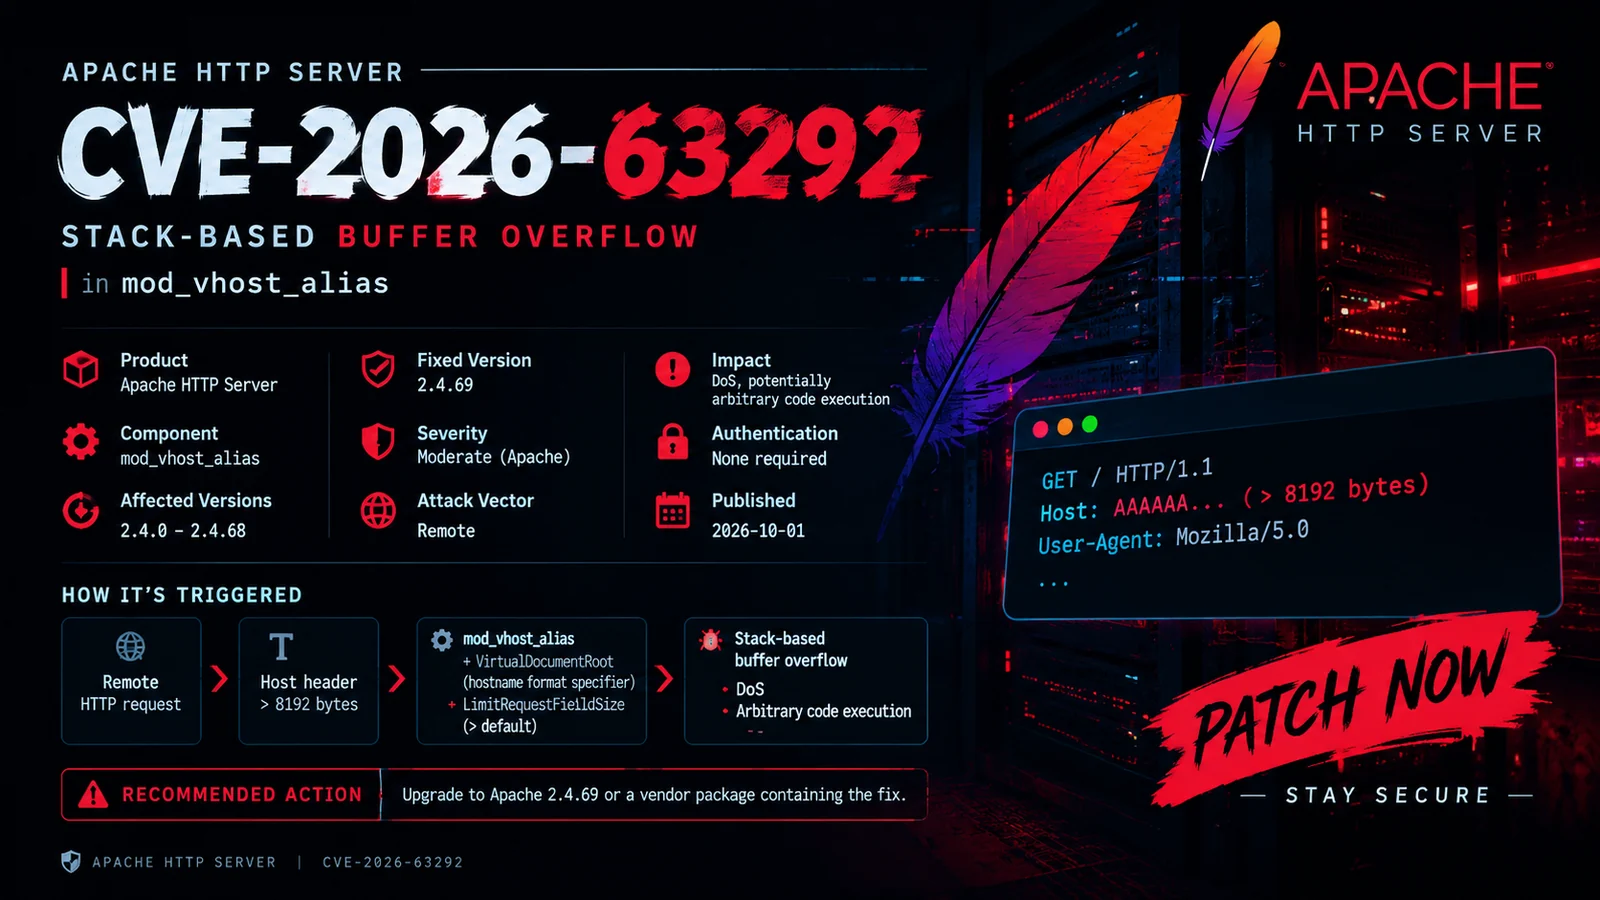
 0xblackash/cve-2026-63292
Documents CVE-2026-63292, a stack-based buffer overflow in Apache mod_vhost_alias, with affected versions, safe version and configuration checks, and…
 cedricbonhomme/stegano
A pure Python steganography module.
 xbufu/adlab
Custom PowerShell module to setup an Active Directory lab environment to practice penetration testing.
 blacksnufkin/novaldr
Threadless Module Stomping In Rust with some features (In memory of those murdered in the Nova party massacre)
 duc-nt/cve-2020-6287-exploit
PoC for CVE-2020-6287 The PoC in python for add user only, no administrator permission set. Inspired by @zeroSteiner from metasploit. Original…
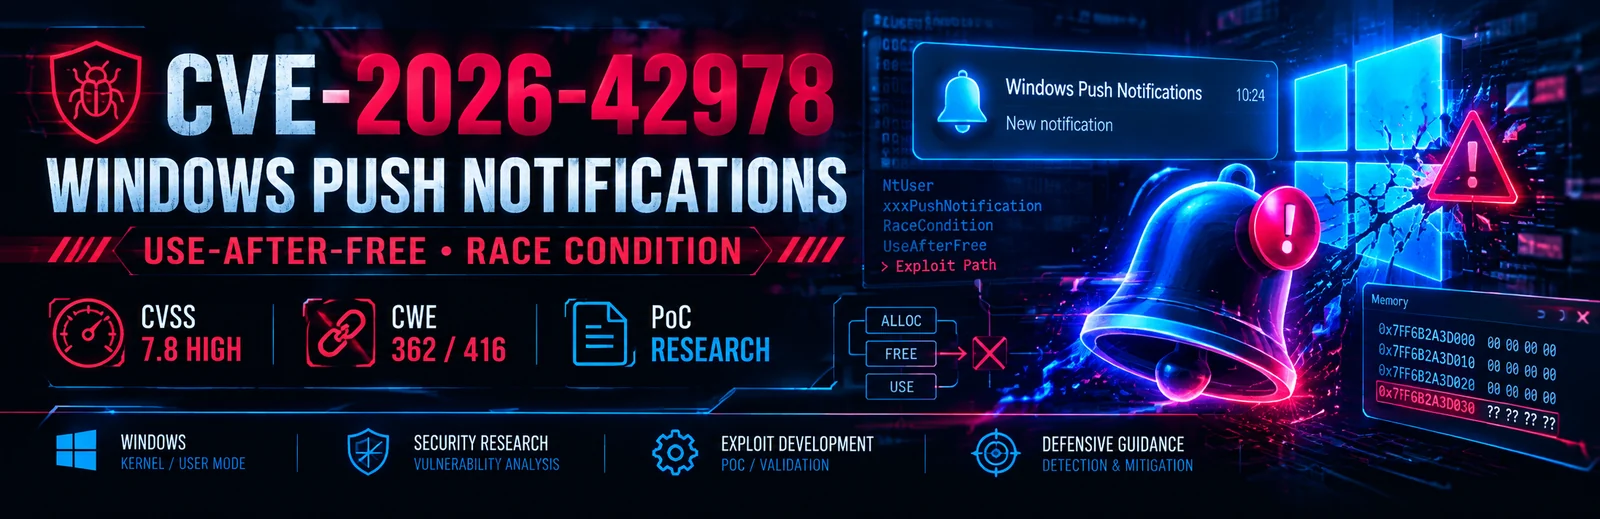 syntaxmethod/cve-2026-42978-poc-research
CVE-2026-42978 Windows Push Notifications (WpnService) Use-After-Free & Race Condition PoC research, diagnostic scanner, and security audit module…
 7h30th3r0n3/cve-2026-9082-drupal-poc
Drupal Core PostgreSQL SQL Injection PoC - CVE-2026-9082. Ethical PoC for the Drupal vulnerability allowing anonymous SQL injection through the…
 kaandemir993/advanced-loader-reverse-engineering
"In-depth reverse engineering analysis of an advanced multi-phase loader targeting Shellhost.exe, amsi.dll, mstscax.dll, and clbcatq.dll using module…
 zerodayvpn/cve-2026-41089-netlogon
🛡️ Official AI Security Tool diagnostic module for CVE-2026-41089 (Windows Netlogon Stack Buffer Overflow RCE). Features technical writeup, attack…
 ochebotar/copy-fail-cve-2026-31431-detection-probe
Safe detection tooling for CVE-2026-31431 "Copy Fail" and CVE-2026-43284 "Dirty Frag" — a local privilege escalation in the Linux kernel's algif_aead…
 g0vguy/cve-2025-61922-poc
A simple, educational proof-of-concept script demonstrating the zero-click account takeover vulnerability in the PrestaShop Checkout module…
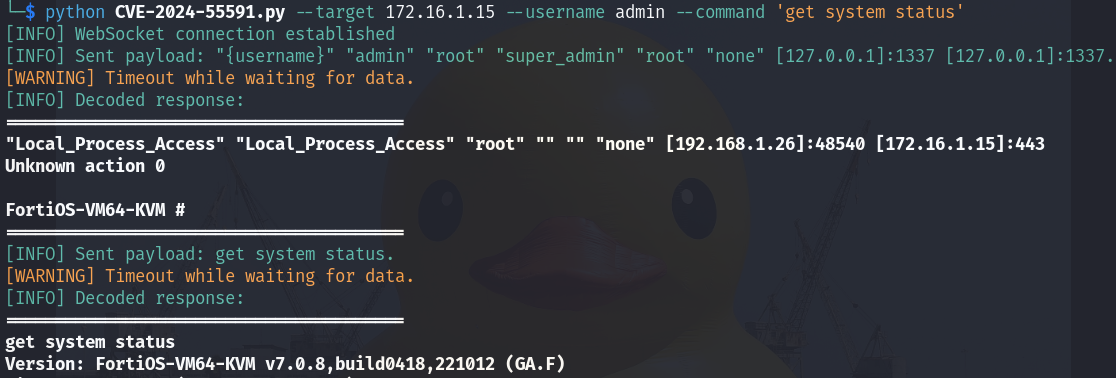 virus-or-not/cve-2024-55591
An Authentication Bypass Using an Alternate Path or Channel vulnerability [CWE-288] affecting FortiOS and FortiProxy may allow a remote attacker to…
 lavclash75/cve-2021-36394-pre-auth-rce-in-moodle
Pre-authentication remote code execution exploit targeting Moodle's Shibboleth authentication module. Includes Docker-based lab environment for…
 forced-request/rails-rce-cve-2016-0752
Proof-of-concept exploit for CVE-2016-0752, a remote code execution vulnerability in Ruby on Rails via dynamic render paths. Includes vulnerable app,…
 theatha/yara_for_config_extraction
Tutorial and source code for building a custom YARA module in C to extract malware configurations, with a practical Danabot example and reusable…
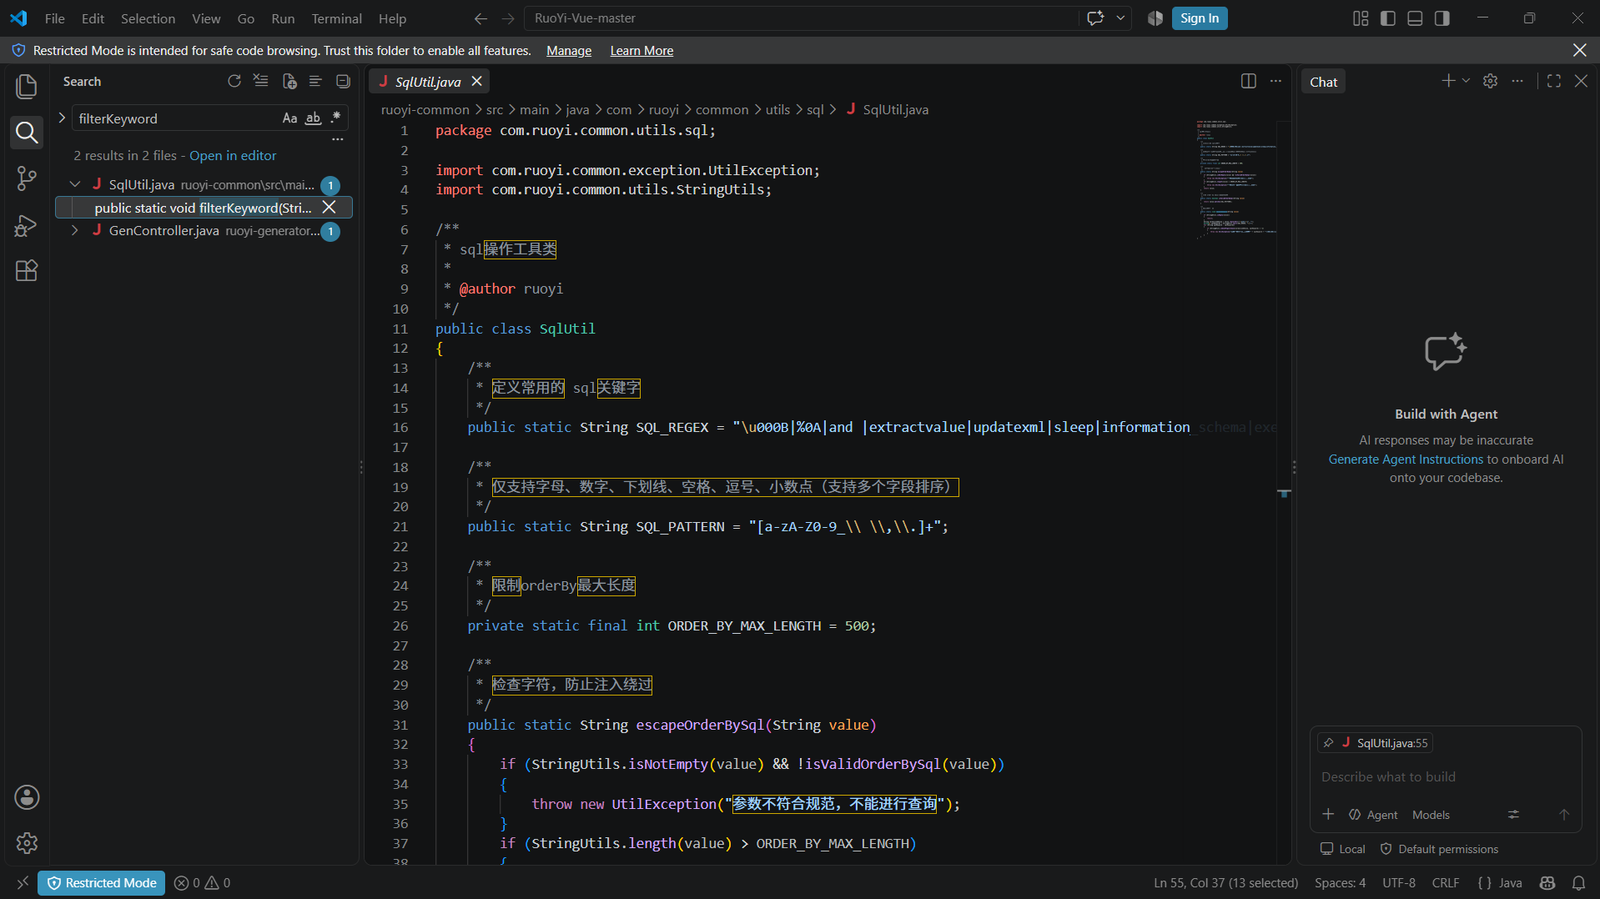 xs2024770/cve-2024-57521-ruoyi-sqli
Static code audit of CVE-2024-57521, an authenticated SQL injection in RuoYi-Vue's generator module, with source-to-sink analysis and a %0b filter…
 tea-on/cve-2023-41425-rce-wondercms-4.3.2
Automates creation and hosting of a JavaScript XSS payload to install a malicious theme module, triggering a reverse shell via Remote Code Execution…