perwendel__spark_CVE-2018-9159_2_7_2_fixed

Lightweight Java 8 web framework for building REST APIs and web applications, with built-in routing, static file serving, and template engine support.

Lightweight Java 8 web framework for building REST APIs and web applications, with built-in routing, static file serving, and template engine support.

Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.

Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…

Deliberately vulnerable microservices API designed for hands-on training in the OWASP API Security Top 10 risks, with built-in challenges and a…

Vulnerable REST API with OWASP top 10 vulnerabilities for security testing

Damn Vulnerable GraphQL Application is an intentionally vulnerable GraphQL service implementation designed for learning about and practising GraphQL…

An intentionally designed broken web application based on REST API.

AI-powered vulnerability scanner extension for Burp Suite with multi-provider support (Ollama, OpenAI, Claude, Gemini)

Open-source adversary emulation for AI agents and MCP servers.

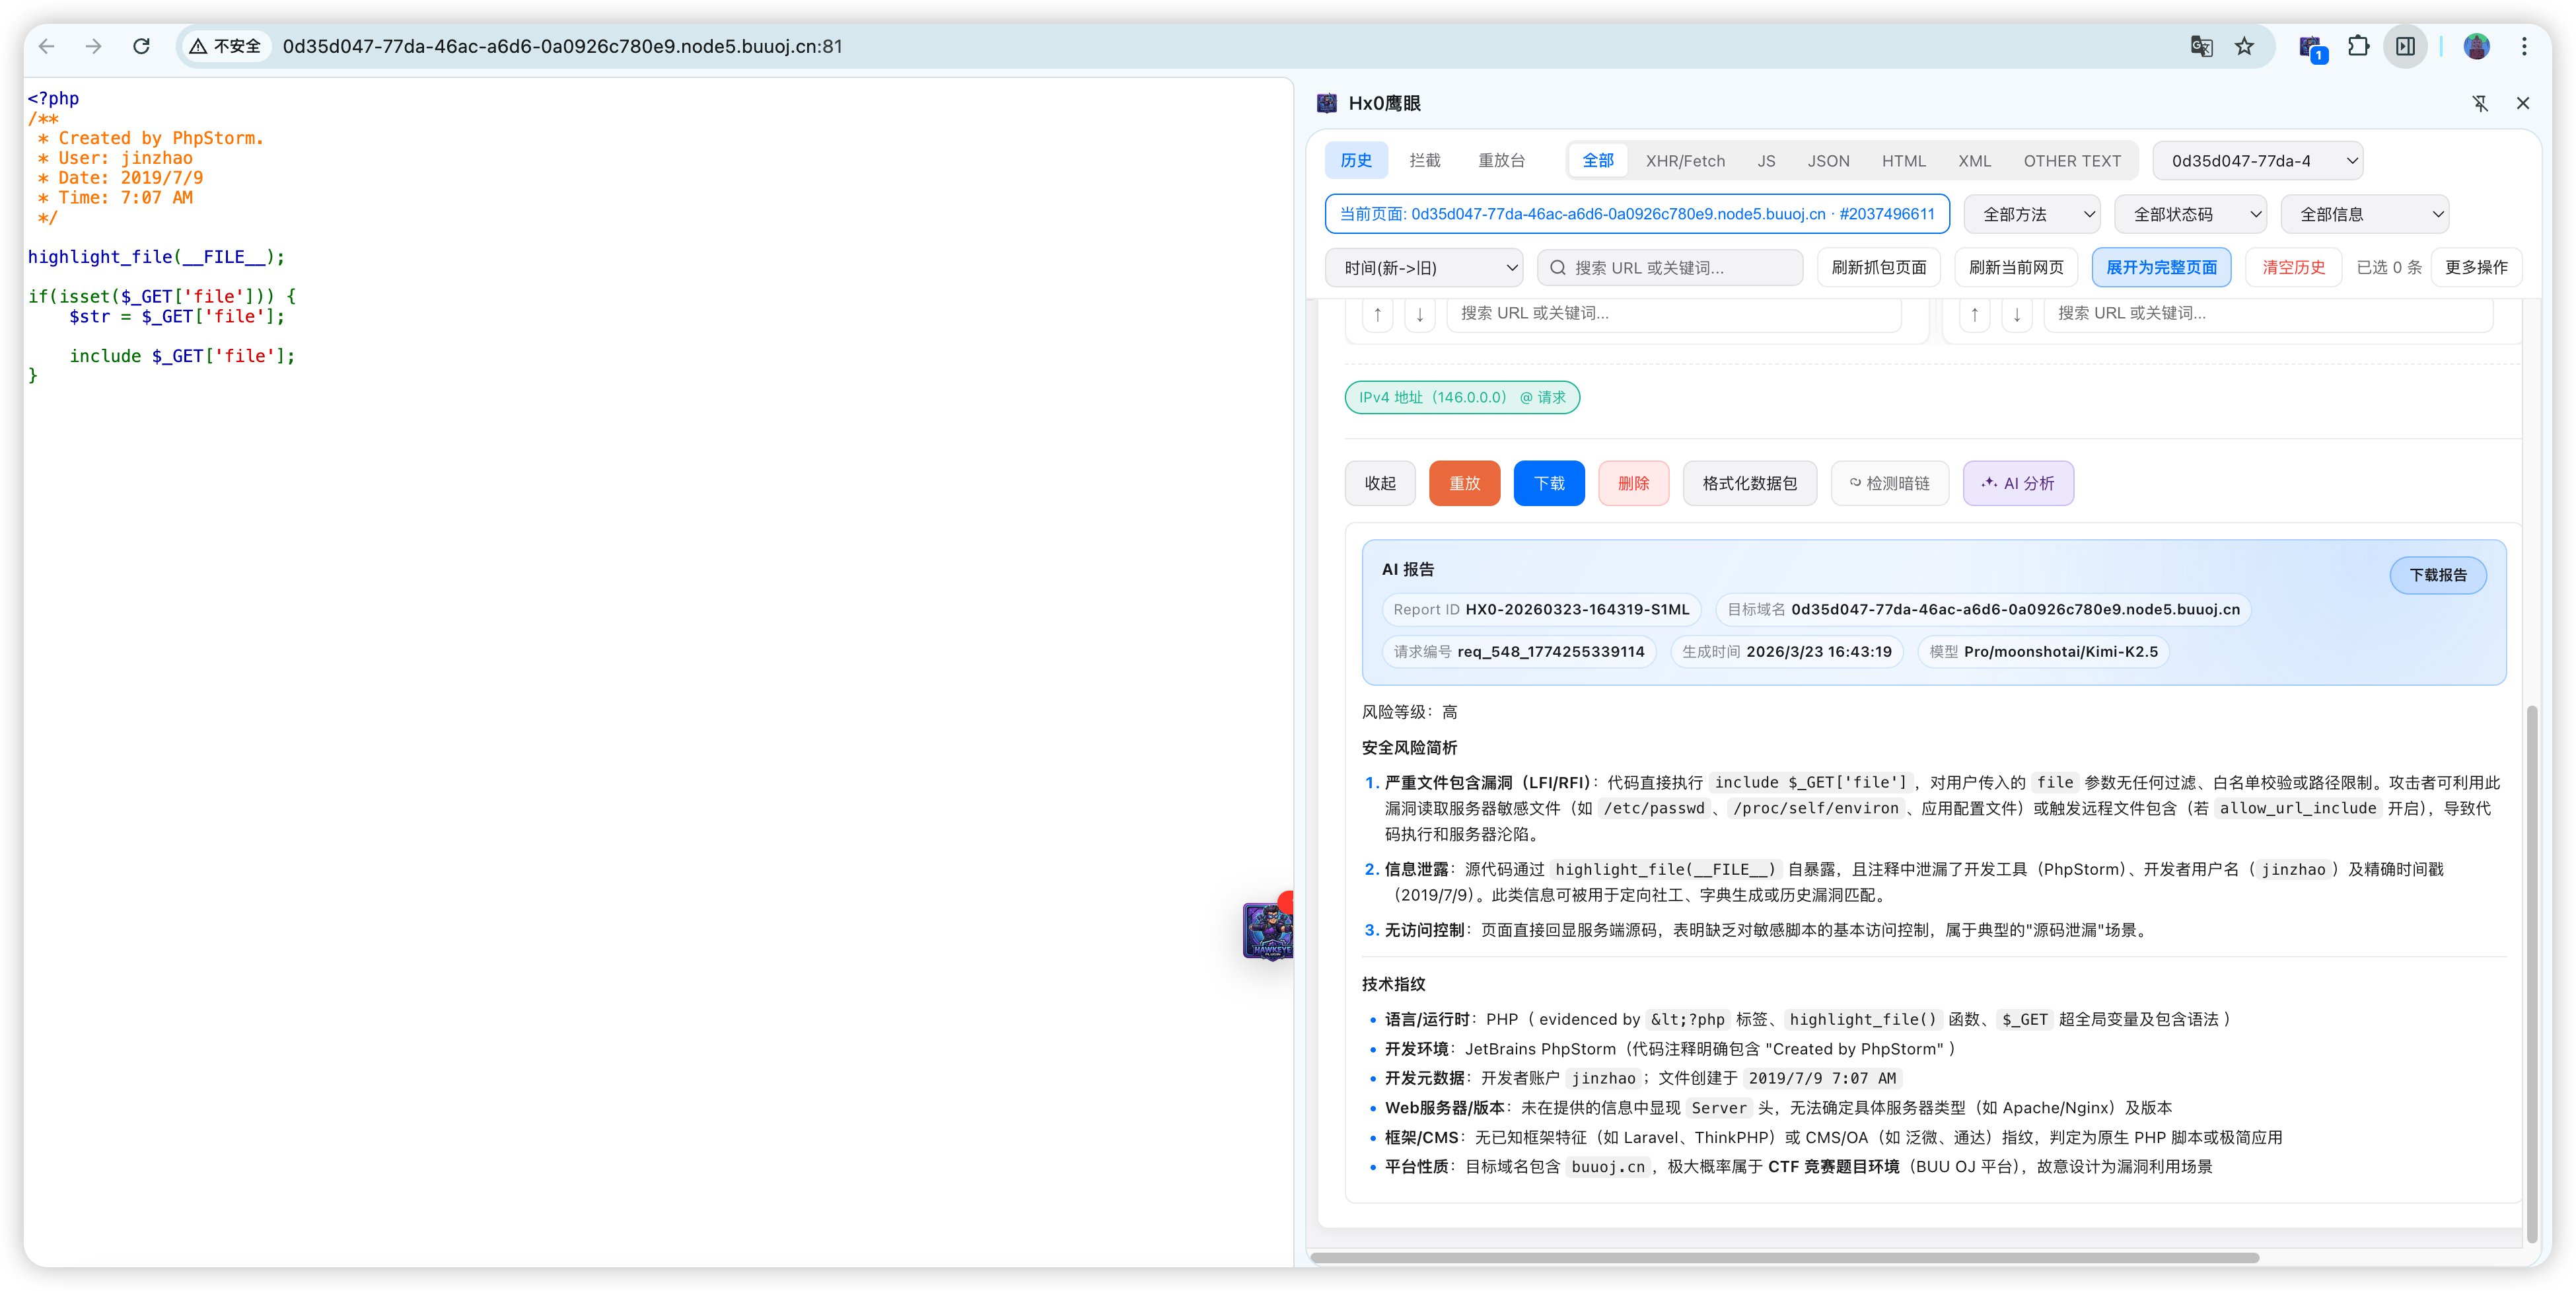
一个轻量级浏览器抓包与安全分析扩展,在浏览器侧边栏中即可完成抓包、拦截、修改、重放、规则检测与AI辅助分析的完整工作流。(A lightweight browser extension for traffic capture and security analysis, enabling…

Executable security regression testing for agentic applications and MCP-integrated systems.

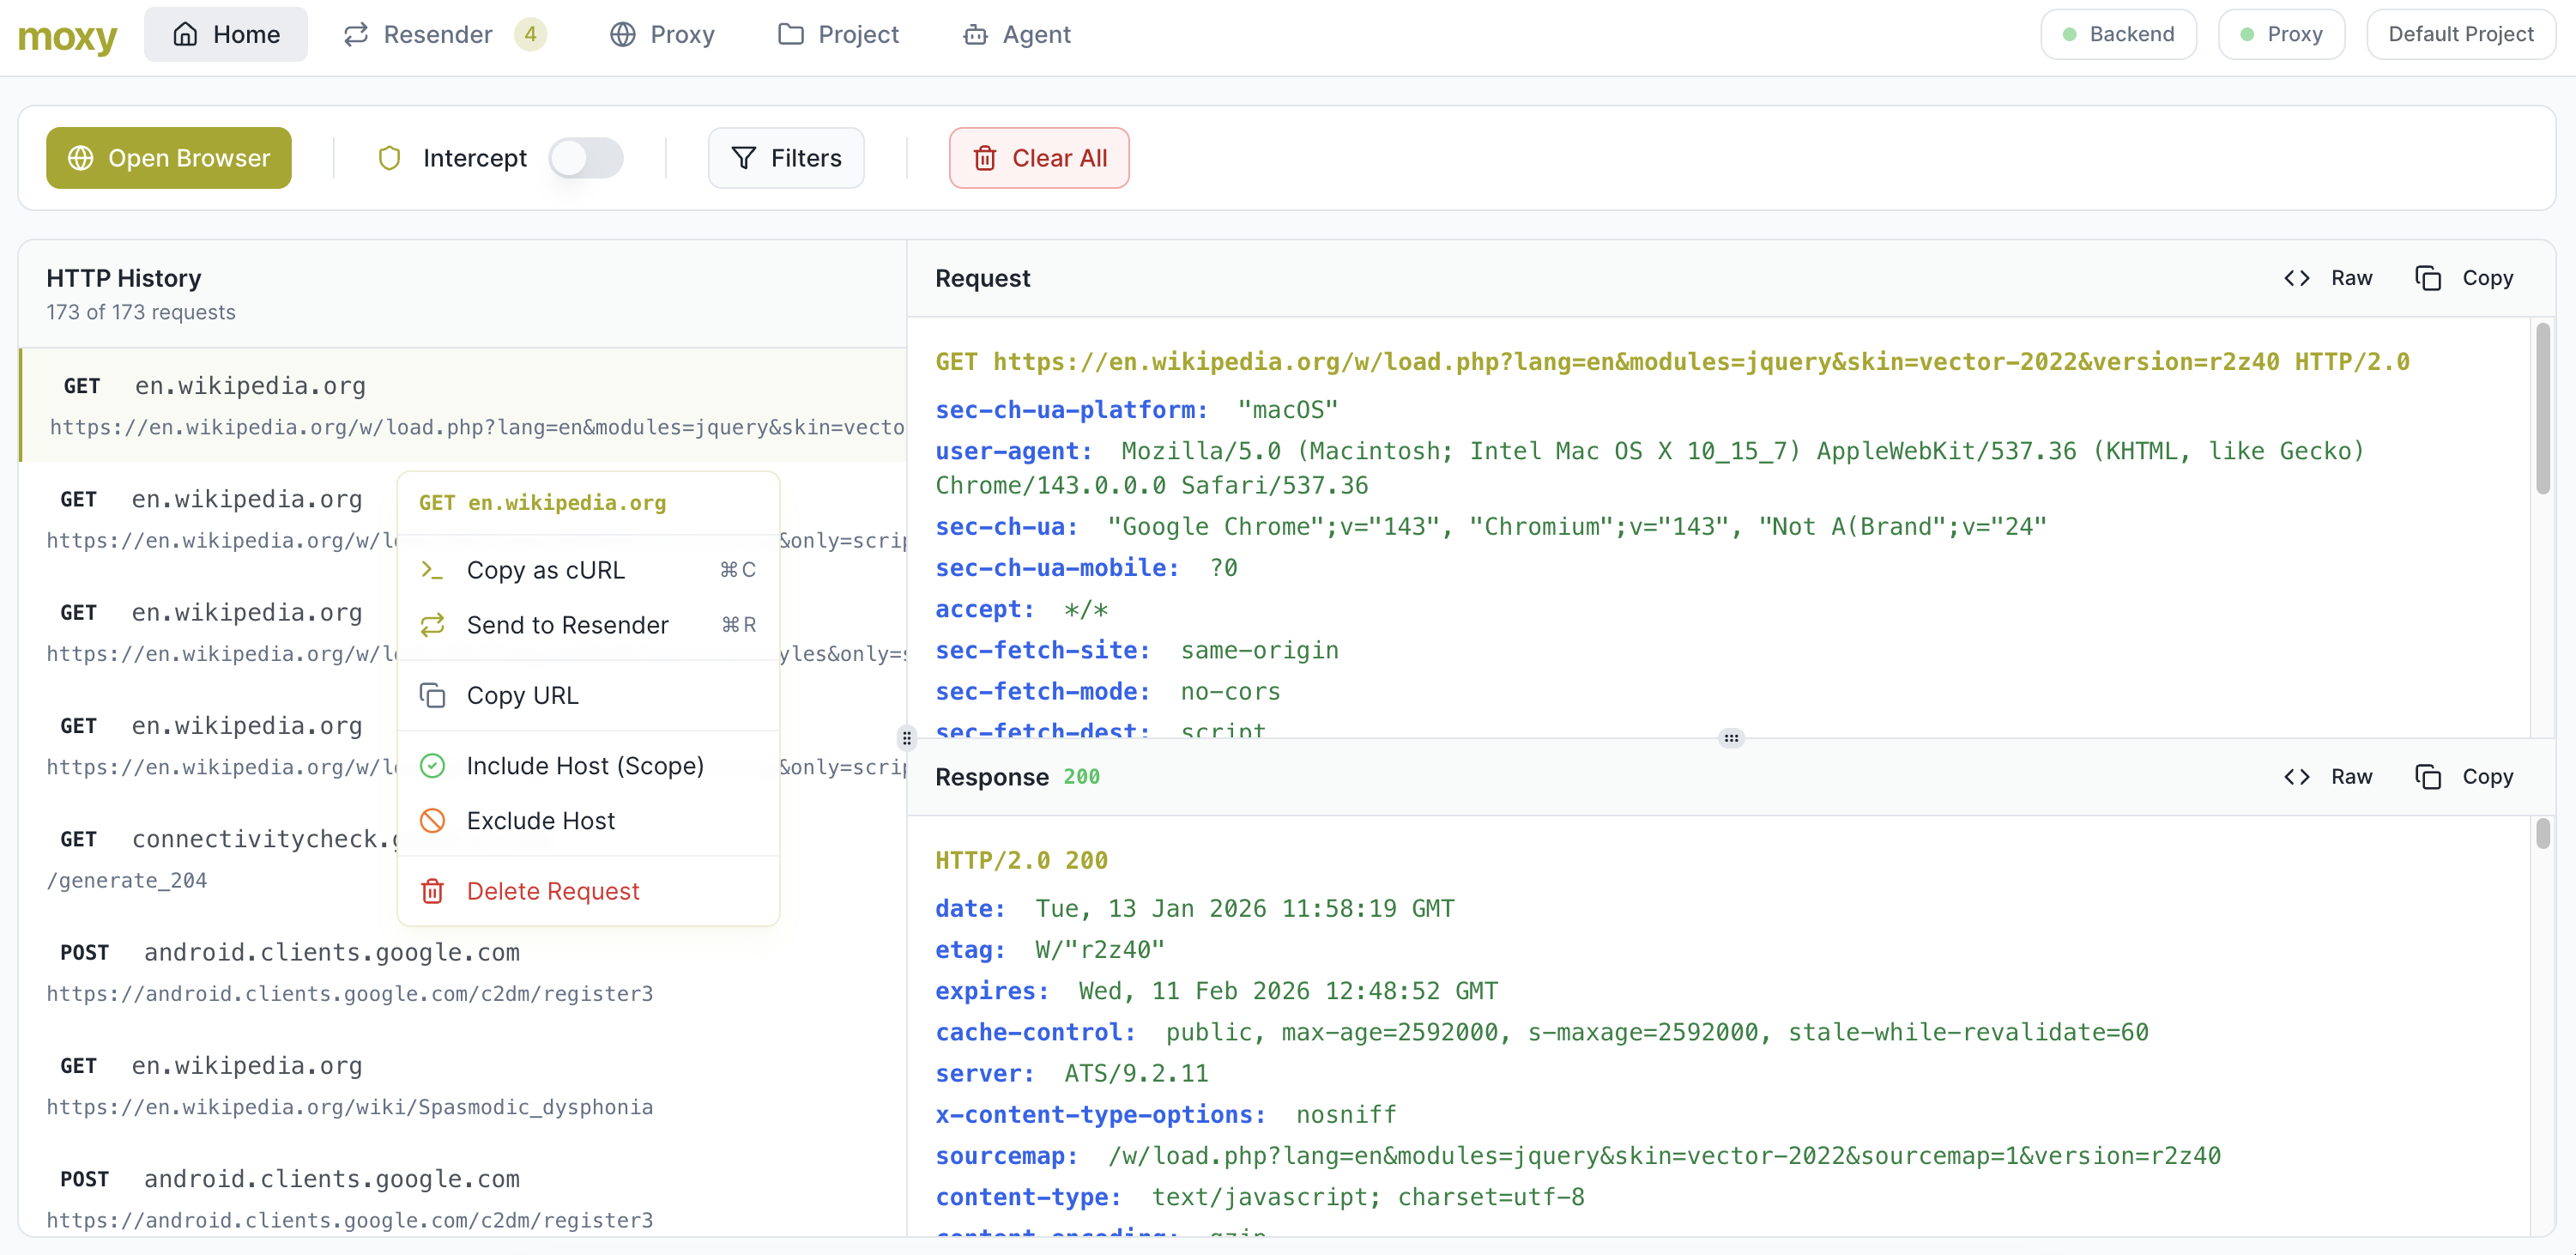
Moxy is an open-source DAST tool designed for modern web application security testing. It provides an easy-to-use interface with agentic capabilities…

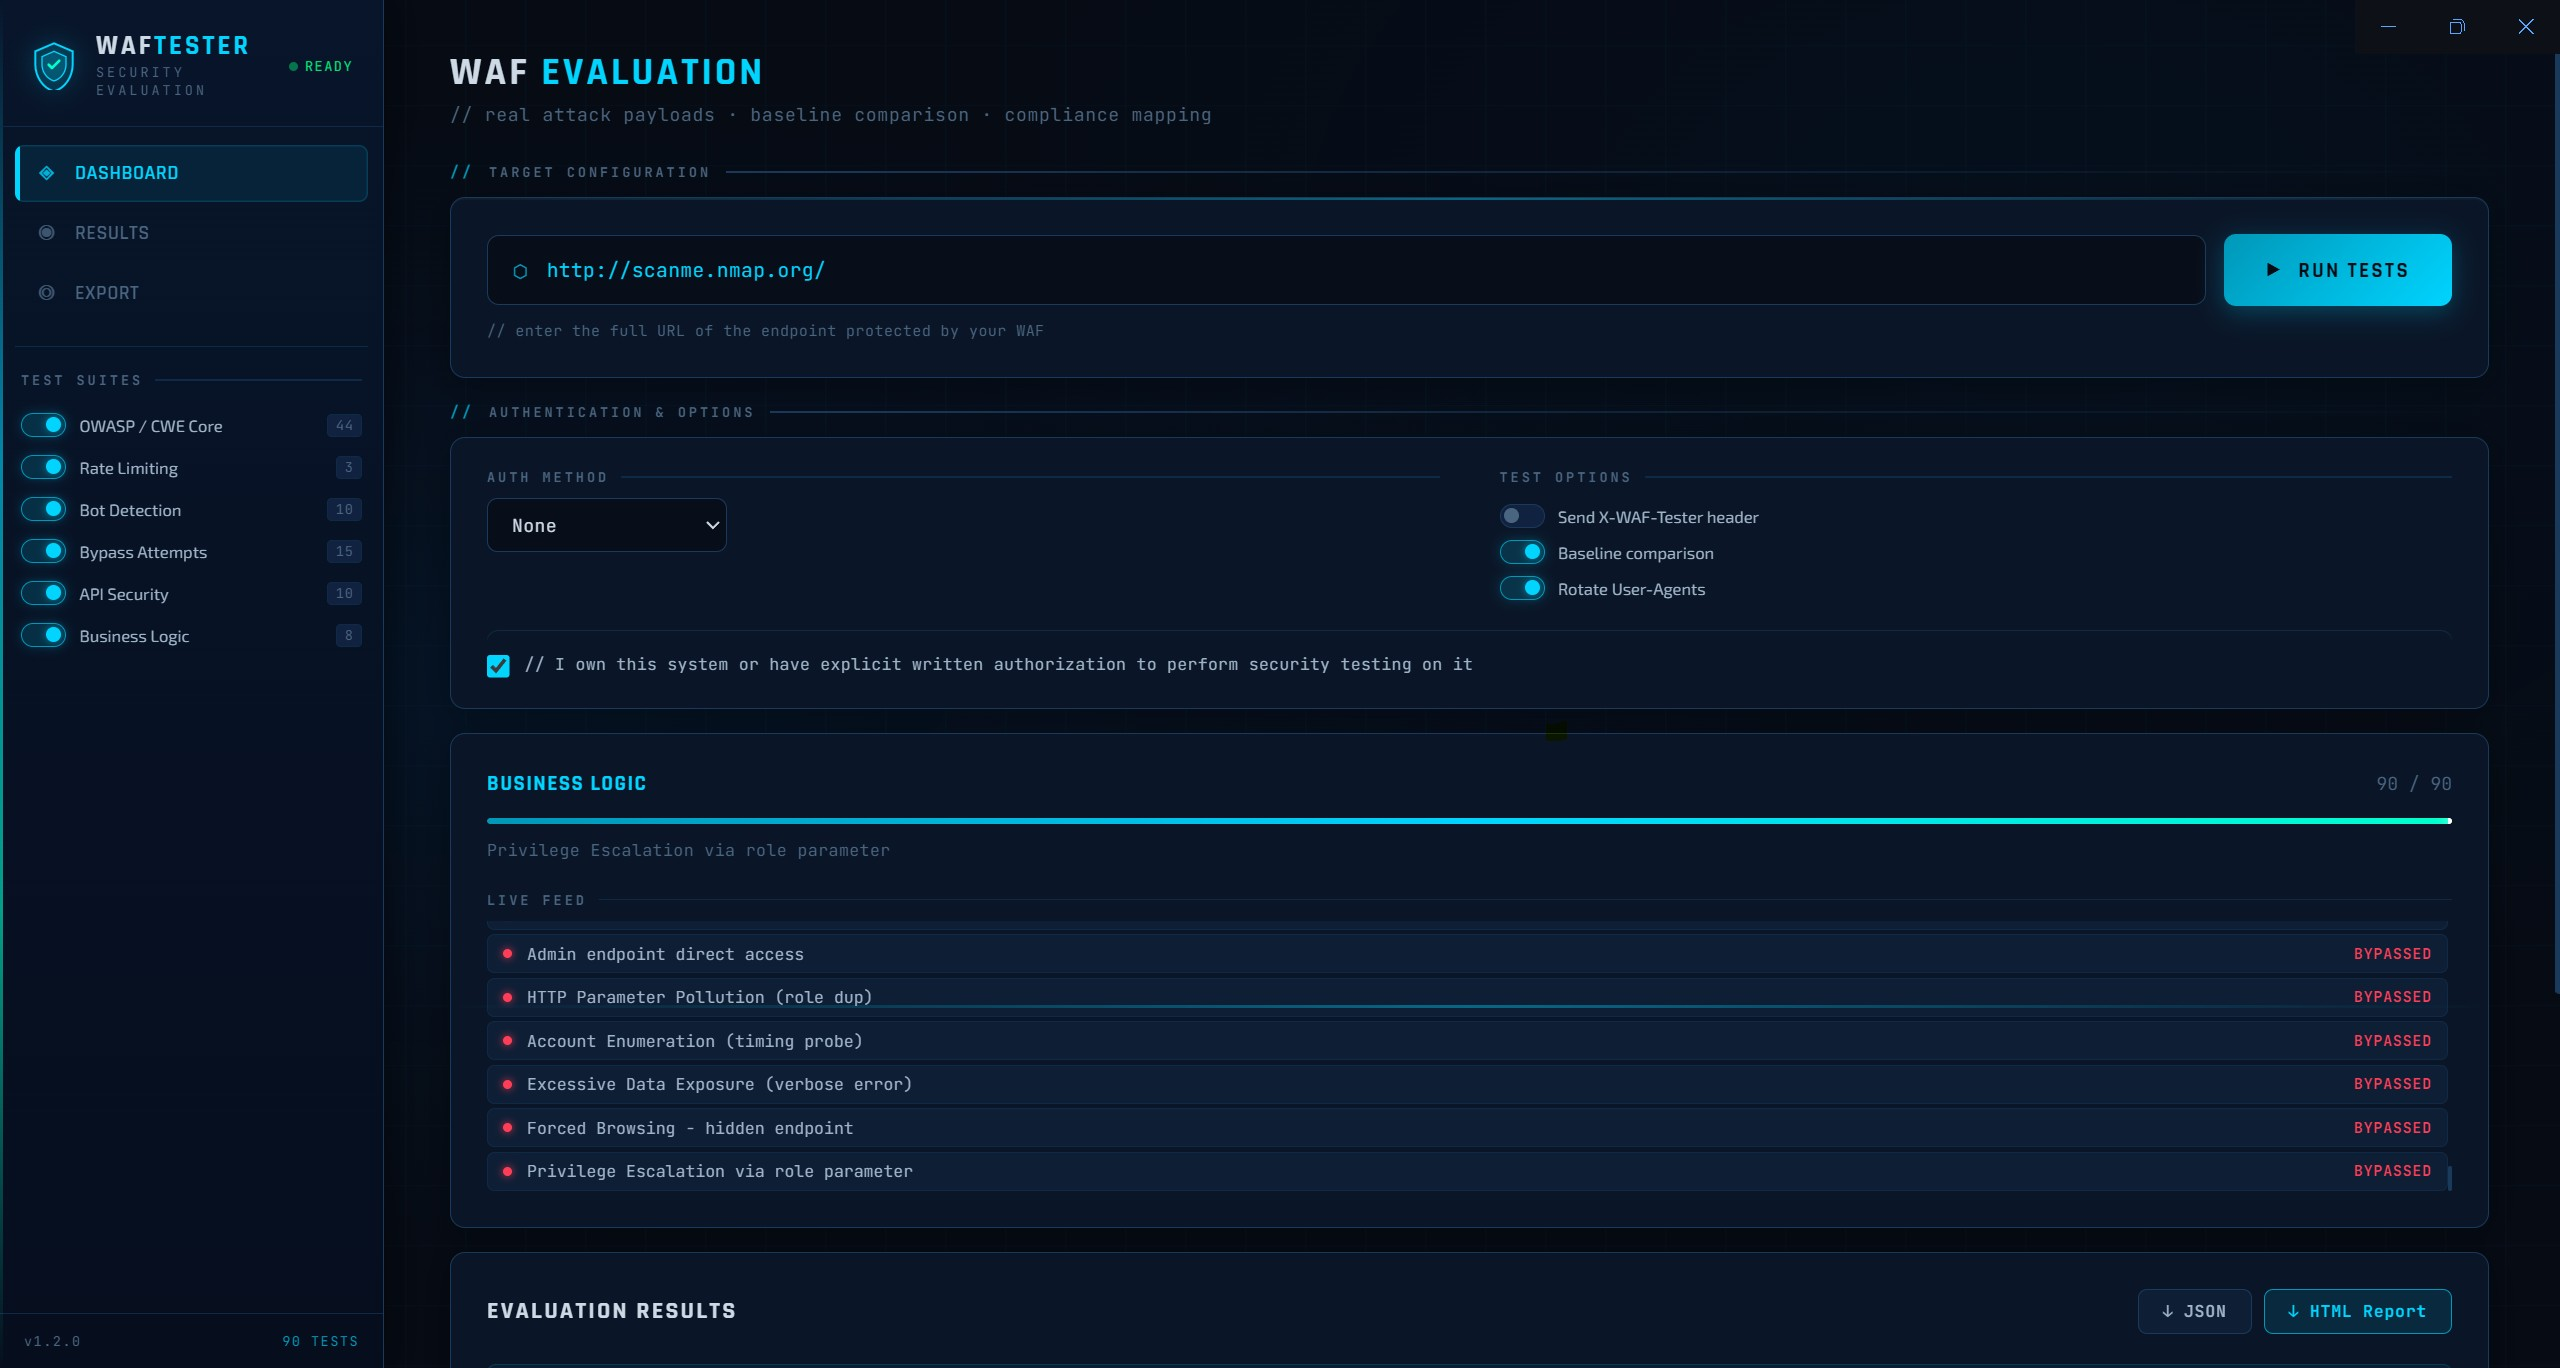
A program for testing WAF functionality

Security scanner for MCP servers. Grades auth, permissions, injection risks, and tool safety. The Lighthouse of agent security.

OWASP Web Security Testing Guide RAG system with ChromaDB, MCP for Claude Code

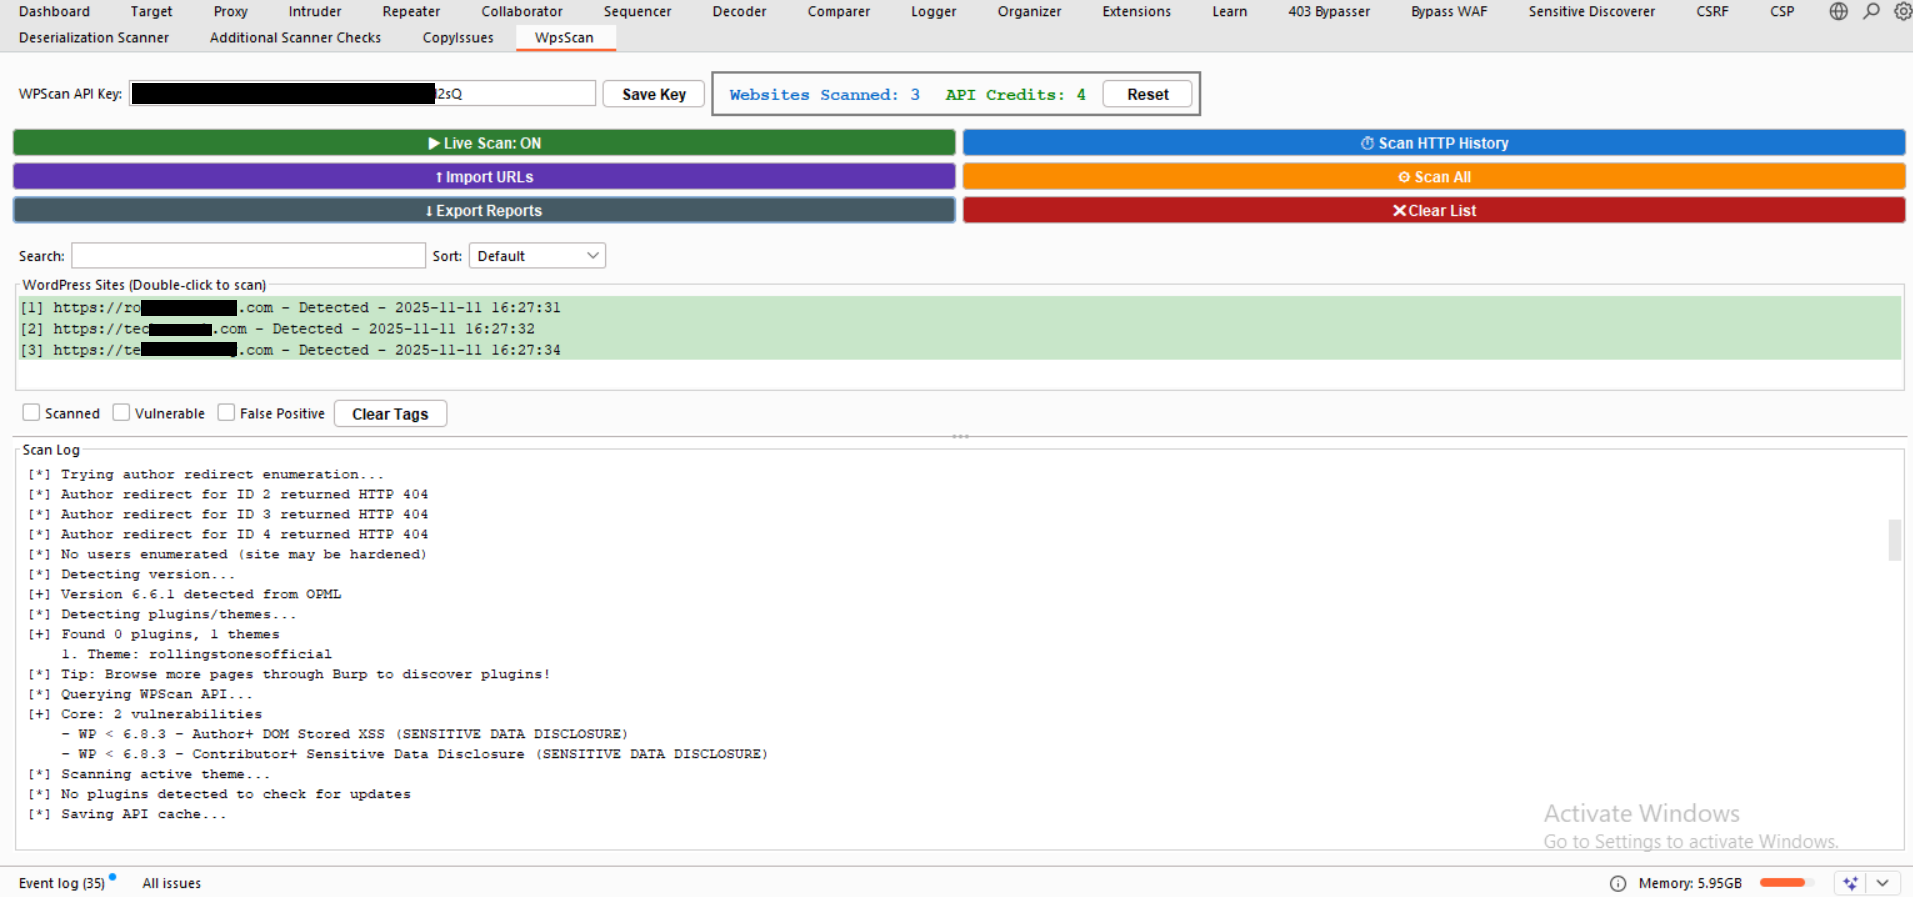
Burp extension for wordpress security scanning

A DAST benchmark of intentionally-vulnerable apps with ground-truth answer keys for scoring scanners

Dockerized exploit lab and script for CVE-2026-19478, a critical unauthenticated GitLab GraphQL code injection enabling arbitrary Ruby method calls,…