
CVE-2026-34486
 404-src/cve-2026-34486
Exploit for Apache Tomcat EncryptInterceptor bypass leading to unauthenticated RCE via Java deserialization on port 4000. Includes lab setup,…
educationexploitationpenetration-testing+3
10
404-src/cve-2026-34486Exploit for Apache Tomcat EncryptInterceptor bypass leading to unauthenticated RCE via Java deserialization on port 4000. Includes lab setup,…
 ab0x90/cve-2021-44228_poc
Python proof-of-concept for CVE-2021-44228 (Log4Shell) that automates exploitation via a crafted Java payload, with argparse options for customizable…
 rub-nds/cve-2020-2655-demoserver
Demonstration server for CVE-2020-2655, a Java deserialization vulnerability, providing a vulnerable endpoint for security testing and research.
 sak110/cve-2026-20131
Detection and proof-of-concept exploit for CVE-2026-20131, a critical unauthenticated Java deserialization RCE in Cisco Secure FMC. Includes a safe…
 mouadk/parquet-rce-poc-cve-2025-30065
Proof-of-concept exploit for CVE-2025-30065 demonstrating remote class instantiation and SSRF via malicious Parquet files in Java applications.
 mattb709/cve-2025-24813-poc-apache-tomcat-rce
A Python proof-of-concept exploit for CVE-2025-24813 - Unauthenticated RCE in Apache Tomcat (v9.0.0-9.0.98/10.1.0-10.1.34/11.0.0-11.0.2) via…
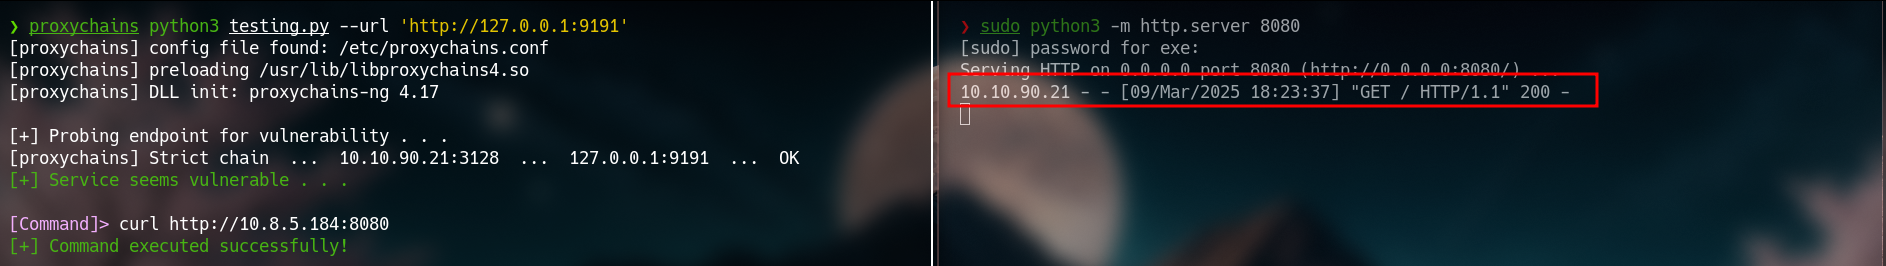 monke443/cve-2023-27350
Unauthenticated remote command execution in Papercut service allows an attacker to execute commands due to improper access controls in the…
 b-abderrahmane/cve-2021-44228-playground
Docker-based lab to validate CVE-2021-44228 (Log4Shell) in Java apps, test mitigations, and simulate RCE via LDAP and HTTP payloads.
 oscerd/cve-2026-49365
PoC reproducer for CVE-2026-49365 (Apache Camel camel-netty-http / camel-undertow): muteException defaults to false, so an uncaught exception's full…
 zlepper/cve-2021-44228-test-server
A small server for verifing if a given java program is succeptibel to CVE-2021-44228
 joaovicdev/exploit-cve-2026-40901
Automated exploit for DataEase: 4-vulnerability chain (auth bypass, JDBC blocklist bypass, SQL injection, Java deserialization) achieving…
 george0papasotiriou/cve-2026-22010-android-intent-redirection-to-exported-component
Proof-of-concept for CVE-2026-22010 Android intent redirection: demonstrates an exported activity forwarding intents to attacker-controlled internal…
 shcesama/cve-2023-4863-analysis
Educational analysis of CVE-2023-4863 (libwebp heap buffer overflow) with Blue Team detection tools, static WebP scanner, defensive Java validator,…
 cucadili/cve-2017-3066
Analysis and exploitation of CVE-2017-3066, a Java deserialization RCE in Adobe ColdFusion's BlazeDS library, with Suricata detection rules and…
 xfei3/cve-2017-3241-poc
POC for java RMI deserialization vulnerability
 reachabilityorg/cve-2022-42889-text4shell-docker
Dockerized vulnerable Java application demonstrating CVE-2022-42889 (Text4Shell) remote code execution via Apache Commons Text string lookups, for…
 al1ex/ysoserial
A proof-of-concept tool for generating payloads that exploit unsafe Java object deserialization
 oscerd/cve-2026-27172
Reproducer for CVE-2026-27172: Apache Camel camel-consul ConsulRegistry Java deserialization (RCE)