

DakshSCRA
 coffeeandsecurity/dakshscra
Framework-aware static code analysis tool for automated source code review with platform-specific rules, taint analysis, effort estimation, and…
code-analysisdevsecopseducation+7
45
coffeeandsecurity/dakshscraFramework-aware static code analysis tool for automated source code review with platform-specific rules, taint analysis, effort estimation, and…
 0xdak/cve-2026-32136_exploit
Proof-of-concept exploit for CVE-2026-32136: unauthenticated authentication bypass in AdGuard Home via HTTP/2 cleartext (h2c) upgrade. Demonstrates…
 0xnxt1me/cve-2025-29927
Proof-of-concept exploit for CVE-2025-29927 that adds x-middleware-subrequest to bypass Next.js middleware authentication checks.
 ubaydev/cve-2024-10508
Proof-of-concept exploit for CVE-2024-10508: unauthenticated privilege escalation via password recovery bypass in RegistrationMagic WordPress plugin…

 alardiians/gitea-cve-2026-28699
Lab + writeup for CVE-2026-28699: Gitea OAuth2 scope enforcement bypass via HTTP Basic auth
 nxploited/cve-2025-3604
Flynax Bridge <= 2.2.0 - Unauthenticated Privilege Escalation via Account Takeover
 owasp/opencre
Interactive platform linking security standards and guidelines for designing, developing, testing, and procuring secure software. Provides a unified…
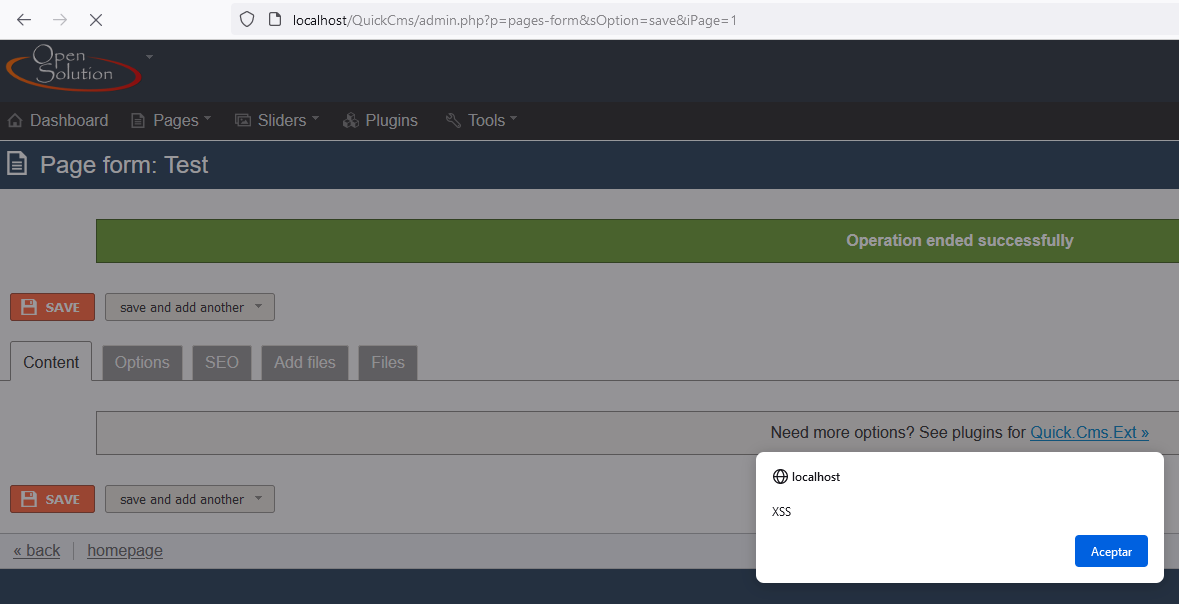 sromanhu/cve-2023-43344-quick-cms-stored-xss---seo-meta-description
Quick CMS 6.7 is affected by a Cross-Site Scripting (XSS) vulnerability that allows attackers to execute arbitrary code via a crafted payload to the…
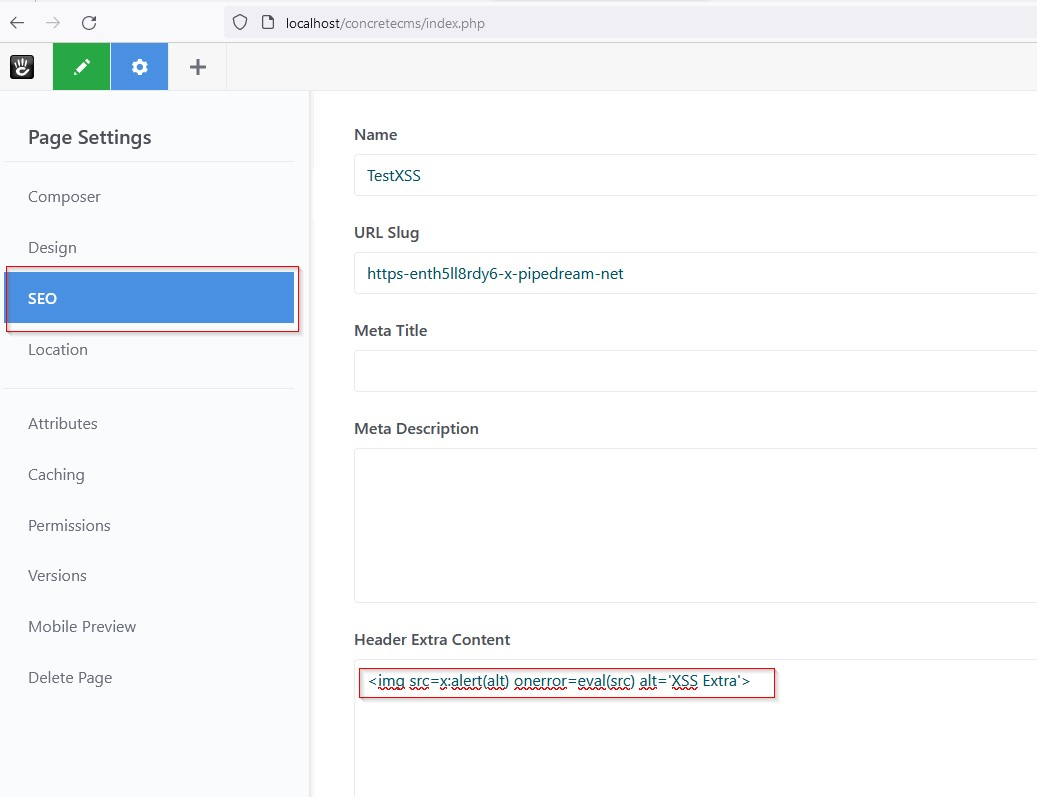 sromanhu/cve-2023-44766_concretecms-stored-xss---seo
Cross Site Scripting vulnerability in ConcreteCMS v.9.2.1 allows a local attacker to execute arbitrary code via a crafted script to the SEO - Header…
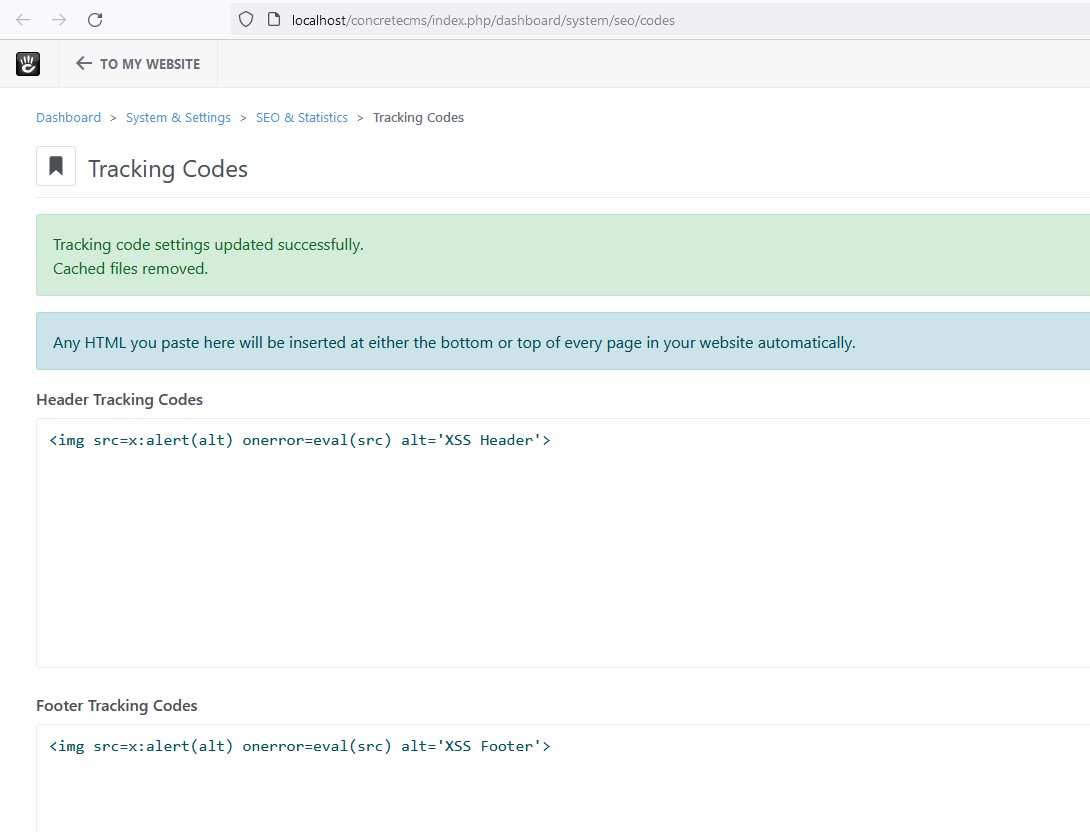 sromanhu/cve-2023-44760_concretecms-stored-xss---trackingcodes
Multiple Cross Site Scripting vulnerability in ConcreteCMS v.9.2.1 allows a local attacker to execute arbitrary code via a crafted script to the…
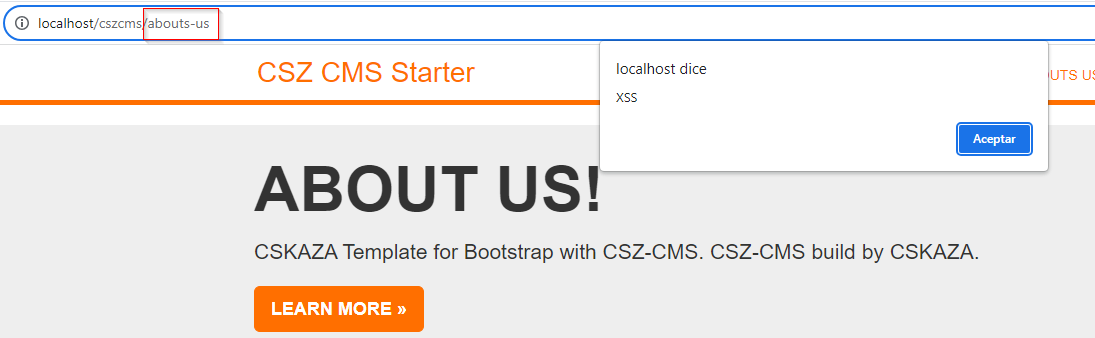 sromanhu/csz-cms-stored-xss---site-settings
CSZ CMS 1.3.0 is affected by a Cross-Site Scripting (XSS) vulnerability that allows attackers to execute arbitrary code via a crafted payload to the…
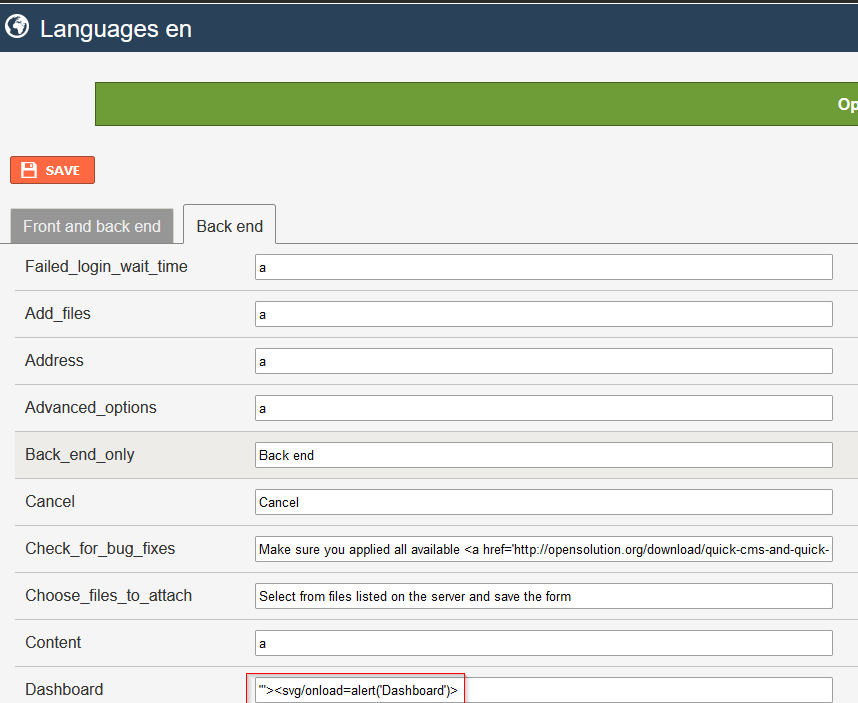 sromanhu/cve-2023-43346-quick-cms-stored-xss---languages-backend
Quick CMS 6.7 is affected by a Cross-Site Scripting (XSS) vulnerability that allows attackers to execute arbitrary code via a crafted payload to the…
 soltanali0/cve-2023-7028
Implementation and exploitation of CVE-2023-7028 account takeover vulnerability related to GO-TO CVE weekly articles of the 11th week.
 sromanhu/cve-2023-44771_zenariocms--stored-xss---page-layout
Zenariocms 9.4.59197 is affected by a Cross-Site Scripting (XSS) vulnerability that allows attackers to execute arbitrary code via a crafted payload…
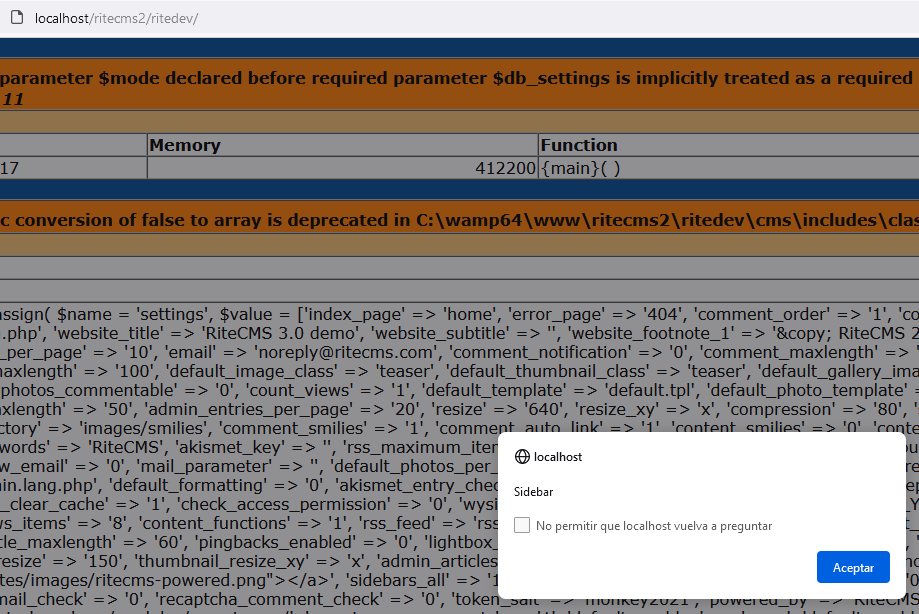 sromanhu/cve-2023-43877-ritecms-stored-xss---home
RiteCMS 3.0 is affected by a Multiple Cross-Site Scripting (XSS) vulnerability that allows attackers to execute arbitrary code via a crafted payload…
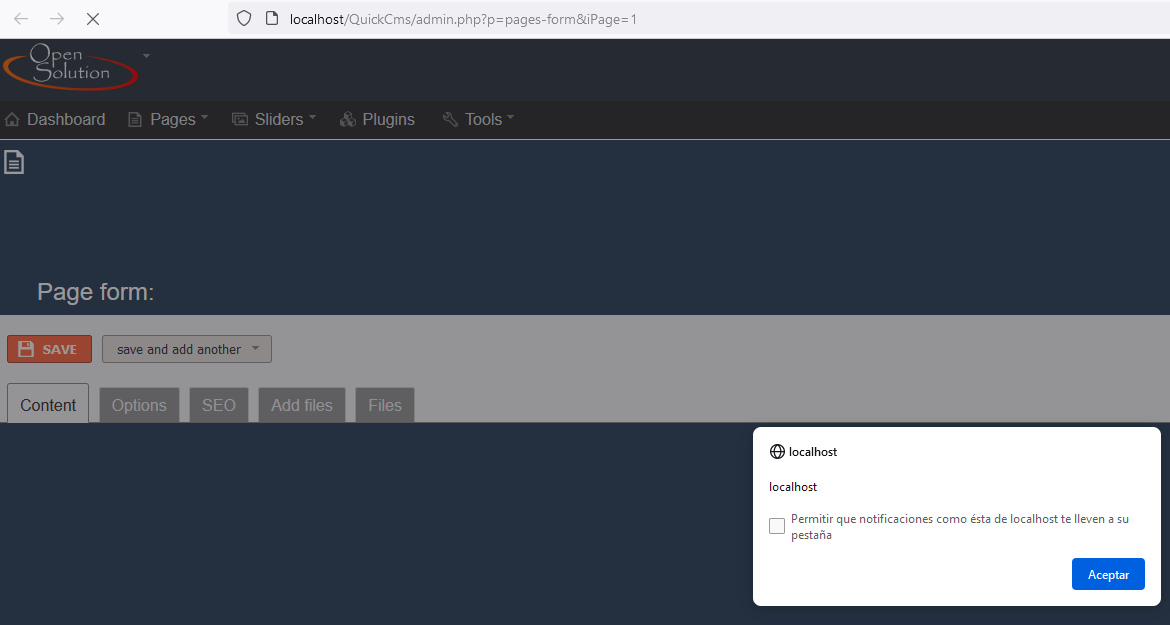 sromanhu/cve-2023-43345-quick-cms-stored-xss---pages-content
Quick CMS 6.7 is affected by a Cross-Site Scripting (XSS) vulnerability that allows attackers to execute arbitrary code via a crafted payload to the…
 instantbox/instantbox
📦 Get a clean, ready-to-go Linux box in seconds.