Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2024-10508 — Proof-of-concept exploit for CVE-2024-10508: unauthenticated privilege escalation via password recovery bypass in RegistrationMagic WordPress plugin up to 6.0.2.6. | Kitploit
Tools/GitHubGitHub/ubaydev/cve-2024-10508
Authentication & AuthorizationPrivilege EscalationPassword AttacksVulnerability AnalysisWeb Application ExploitationLearning & Education
GitHububaydev/cve-2024-10508

CVE-2024-10508

Proof-of-concept exploit for CVE-2024-10508: unauthenticated privilege escalation via password recovery bypass in RegistrationMagic WordPress plugin up to 6.0.2.6.

View Repository
1281 year agoNot yet reviewed
Share

Unauthenticated Privilege Escalation via Password Recovery on RegistrationMagic <= 6.0.2.6

Disclaimer: This information is provided for educational purposes only. This document aims to raise awareness of security vulnerabilities and should not be used for any unauthorized or malicious activities. Engaging in actions that exploit these vulnerabilities without permission is illegal and unethical.

The RegistrationMagic – User Registration Plugin with Custom Registration Forms plugin for WordPress is vulnerable to privilege escalation via account takeover in all versions up to, and including, 6.0.2.6. This is due to the plugin not properly validating the password reset token prior to updating a user's password. This makes it possible for unauthenticated attackers to reset the password of arbitrary users, including administrators, and gain access to these accounts.

After researching from several sources related to this CVE, I realized that the attack on this CVE is quite easy and does not require additional applications such as Burpsuite or Postman, this CVE only requires an email from an account that has an administrator level and resets it via the /password-recovery page or another custom password reset page.

Dependencies

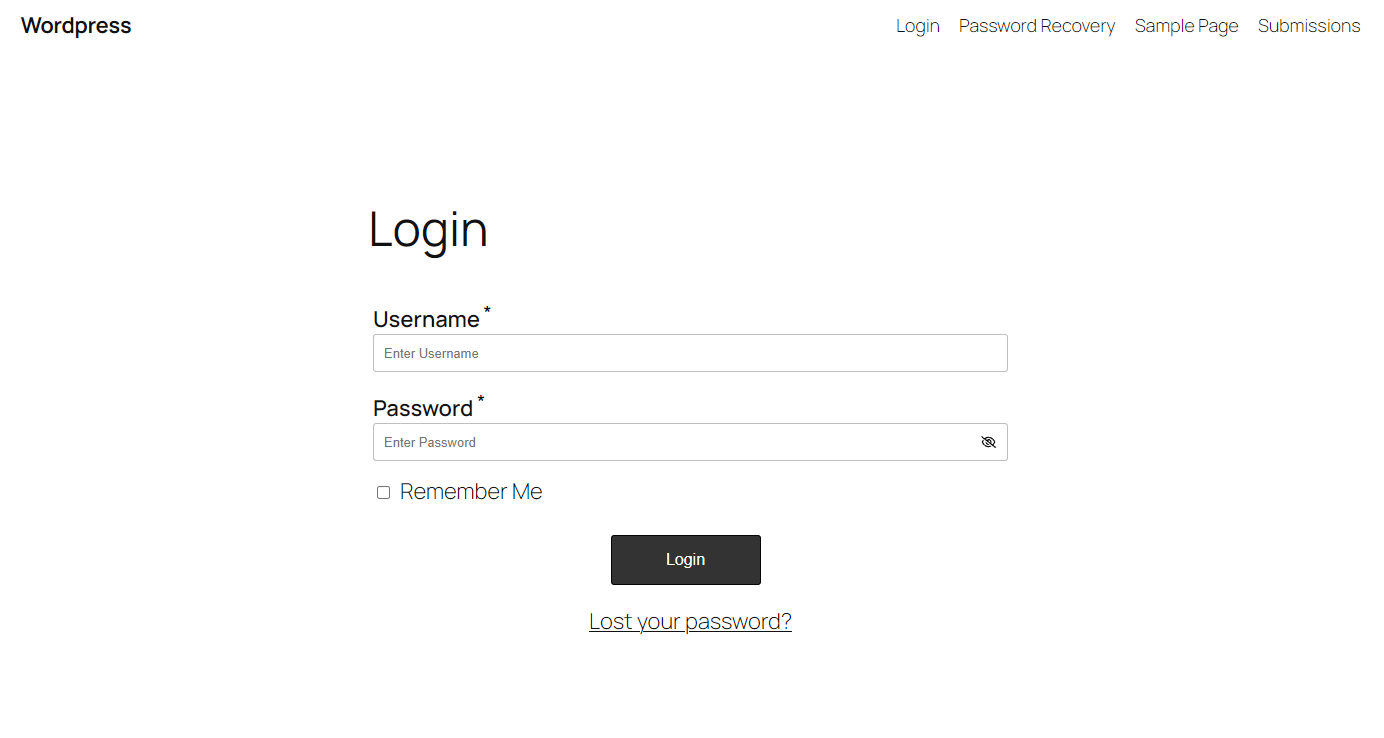
  • Password reset page that has been set by admin (by default not) Screenshot 2
  • Knowing email accounts that have administrator level

PoC

  1. Go to the login page of the target that has this plugin (RegistrationMagic) Screenshot 2
  2. Click “Lost your password”, if the page leads to the password reset page, the password reset page has been set by the admin. if not, it means not. Screenshot 2
  3. fill in an email that has an administrator level, and send it Screenshot 2
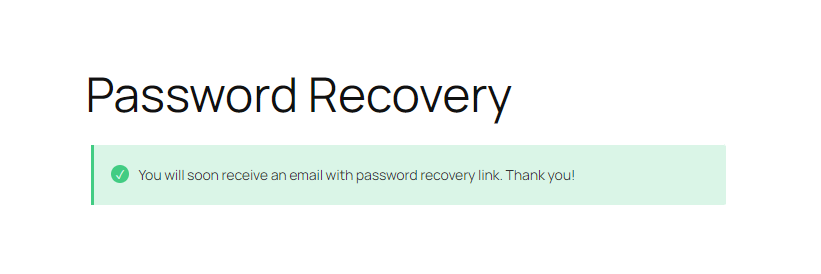
  4. After that add ?reset_token= at the end of the url, and reset the password. Screenshot 2 Screenshot 2
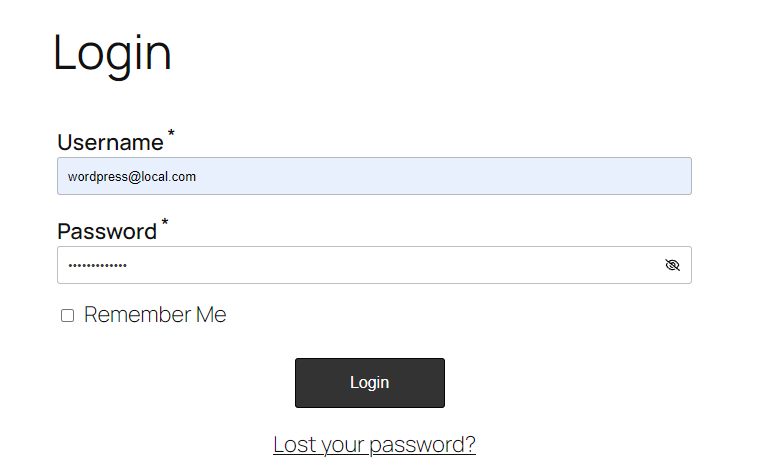
  5. After resetting your password, you can now log in using the password you sent earlier. Screenshot 2 Screenshot 2
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    524
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    478
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    357
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    317
  • 5

    estorides

    grisuno/estorides

    Aggregates 99+ free OSINT sources in parallel, resolves entities into a knowledge graph, and exports STIX 2.1, MISP, or GraphML with LLM-assisted analysis.

    305
  • 6

    opencti

    opencti-platform/opencti

    Open Cyber Threat Intelligence Platform

    275

Explore all tools

Browse our collection of tools

View all tools →