
CVE-2026-55255-Lab
Local Docker lab for reproducing CVE-2026-55255, an IDOR vulnerability in Langflow's Responses API. Validates cross-user flow execution in vulnerable…

Local Docker lab for reproducing CVE-2026-55255, an IDOR vulnerability in Langflow's Responses API. Validates cross-user flow execution in vulnerable…

Reproducer for CVE-2026-46588: Apache Camel camel-couchdb CouchDb* header injection (operation confusion) subverting a write-only endpoint into read…

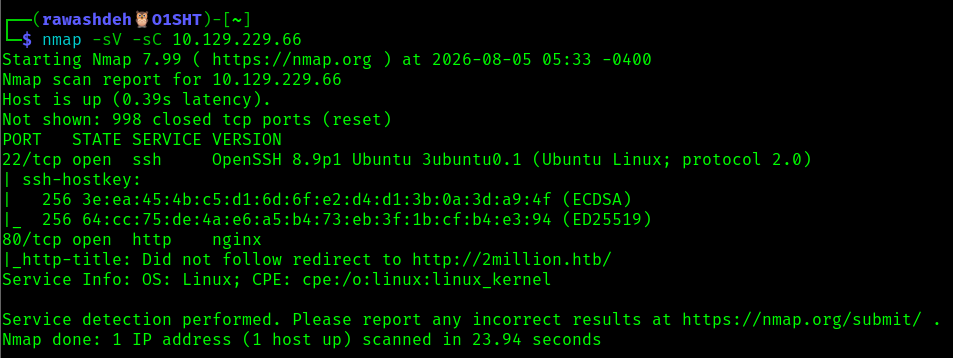
Hack The Box TwoMillion machine writeup — JWT/invite-code bypass, IDOR, command injection, and CVE-2023-0386 privilege escalation.

Find the vulnerability your tests were never written to catch. A ReGrade demo modeling CVE-2023-5968: catch a password-hash leak by comparing an app…

Authenticated WordPress IDOR exploit for CVE-2026-12400; enumerates FlowForms REST form IDs and modifies form content or hijacks email notifications.

Proof-of-concept exploit for CVE-2026-35045, a broken object-level authorization vulnerability in Tandoor Recipes, demonstrating unauthorized recipe…

Proof-of-concept for CVE-2025-63406 in GroupOffice, demonstrating API-based object manipulation and authentication flow for vulnerability analysis…

演示 Next.js 中的 Middleware 授權繞過漏洞 (CVE-2025-29927) 允許未經授權的用戶存取受保護的資訊。

The code for personally reproducing the corresponding vulnerability

Time-based blind SQL injection proof-of-concept for LiteLLM v1.65.4. Exploits the `/key/block` endpoint to extract database contents and read server…

Docker-based lab for reproducing CVE-2026-46645, an authorization bypass in SQLAdmin's ajax_lookup endpoint. Includes vulnerable and patched targets,…

CVE-2026-24136 | Lab khai thác lỗ hổng IDOR trên Saleor GraphQL - query order() không kiểm tra xác thực, lộ toàn bộ PII (email, địa chỉ, SĐT) của…

Demonstrates CVE-2023-27524 Broken Object Level Authorization (BOLA) vulnerability with vulnerable and fixed Flask API implementations for security…

Validation target: minimal WordPress core slice reproducing the wp2shell (CVE-2026-63030 + CVE-2026-60137) REST-to-SQLi chain

Hybrid ML and heuristic-based URL phishing detector with real-time analysis, explainable confidence scores, and REST API for programmatic security…

The vulnerability exists in the Student Payment API. The application fails to properly validate whether the user requesting a receipt is authorized…

Proof-of-concept exploit for CVE-2026-24134, a Broken Object Level Authorization vulnerability in StudioCMS, demonstrating unauthorized access to…

Interactive demo for CVE-2023-45857 (axios XSRF token bypass). Step-by-step guide to reproduce the vulnerability in a controlled dev container…