ESAPI__esapi-java-legacy_CVE-2022-23457_2-2-3-1

Enterprise Security API library providing security controls for Java web applications, including authentication, access control, input validation,…

Enterprise Security API library providing security controls for Java web applications, including authentication, access control, input validation,…

Insecure TeamCity CI environment for hands-on penetration testing training: reconnaissance, credential theft, privilege escalation, and lateral…

An intentionally designed broken web application based on REST API.

A comprehensive web application security testing toolkit that combines 10 powerful penetration testing features into one tool.

Web2 bug bounty Agent Skill — evidence-based, no AI slop. Covers 18 vulnerability classes across HackerOne, Bugcrowd, Intigriti, and YesWeHack.

The Super Vulnerable Java Application (SVJA), as demonstrated in the Roniel and DaRon Podcast Show, is an Apache Struts application designed to…

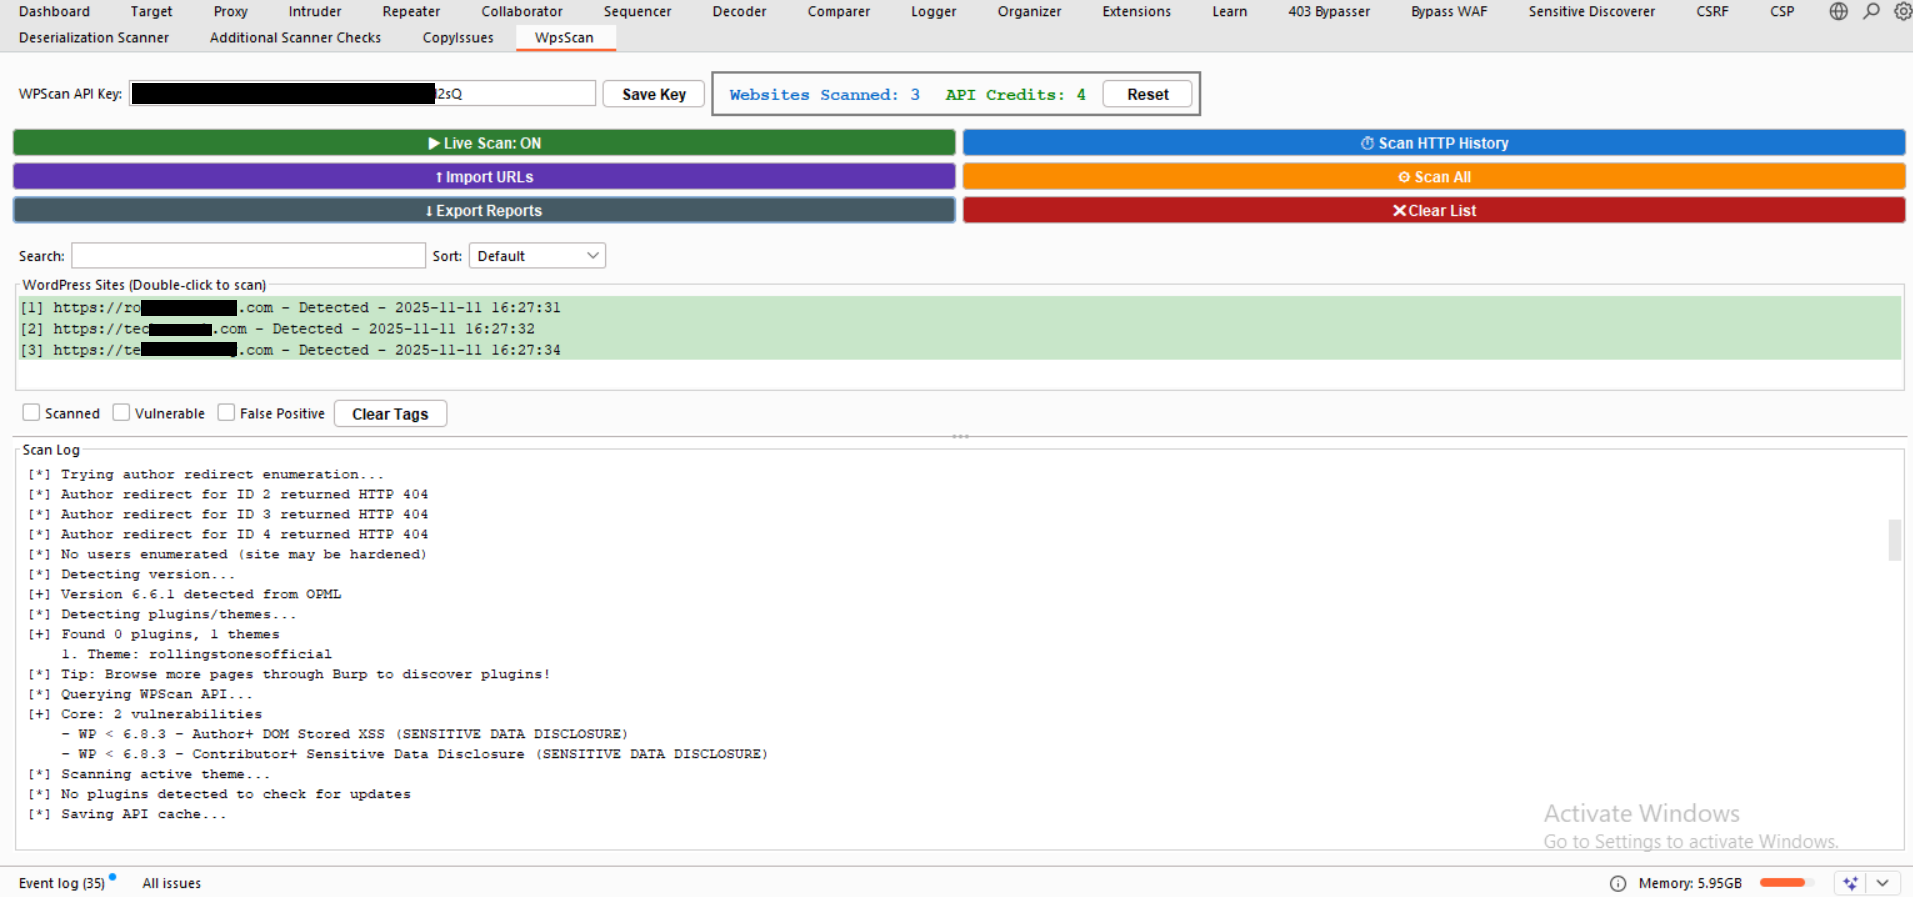
Burp extension for wordpress security scanning

Reproducible BOLA/IDOR PoC against Onlook's tRPC API (CVE-2026-65013), with a 12-step exploit chain, vulnerable and patched Docker targets, and…

A DAST benchmark of intentionally-vulnerable apps with ground-truth answer keys for scoring scanners


Dockerized exploit lab and script for CVE-2026-19478, a critical unauthenticated GitLab GraphQL code injection enabling arbitrary Ruby method calls,…

PoC for CVE-2025-59528 used to achieve remote code execution on the Silentium machine at HTB

Reproducer for CVE-2026-48206: Apache Camel camel-jira IssueKey (and other non-Camel-prefixed) header injection driving arbitrary JIRA issue…

Reproducer for CVE-2026-46592: Apache Camel camel-cxf operationName header injection redirecting the invoked SOAP operation (confused deputy) from a…

Reproducer for CVE-2026-46453 — Apache Camel camel-elasticsearch-rest-client unprefixed-header injection (operation/query override via inbound HTTP…

Reproducer for CVE-2026-46587: Apache Camel camel-couchbase CCB_* header injection enabling document disclosure, tampering, and TTL-forced data…

PoC reproducer for CVE-2026-49099 (Apache Camel camel-salesforce): the non-Camel-prefixed sObjectQuery header escapes the HTTP header filter and…