

log4shell-coraza
 tieupham267/log4shell-coraza
Log4Shell (CVE-2021-44228) defense lab — nginx + Coraza WAF dynamic module + OWASP CRS v4. Educational use only.
defensive-toolseducationexploitation+8
tieupham267/log4shell-corazaLog4Shell (CVE-2021-44228) defense lab — nginx + Coraza WAF dynamic module + OWASP CRS v4. Educational use only.
 mohamedniane/cve-2025-55182-analysis
Security research & exploitation analysis of CVE-2025-55182 (React) — CVSS + OWASP Top 10 mapping
 az9713/cve-lite-on-pi
Running OWASP cve-lite-cli against the pi monorepo: scan journey and key finding (vitest CVE-2026-47429).
 klairmanraj/multi-vlan-enterprise-network-security-infrastructure
Multi-VM virtual network lab with GRE tunneling, nftables firewall, Active Directory, BIND9 DNS, and Docker services. Includes vulnerability…
 axselll/cve-2025-20384
Proof-of-concept demonstrating log injection and poisoning in Splunk via crafted URL parameters, highlighting OWASP log injection risks.
 waburig/open-worldwide-application-security-project-owasp-
Automated Web Vulnerability Assessment of DVWA using OWASP ZAP to identify and analyze critical security flaws like Remote Code Execution…

 mbrandner-group/juiceshopgl
Intentionally vulnerable web application for security training, CTF competitions, and testing security tools. Covers OWASP Top Ten vulnerabilities…
 brunoh6/web-threat-mitigation
Hands-on lab on detecting and mitigating web app threats using OWASP ZAP, Burp Suite, and ModSecurity WAF (with OWASP CRS). Case study: Spring4Shell…
 khaliquesx/cve-2024-48415
Proof-of-concept for CVE-2024-48415: stored XSS vulnerability in itsourcecode Loan Management System v1.0 via borrower profile fields. Includes…
 nvisium-jack-mannino/owasp-goatdroid-project
*This project is no longer maintained* OWASP GoatDroid is a fully functional and self-contained training environment for educating developers and…
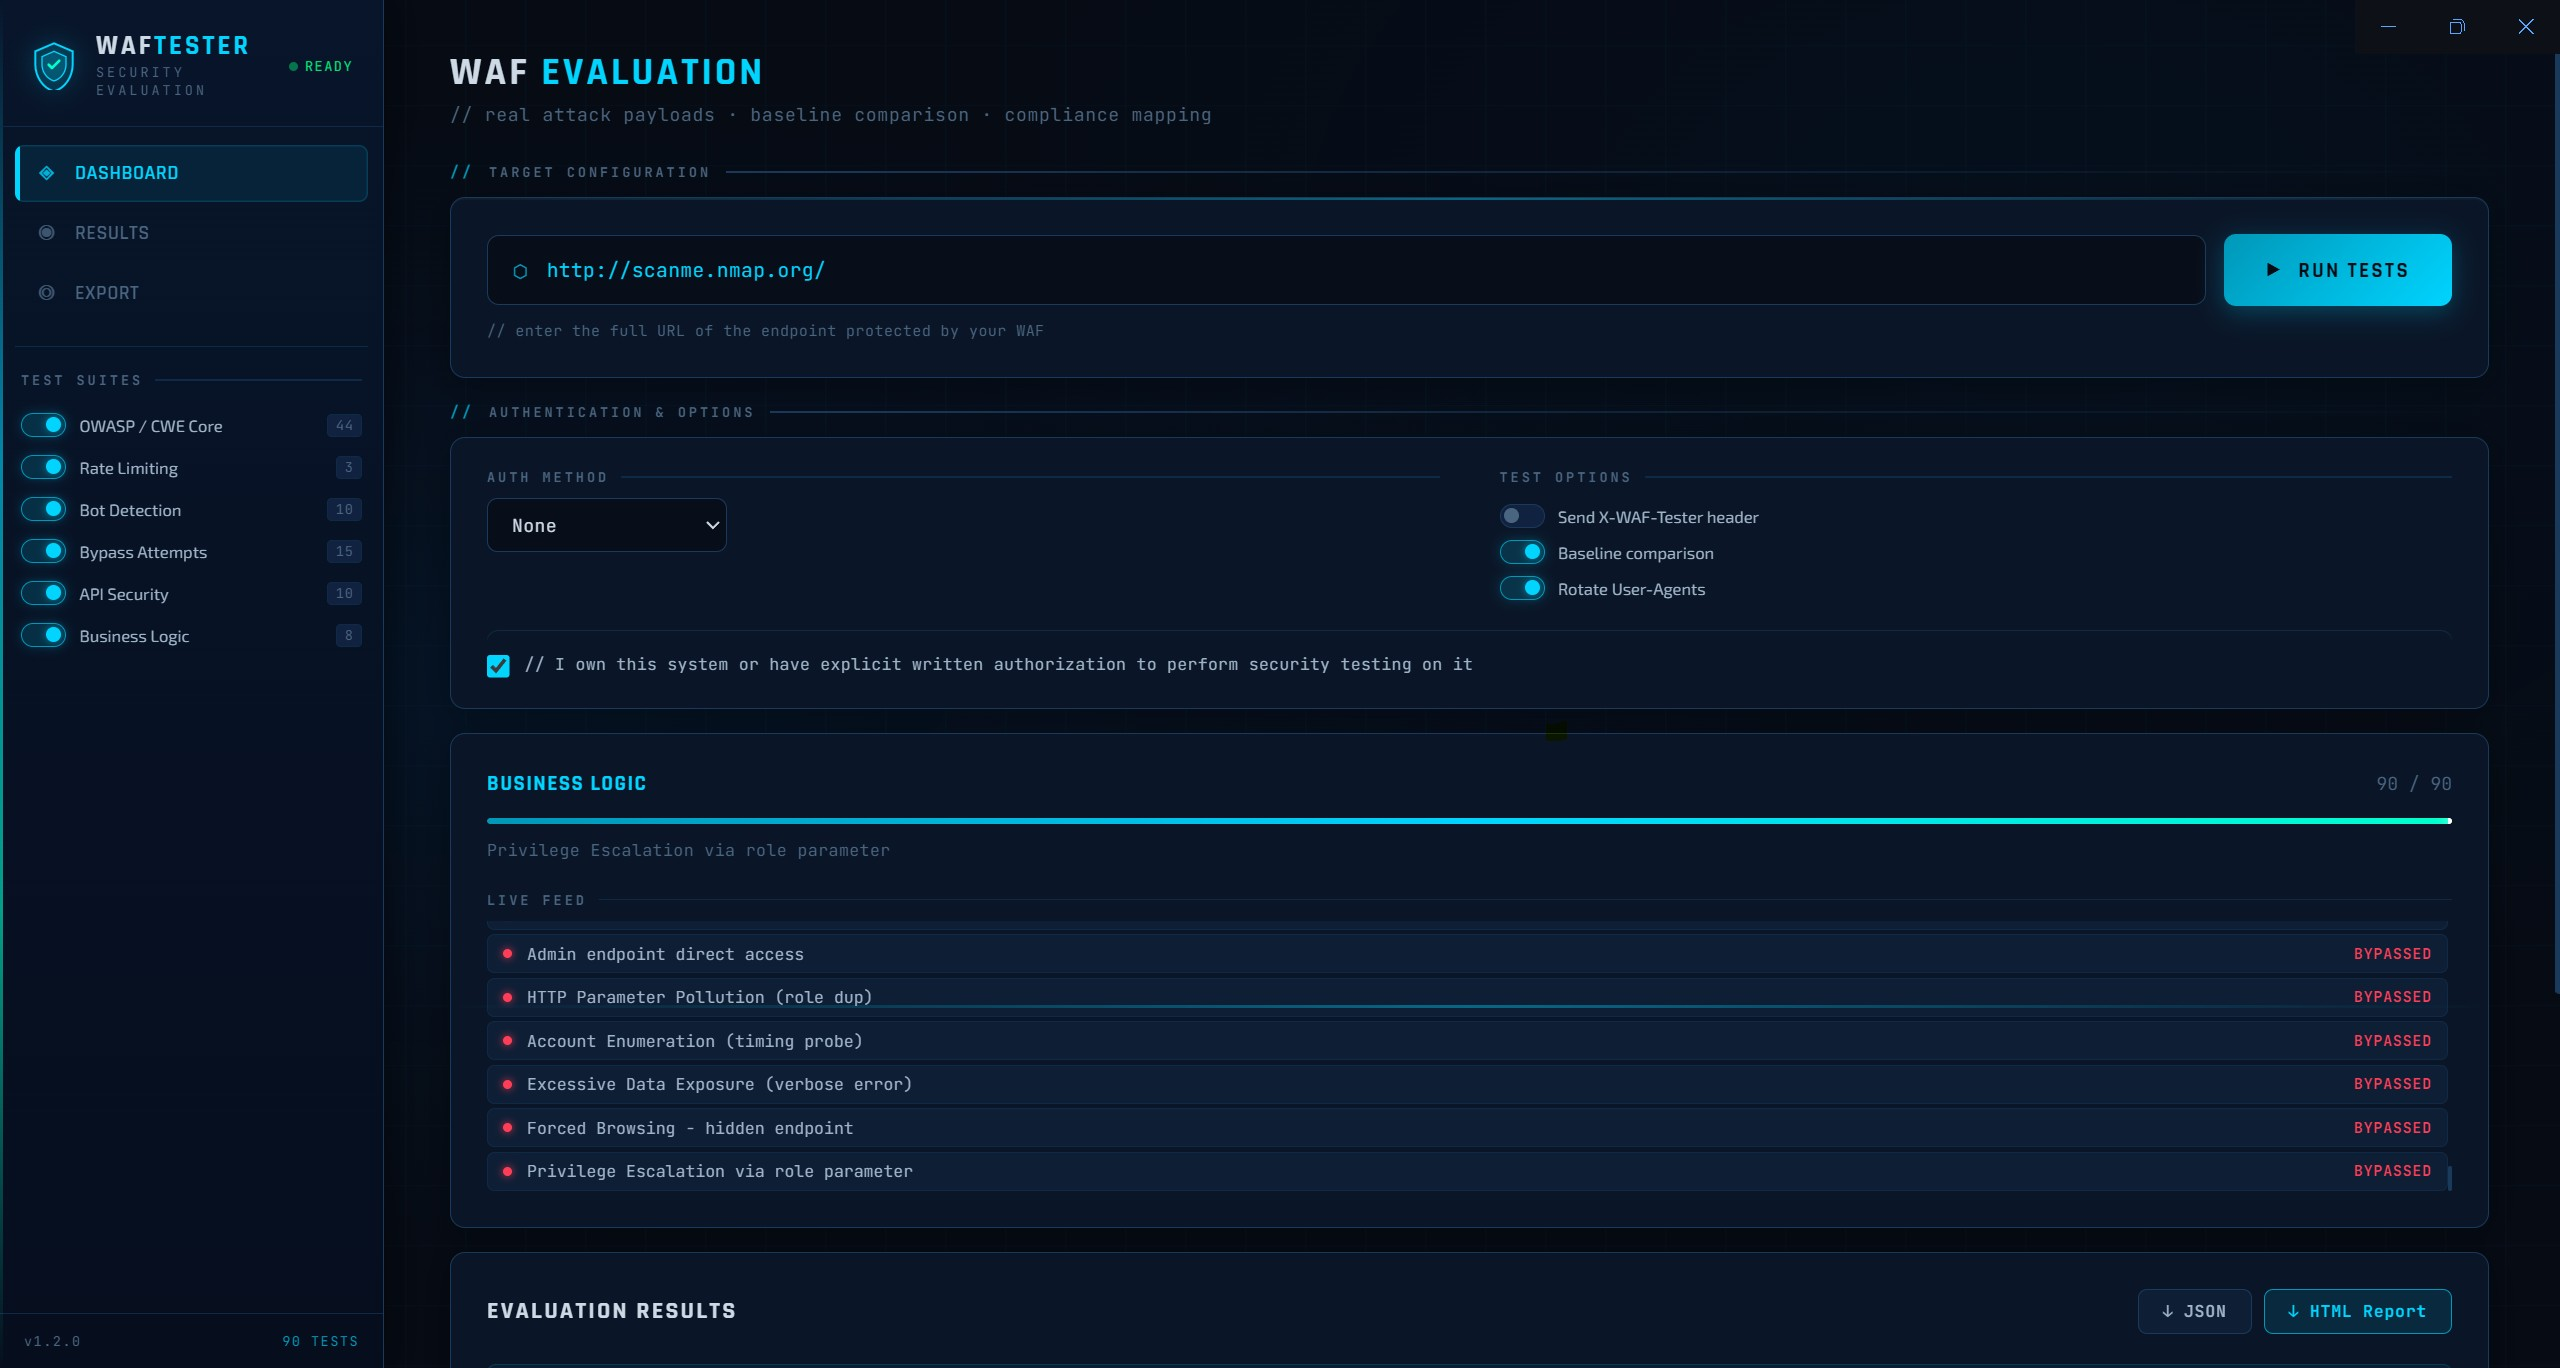 kpomin57/waf-tester
A program for testing WAF functionality
 ottosulin/awesome-ai-security
A collection of awesome resources related AI security
 ine-labs/azuregoat
AzureGoat : A Damn Vulnerable Azure Infrastructure
 ine-labs/gcpgoat
GCPGoat : A Damn Vulnerable GCP Infrastructure
 bhavsec/autopentest-ai
Agentic Pentesting MCP server that discovers, exploits, and reports web application vulnerabilities.
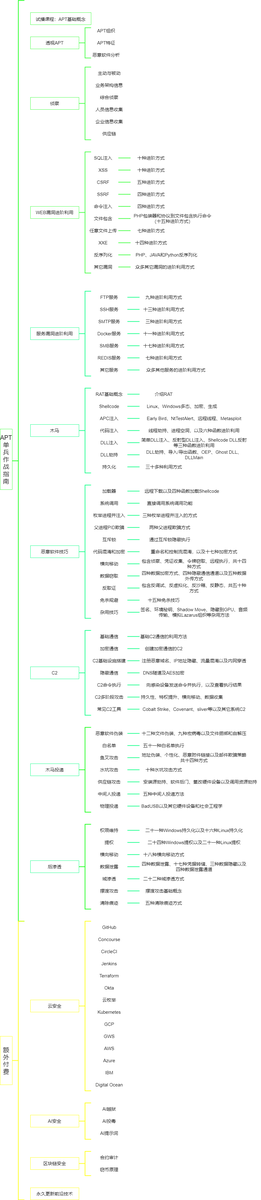 ghostwolflab/ai_security_top
A structured knowledge base covering AI security fundamentals, threat modeling, red team offensive techniques, and blue team defenses, including LLM…
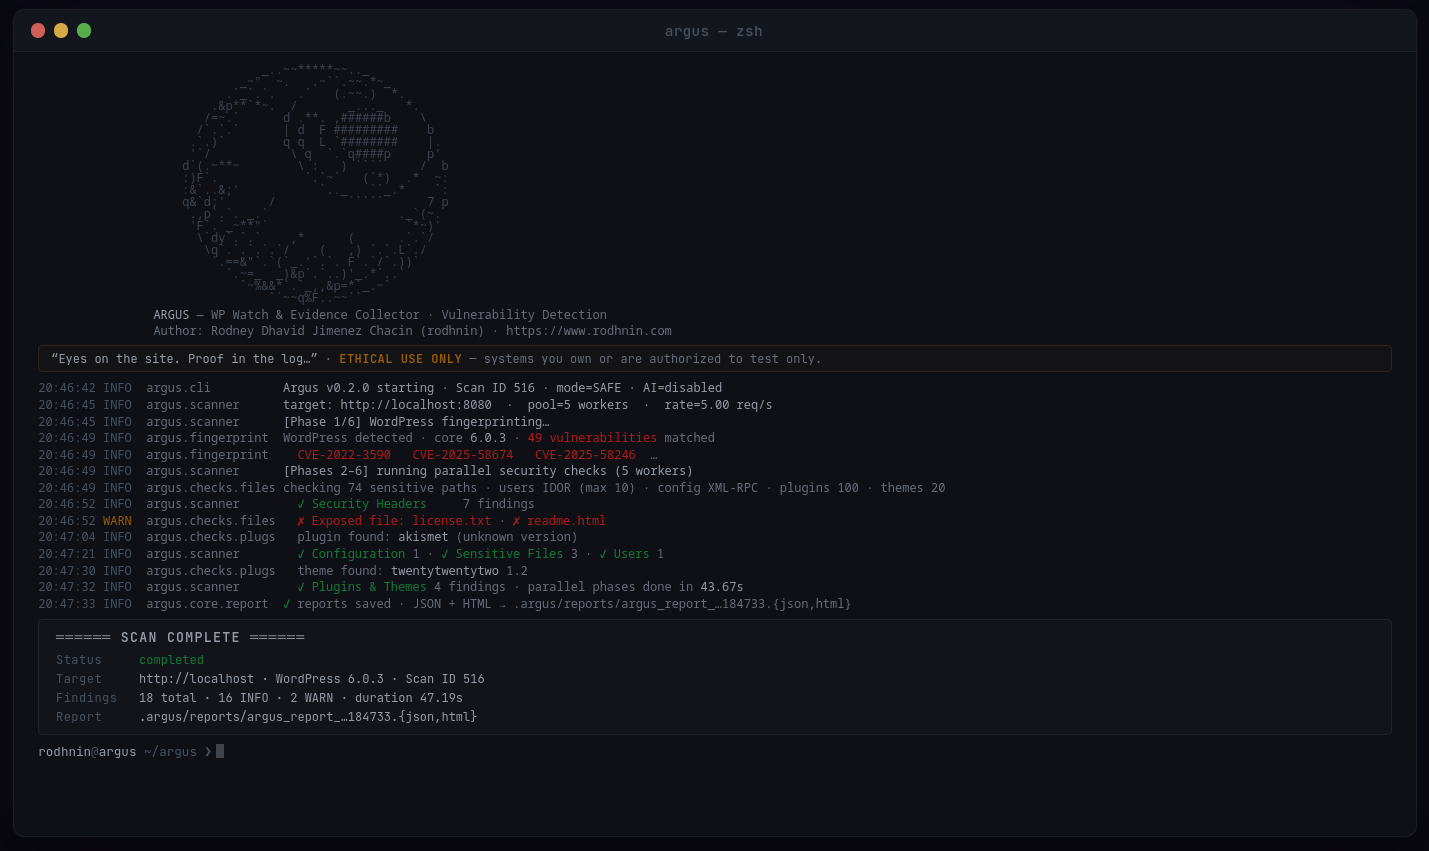 rodhnin/argus-wp-watcher
WordPress security scanner with AI-powered analysis, ethical compliance framework, and professional reporting.
 nxploited/cve-2025-3776
WordPress Verification SMS with TargetSMS Plugin <= 1.5 is vulnerable to Remote Code Execution (RCE)