
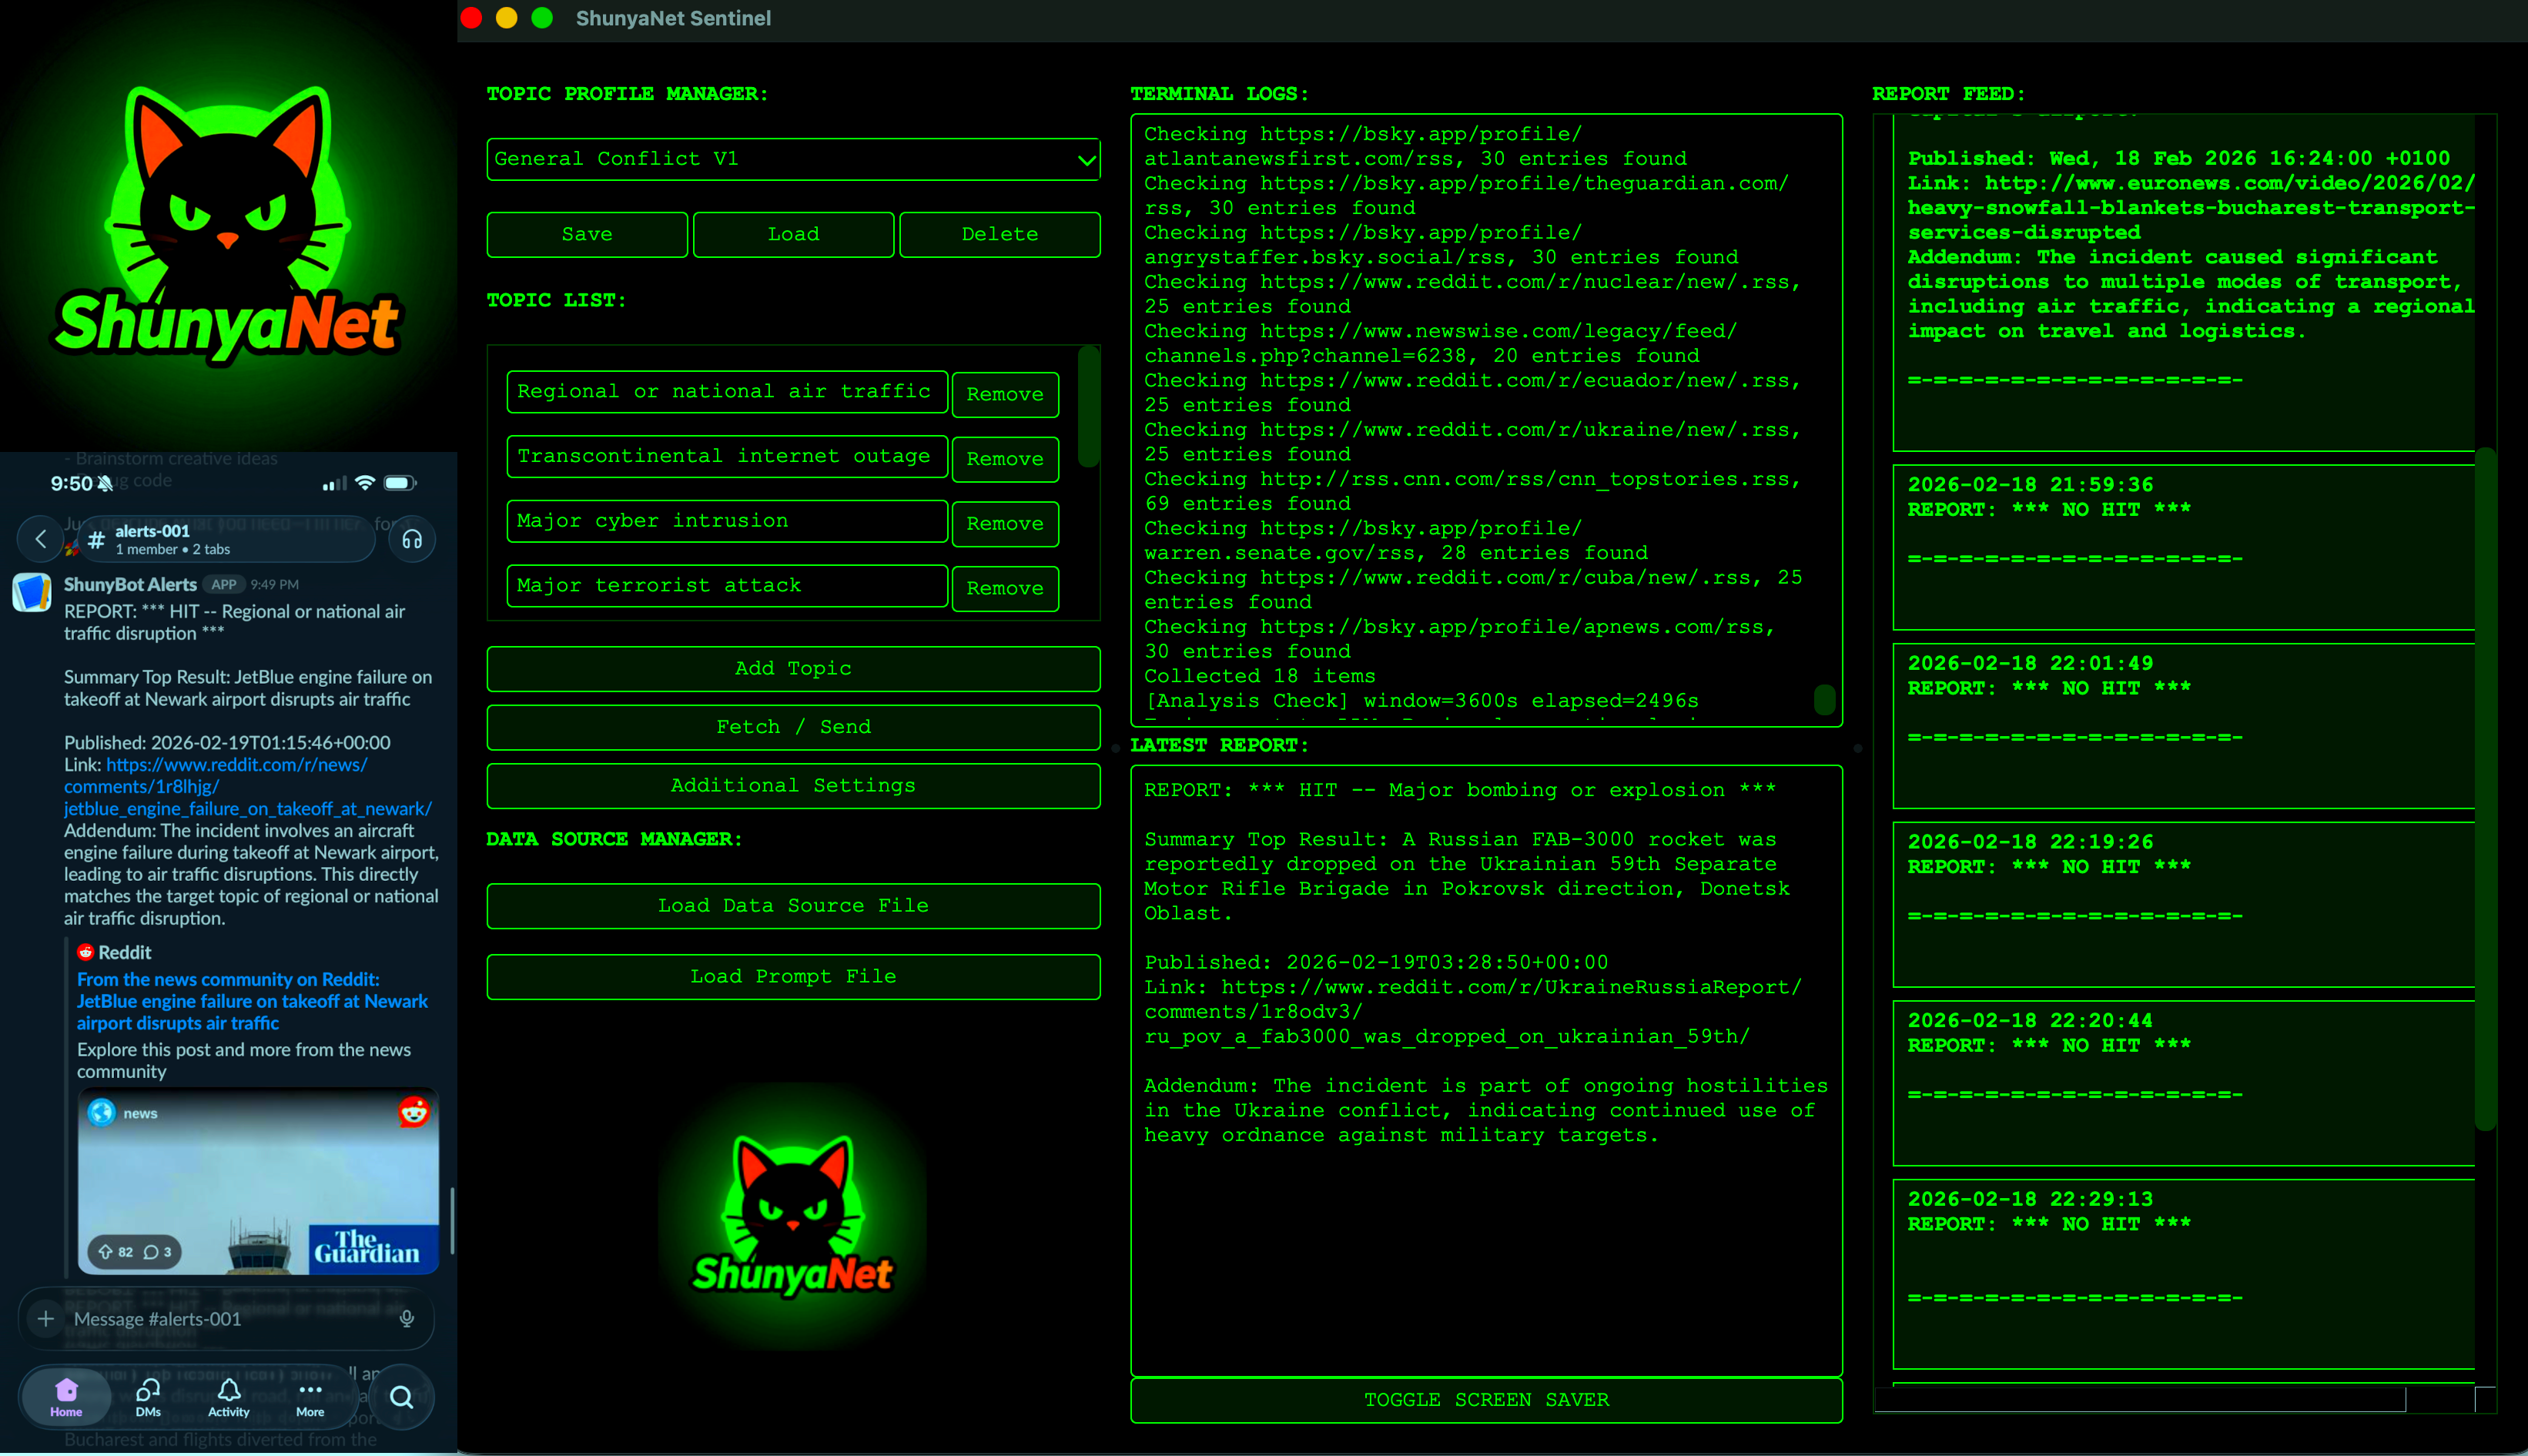
ShunyaNet-Sentinel
 everythingscomputer/shunyanet-sentinel
ShunyaNet Sentinel is a lightweight program that monitors RSS feeds, sends them to an LLM for analysis, and delivers summaries or alerts directly to…
educationinformation-gatheringosint+2
40
everythingscomputer/shunyanet-sentinelShunyaNet Sentinel is a lightweight program that monitors RSS feeds, sends them to an LLM for analysis, and delivers summaries or alerts directly to…
 nanocoai/nanoclaw
A lightweight alternative to OpenClaw that runs in containers for security. Connects to WhatsApp, Telegram, Slack, Discord, Gmail and other messaging…
 capstone-engine/capstone
Multi-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…
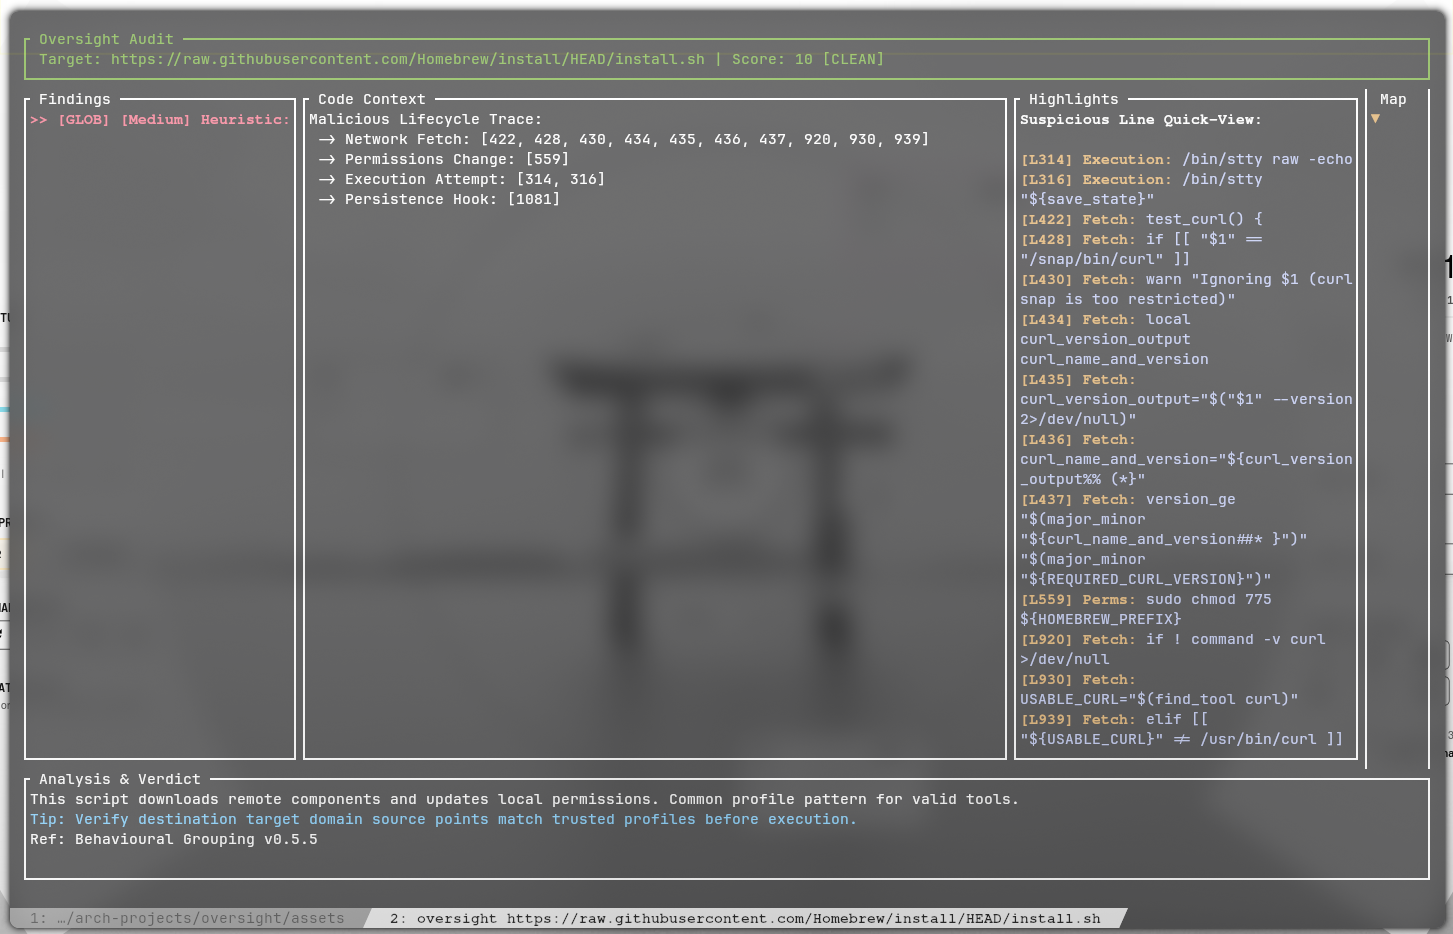 rakosn1cek/oversight
A lightweight security auditor and sandbox for shell scripts. Oversight combines a Static Analysis engine (Rust) with Dynamic Enforcement (Linux…
 semgrep/semgrep
Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.
 division-36/z-jail
A lightweight, multi-layer Linux sandbox combining namespaces, pivot_root, seccomp-bpf, capability dropping, and an evidence-based verdict engine…
 meshcore-dev/meshcore
A new lightweight, hybrid routing mesh protocol for packet radios
 asaotomo/hx0-hawkeye
一个轻量级浏览器抓包与安全分析扩展,在浏览器侧边栏中即可完成抓包、拦截、修改、重放、规则检测与AI辅助分析的完整工作流。(A lightweight browser extension for traffic capture and security analysis, enabling…
 sushank05/mcp-doorman
A lightweight mcp to prevent poisoning CVE (CVE-2025-54136), researchers hijacking Claude Code/Copilot/Gemini via prompt injection, and hundreds of…
 alex-w-developer/getblocked
Lightweight, local-only MV3 Chrome extension for reducing common third-party web tracking.
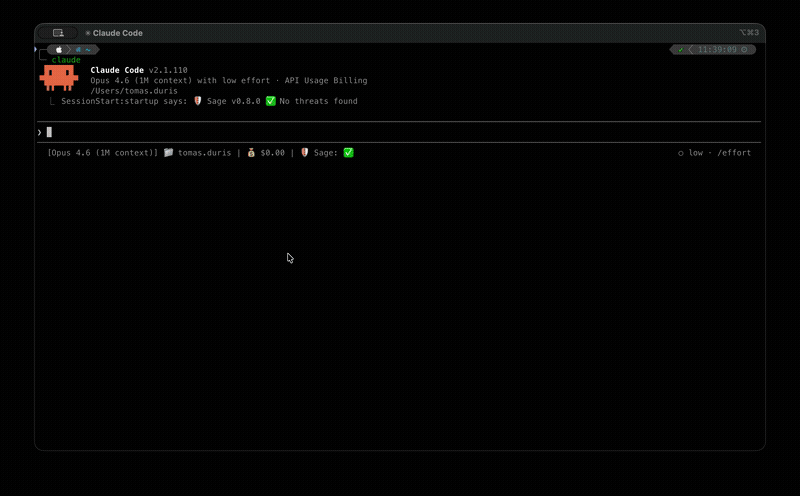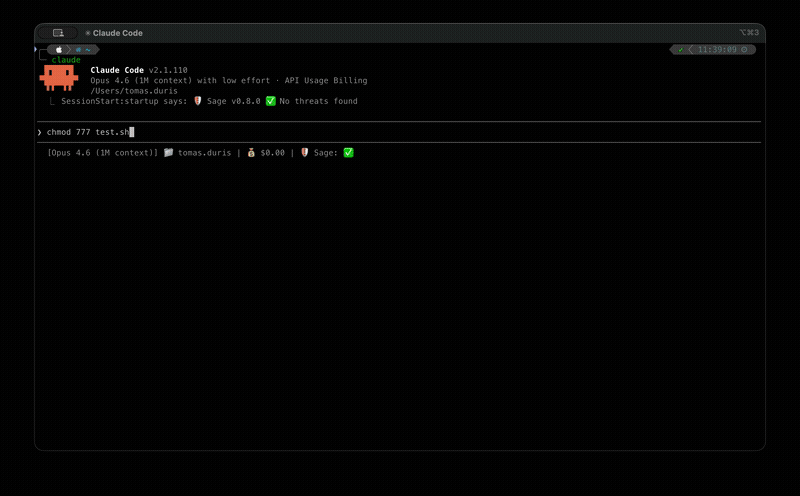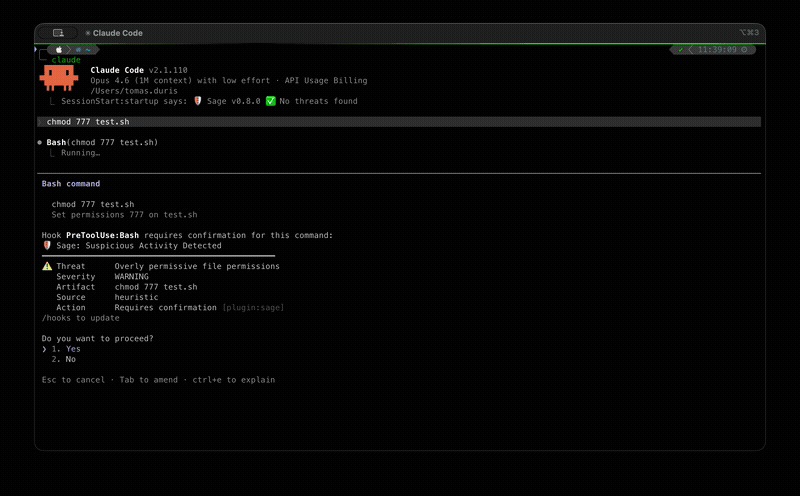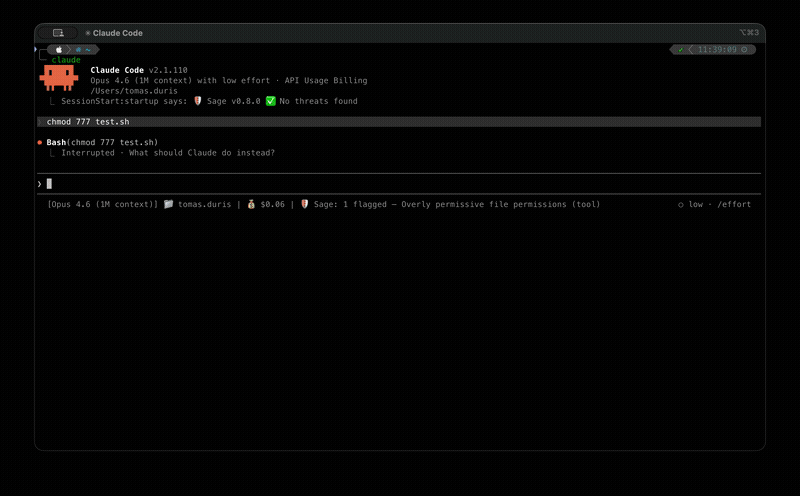 gendigitalinc/sage
Lightweight Agent Detection & Response (ADR) layer for AI agents — guards commands, files, and web requests. Part of Gen Agent Trust Hub.

 sakispat/simple-pentesting
An educational Python toolkit for authorized penetration testing: threaded port scanner, subdomain & directory enumeration, banner grabber and host…
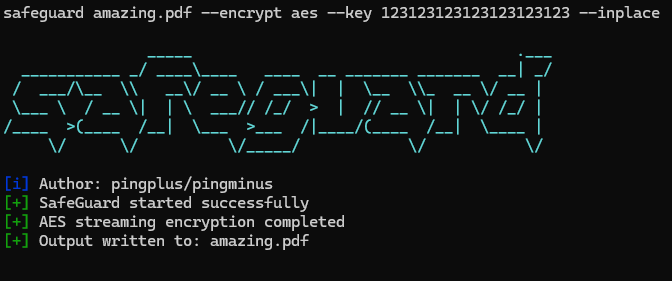 pingpongplus/safeguard
CLI Encryption tool written in Go only for learning purposes (not secure)
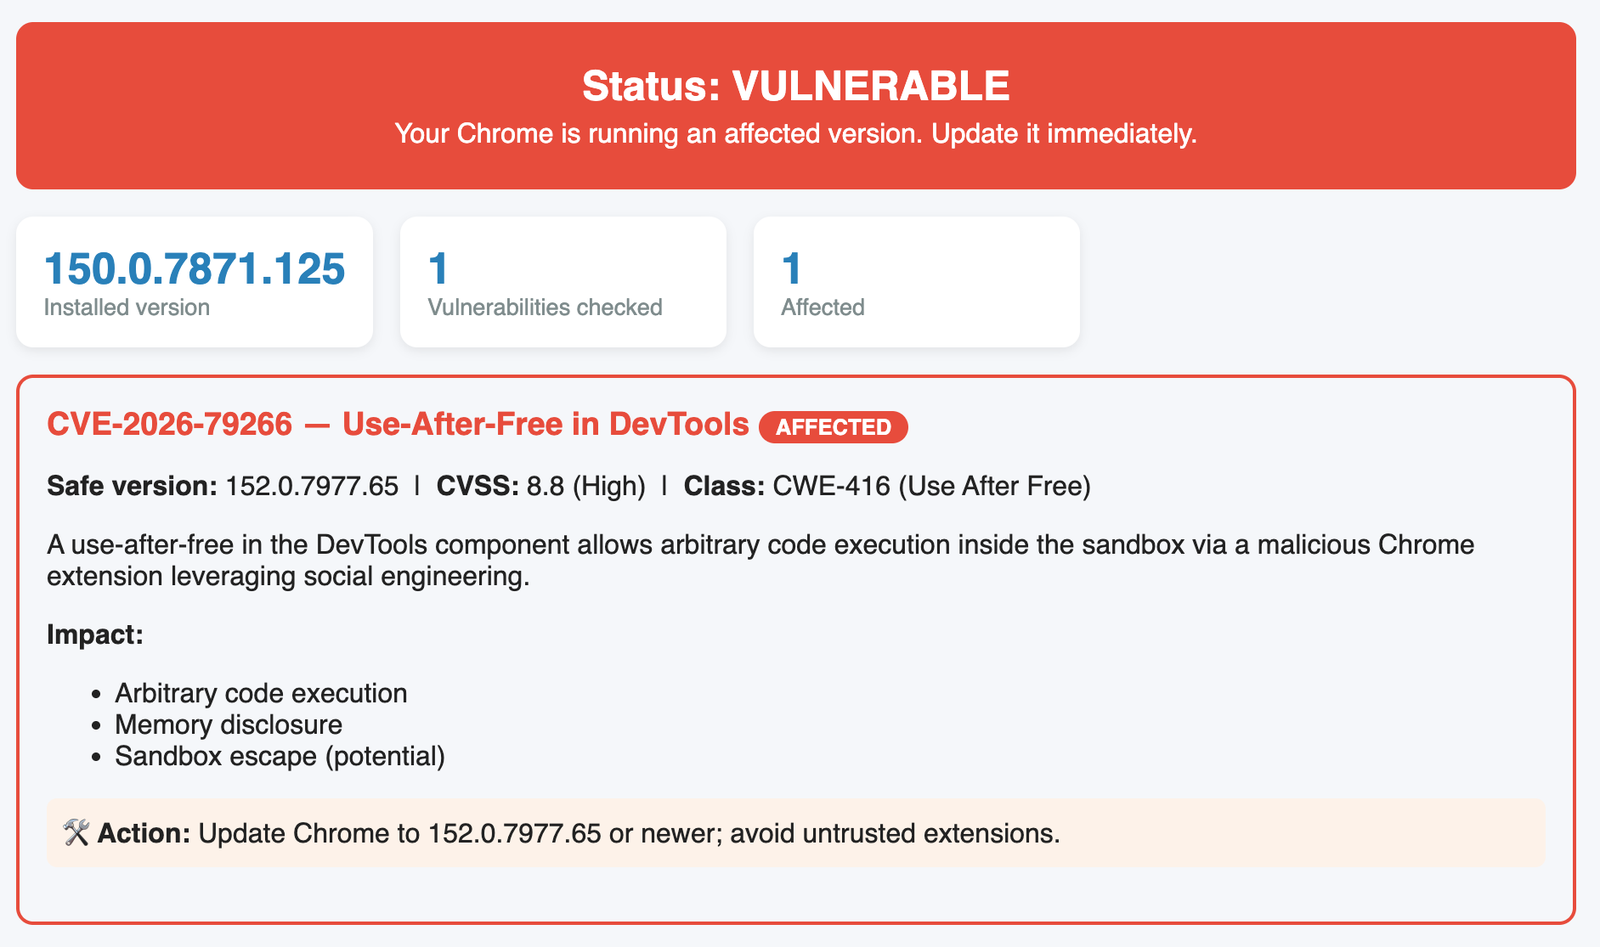 virologi-info/chrome-vuln-scanner
Check for CVE-2026-79266. A use-after-free in the DevTools component allows arbitrary code execution inside the sandbox via a malicious Chrome…
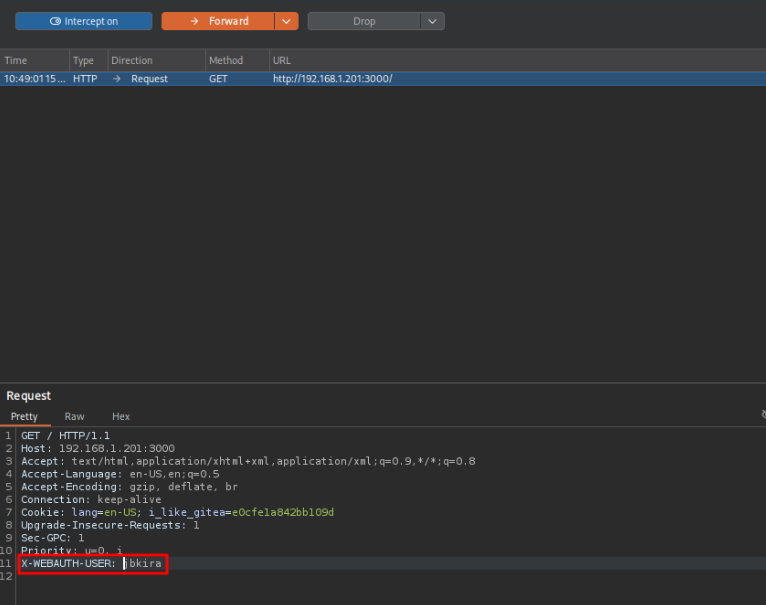 judgedbykira/cve-2026-20896-gitea-authentication-bypass
An explanation and PoC to exploit CVE-2026-20896 Authentication Bypass Vulnerability on Gitea. Being able to steal session tokens for valid users in…
 skimask1690/wisedelete
Windows utility that uses the vulnerable WiseDelfile64.sys driver affected by CVE-2025-66680 to enable kernel-assisted file deletion.
 euva-project/euva
A lightweight hex editor and decompiler to solve your binary file analysis problems.
 george0papasotiriou/cve-2026-6789-stack-buffer-overflow-in-embedded-tls-certificate-parser
Stack buffer overflow PoC in an embedded TLS certificate parser using a crafted X.509 SAN extension for remote code execution on IoT and industrial…