

CheatSheetSeries
 owasp/cheatsheetseries
The OWASP Cheat Sheet Series was created to provide a concise collection of high value information on specific application security topics.
api-securityauthenticationcloud-security+6
33.8k
owasp/cheatsheetseriesThe OWASP Cheat Sheet Series was created to provide a concise collection of high value information on specific application security topics.
 corazawaf/coraza
Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…
 mrwadams/stride-gpt
An AI-powered threat modeling tool that leverages OpenAI's GPT models to generate threat models for a given application based on the STRIDE…
 owasp/securityshepherd
Web and mobile application security training platform
 nvidia/garak
Modular LLM vulnerability scanner that probes for hallucination, data leakage, prompt injection, jailbreaks, and toxicity using static, dynamic, and…
 pnwcomputers/ultimate-cybersecurity-master-guide
This repository provides a centralized resource for operational cyber defense and offense, compiling Theory, Tools, Operating Procedures, and…

 rdelasierra-uy/portfolio
Vitrina profesional: writeups de Hack The Box, informes, casos de estudio GRC (ISO 27001/27002/27005/27035, ISO 31000 + MAGERIT), scripts de…
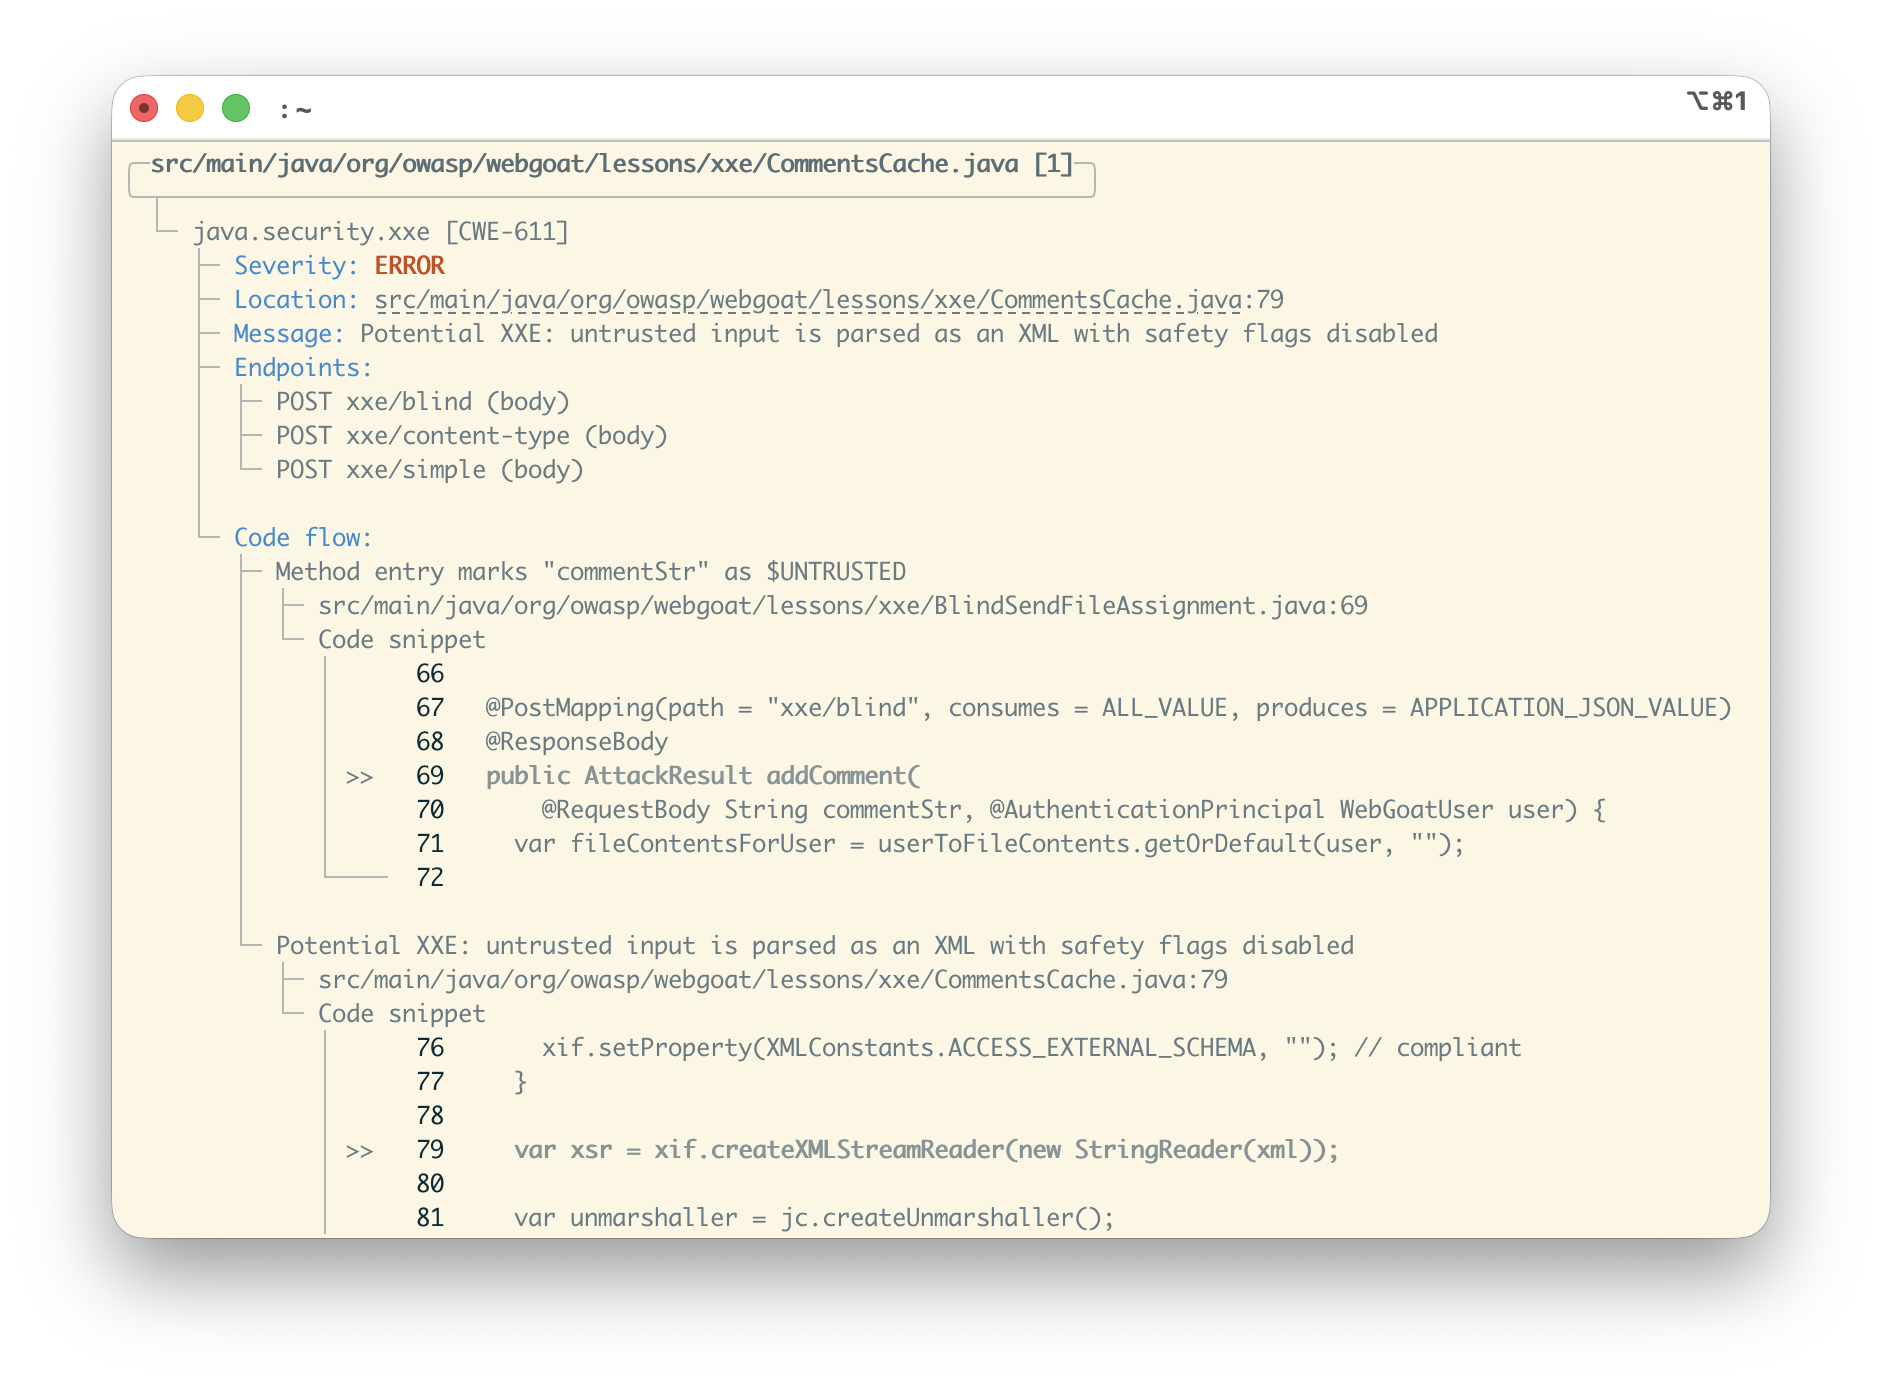 seqra/opentaint
Formal inter-procedural taint analysis engine for application security. Tracks untrusted data across function boundaries, persistence layers, and…
 owasp/open-sammy
Web-based tool for assessing and tracking software security maturity using the OWASP SAMM and DSOMM models, with Docker support and automated mailing.
 owasp/asvs
Application Security Verification Standard
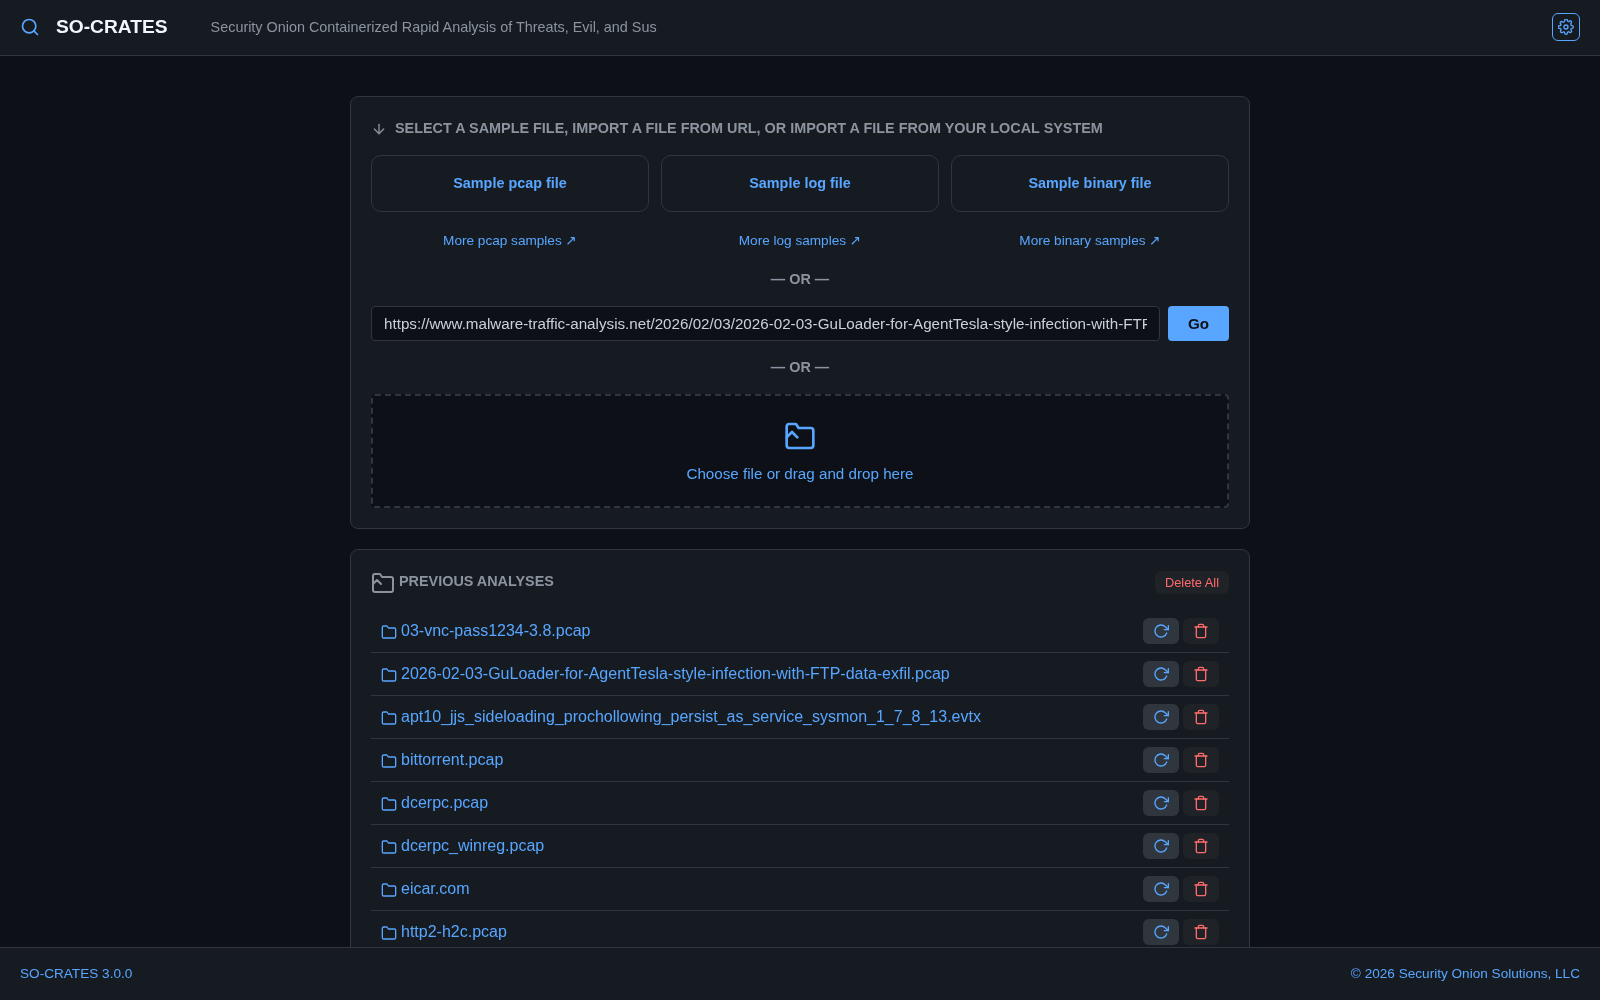 dougburks/so-crates
SO-CRATES: Security Onion Containerized Rapid Analysis of Threats, Evil, and Sus!
 0xblackash/cve-2026-101767
Advisory and technical research analysis of CVE-2026-101767, a critical unauthenticated RCE in Oracle E-Business Suite Application Object Library,…
 rknf404/chromium-hardening-guide
Harden chromium (somewhat) for privacy and security (and performance)
 owasp/secure-headers-project
OWASP knowledge base and validator for HTTP security response headers, providing recommendations, statistics, and automated configuration checks.
 leebaird/engagement-mgr
Engagement Manager is a web application for tracking offensive security engagements. It features a modern UI, built with Next.js, Prisma, and…
 owasp/mastg
Comprehensive OWASP guide for mobile app security testing, reverse engineering, and verifying MASVS/MASWE weaknesses through static, dynamic, and…
 owasp/wstg
The Web Security Testing Guide is a comprehensive Open Source guide to testing the security of web applications and web services.
 jschauma/emudhra
Example programs in Go, Java, Node, Perl, Python, Ruby, Rust, and curl that test whether a TLS trust store rejects connections to known-bad eMudhra…