

strix
 usestrix/strix
Open-source AI penetration testing tool to find and fix your app’s vulnerabilities.
ai-securityapi-security-testingcode-analysis+9
64.4k
usestrix/strixOpen-source AI penetration testing tool to find and fix your app’s vulnerabilities.
 semgrep/semgrep
Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.
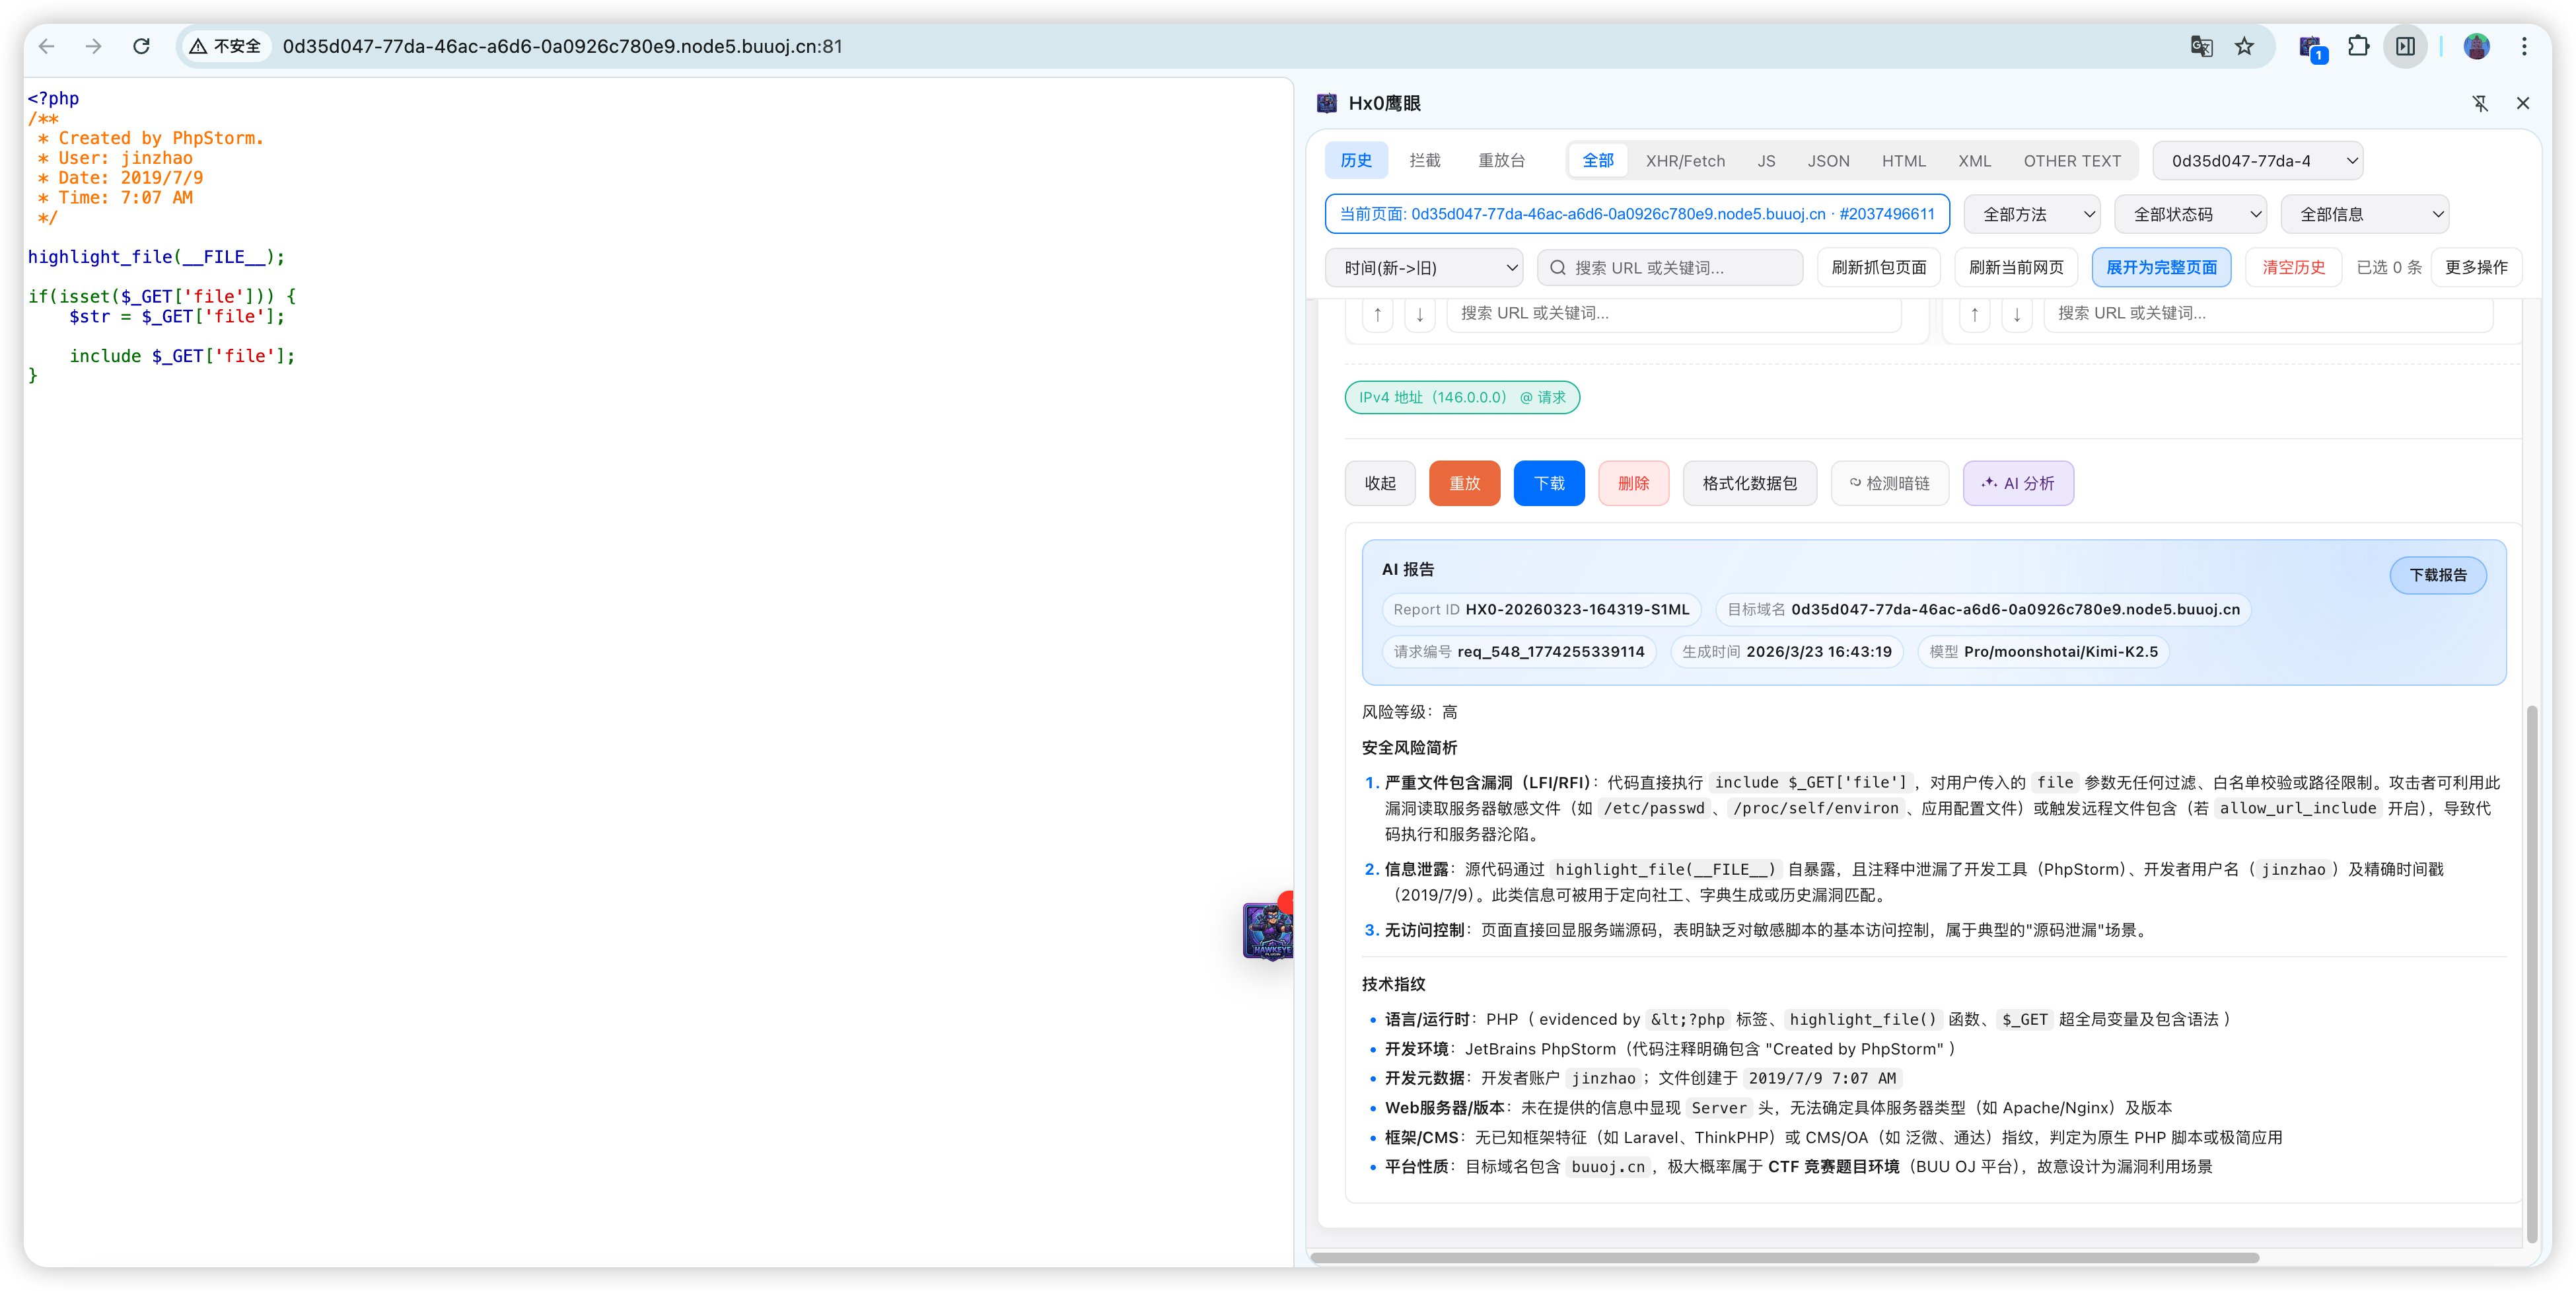 asaotomo/hx0-hawkeye
一个轻量级浏览器抓包与安全分析扩展,在浏览器侧边栏中即可完成抓包、拦截、修改、重放、规则检测与AI辅助分析的完整工作流。(A lightweight browser extension for traffic capture and security analysis, enabling…
 isaca0315/cve-2026-65013-bola-idor
Reproducible BOLA/IDOR PoC against Onlook's tRPC API (CVE-2026-65013), with a 12-step exploit chain, vulnerable and patched Docker targets, and…
 elastic/agent-skills
Official Elastic Skills
 owasp/crapi
Deliberately vulnerable microservices API designed for hands-on training in the OWASP API Security Top 10 risks, with built-in challenges and a…
 corazawaf/coraza
Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…
 j3ssie/dynast-bench
A DAST benchmark of intentionally-vulnerable apps with ground-truth answer keys for scoring scanners
 punitdarji/gitlab-cve-2026-19478
Dockerized exploit lab and script for CVE-2026-19478, a critical unauthenticated GitLab GraphQL code injection enabling arbitrary Ruby method calls,…
 curtail-inc/hello-regrade-security
Find the vulnerability your tests were never written to catch. A ReGrade demo modeling CVE-2023-5968: catch a password-hash leak by comparing an app…
 keyvaluesoftwaresystems/agent-opfor
Open-source adversary emulation for AI agents and MCP servers.
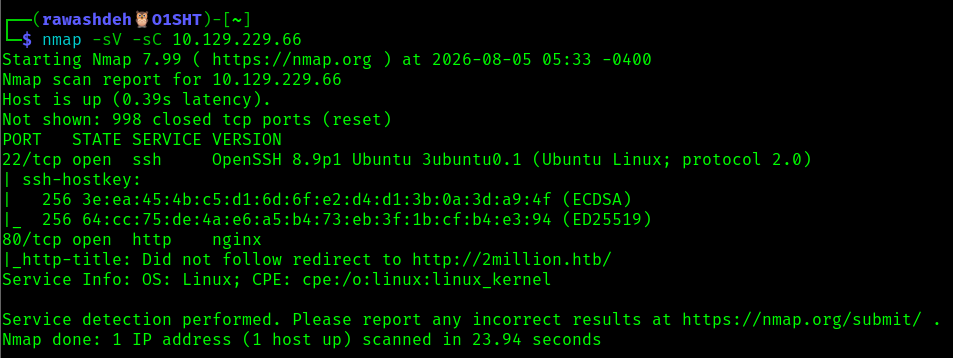 abedallarawashdeh/htb-twomillion-machine
Hack The Box TwoMillion machine writeup — JWT/invite-code bypass, IDOR, command injection, and CVE-2023-0386 privilege escalation.
 loaxert/cve-2025-59528-poc
PoC for CVE-2025-59528 used to achieve remote code execution on the Silentium machine at HTB
 imzanggg/cve-2026-24055-oauth-langfuse
 owasp/agent-security-regression-harness
Executable security regression testing for agentic applications and MCP-integrated systems.
 ananay/wp2shell-lab
Validation target: minimal WordPress core slice reproducing the wp2shell (CVE-2026-63030 + CVE-2026-60137) REST-to-SQLi chain
 oscerd/cve-2026-46592
Reproducer for CVE-2026-46592: Apache Camel camel-cxf operationName header injection redirecting the invoked SOAP operation (confused deputy) from a…
 oscerd/cve-2026-49099
PoC reproducer for CVE-2026-49099 (Apache Camel camel-salesforce): the non-Camel-prefixed sObjectQuery header escapes the HTTP header filter and…