
LBFH
 naimkowshik/lbfh
About All in one tool for Information Gathering, Vulnerability Scanning and Crawling. A must have tool for all penetration testers
educationexploitationhash-analysis+9
725 years ago
naimkowshik/lbfhAbout All in one tool for Information Gathering, Vulnerability Scanning and Crawling. A must have tool for all penetration testers
 ekitji/siem
Curated SIEM queries and techniques for offensive discovery of Windows privilege escalation, misconfigured ACLs, services, scheduled tasks, and…
 sakispat/simple-pentesting
An educational Python toolkit for authorized penetration testing: threaded port scanner, subdomain & directory enumeration, banner grabber and host…
 fuzzingbrain/fuzzingbrain-bench
A benchmark for LLM-driven bug discovery: 77 challenges across 43 open-source projects (C/C++/Java).
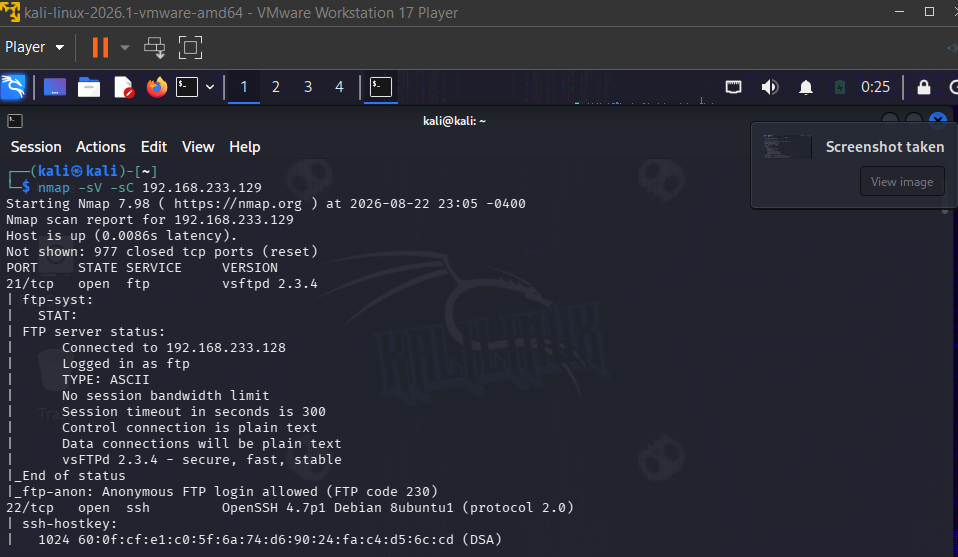 rsakthikumar-cmd/metasploitable2-vsftpd-writeup
Exploiting the vsftpd 2.3.4 backdoor (CVE-2011-2523) on Metasploitable2 — a hands-on pentesting lab writeup covering recon, exploitation, and…
 hyp3rlinx/pstrojanfile
Unfixed Windows PowerShell Filename Code Execution POC
 verylazytech/cve-2025-29306
Proof-of-concept exploit for FoxCMS v1.2.5 remote code execution via the index.html component, with FOFA dork for target discovery.
 jeevananand1202/penetration-test
Full penetration test report against `IP` (Ubuntu VM). Attack chain: directory enumeration → backup file discovery → password cracking → CMS file…
 yagnikkrish/metasploitable-penetration-testing-lab
Controlled penetration testing lab demonstrating CVE-2011-2523 exploitation and mitigation techniques.
 siv-nick/whocord
Scans Discord links across mutual guilds to extract profiles, cross‑references 700+ sites, searches usernames with 30+ tools, and generates an…
 azqzazq1/lid
LID — Linux Integrity Drift: Bypassing AppArmor via eBPF pathname rewriting. Pre-LSM syscall argument manipulation with zero audit footprint. "Linux…
 mind2hex/cve-2022-39986-raspap-2.8.0-2.8.7-rce
bash script for automated discovery and exploitation of machines with the CVE-2022-39986 vulnerability
 dungsocool/cve-2017-11610
Step-by-step exploit writeup for CVE-2017-11610 (Supervisord XML-RPC RCE) with attack surface analysis, namespace traversal discovery, and…
 hamed233/cybersecurity-mastery-roadmap
A comprehensive, step-by-step guide to mastering cybersecurity from beginner to expert level with curated resources, tools, and career guidance
 0x4m4/hexstrike-ai
MCP server enabling AI agents to autonomously execute 150+ cybersecurity tools for automated penetration testing, vulnerability discovery, bug bounty…
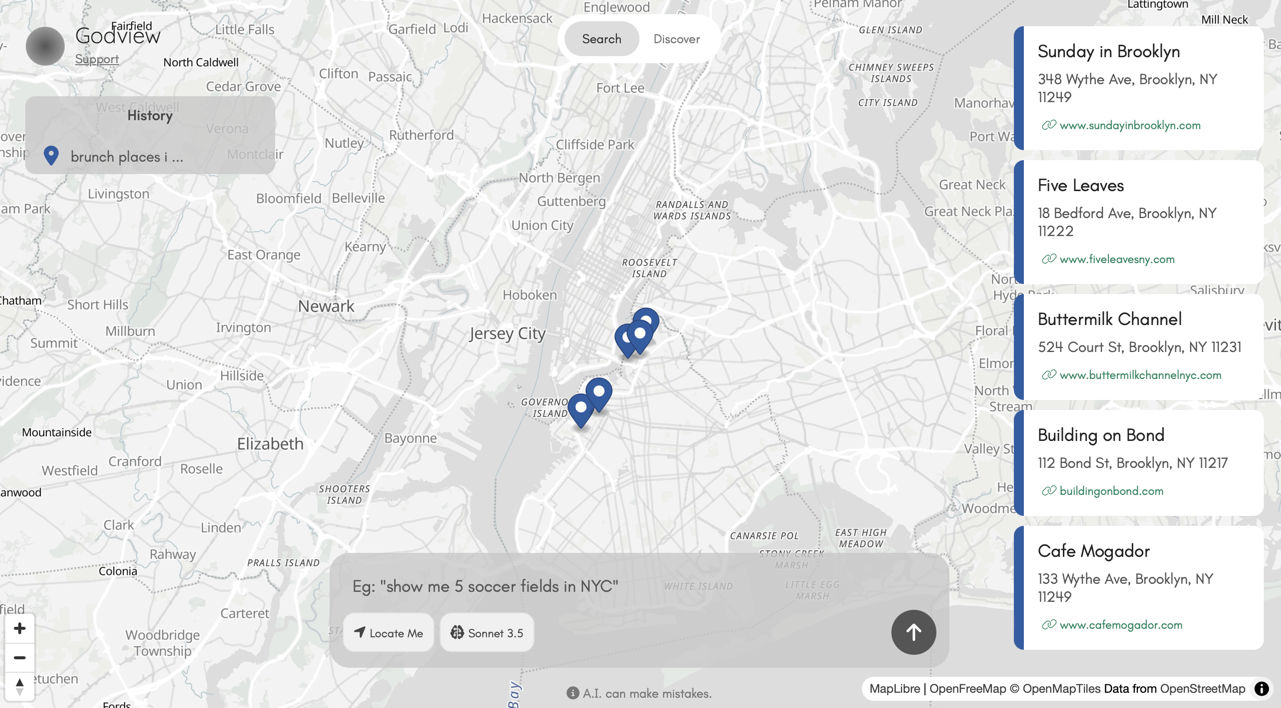 space0blaster/smartmap
LLM based map for research, exploration and discovery.
 frishtik/osint-tools-mcp-server
MCP server exposing multiple OSINT tools for AI assistants like Claude
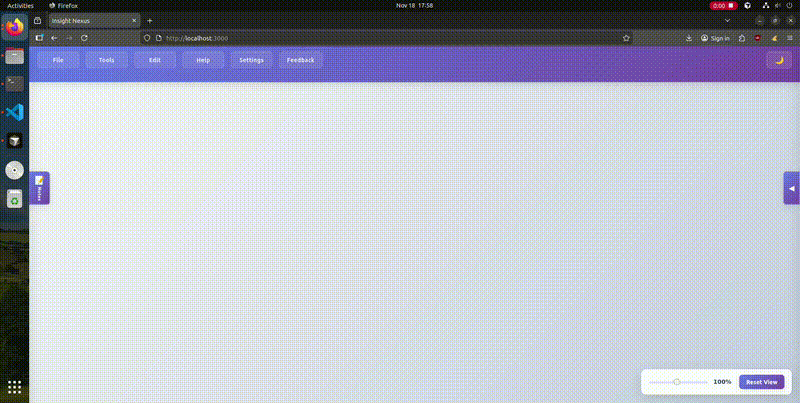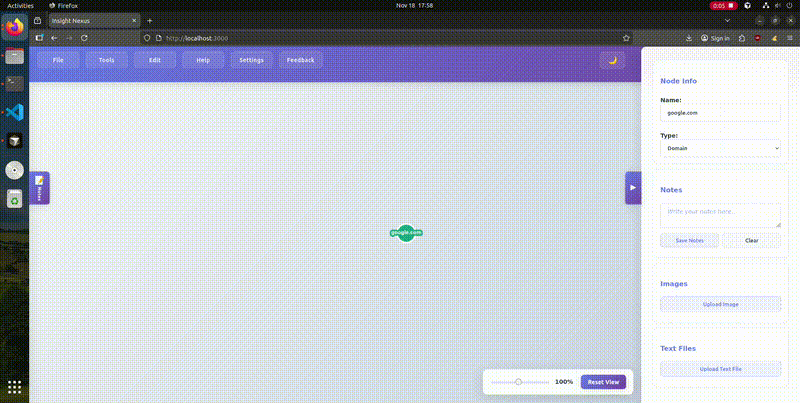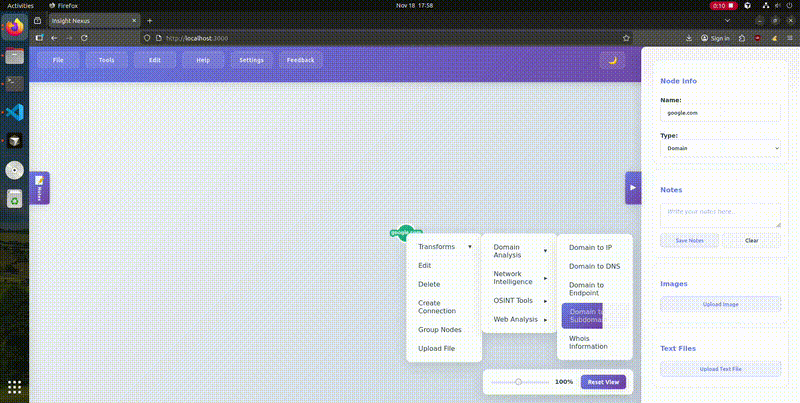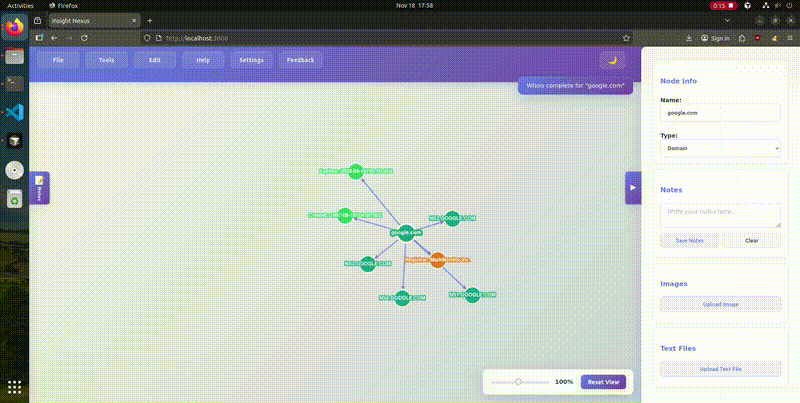 cyberintel-labs/insightsnexus
OSINT Graph Investigation Application