

ida_bochs_windows
 therealdreg/ida_bochs_windows
Helper script for Windows kernel debugging with IDA Pro on native Bochs debugger (including PDB symbols)
binary-analysisdebuggersdynamic-code-analysis+1
62
therealdreg/ida_bochs_windowsHelper script for Windows kernel debugging with IDA Pro on native Bochs debugger (including PDB symbols)
 sentinel-one/peafl64
Static Binary Instrumentation tool for Windows x64 executables
 ghostvectoracademy/dllhijackhunter
Automated DLL Hijacking Discovery, Validation, and Confirmation. Turning local misconfigurations into weaponized, confirmed attack paths.
 rogerorr/nttrace
An strace-like program for the Windows 'native' API
 kaisonox/apiscope
An API hooking framework for intercepting and monitoring Windows applications
 microsoft/detours
Runtime Windows API interception library for hooking, monitoring, and instrumenting function calls. Supports binary rewriting and DLL injection,…
 nccgroup/winstrument
Winstrument is a framework of modular scripts to aid in instrumenting Windows software using Frida for reverse engineering and attack surface…
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
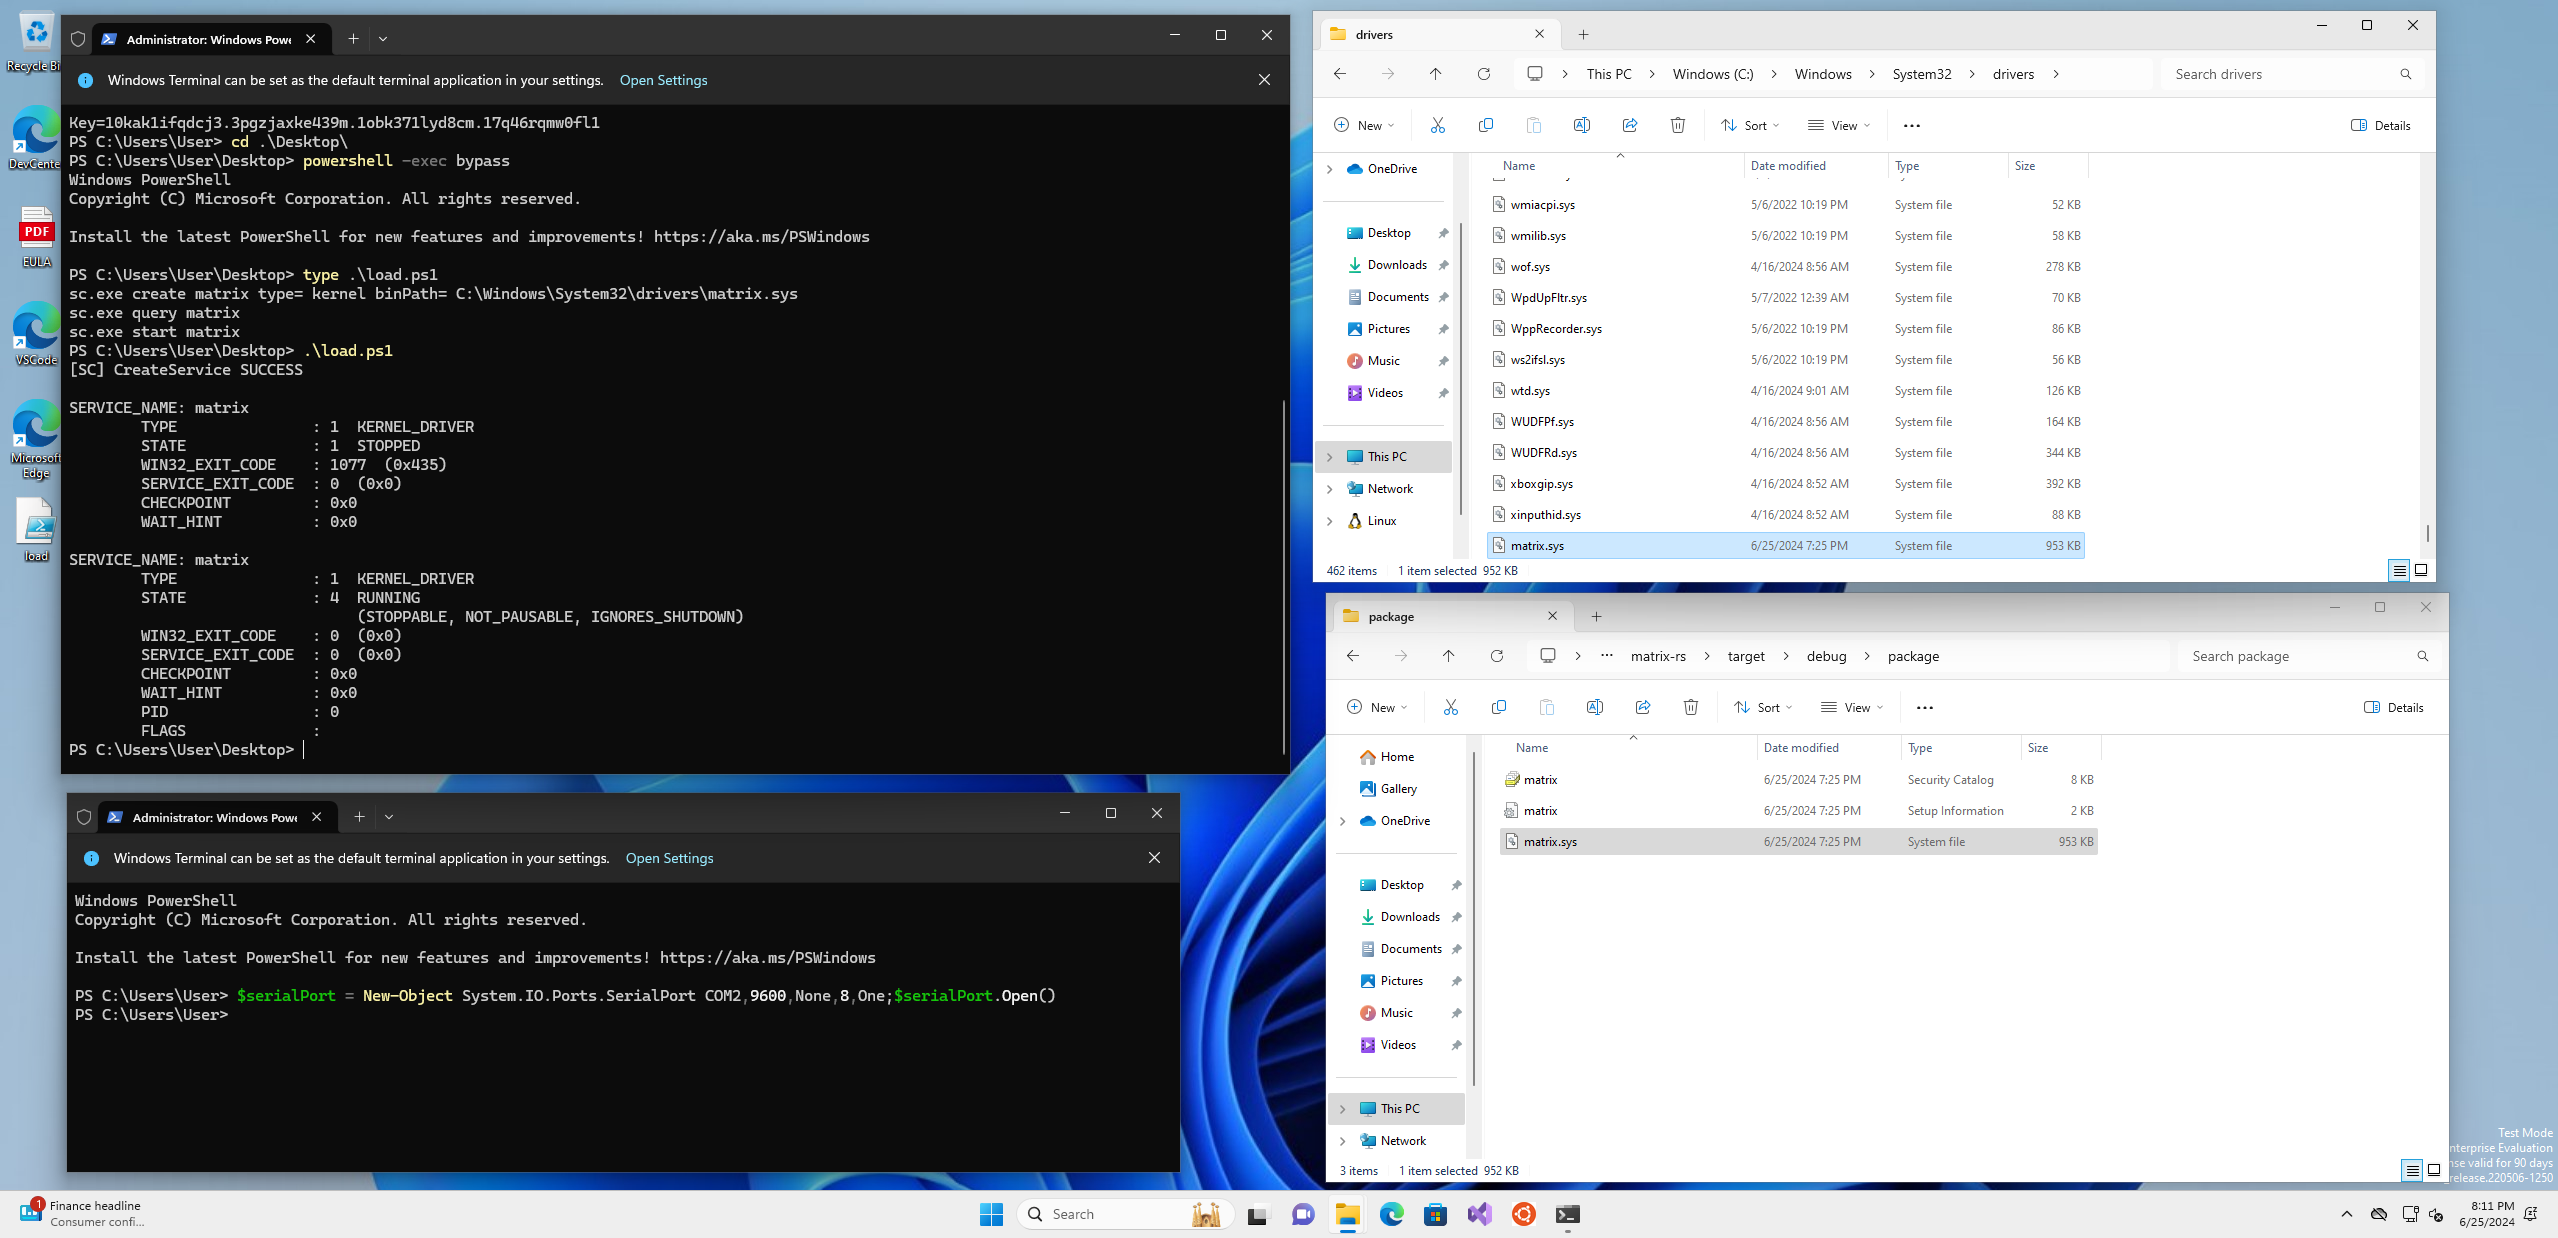 memn0ps/matrix-rs
Rusty Hypervisor - Windows Kernel Blue Pill Type-2 Hypervisor in Rust (Codename: Matrix)
 nccgroup/dibf
Windows NT ioctl bruteforcer and modular fuzzer
 skylined/bugid
Detect, analyze and uniquely identify crashes in Windows applications
 advdebug/brovan
User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…
 pizlonator/fil-c
Fil-C: completely compatible memory safety for C and C++
 microsoft/windbg-samples
Sample extensions, scripts, and API uses for WinDbg.
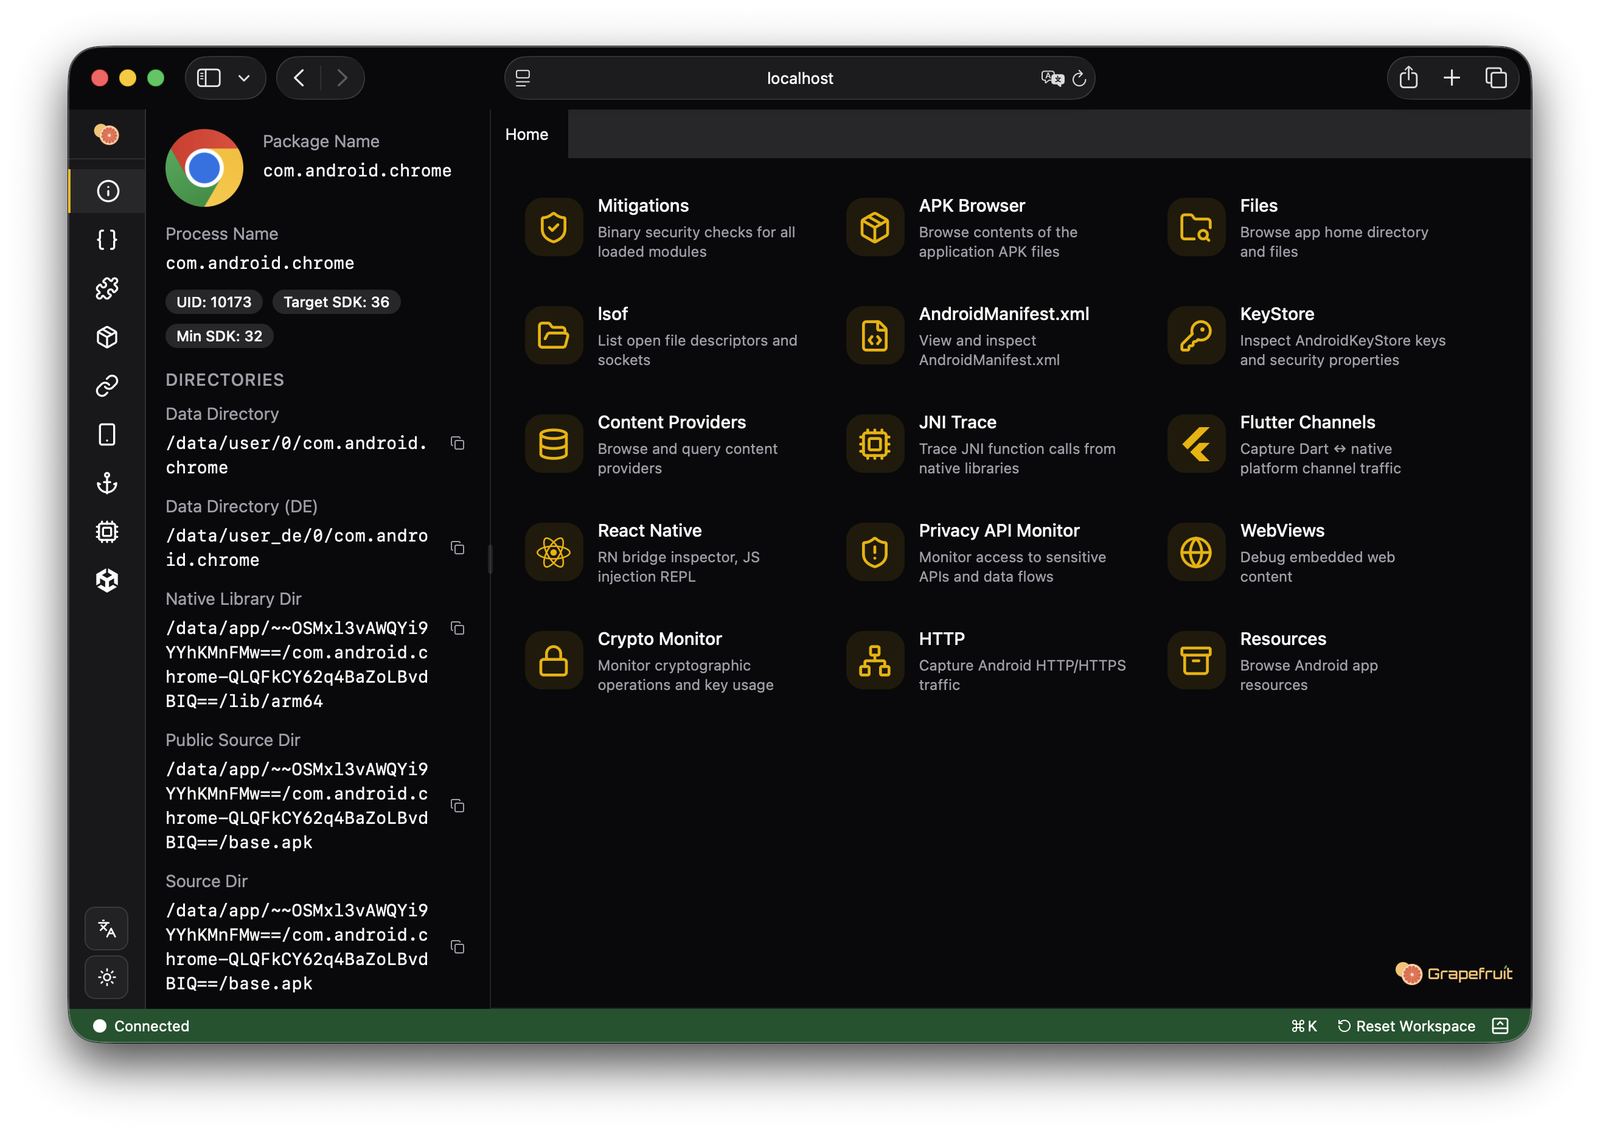 chichou/grapefruit
Open-source mobile security testing suite for iOS and Android. Previously Passionfruit
 rust-fuzz/cargo-fuzz
Cargo subcommand for coverage-guided Rust fuzzing with libFuzzer: create and run fuzz targets, minimize failures and corpora, and report coverage.
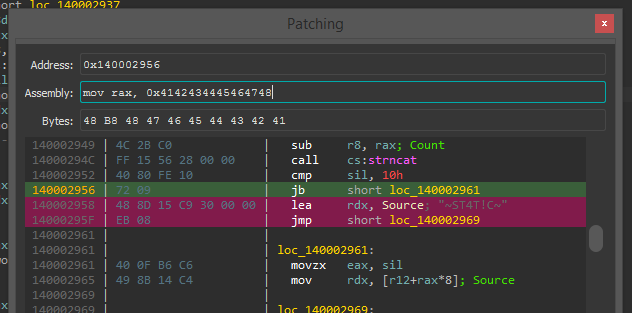 gaasedelen/patching
An Interactive Binary Patching Plugin for IDA Pro
 lifting-bits/sleigh
CMake build of Ghidra's SLEIGH processor specification library, providing standalone disassembly and p-code lifting engines for reverse engineering…