
Archived
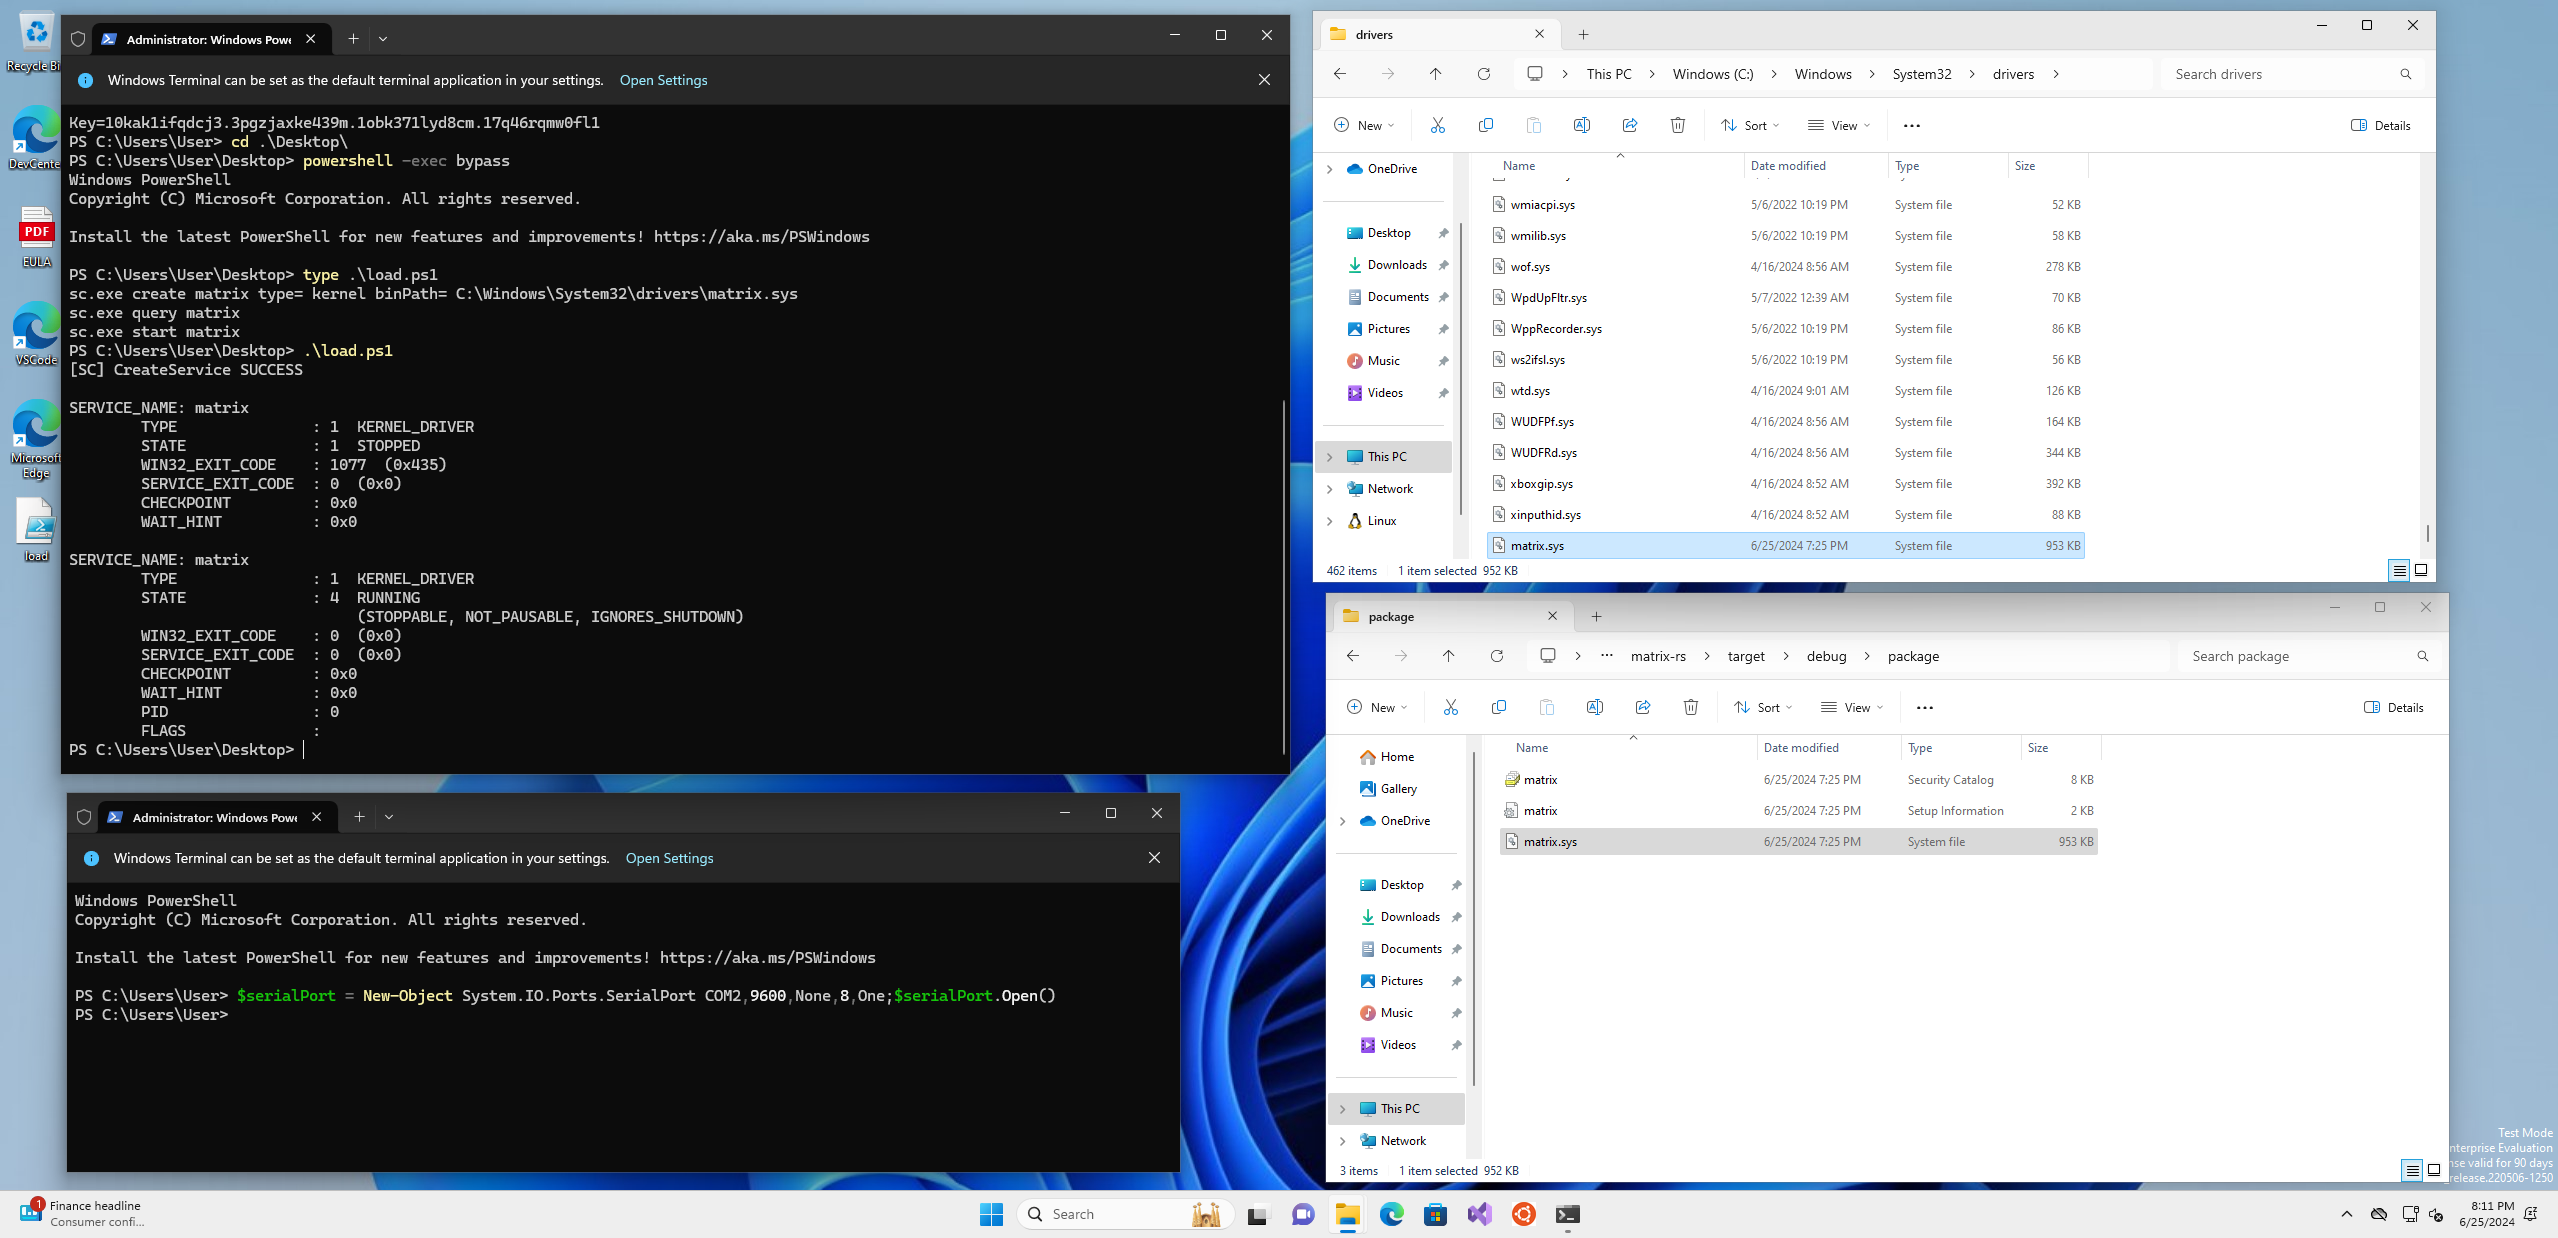
matrix-rs
 memn0ps/matrix-rs
Rusty Hypervisor - Windows Kernel Blue Pill Type-2 Hypervisor in Rust (Codename: Matrix)
dynamic-code-analysiseducationids-ips-evasion+3
359
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
 advdebug/brovan
User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…
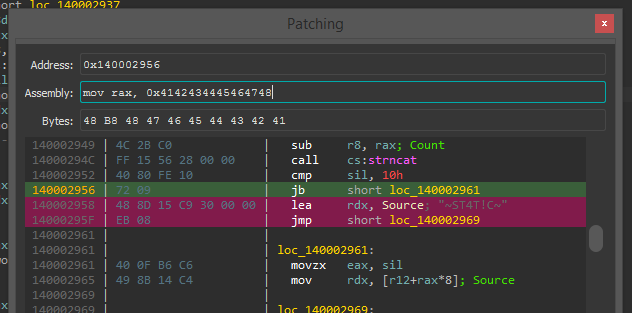 gaasedelen/patching
An Interactive Binary Patching Plugin for IDA Pro
 nccgroup/dibf
Windows NT ioctl bruteforcer and modular fuzzer
 veridiff/veridiff
Dynamic branch-divergence finder for native code -- traces two Frida executions and finds the exact instruction where they diverge.
 pizlonator/fil-c
Fil-C: completely compatible memory safety for C and C++
 awslabs/snapchange
Lightweight fuzzing of a memory snapshot using KVM
 cornerpirate/java-stager
A PoC Java Stager which can download, compile, and execute a Java file in memory.
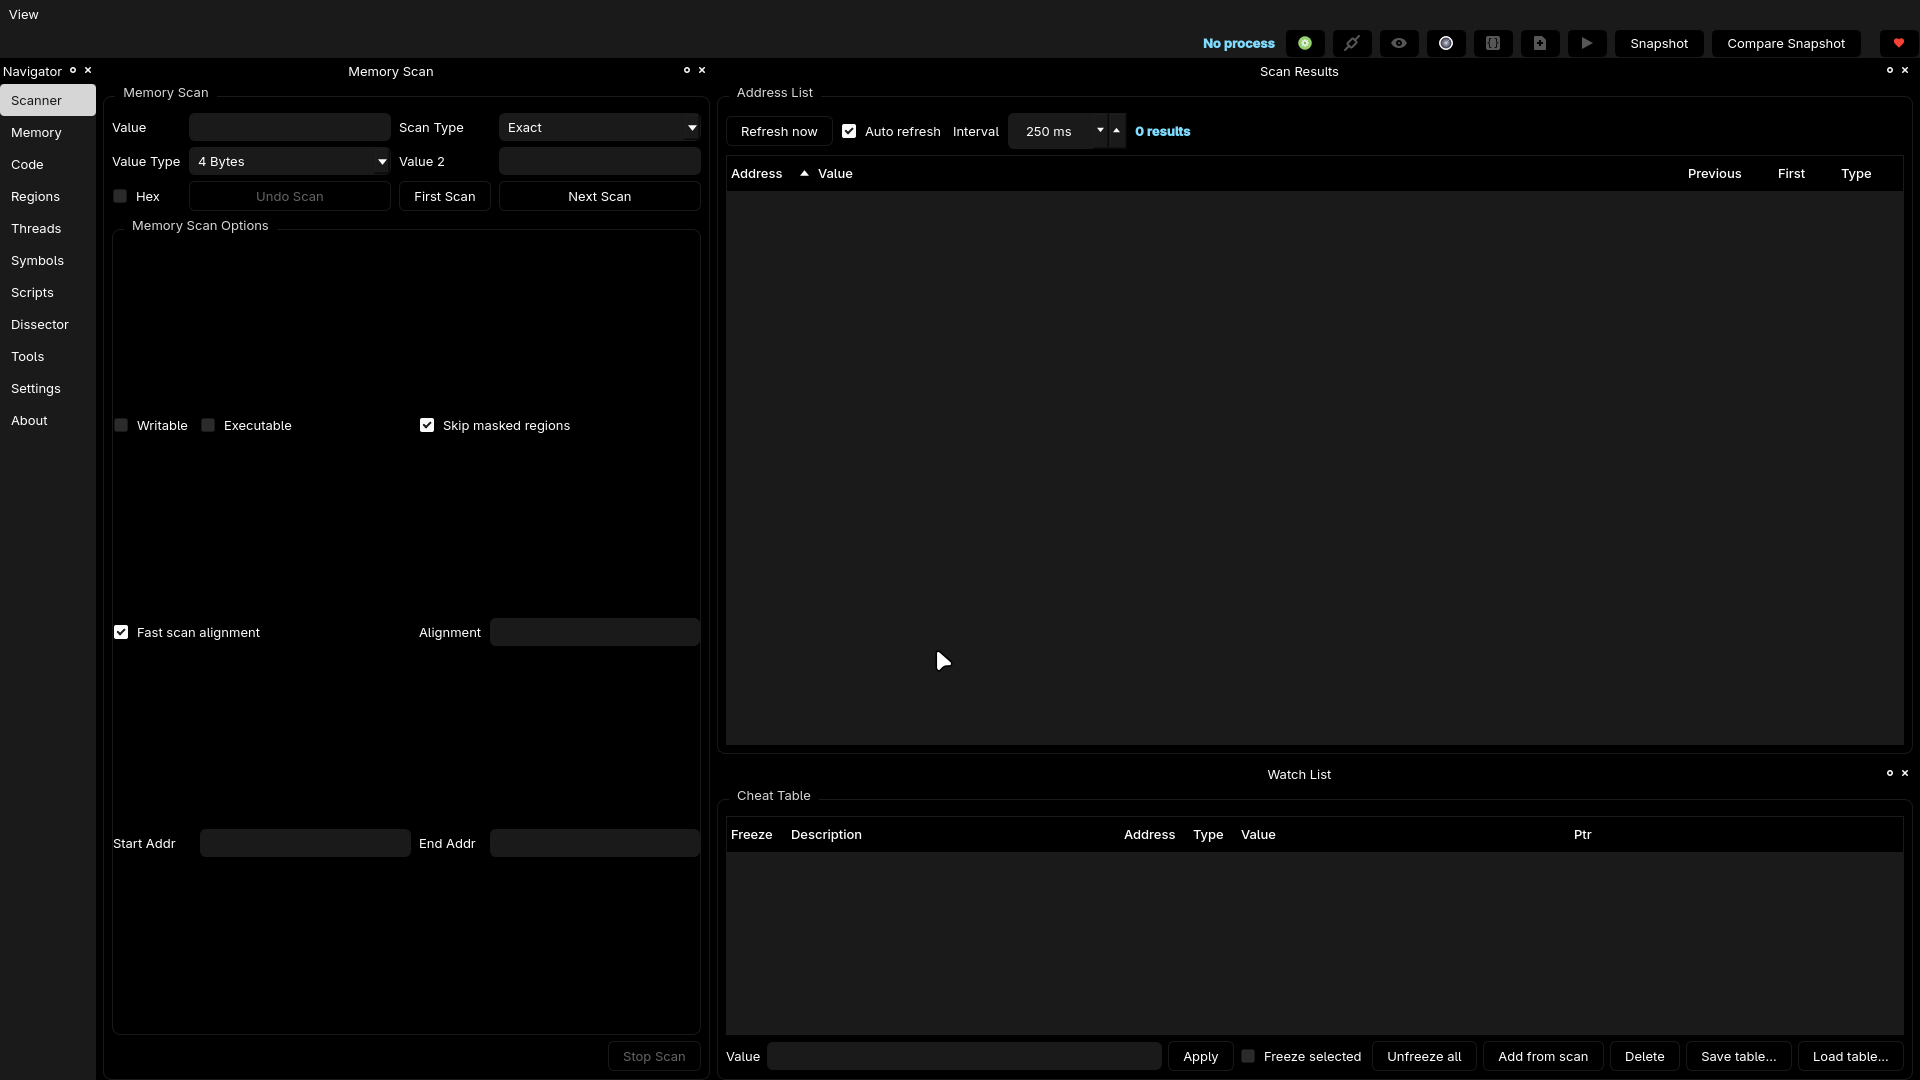 kashithecomfy/comfyengine
ComfyEngine is a memory exploration toolkit built for people who need to monitor, patch, and script a running process.
 0x3c3e/slides
CodeQL + DTrace = Memory Disclosure Vulnerabilities in XNU
 momalab/icsfuzz
Instrumented fuzzer for PLC-based ICS control applications, targeting Codesys runtime on Wago controllers to uncover memory corruption and…
 whatswrongandwhy/ptrace
Linux ptrace-based process tracing and debugging utility for inspecting system calls, memory, and program execution flow.
 tca-iscas/cooper-ndss-2022
A tool for effective testing the binding layer of scripting languages