
Cooper-ndss-2022
 tca-iscas/cooper-ndss-2022
A tool for effective testing the binding layer of scripting languages
binary-analysisdynamic-code-analysisfuzzing+2
81
tca-iscas/cooper-ndss-2022A tool for effective testing the binding layer of scripting languages
 dvyukov/centipede
Distributed coverage-guided fuzzing engine compatible with libFuzzer targets; scales to thousands of concurrent jobs, uses sanitizers and corpus…
 0xbigshaq/apatchy
Fuzzing Framework for Modules in Apache HTTPD Server
 hasherezade/pesieve-go
Golang bindings for PE-sieve
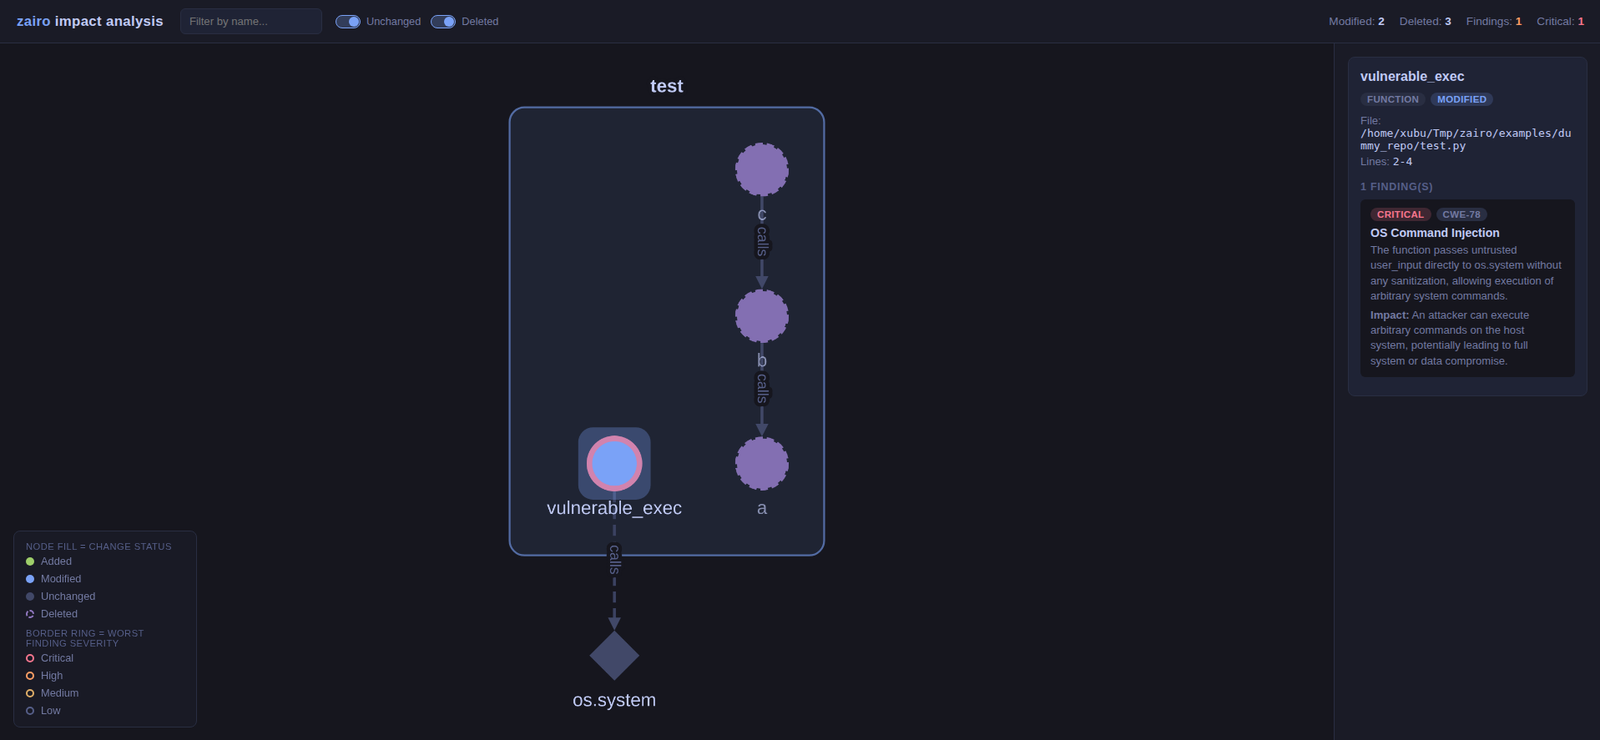 iamavu/zairo
Scans code diffs with context to build an impact graph and uses LLMs to find vulnerabilities, supporting multi-repo scans and CI gating with SARIF…
 abubakar-shahid/cve-2024-36886
Academic research on N-Day Linux kernel vulnerabilities, analyzing CVE-2024-36886 in the TIPC networking subsystem, lifecycle, impact, and mitigation…
 de4dot/de4dot
.NET deobfuscator and unpacker.
 lolcaken/javascript-deobfuscator
Deobfuscator for javascript-obfuscator 5.x output (string arrays, control-flow flattening, self-defending, RC4/base64)
 sentinel-one/peafl64
Static Binary Instrumentation tool for Windows x64 executables
 google/path-auditor
Runtime libc function auditor that detects file access race conditions and symlink vulnerabilities by hooking filesystem syscalls via LD_PRELOAD,…
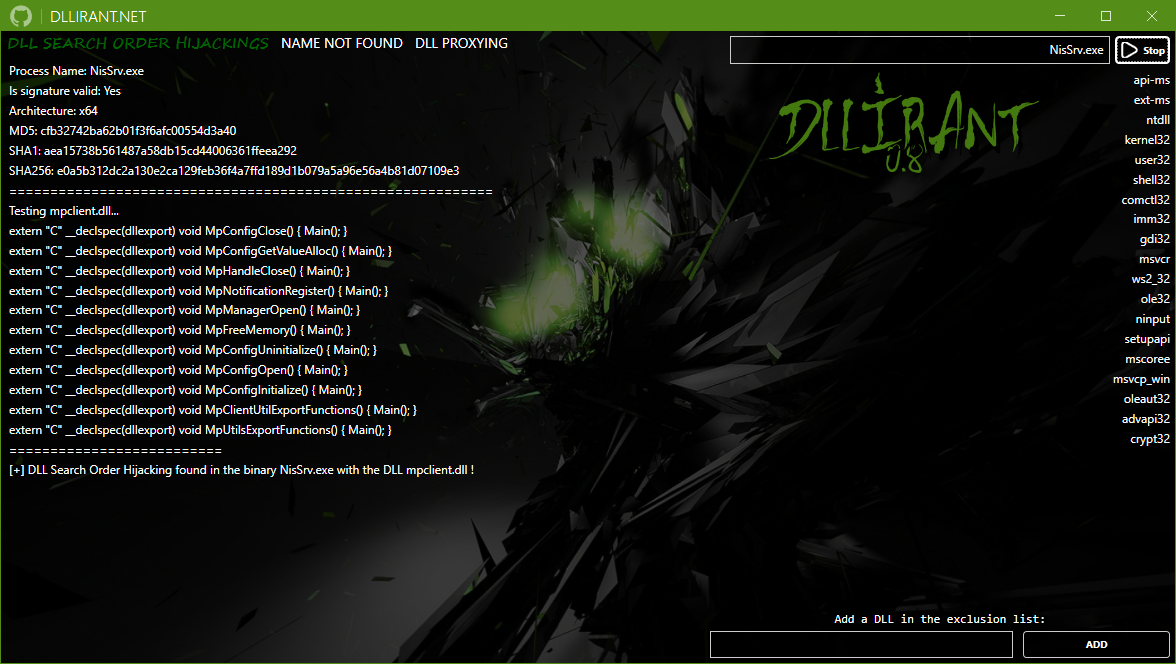 redteamsocietegenerale/dllirant
DLLirant is a tool to automatize the DLL Hijacking researches on a specified binary.
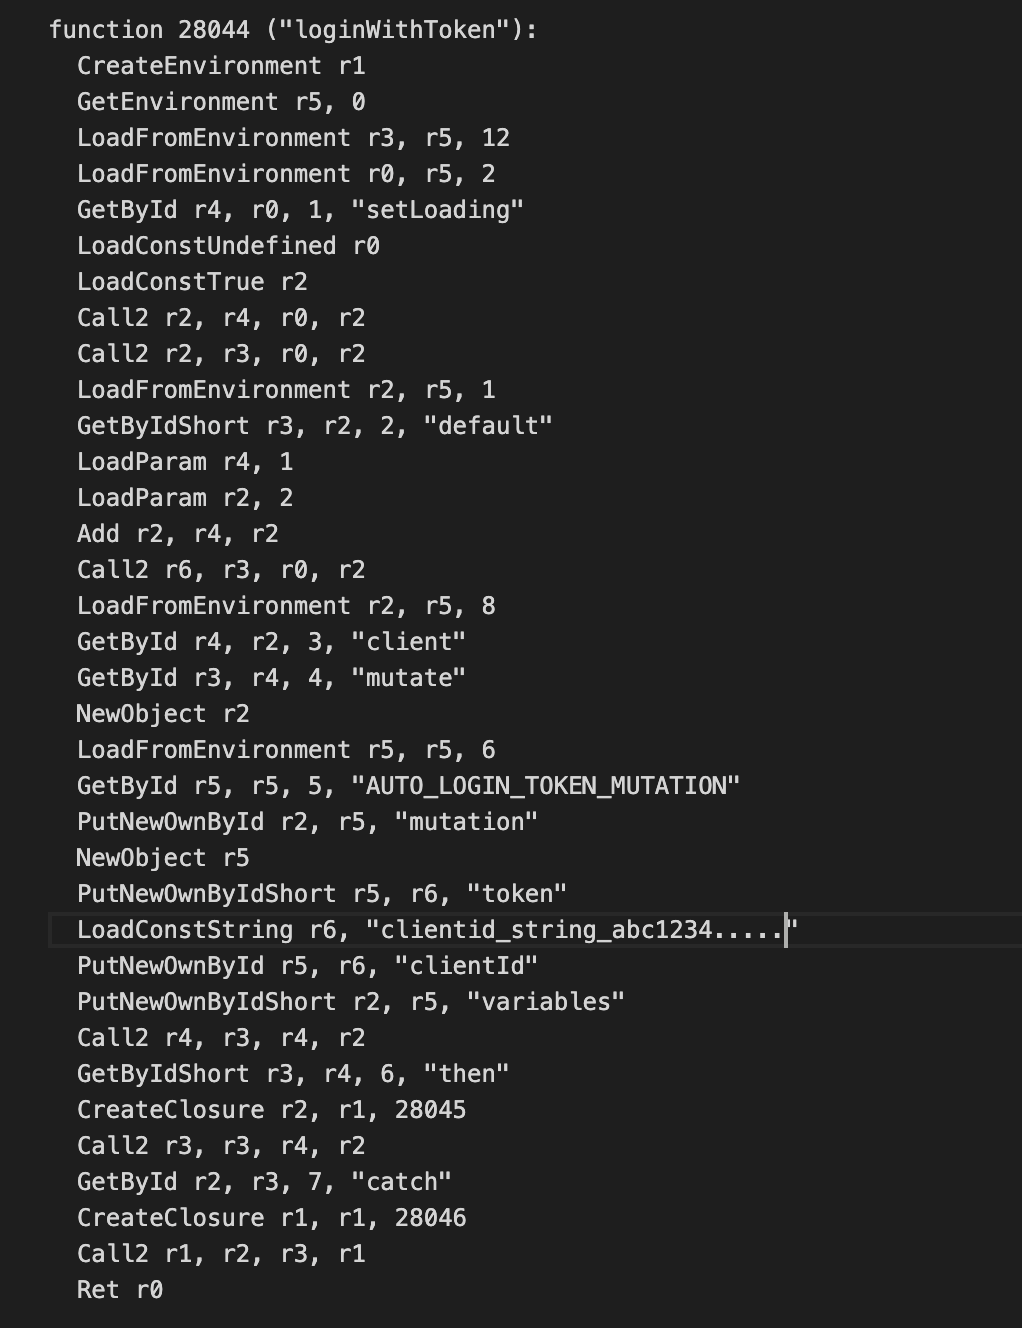 symbioticsec/hermes-decomp
A powerful decompiler that lets you reverse-engineer React Native mobile apps by converting their compiled Hermes bytecode (.hbc) files back into…
 robertdfrench/ifuncd-up
GNU IFUNC is the real culprit behind CVE-2024-3094
 1rhino2/fnprint
match functions in binaries by what they do, not what their bytes look like. behavioral function fingerprinting via microexecution.
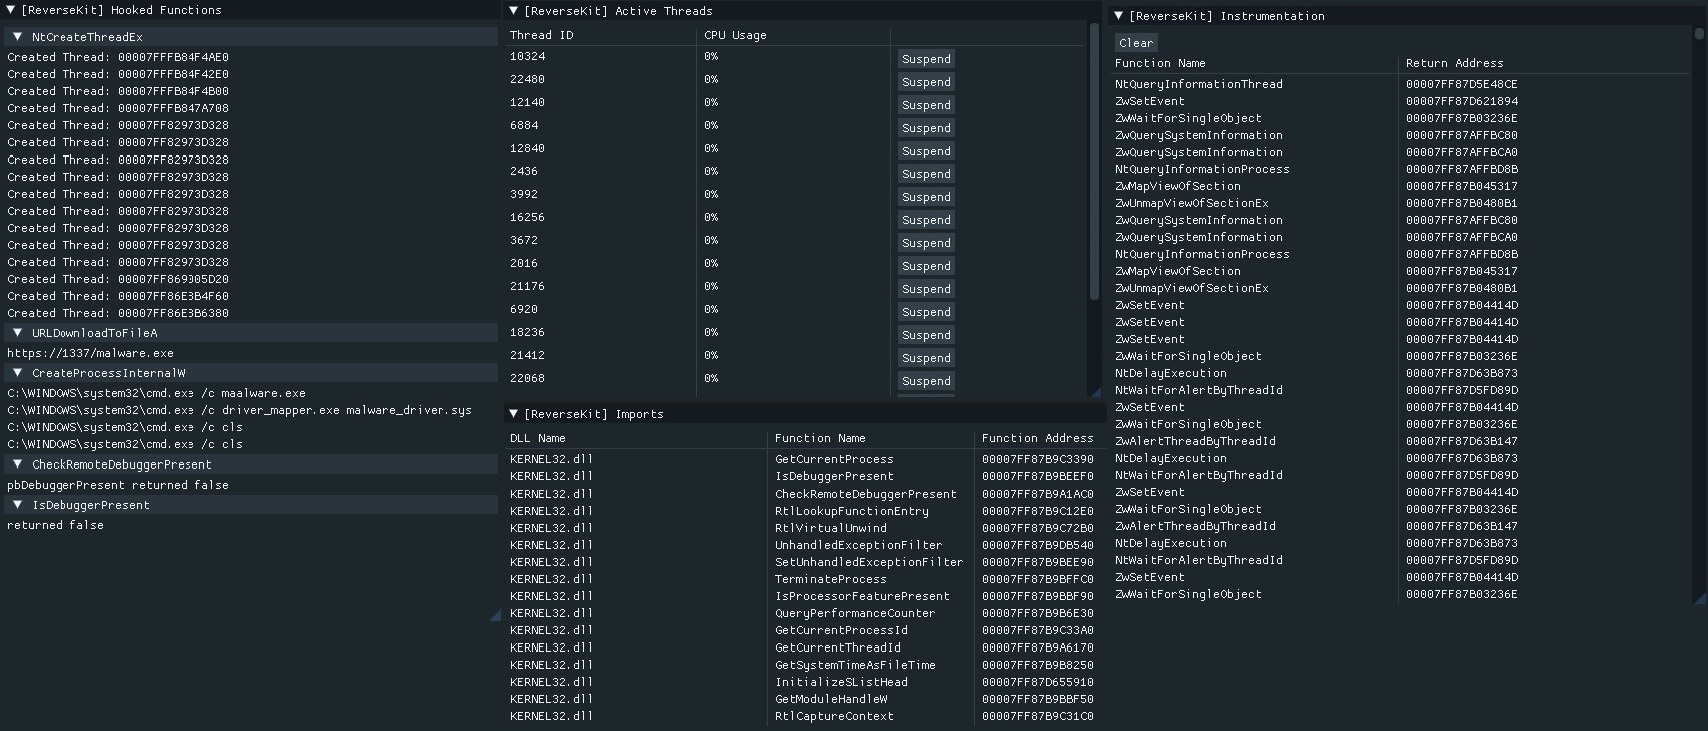 zer0condition/reversekit
x64 Dynamic Reverse Engineering Toolkit
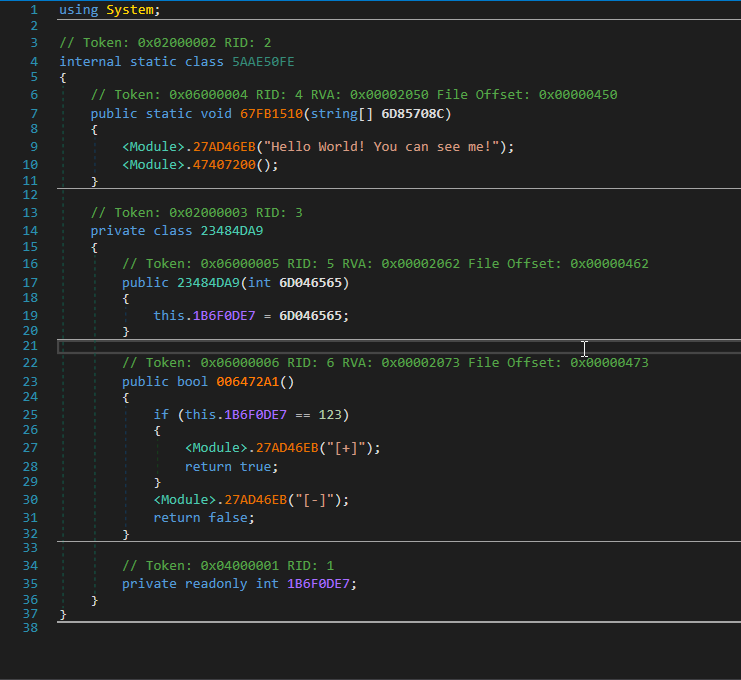 void-stack/vmunprotect.dumper
VMUnprotect.Dumper can dynamically untamper VMProtected Assembly.
 binsec/xyntia
Xyntia, the black-box deobfuscator
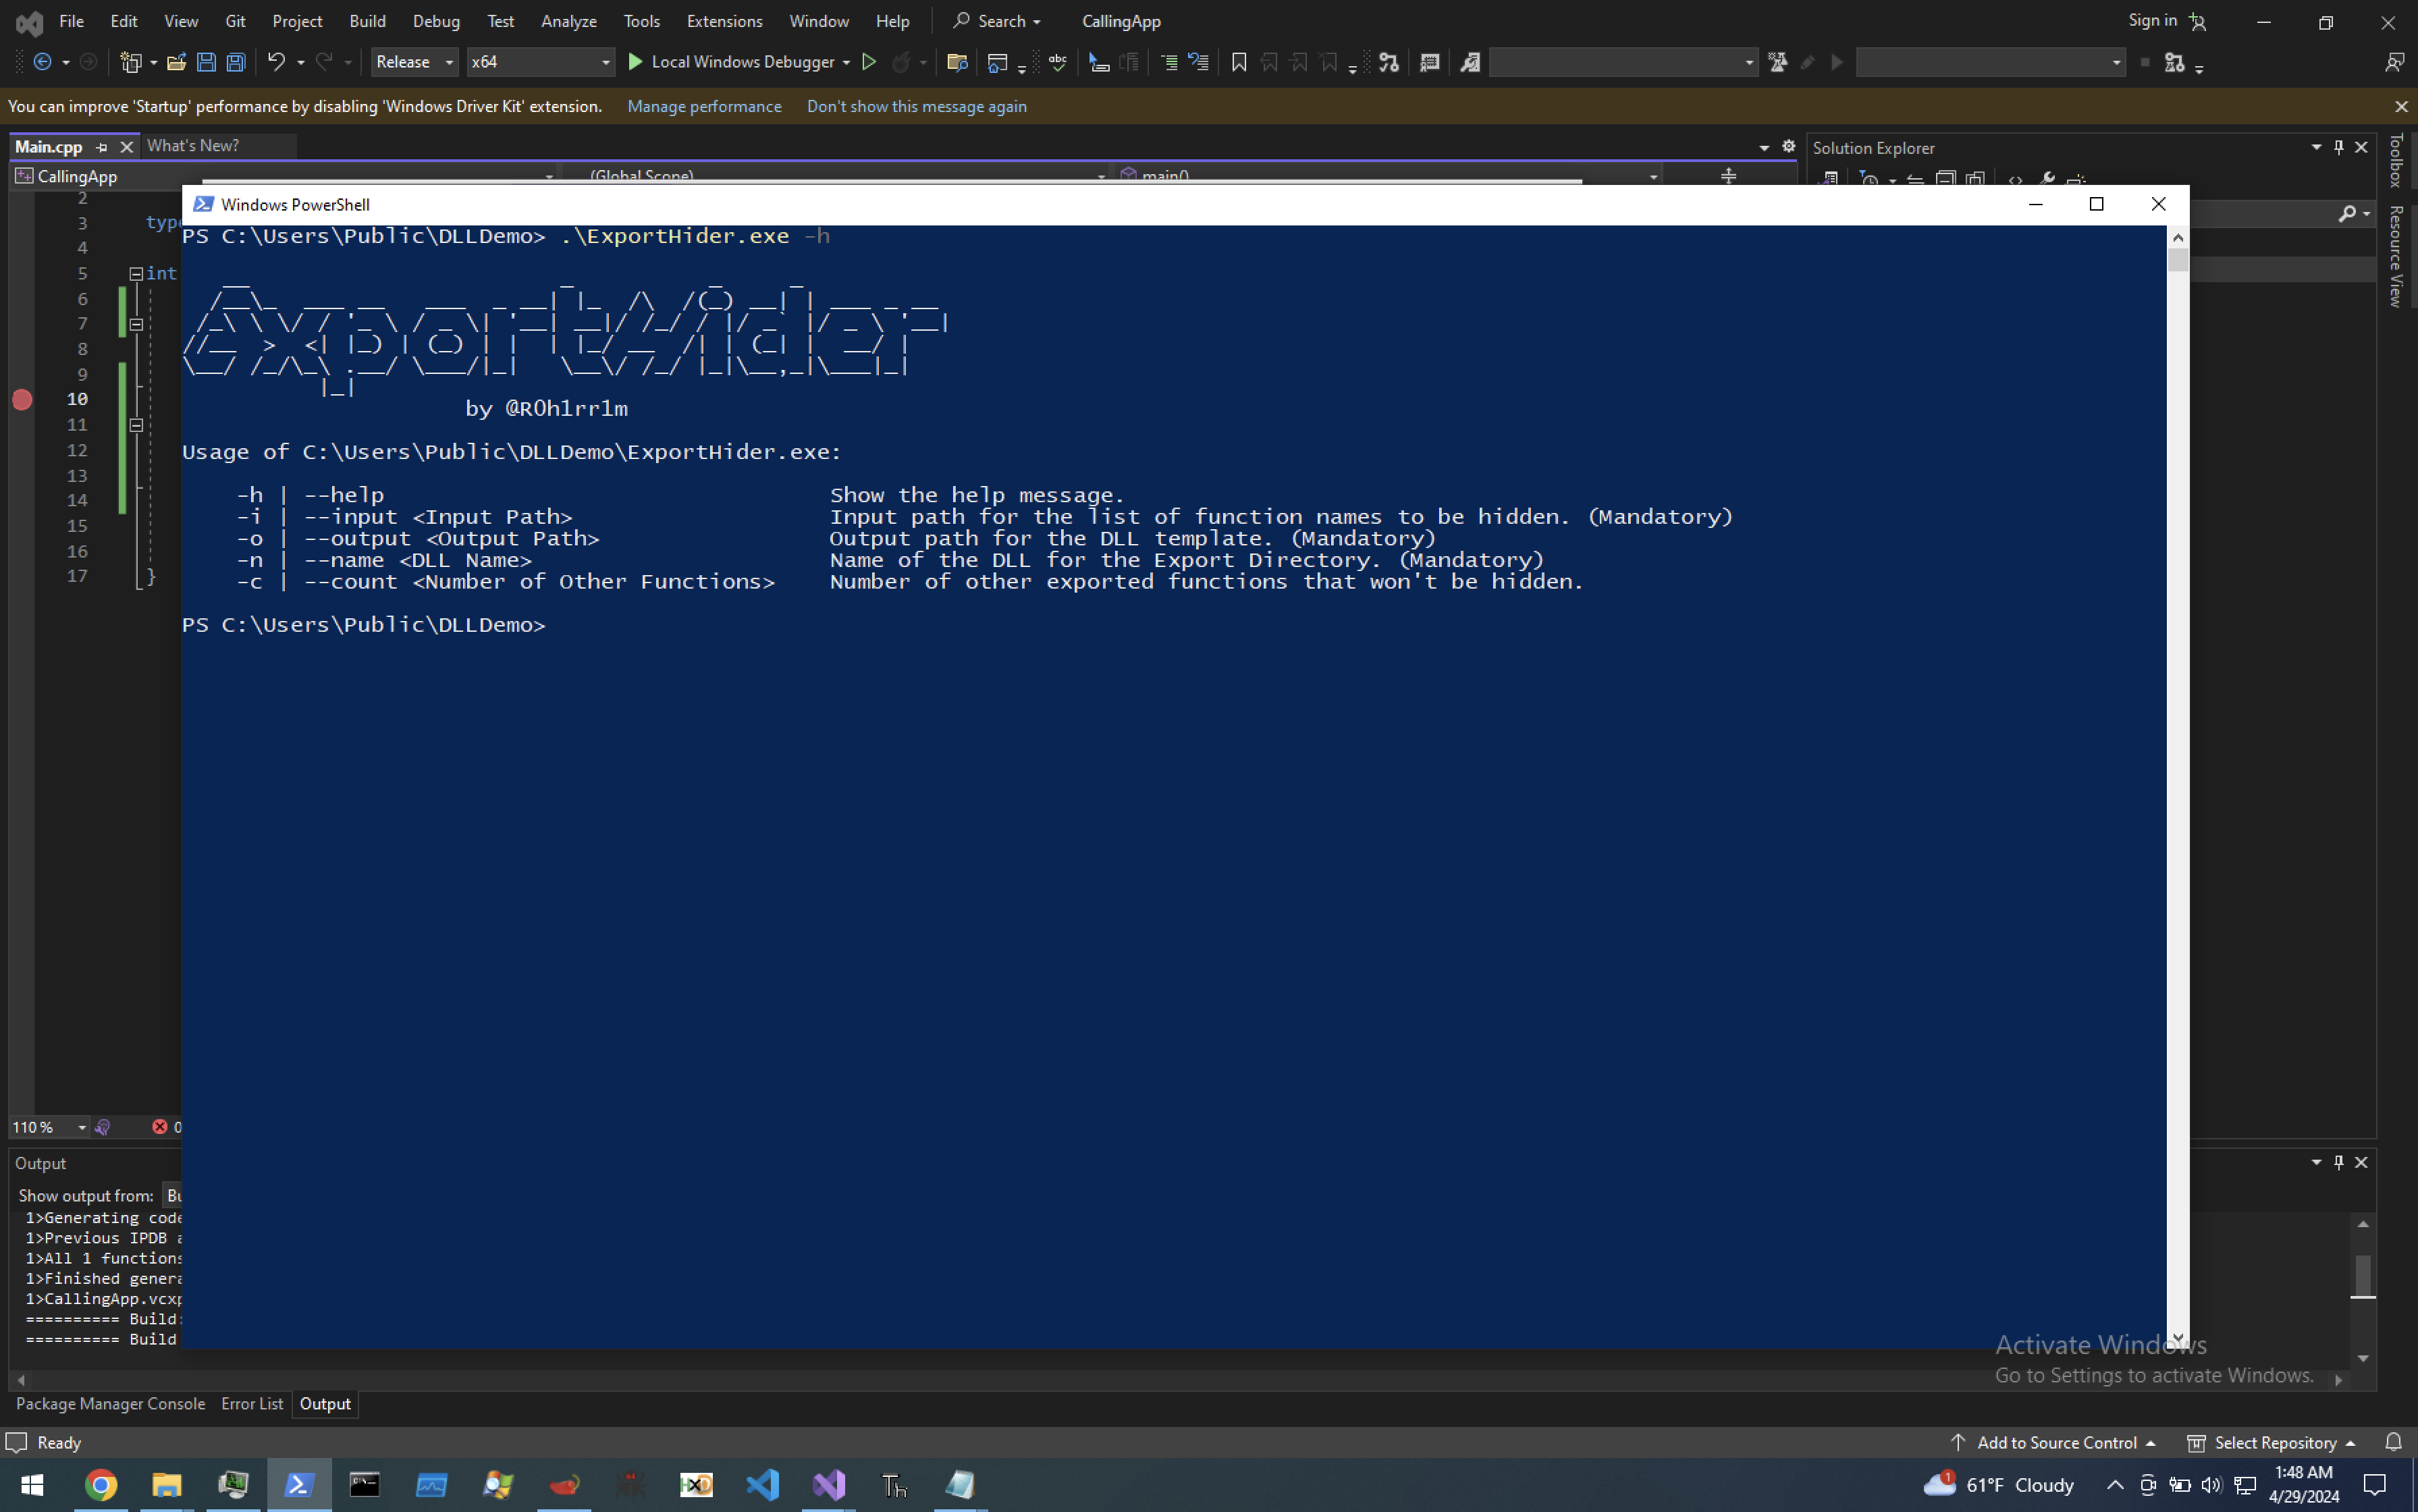 frkngksl/exporthider
ExportHider: Generating Export Table during Runtime to Hide the Exported Functions from the DLL File.