
malware-research
 eset/malware-research
Code written as part of our various malware investigations
digital-forensicsdynamic-code-analysismalware-analysis+4
417
eset/malware-researchCode written as part of our various malware investigations
 zer0condition/reversekit
x64 Dynamic Reverse Engineering Toolkit
 skylined/bugid
Detect, analyze and uniquely identify crashes in Windows applications
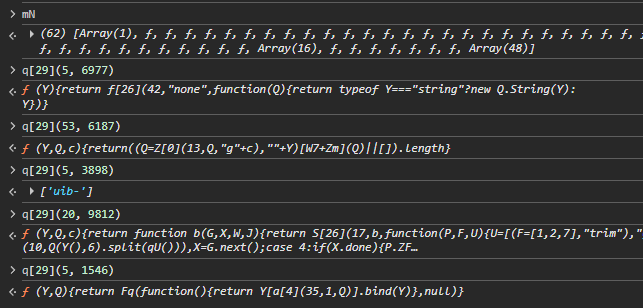 elyelysiox/recaptcha
Documentation and reverse engineering of reCAPTCHA
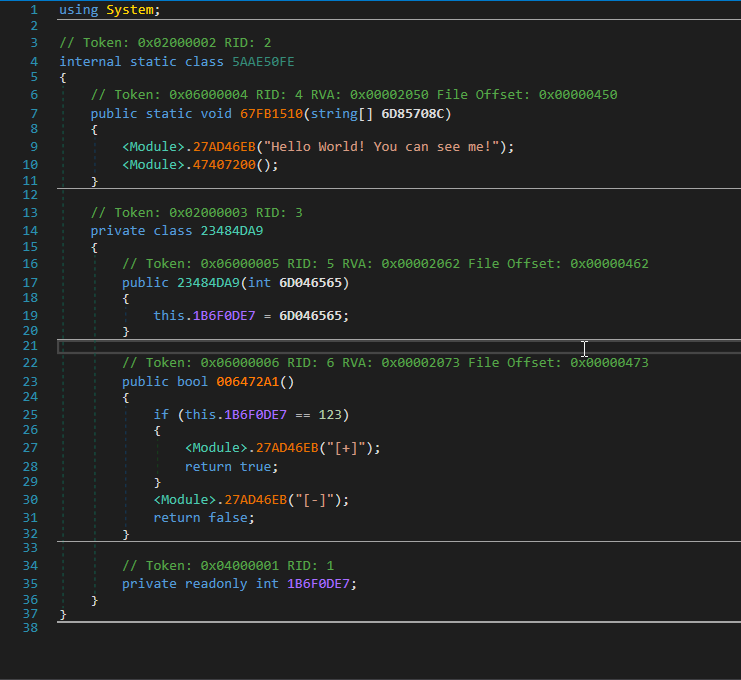 void-stack/vmunprotect.dumper
VMUnprotect.Dumper can dynamically untamper VMProtected Assembly.
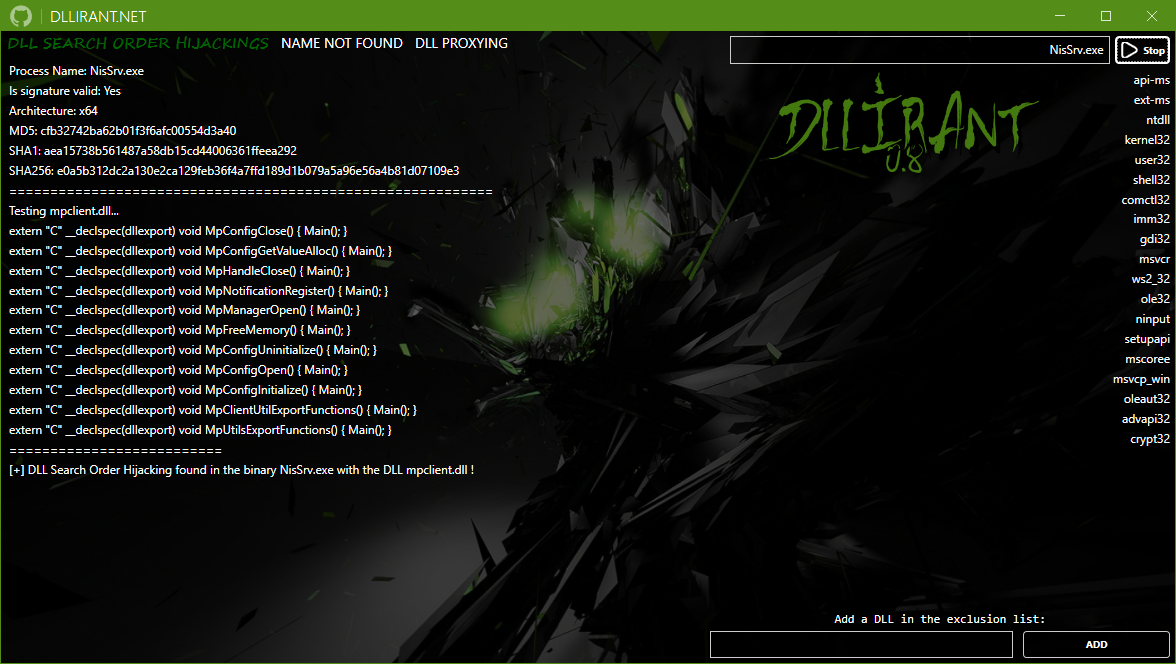 redteamsocietegenerale/dllirant
DLLirant is a tool to automatize the DLL Hijacking researches on a specified binary.
 mandiant/strace
A DTrace on Windows Reimplementation
 cornerpirate/java-stager
A PoC Java Stager which can download, compile, and execute a Java file in memory.
 dobin/burpsentinel
GUI Burp Plugin to ease discovering of security holes in web applications
 neurosaki987/tvm-recover
Devirtualizes Tencent VM .tvm0 sections: lifts VM handlers to guest-level listings and LLVM IR, recovers CFG and dispatch, and patches recovered code…
 robertdfrench/ifuncd-up
GNU IFUNC is the real culprit behind CVE-2024-3094
 worksbutnottested/lightkeeper
Maps execution-coverage data onto Ghidra disassembly to highlight visited code paths and accelerate reverse-engineering workflows.
 1rhino2/fnprint
match functions in binaries by what they do, not what their bytes look like. behavioral function fingerprinting via microexecution.
 binsec/xyntia
Xyntia, the black-box deobfuscator
 ejfkdev/jscd
Reverse bytenode .jsc (V8 code cache) to JavaScript — static, pure Rust, no patched V8/Node. Node 8→26 / V8 5.8–14.6; 25k .jsc tested, 0 fail.
 dvyukov/centipede
Distributed coverage-guided fuzzing engine compatible with libFuzzer targets; scales to thousands of concurrent jobs, uses sanitizers and corpus…
 0x3c3e/slides
CodeQL + DTrace = Memory Disclosure Vulnerabilities in XNU