

pyREtic
 mynameismeerkat/pyretic
pyREtic is an extensible framework for in-memory Python 2.x bytecode reverse engineering
binary-analysiscode-analysisdebuggers+5
mynameismeerkat/pyreticpyREtic is an extensible framework for in-memory Python 2.x bytecode reverse engineering
 pietroborrello/customprocessingunit
The first analysis framework for CPU microcode
 hugsy/windbg_js_scripts
Toy scripts for playing with WinDbg JS API
 advdebug/brovan
User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…
 dougwithseismic/dezlock-dump
Runtime schema + RTTI extraction tool for Deadlock, CS2, Dota, and others (Source 2). No source2gen required.
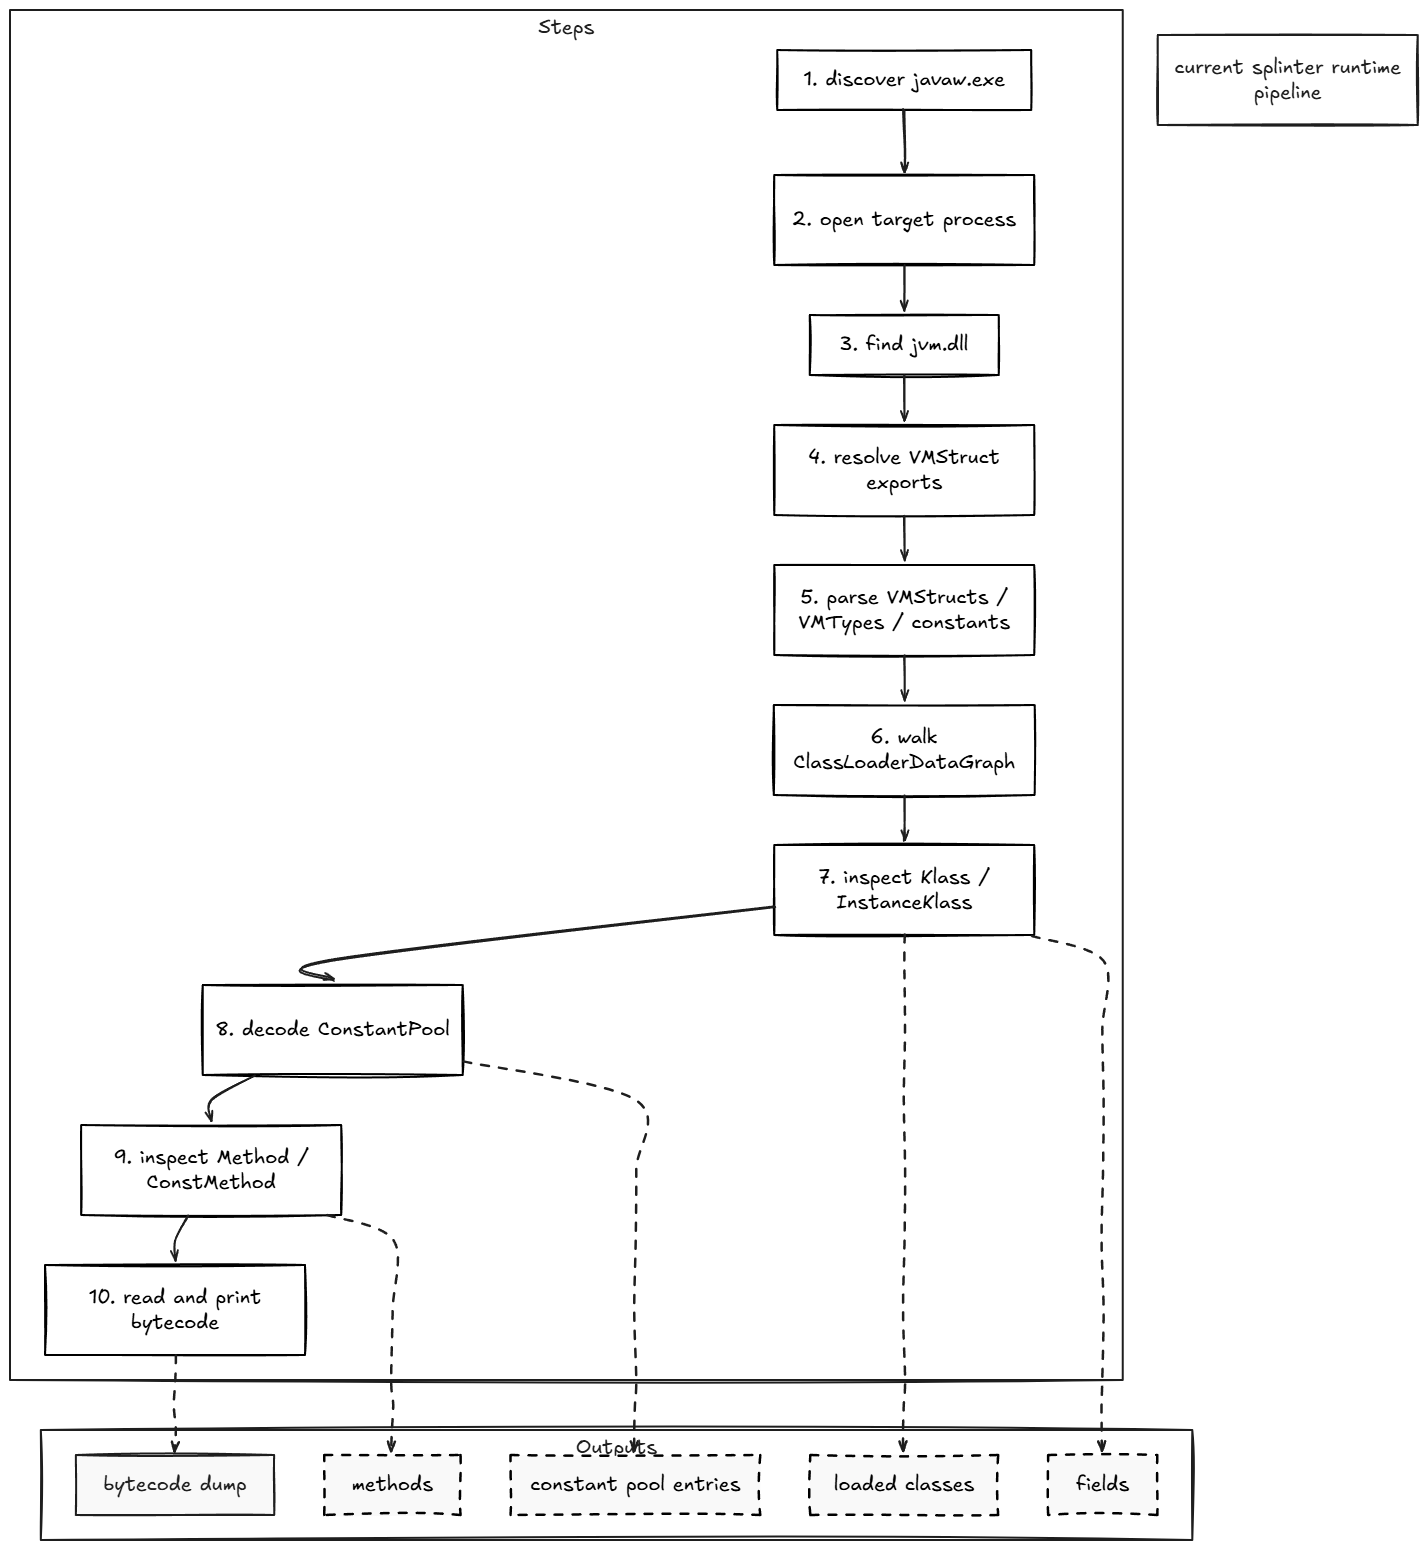 awrped/splinter
Runtime JVM analysis toolkit for inspecting classes, methods, fields, constant pool, and bytecode
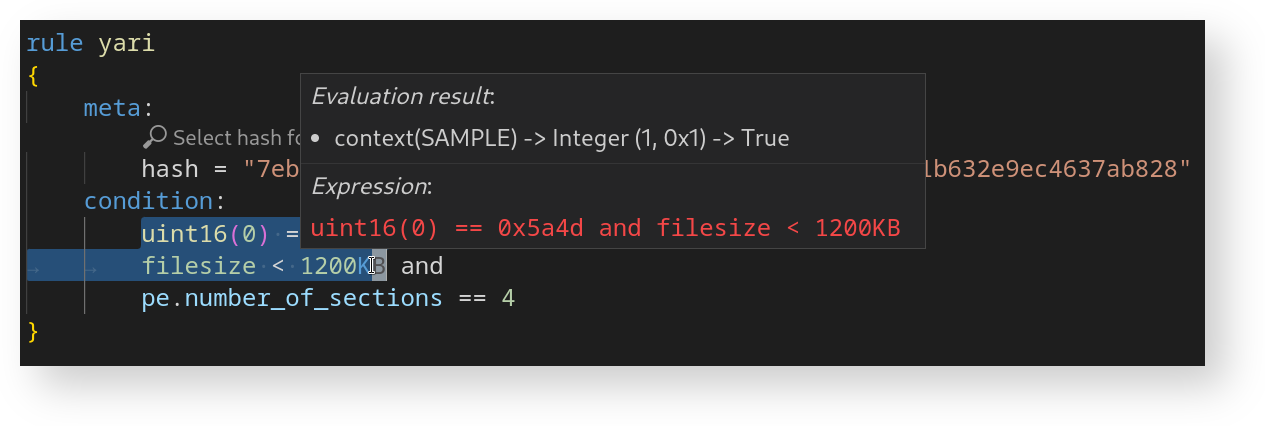 avast/yari
YARI is an interactive debugger for YARA Language.
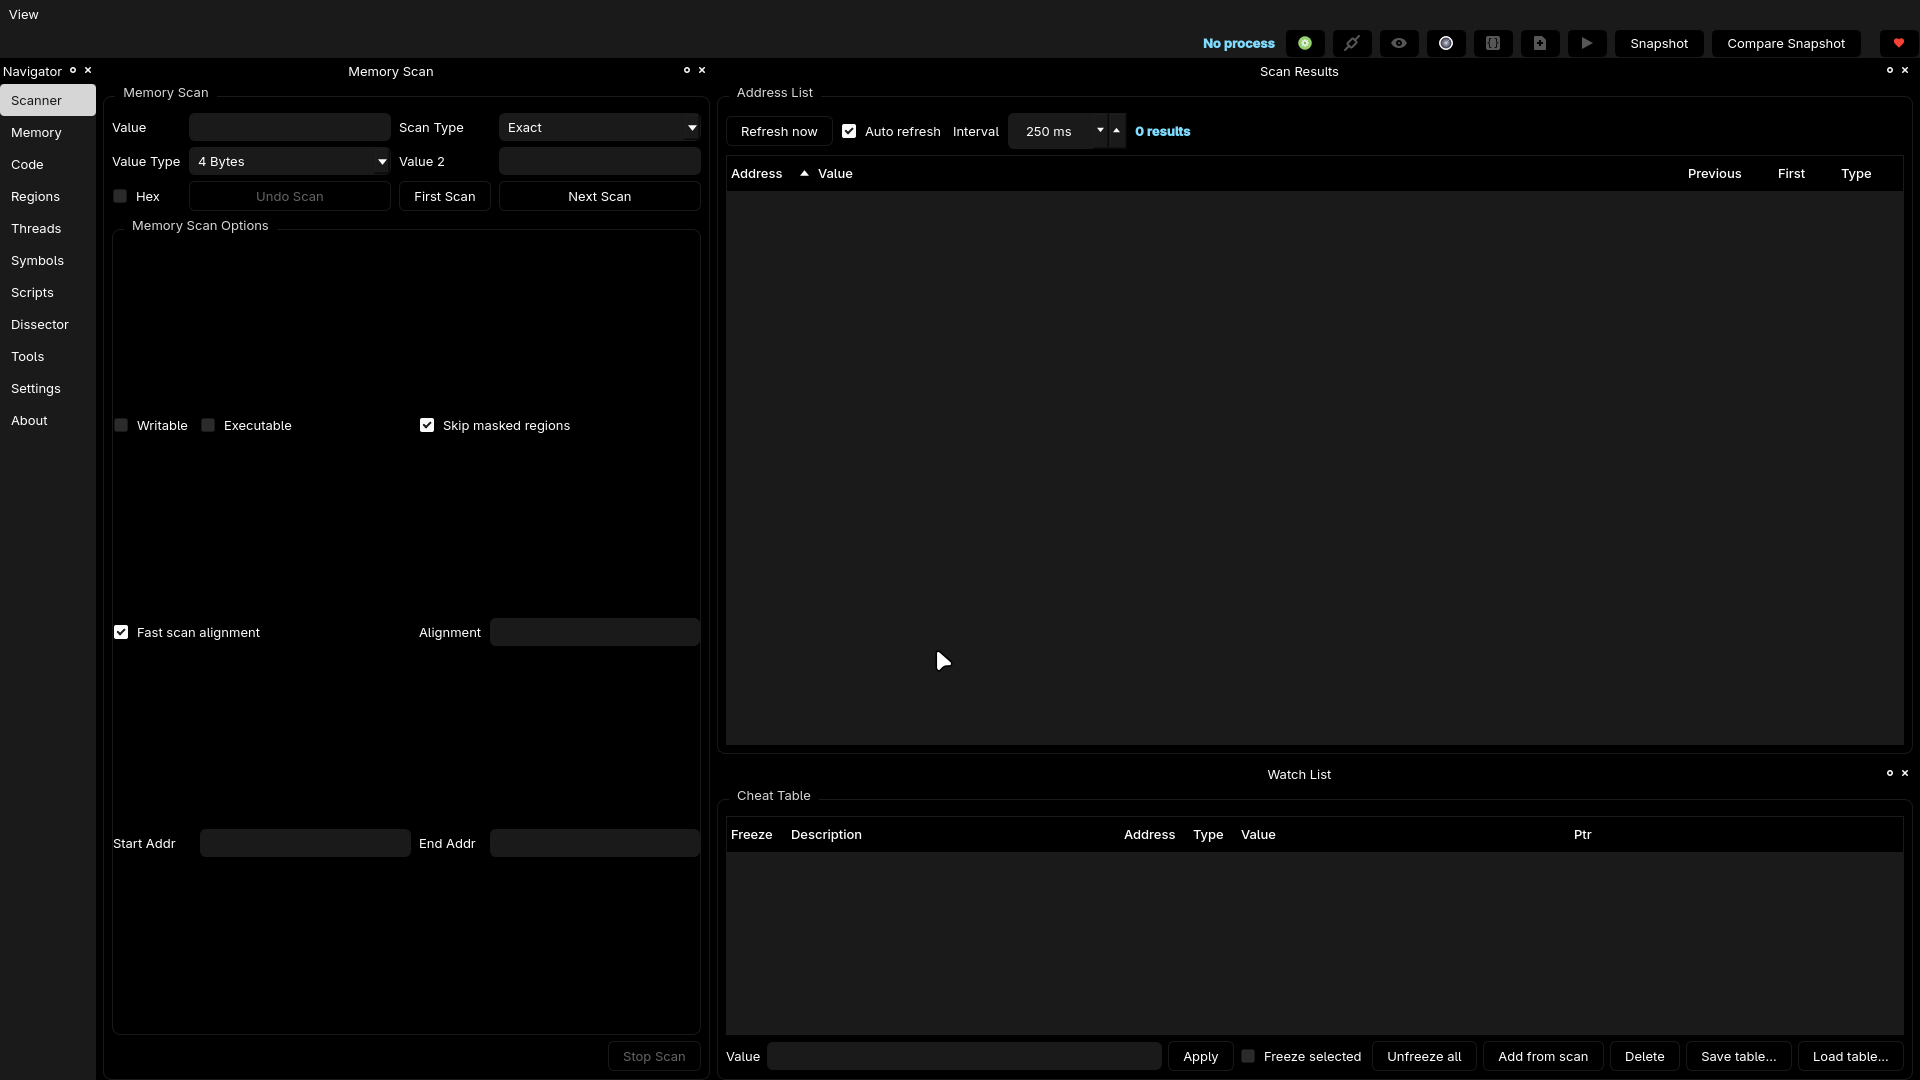 kashithecomfy/comfyengine
ComfyEngine is a memory exploration toolkit built for people who need to monitor, patch, and script a running process.
 therealdreg/ida_bochs_windows
Helper script for Windows kernel debugging with IDA Pro on native Bochs debugger (including PDB symbols)
 ddudle/ctxdebug
MCP-powered reverse engineering platform connecting WinDbg, IDA Pro & x64dbg with 160+ AI-accessible debugging and analysis tools.
 whatswrongandwhy/ptrace
Linux ptrace-based process tracing and debugging utility for inspecting system calls, memory, and program execution flow.
 awslabs/snapchange
Lightweight fuzzing of a memory snapshot using KVM
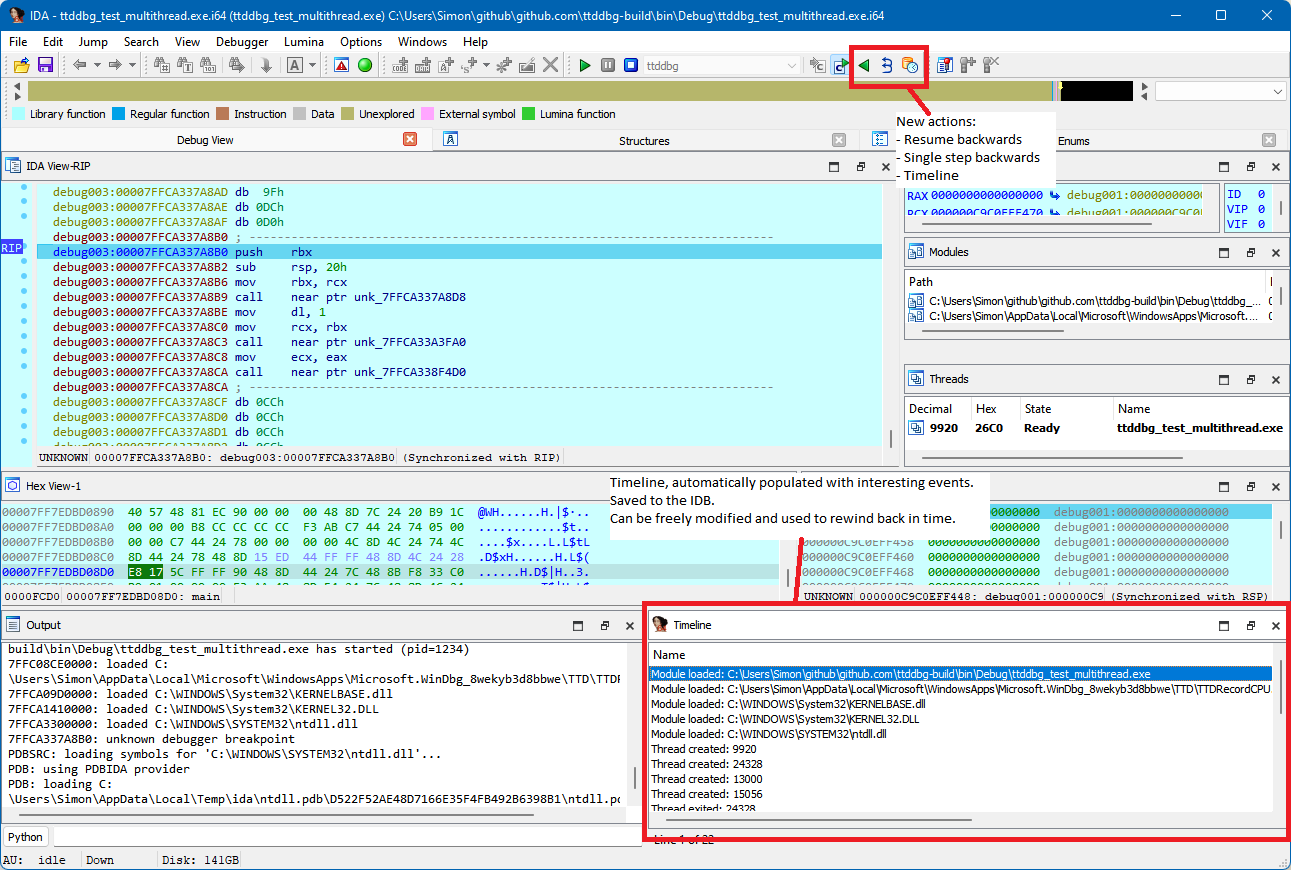 airbus-cert/ttddbg
Time Travel Debugging IDA plugin
 rbmm/ntdetours
Detours implementation (x64/x86) which used only ntdll import
 skylined/bugid
Detect, analyze and uniquely identify crashes in Windows applications
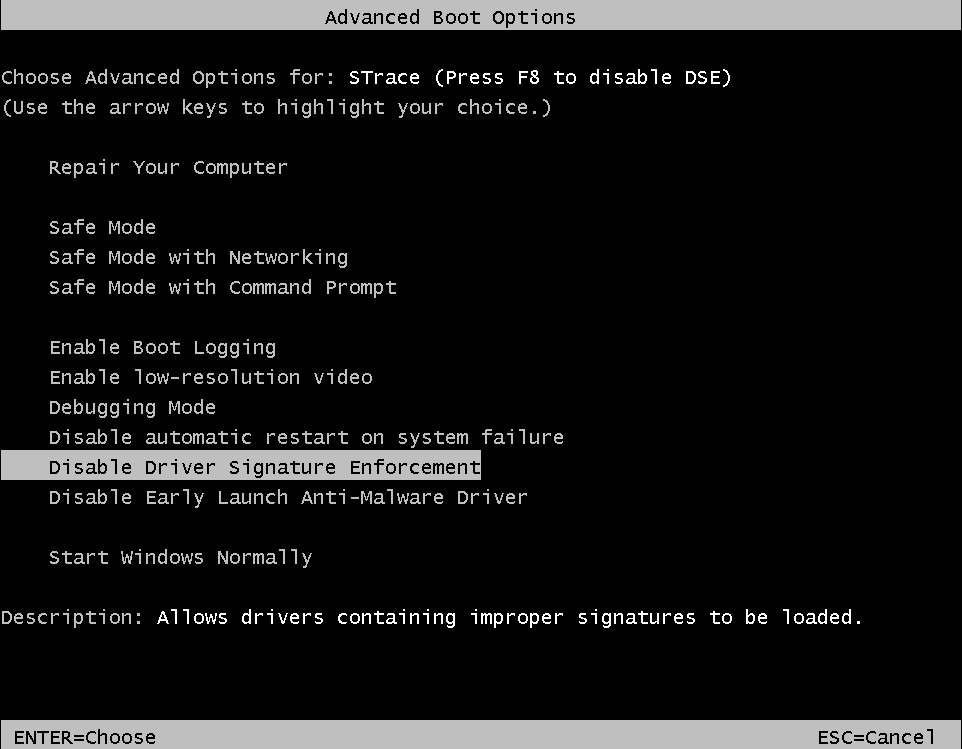 mandiant/strace
A DTrace on Windows Reimplementation
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…