
STrace
 mandiant/strace
A DTrace on Windows Reimplementation
debuggersdynamic-code-analysisincident-response+2
mandiant/straceA DTrace on Windows Reimplementation
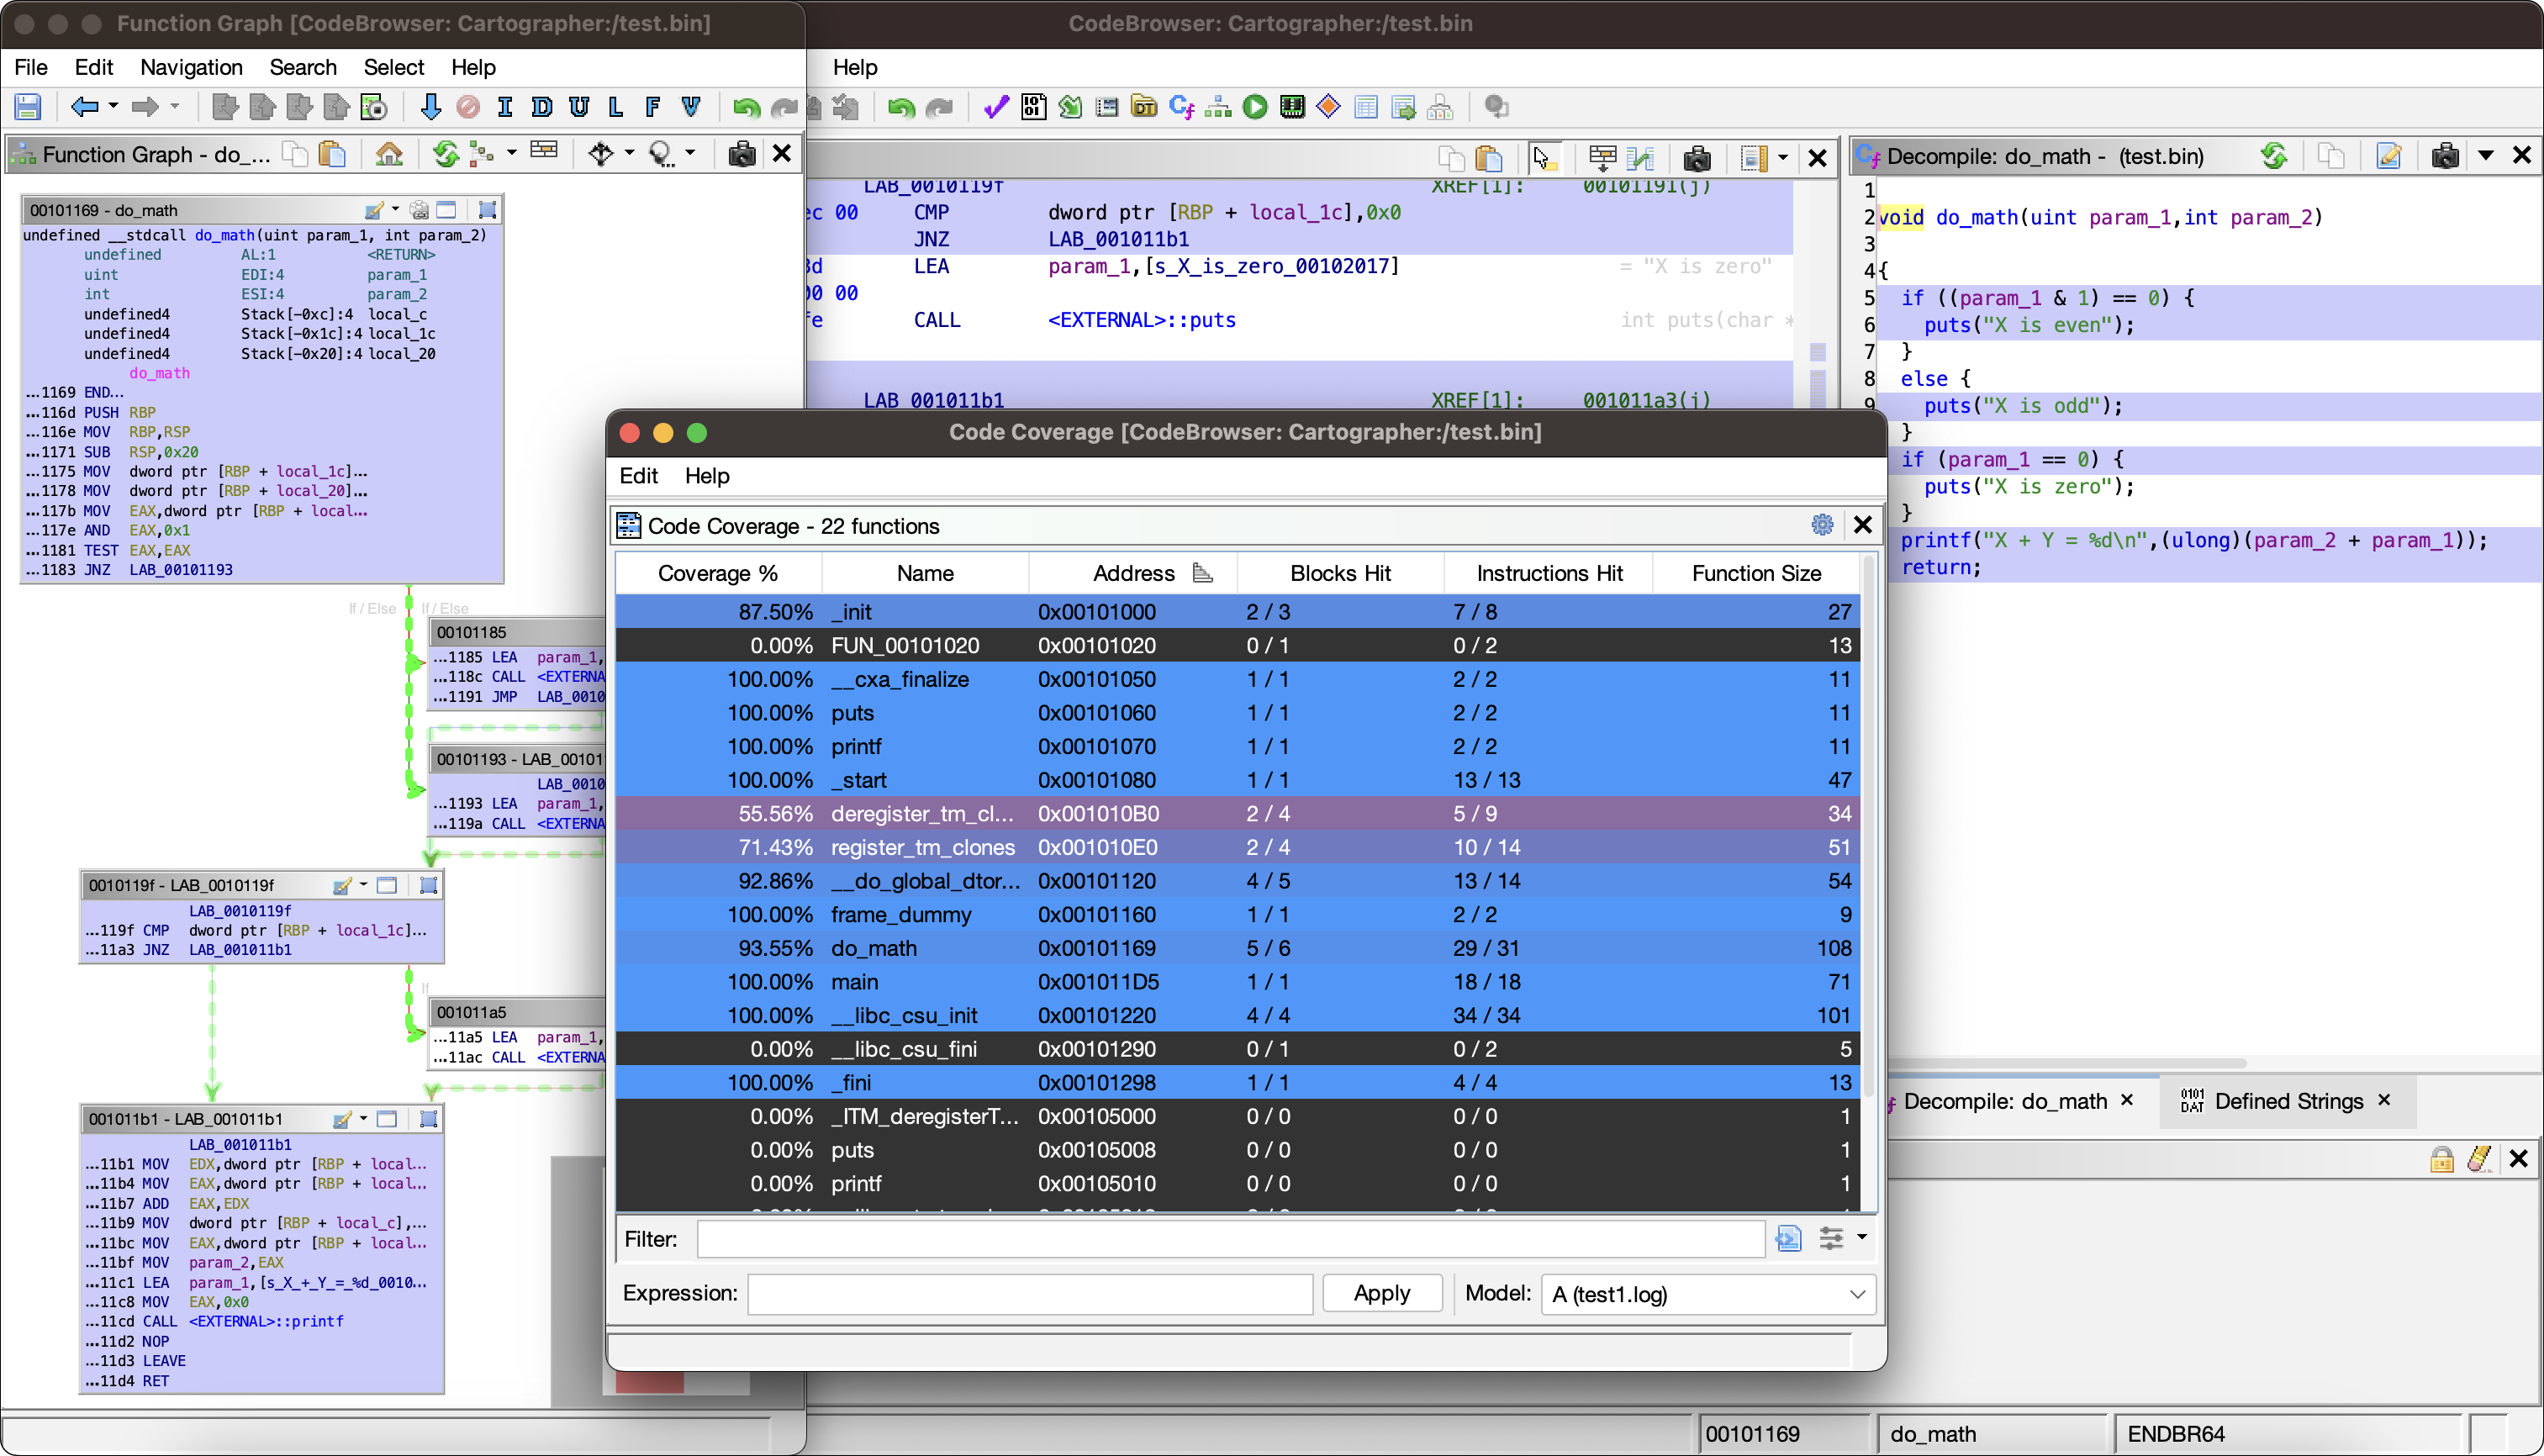 nccgroup/cartographer
Code Coverage Exploration Plugin for Ghidra
 pietroborrello/customprocessingunit
The first analysis framework for CPU microcode
 yuatemycat/superghidra
Python toolkit accelerating Ghidra with a cached daemon, ARM64 P-code lifting, Z3 equivalence proofs, GPU-accelerated scanning, binary diffing, and…
 hugsy/windbg_js_scripts
Toy scripts for playing with WinDbg JS API
 cobbr/elite
Elite is the client-side component of the Covenant project. Covenant is a .NET command and control framework that aims to highlight the attack…
 cornerpirate/java-stager
A PoC Java Stager which can download, compile, and execute a Java file in memory.
 ch0pin/rdx
A native APK and DEX decompiler written in Rust
 advdebug/brovan
User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…
 lauriewired/artful
The ARTful library for dynamically modifying the Android Runtime
 symbioticsec/hermes-decomp
A powerful decompiler that lets you reverse-engineer React Native mobile apps by converting their compiled Hermes bytecode (.hbc) files back into…
 dougwithseismic/dezlock-dump
Runtime schema + RTTI extraction tool for Deadlock, CS2, Dota, and others (Source 2). No source2gen required.
 giveen/decomp.anything
decomp.wtf fork: Windows PE matching, MinGW/clang-cl toolchains, and an optional REA MCP bridge
 nccgroup/dibf
Windows NT ioctl bruteforcer and modular fuzzer
 dobin/burpsentinel
GUI Burp Plugin to ease discovering of security holes in web applications
 we5ter/flerken
A Solution For Cross-Platform Obfuscated Commands Detection presented on CIS2019 China. 动静态Bash/CMD/PowerShell命令混淆检测框架 - CIS 2019大会
 rbmm/ntdetours
Detours implementation (x64/x86) which used only ntdll import