
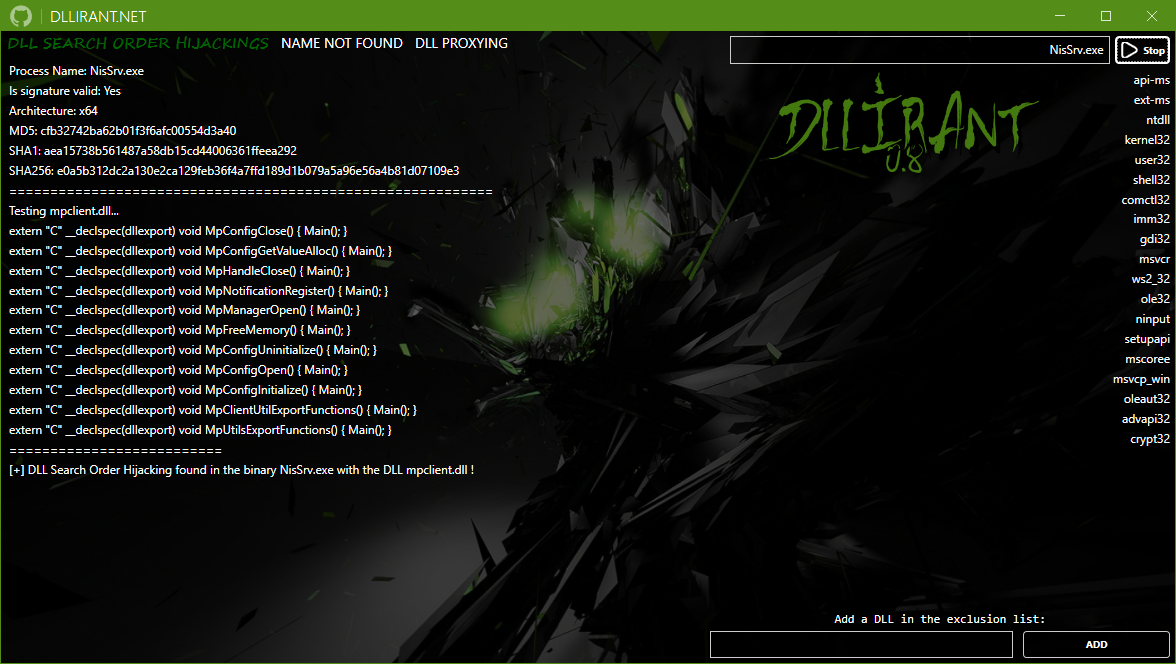
DLLirant
 redteamsocietegenerale/dllirant
DLLirant is a tool to automatize the DLL Hijacking researches on a specified binary.
binary-analysisdynamic-code-analysisexploitation+3
502
redteamsocietegenerale/dllirantDLLirant is a tool to automatize the DLL Hijacking researches on a specified binary.
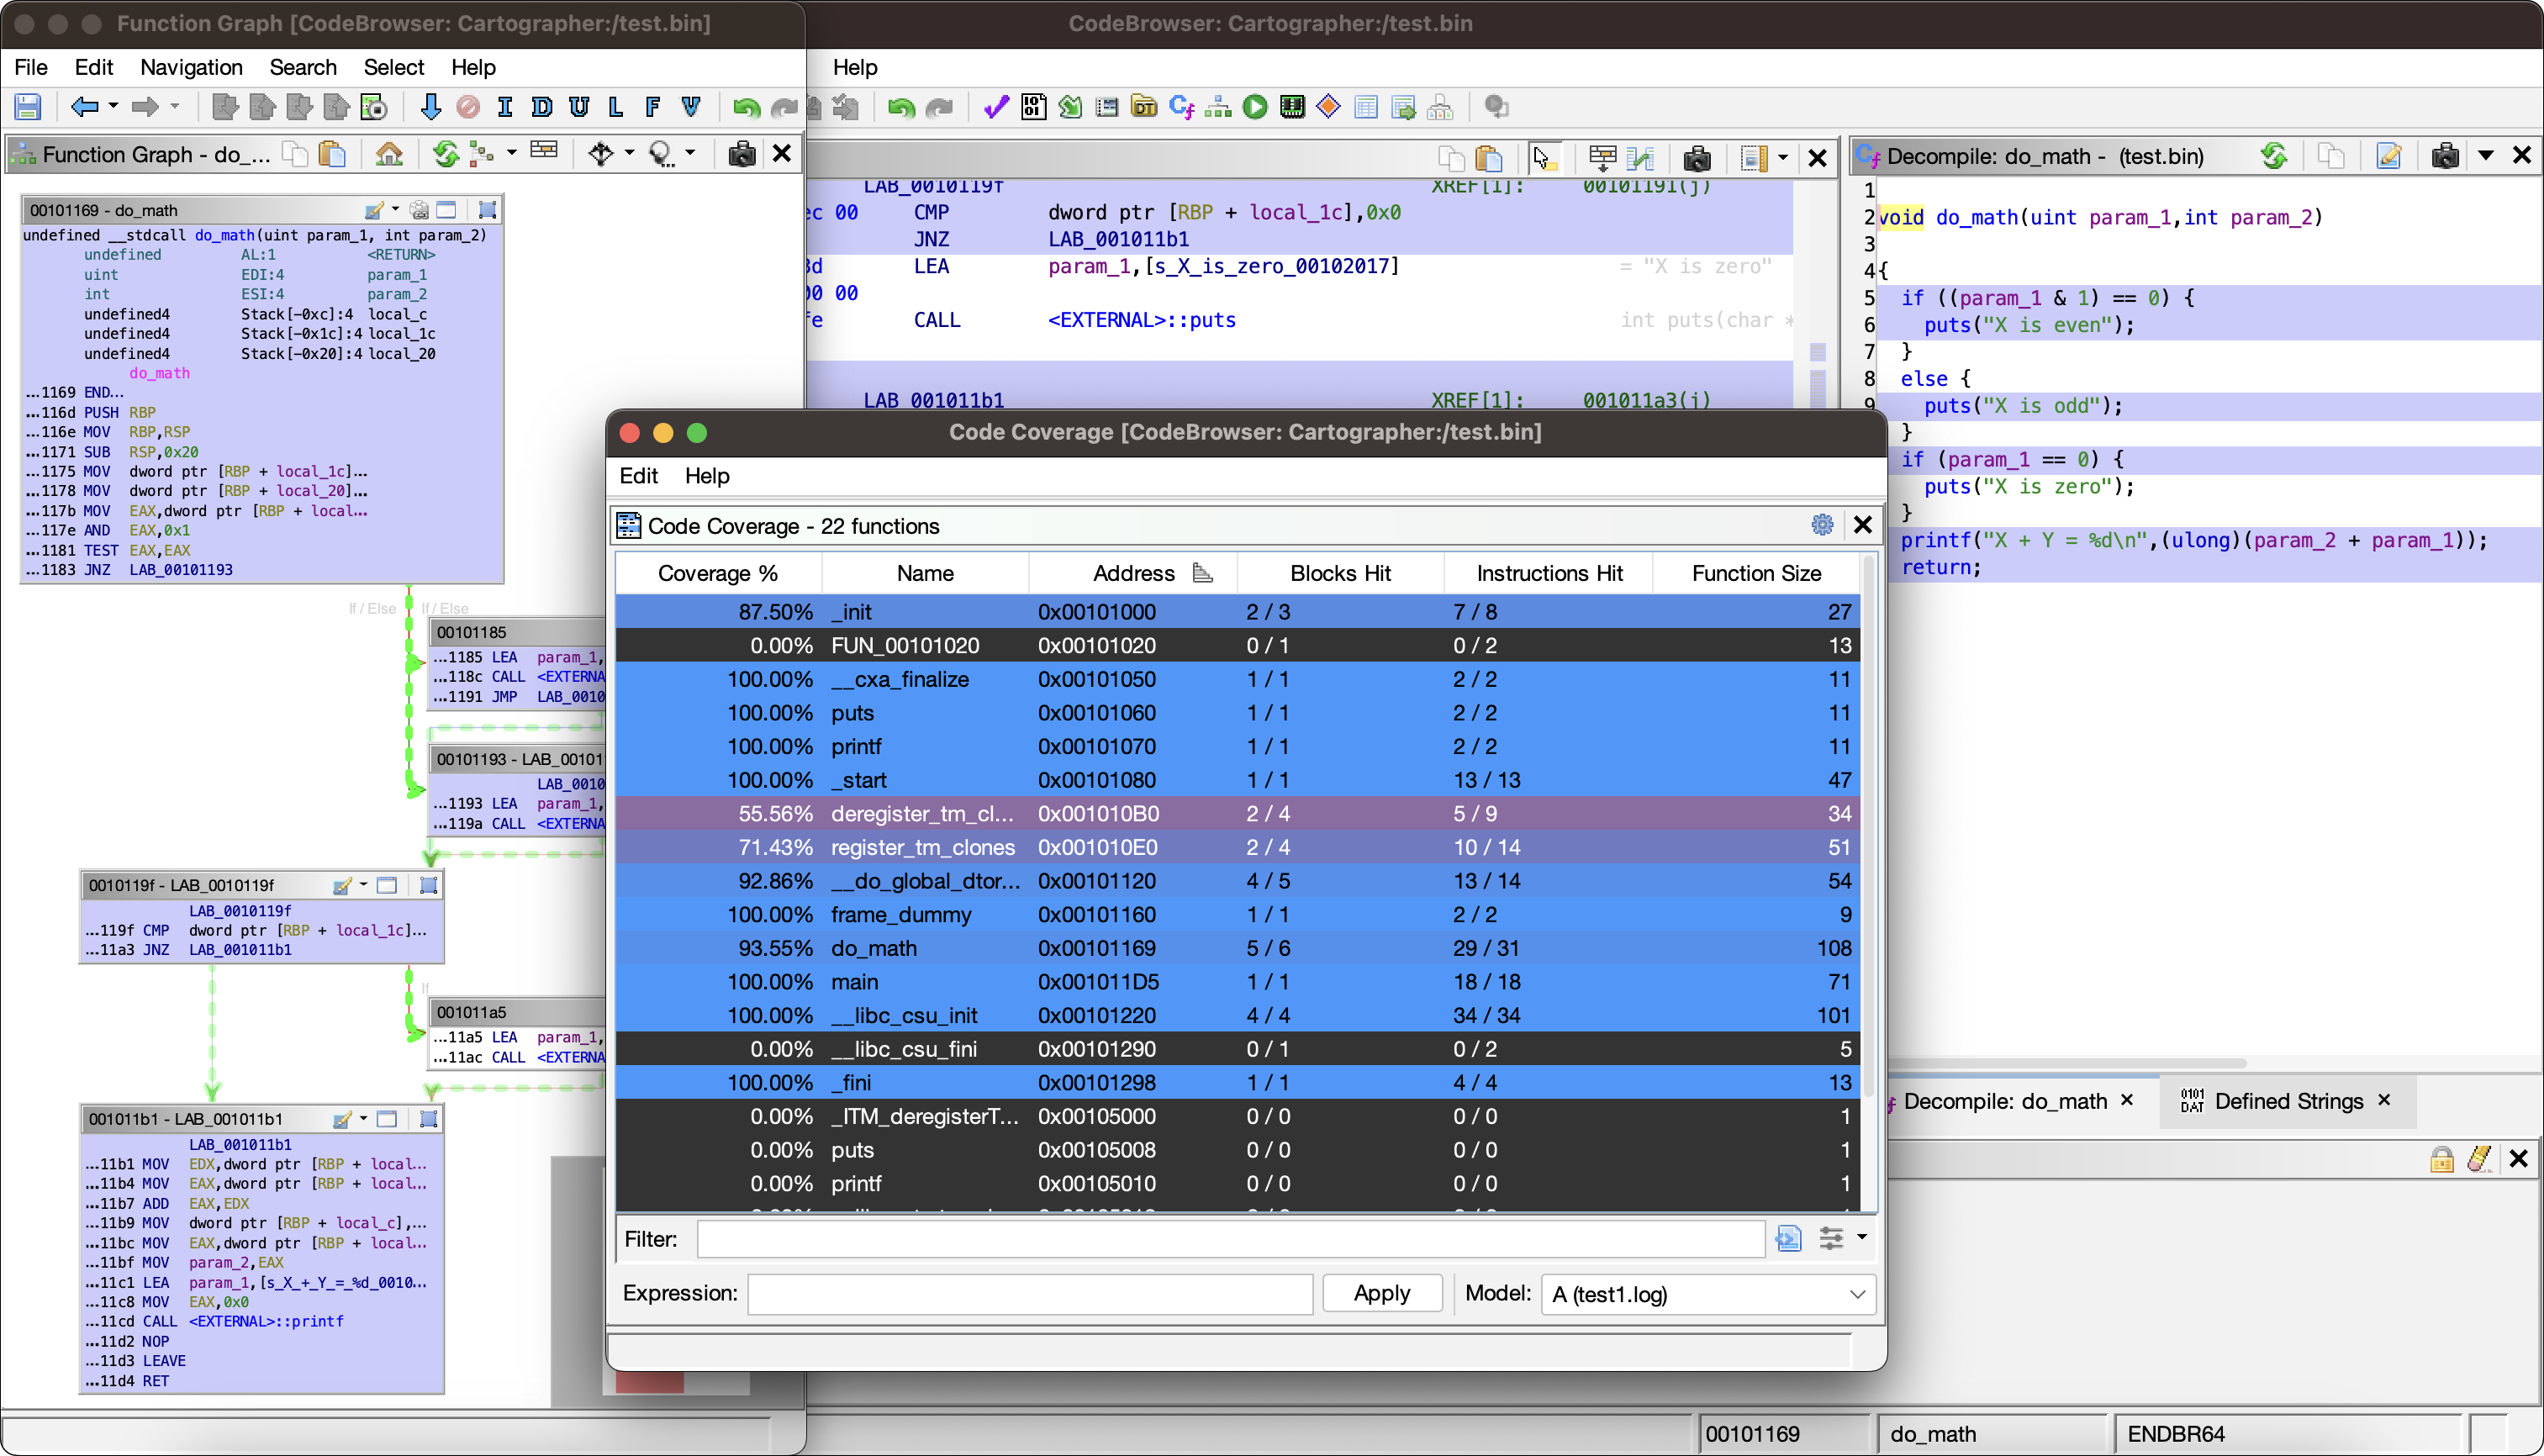 nccgroup/cartographer
Code Coverage Exploration Plugin for Ghidra
 symbioticsec/hermes-decomp
A powerful decompiler that lets you reverse-engineer React Native mobile apps by converting their compiled Hermes bytecode (.hbc) files back into…
 cobbr/elite
Elite is the client-side component of the Covenant project. Covenant is a .NET command and control framework that aims to highlight the attack…
 cornerpirate/java-stager
A PoC Java Stager which can download, compile, and execute a Java file in memory.
 we5ter/flerken
A Solution For Cross-Platform Obfuscated Commands Detection presented on CIS2019 China. 动静态Bash/CMD/PowerShell命令混淆检测框架 - CIS 2019大会
 lauriewired/artful
The ARTful library for dynamically modifying the Android Runtime
 ch0pin/rdx
A native APK and DEX decompiler written in Rust
 nccgroup/dibf
Windows NT ioctl bruteforcer and modular fuzzer
 worksbutnottested/lightkeeper
Maps execution-coverage data onto Ghidra disassembly to highlight visited code paths and accelerate reverse-engineering workflows.
 r00tkitsmm/pishi
Pishi is a code coverage tool like kcov for macOS.
 jpiechowka/jenkins-cve-2016-0792
Exploit for Jenkins serialization vulnerability - CVE-2016-0792
 robertdfrench/ifuncd-up
GNU IFUNC is the real culprit behind CVE-2024-3094
 binsec/xyntia
Xyntia, the black-box deobfuscator
 1rhino2/fnprint
match functions in binaries by what they do, not what their bytes look like. behavioral function fingerprinting via microexecution.
 nccgroup/winstrument
Winstrument is a framework of modular scripts to aid in instrumenting Windows software using Frida for reverse engineering and attack surface…
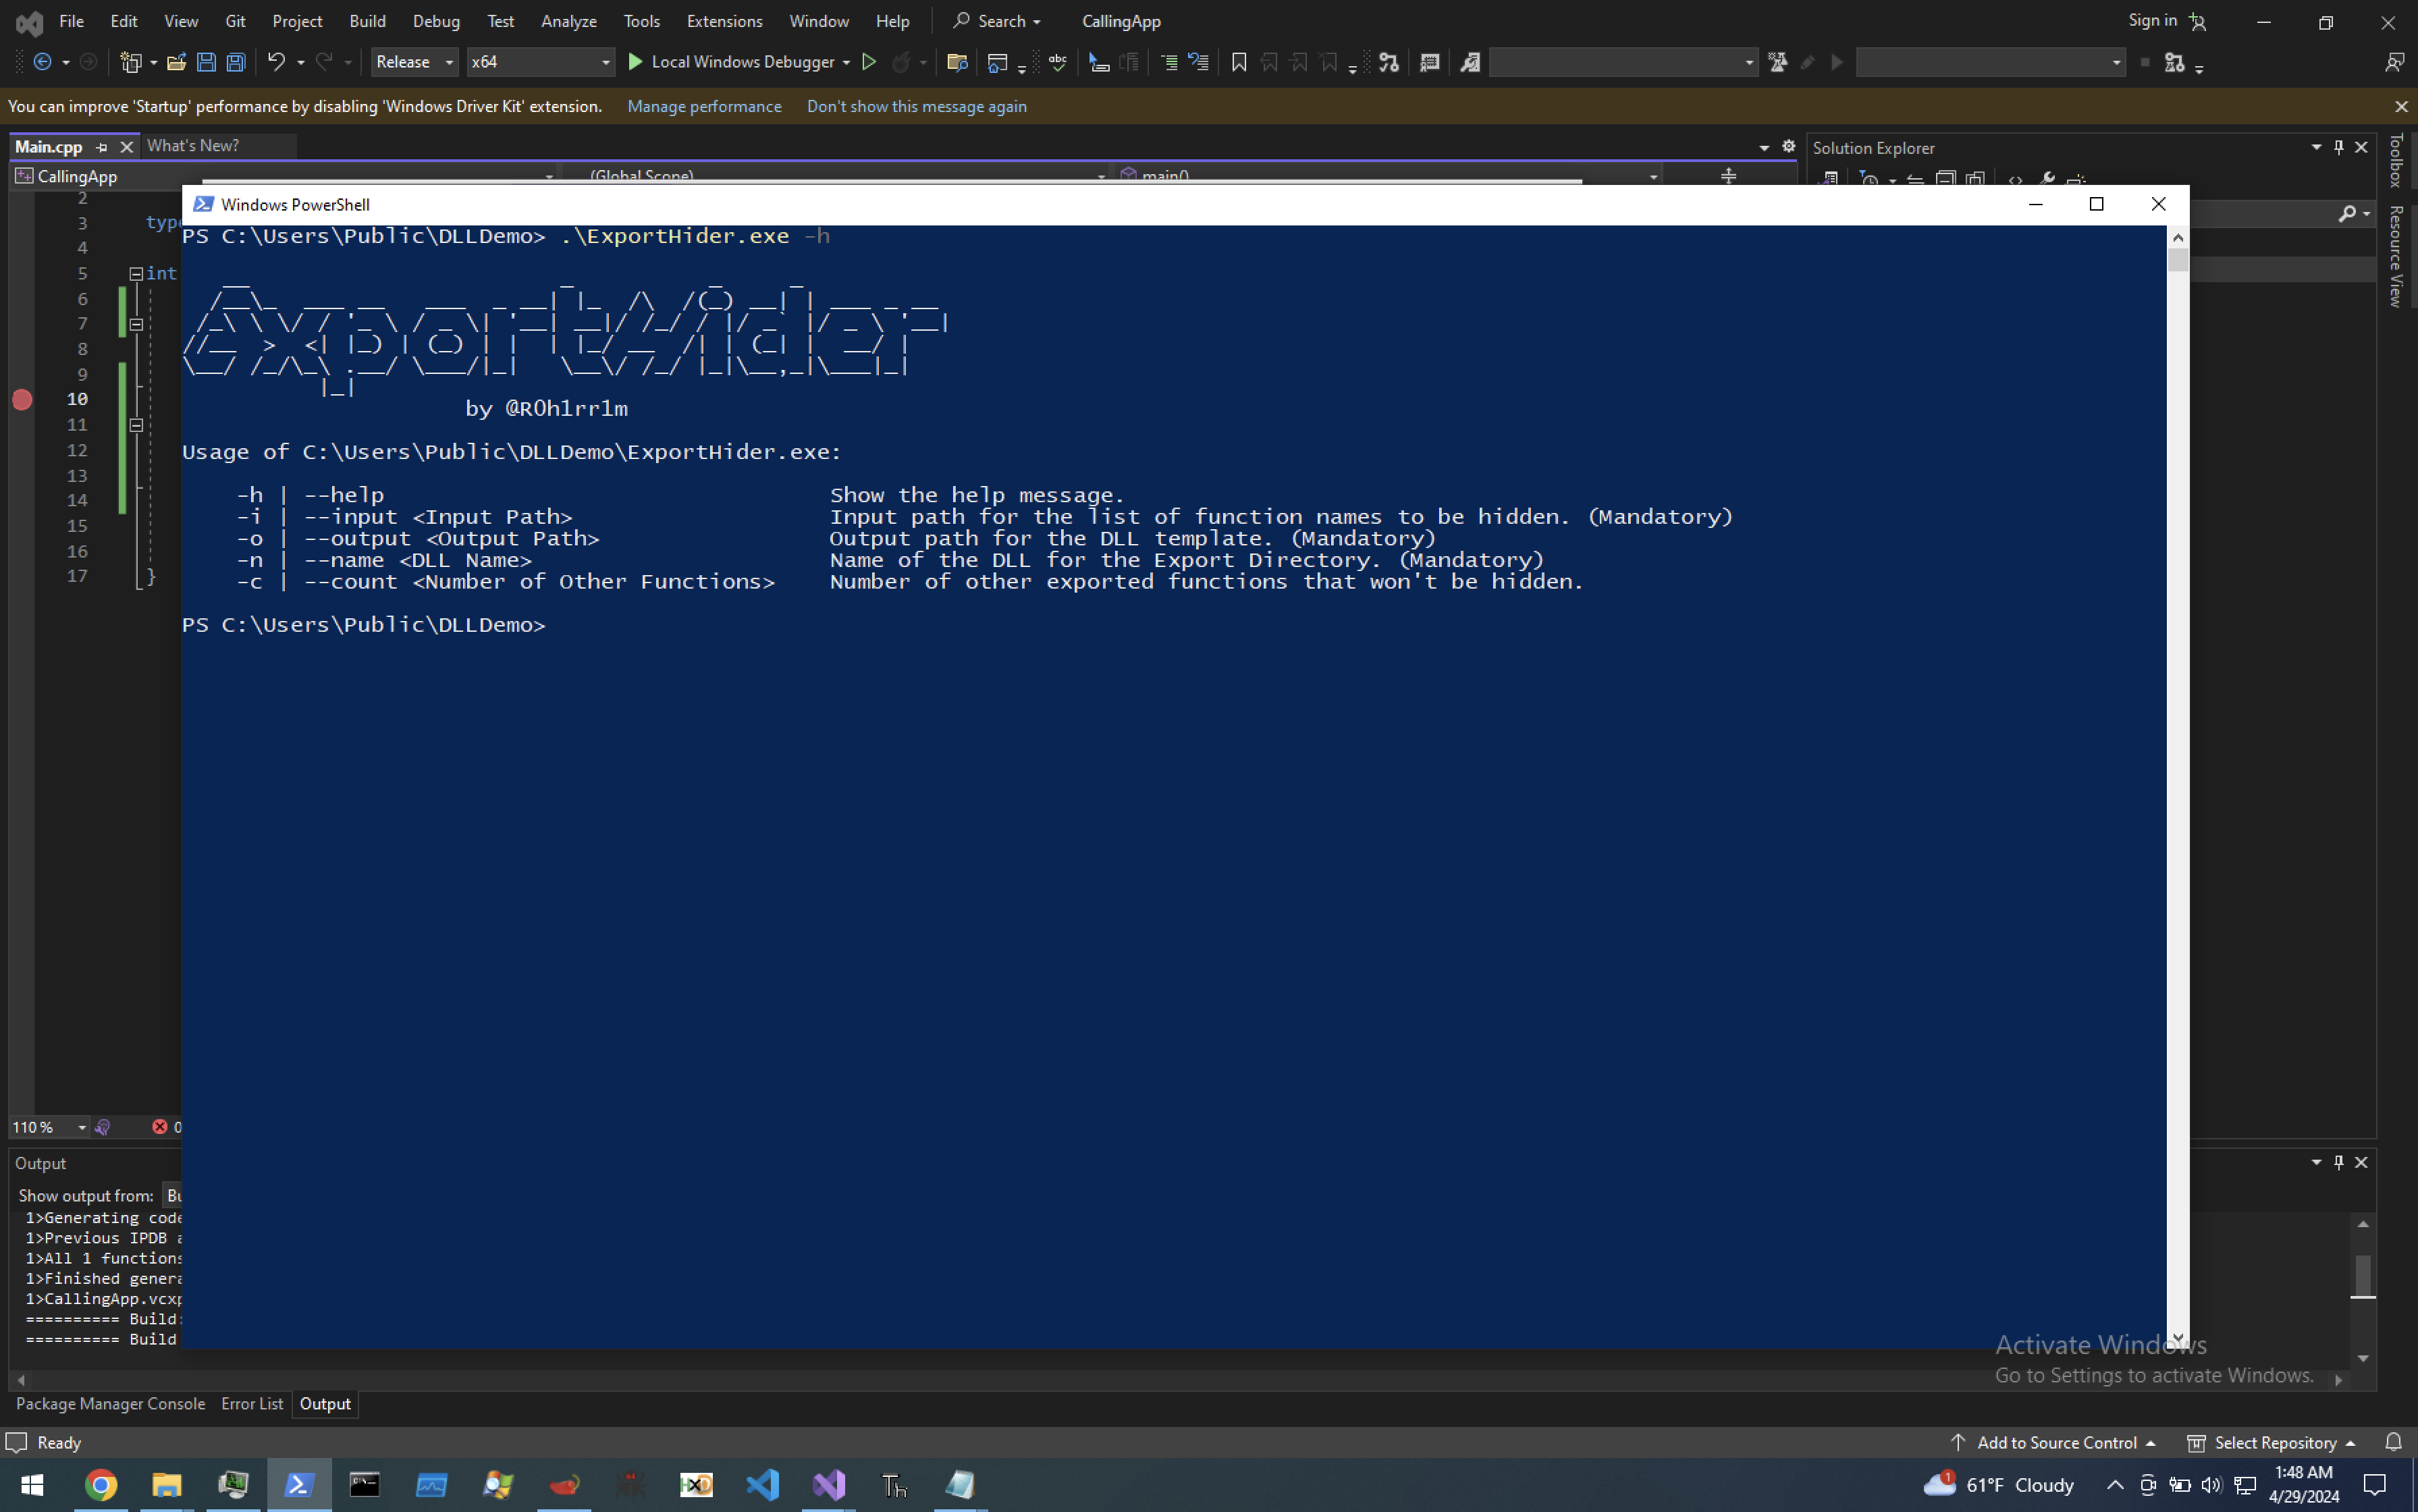 frkngksl/exporthider
ExportHider: Generating Export Table during Runtime to Hide the Exported Functions from the DLL File.
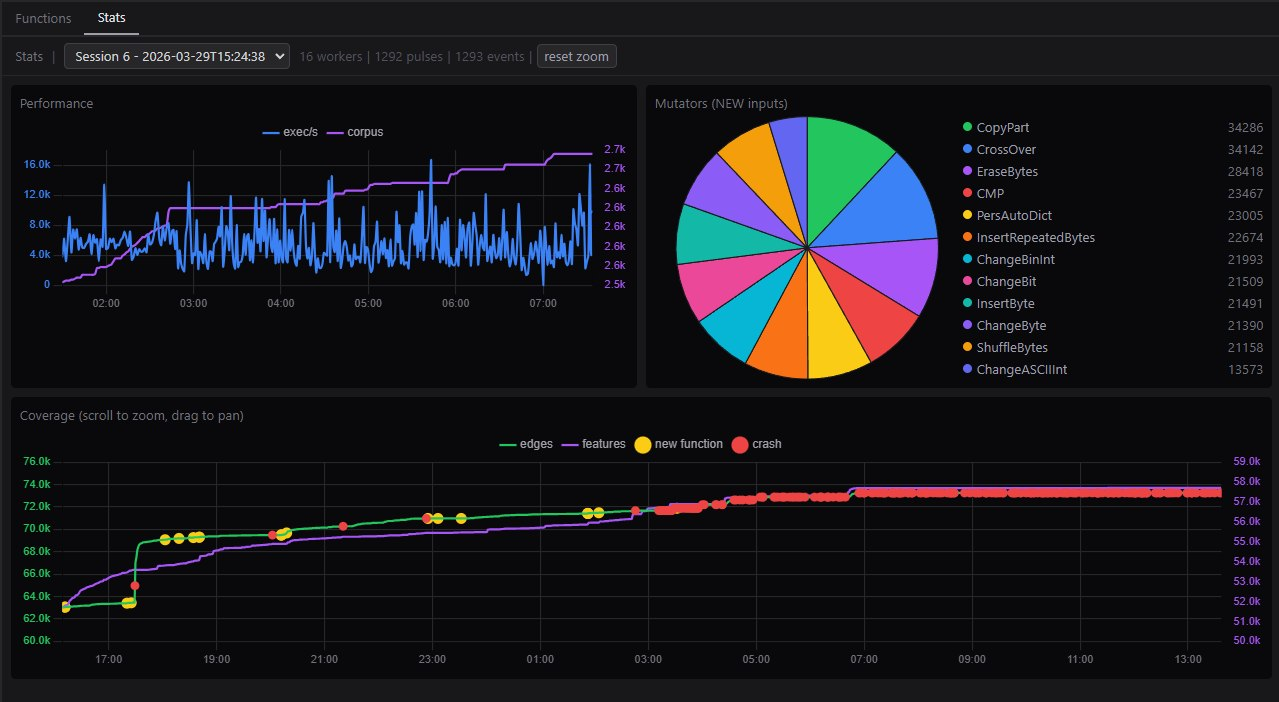 0xbigshaq/apatchy
Fuzzing Framework for Modules in Apache HTTPD Server