
xyntia
 binsec/xyntia
Xyntia, the black-box deobfuscator
binary-analysiscode-analysisdynamic-code-analysis+1
binsec/xyntiaXyntia, the black-box deobfuscator
 1rhino2/fnprint
match functions in binaries by what they do, not what their bytes look like. behavioral function fingerprinting via microexecution.
 nccgroup/winstrument
Winstrument is a framework of modular scripts to aid in instrumenting Windows software using Frida for reverse engineering and attack surface…
 stealthcopter/wordpress-hacking
A collection of useful resources for hacking WordPress and it's plugins and themes
 ylca0/idalib-cli
Agent-native CLI wrapping IDA Pro IDALib for stateless, JSON-output binary analysis: disassembly, Hex-Rays decompilation, CFG, xrefs, strings, and…
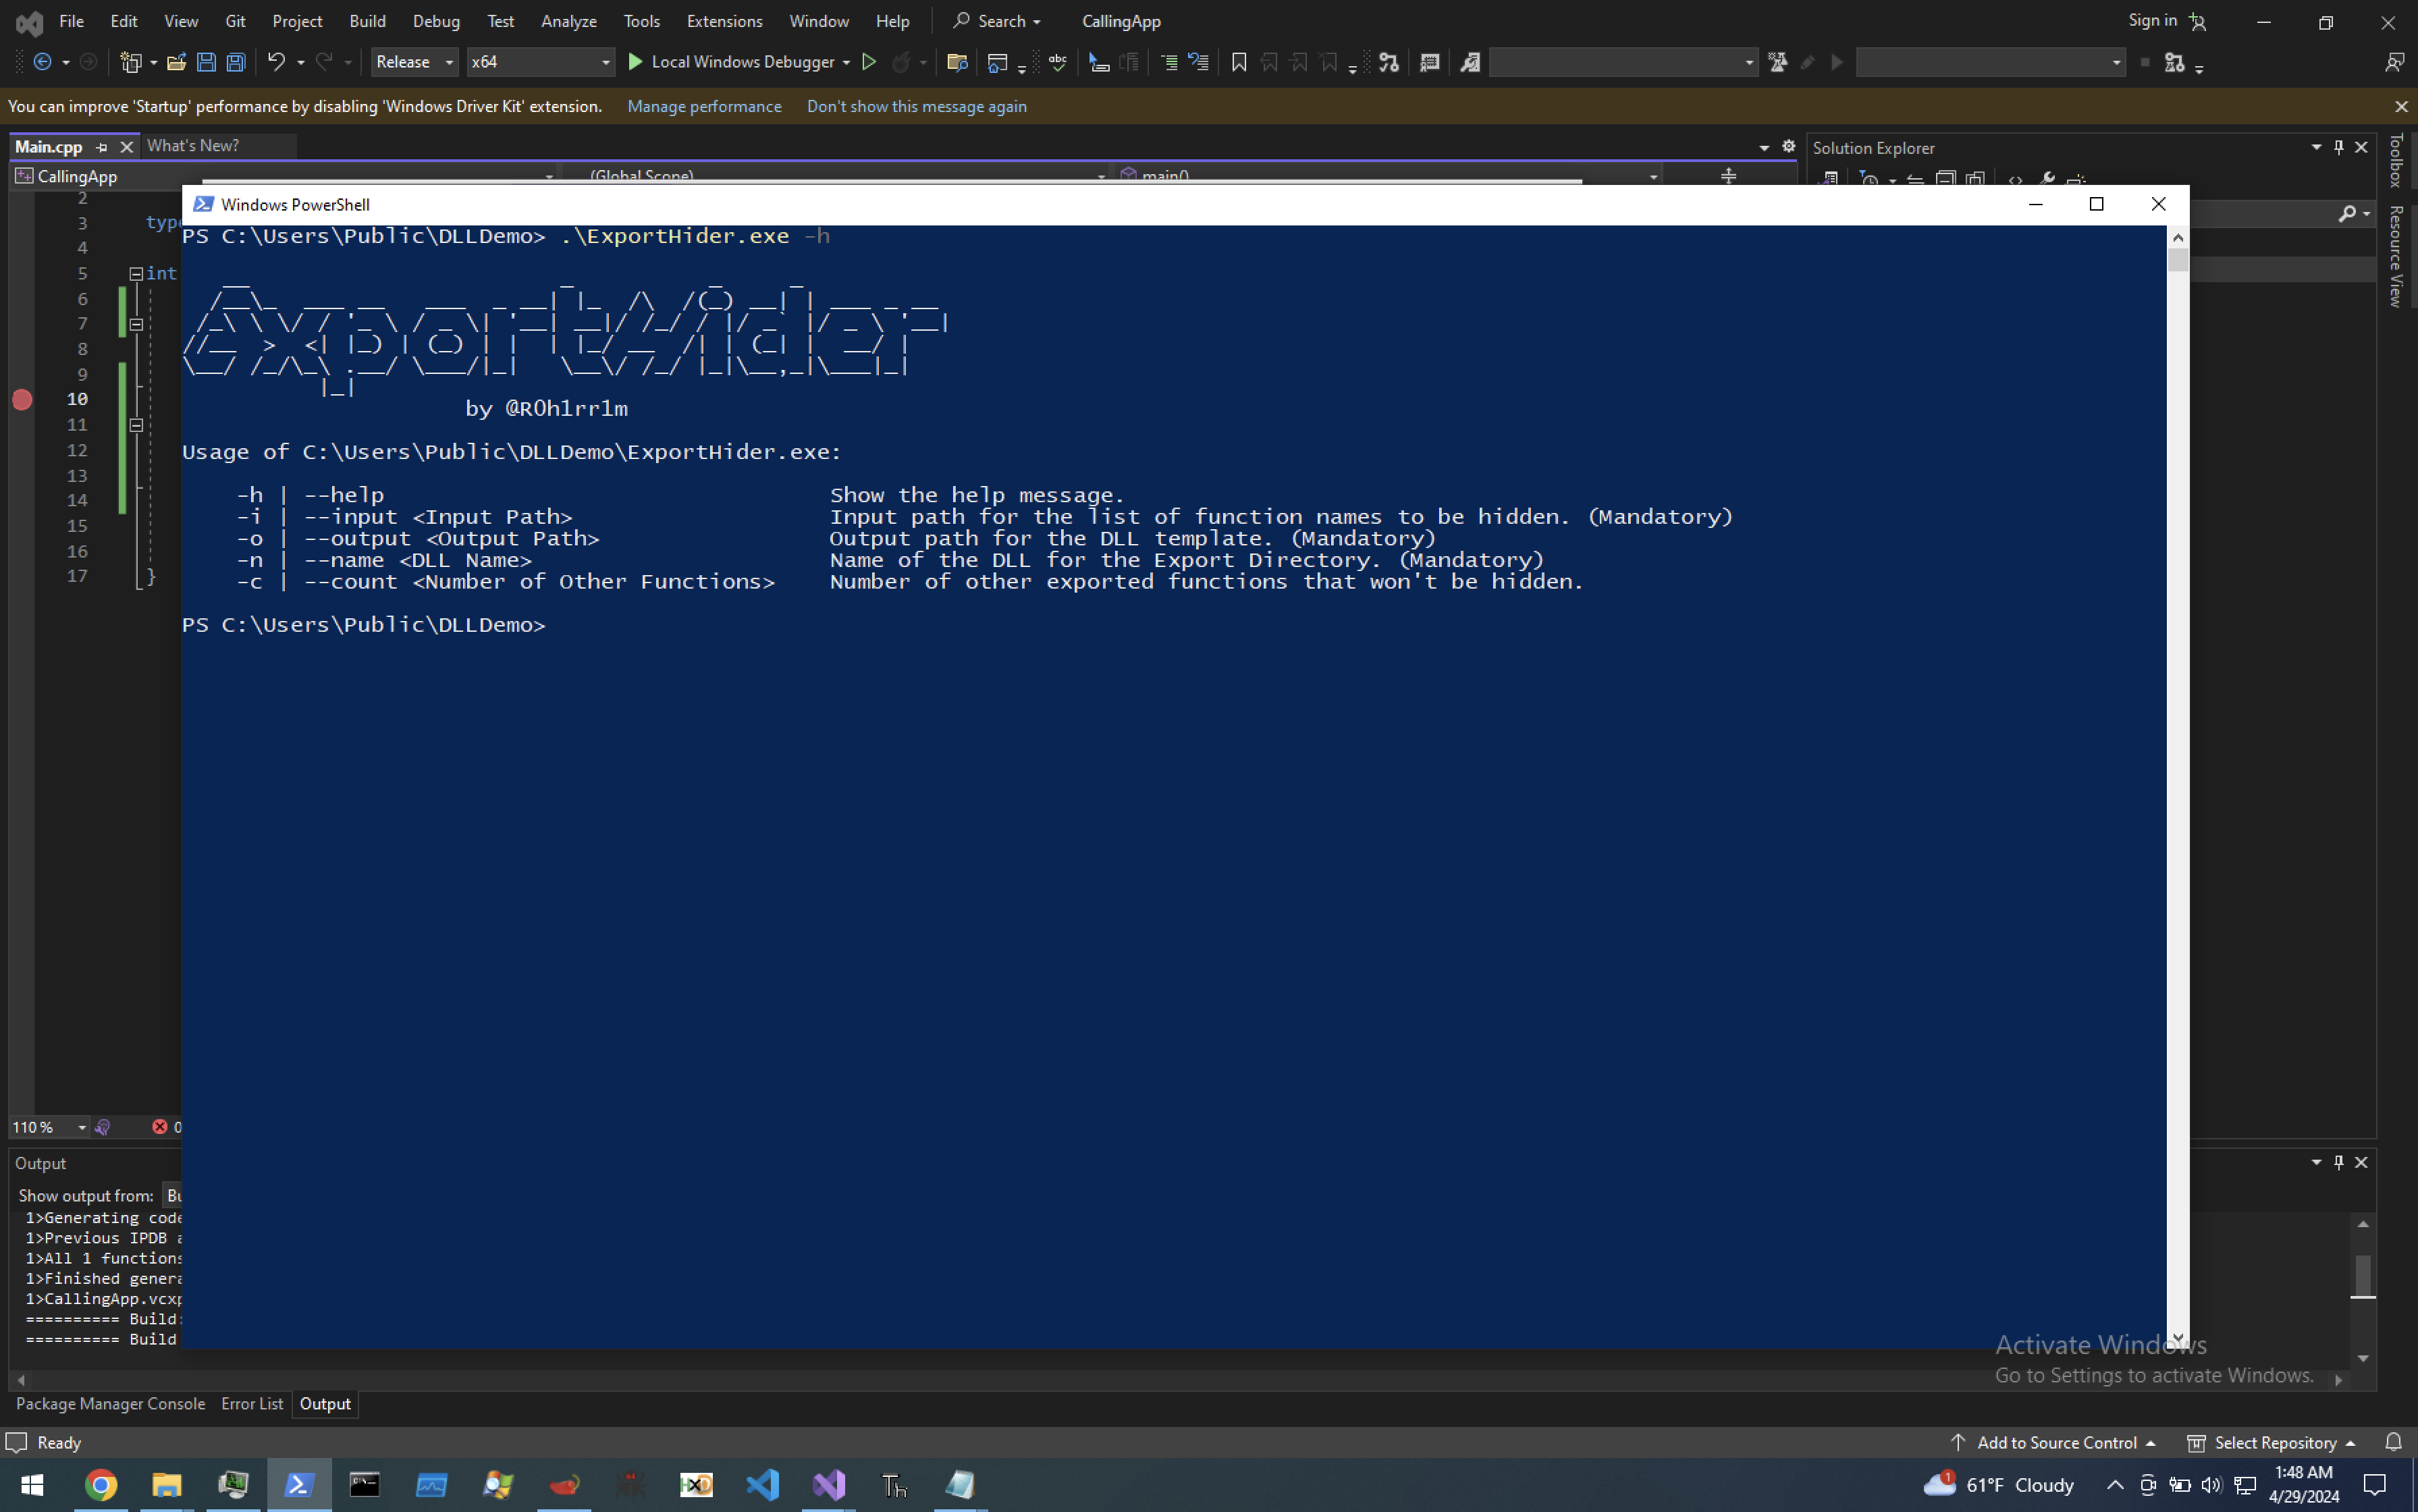 frkngksl/exporthider
ExportHider: Generating Export Table during Runtime to Hide the Exported Functions from the DLL File.
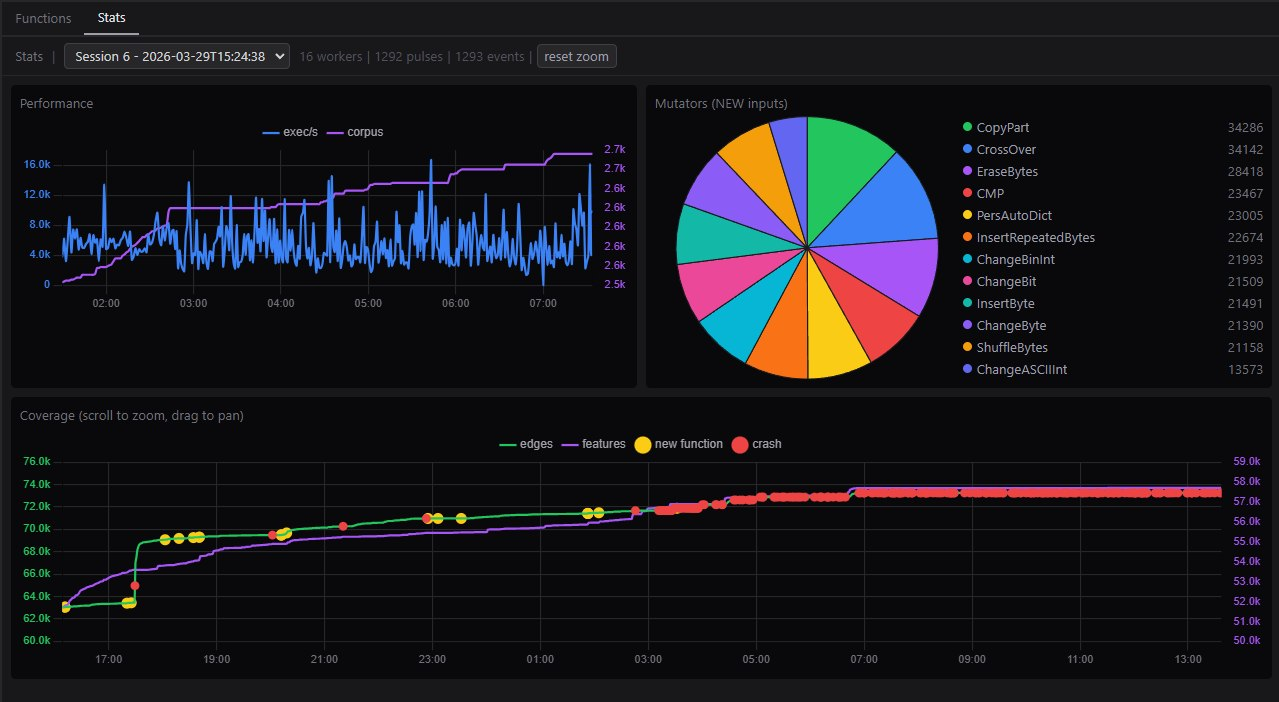 0xbigshaq/apatchy
Fuzzing Framework for Modules in Apache HTTPD Server
 zxgio/ghidra_stack_strings
A script to detect stack-strings by using emulation (leveraging Unicorn)
 hasherezade/pesieve-go
Golang bindings for PE-sieve
 iamavu/zairo
Scans code diffs with context to build an impact graph and uses LLMs to find vulnerabilities, supporting multi-repo scans and CI gating with SARIF…
 shoucheng3/x-stream__xstream_cve-2021-21345_1-4-15
Java XML serialization library with a focus on CVE-2021-21345 exploit analysis and deserialization vulnerability testing for web applications.
 hupe1980/cve-2021-3129
Laravel debug mode - Remote Code Execution (RCE)
 de4dot/de4dot
.NET deobfuscator and unpacker.
 ejfkdev/jscd
Reverse bytenode .jsc (V8 code cache) to JavaScript — static, pure Rust, no patched V8/Node. Node 8→26 / V8 5.8–14.6; 25k .jsc tested, 0 fail.
 aftermathlabs/vmp2
Unpack and deobfuscate VMProtect 2 protected binaries with an emulation-based VM explorer, handler profiler, and experimental LLVM recompiler for…
 sentinel-one/peafl64
Static Binary Instrumentation tool for Windows x64 executables
 google/path-auditor
Runtime libc function auditor that detects file access race conditions and symlink vulnerabilities by hooking filesystem syscalls via LD_PRELOAD,…