
jaeles
 jaeles-project/jaeles
The Swiss Army knife for automated Web Application Testing
dynamic-code-analysispenetration-testingvulnerability-scanners+2
2.4k
jaeles-project/jaelesThe Swiss Army knife for automated Web Application Testing
 wapiti-scanner/wapiti
Web vulnerability scanner written in Python3
 hackmanit/tinja
TInjA is a CLI tool for testing web pages for template injection vulnerabilities and supports 44 of the most relevant template engines for eight…
 dobin/burpsentinel
GUI Burp Plugin to ease discovering of security holes in web applications
 shoucheng3/x-stream__xstream_cve-2021-21345_1-4-15
Java XML serialization library with a focus on CVE-2021-21345 exploit analysis and deserialization vulnerability testing for web applications.
 shoucheng3/esapi__esapi-java-legacy_cve-2022-23457_2-2-3-1
Enterprise Security API library providing security controls for Java web applications, including authentication, access control, input validation,…
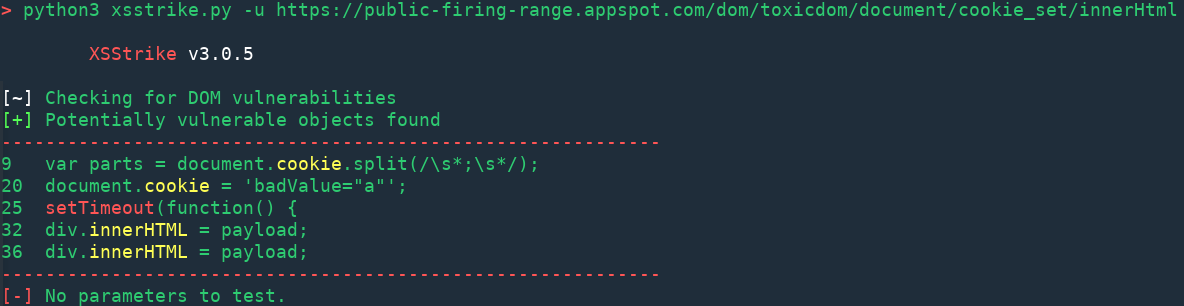
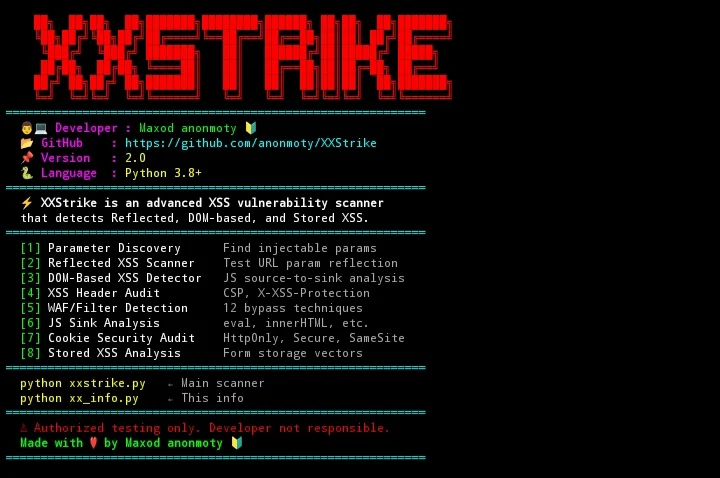 anonmoty/xxstrike
XSStrike based XSS scanner with custom features. Detects XSS vulnerabilities in web applications.
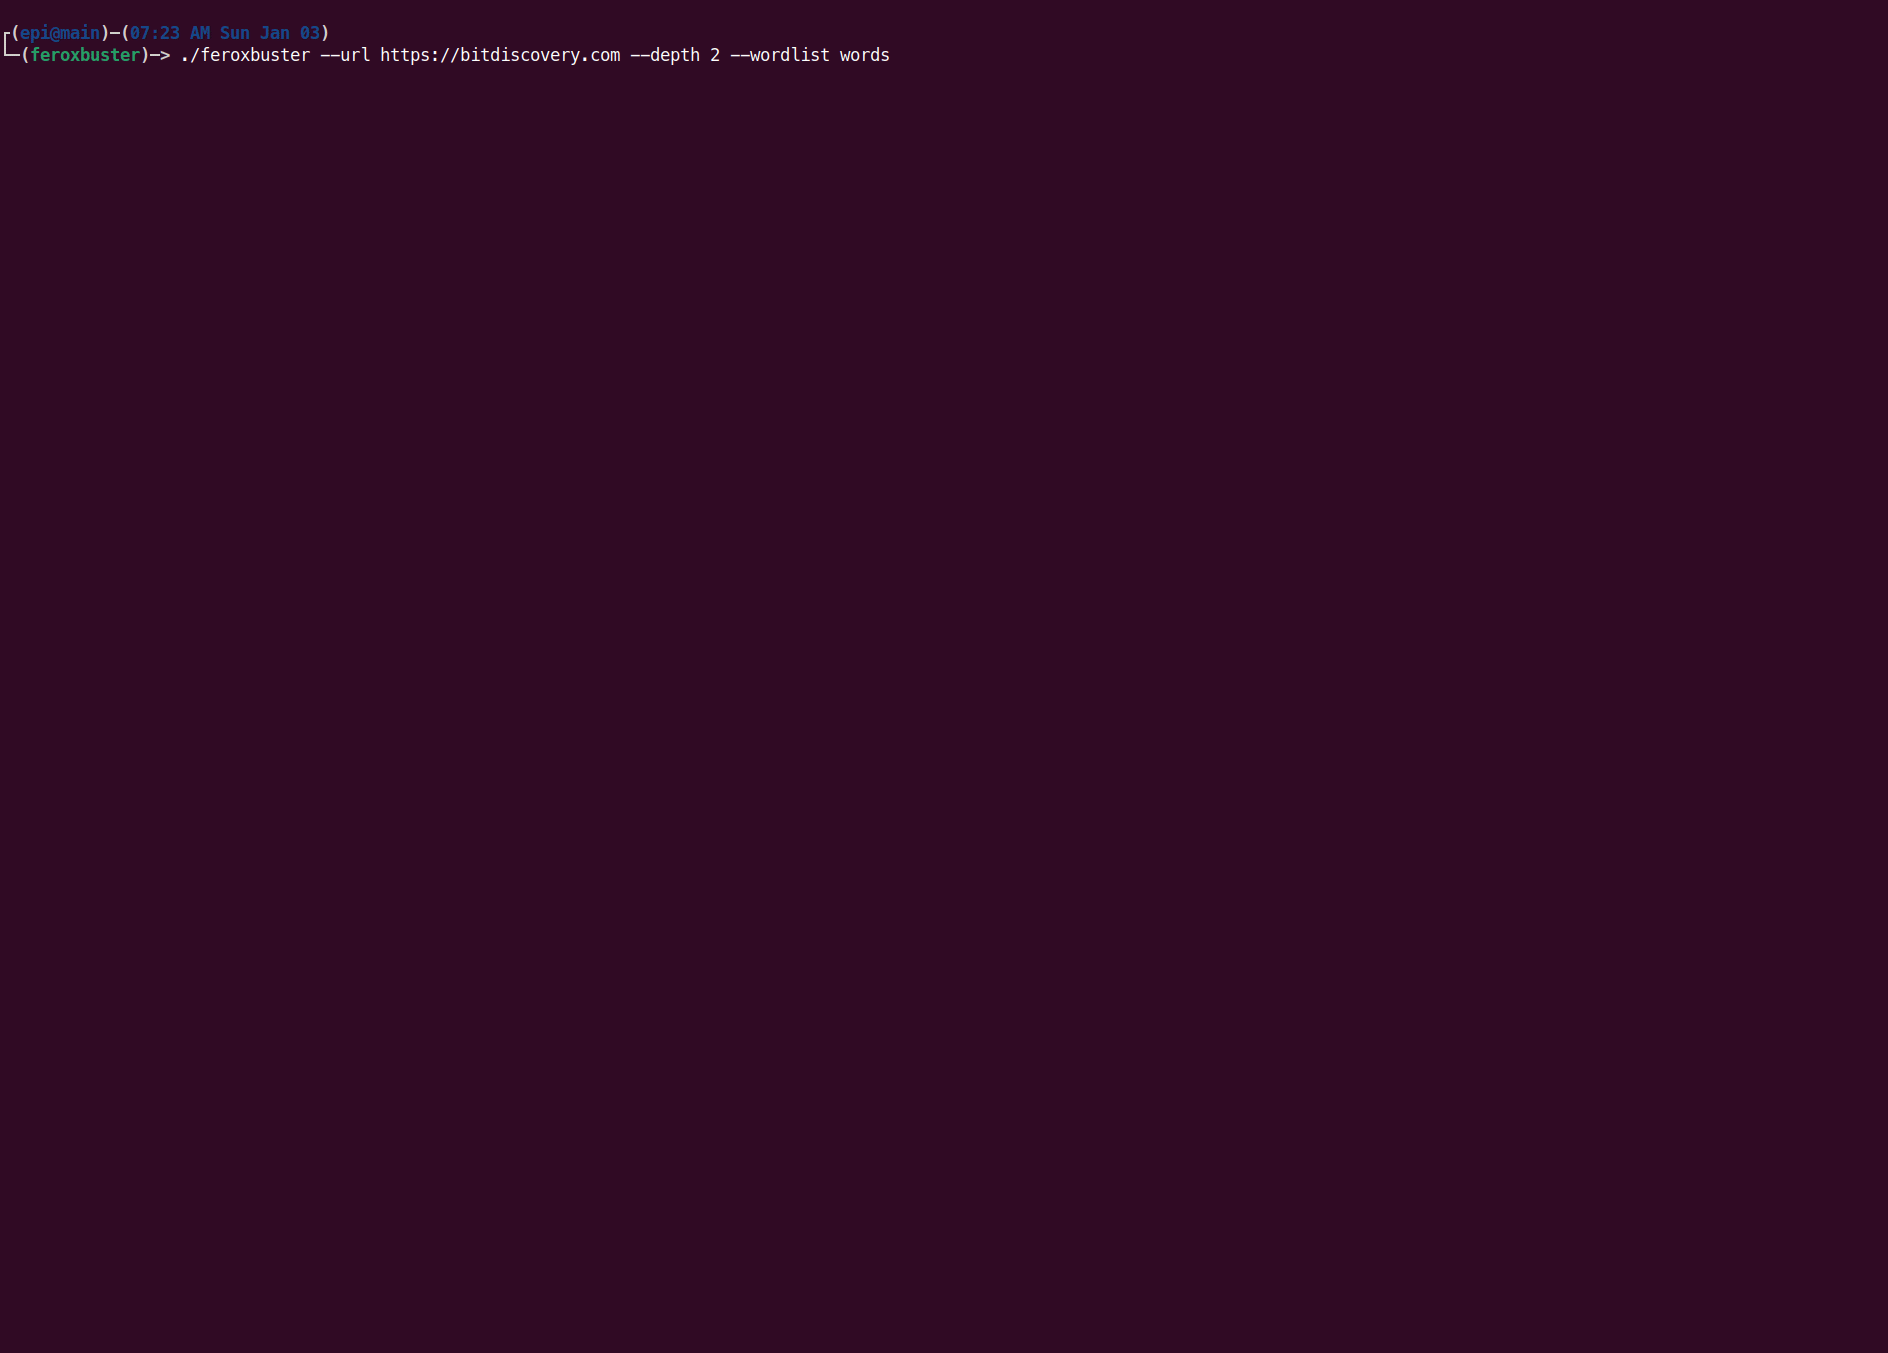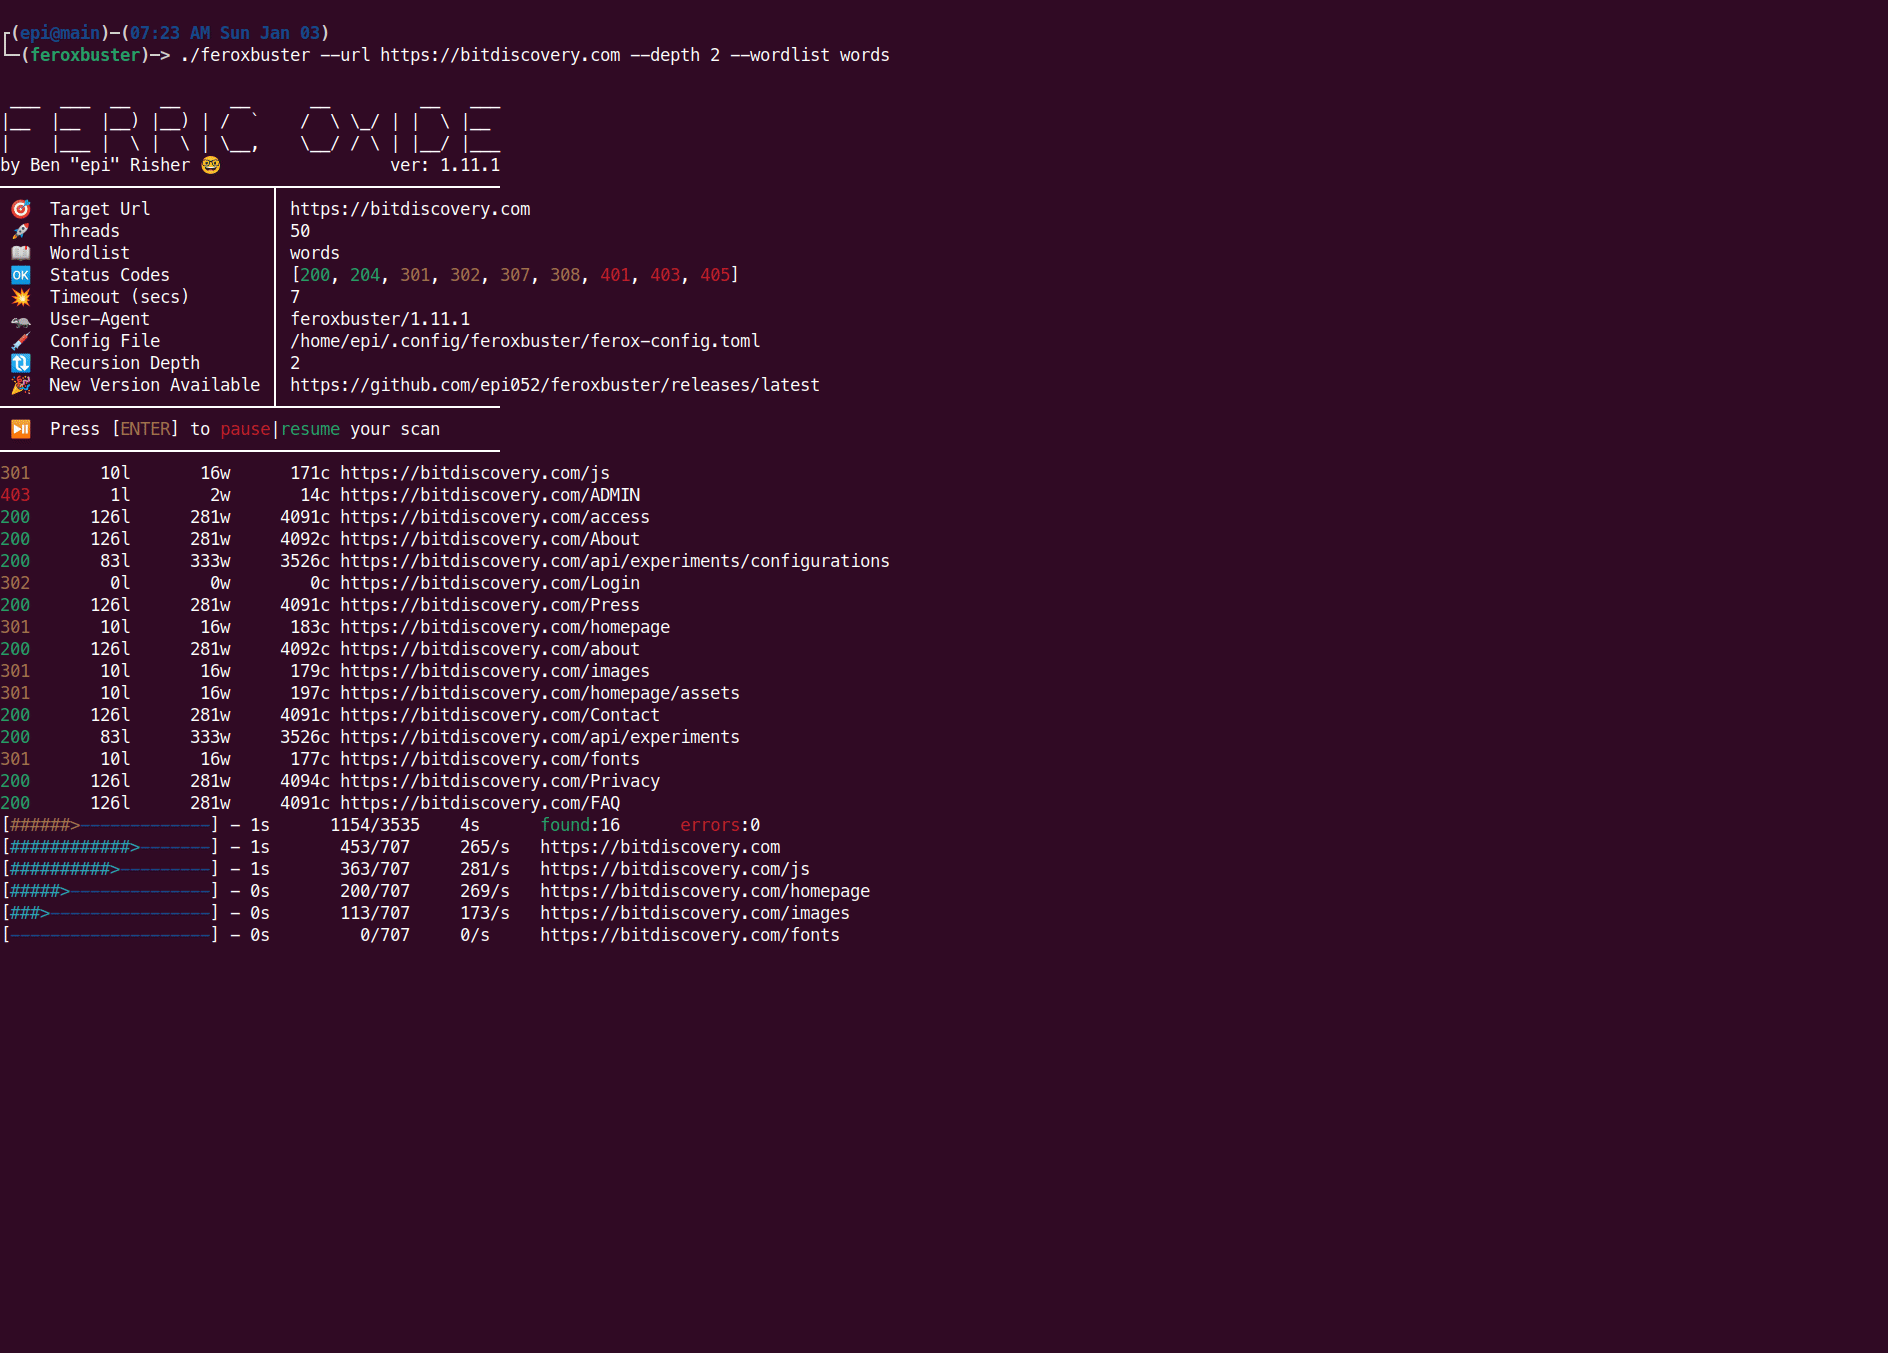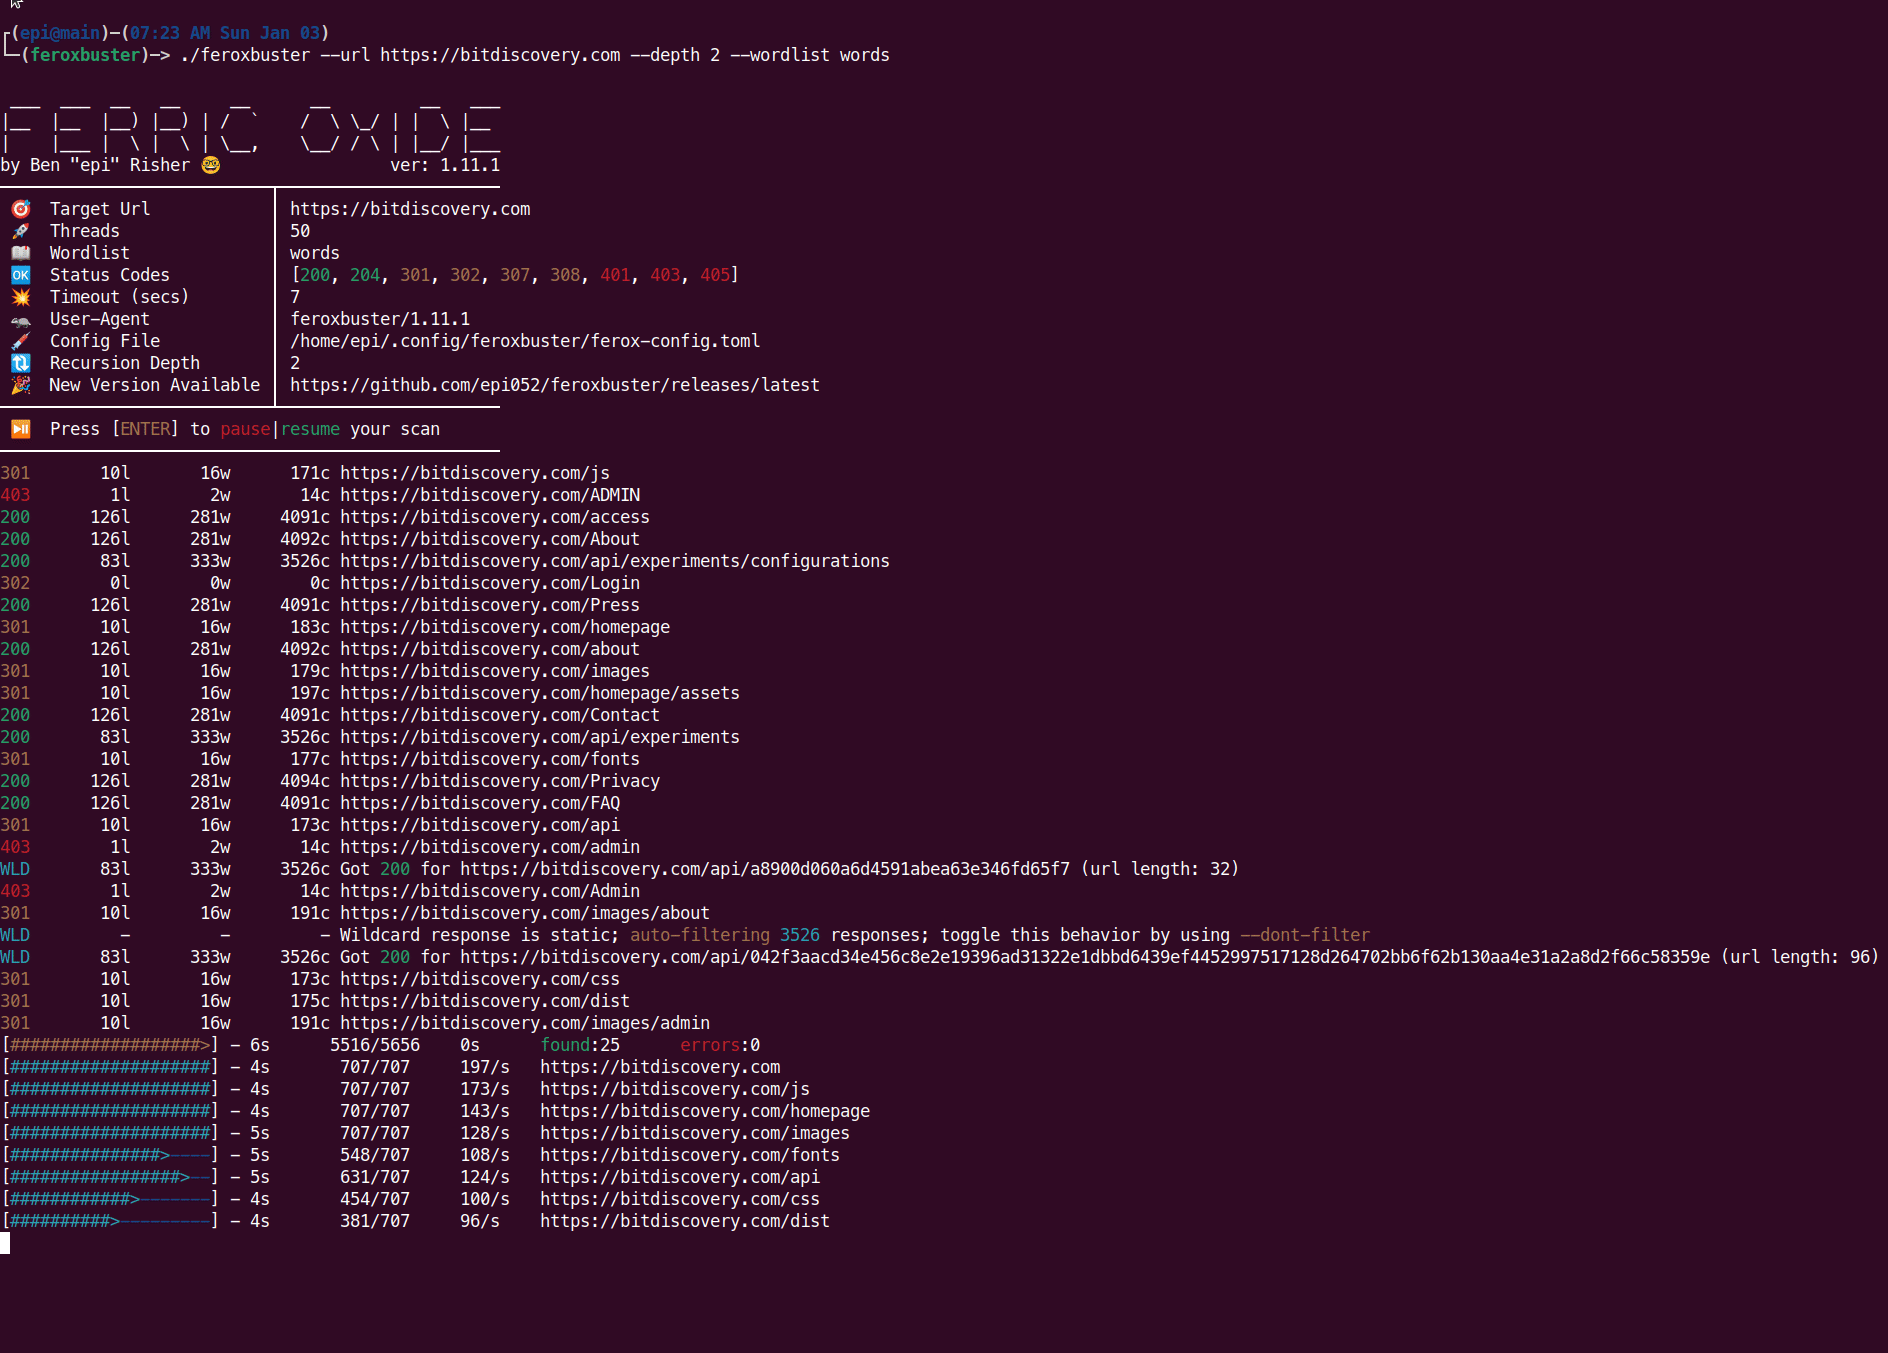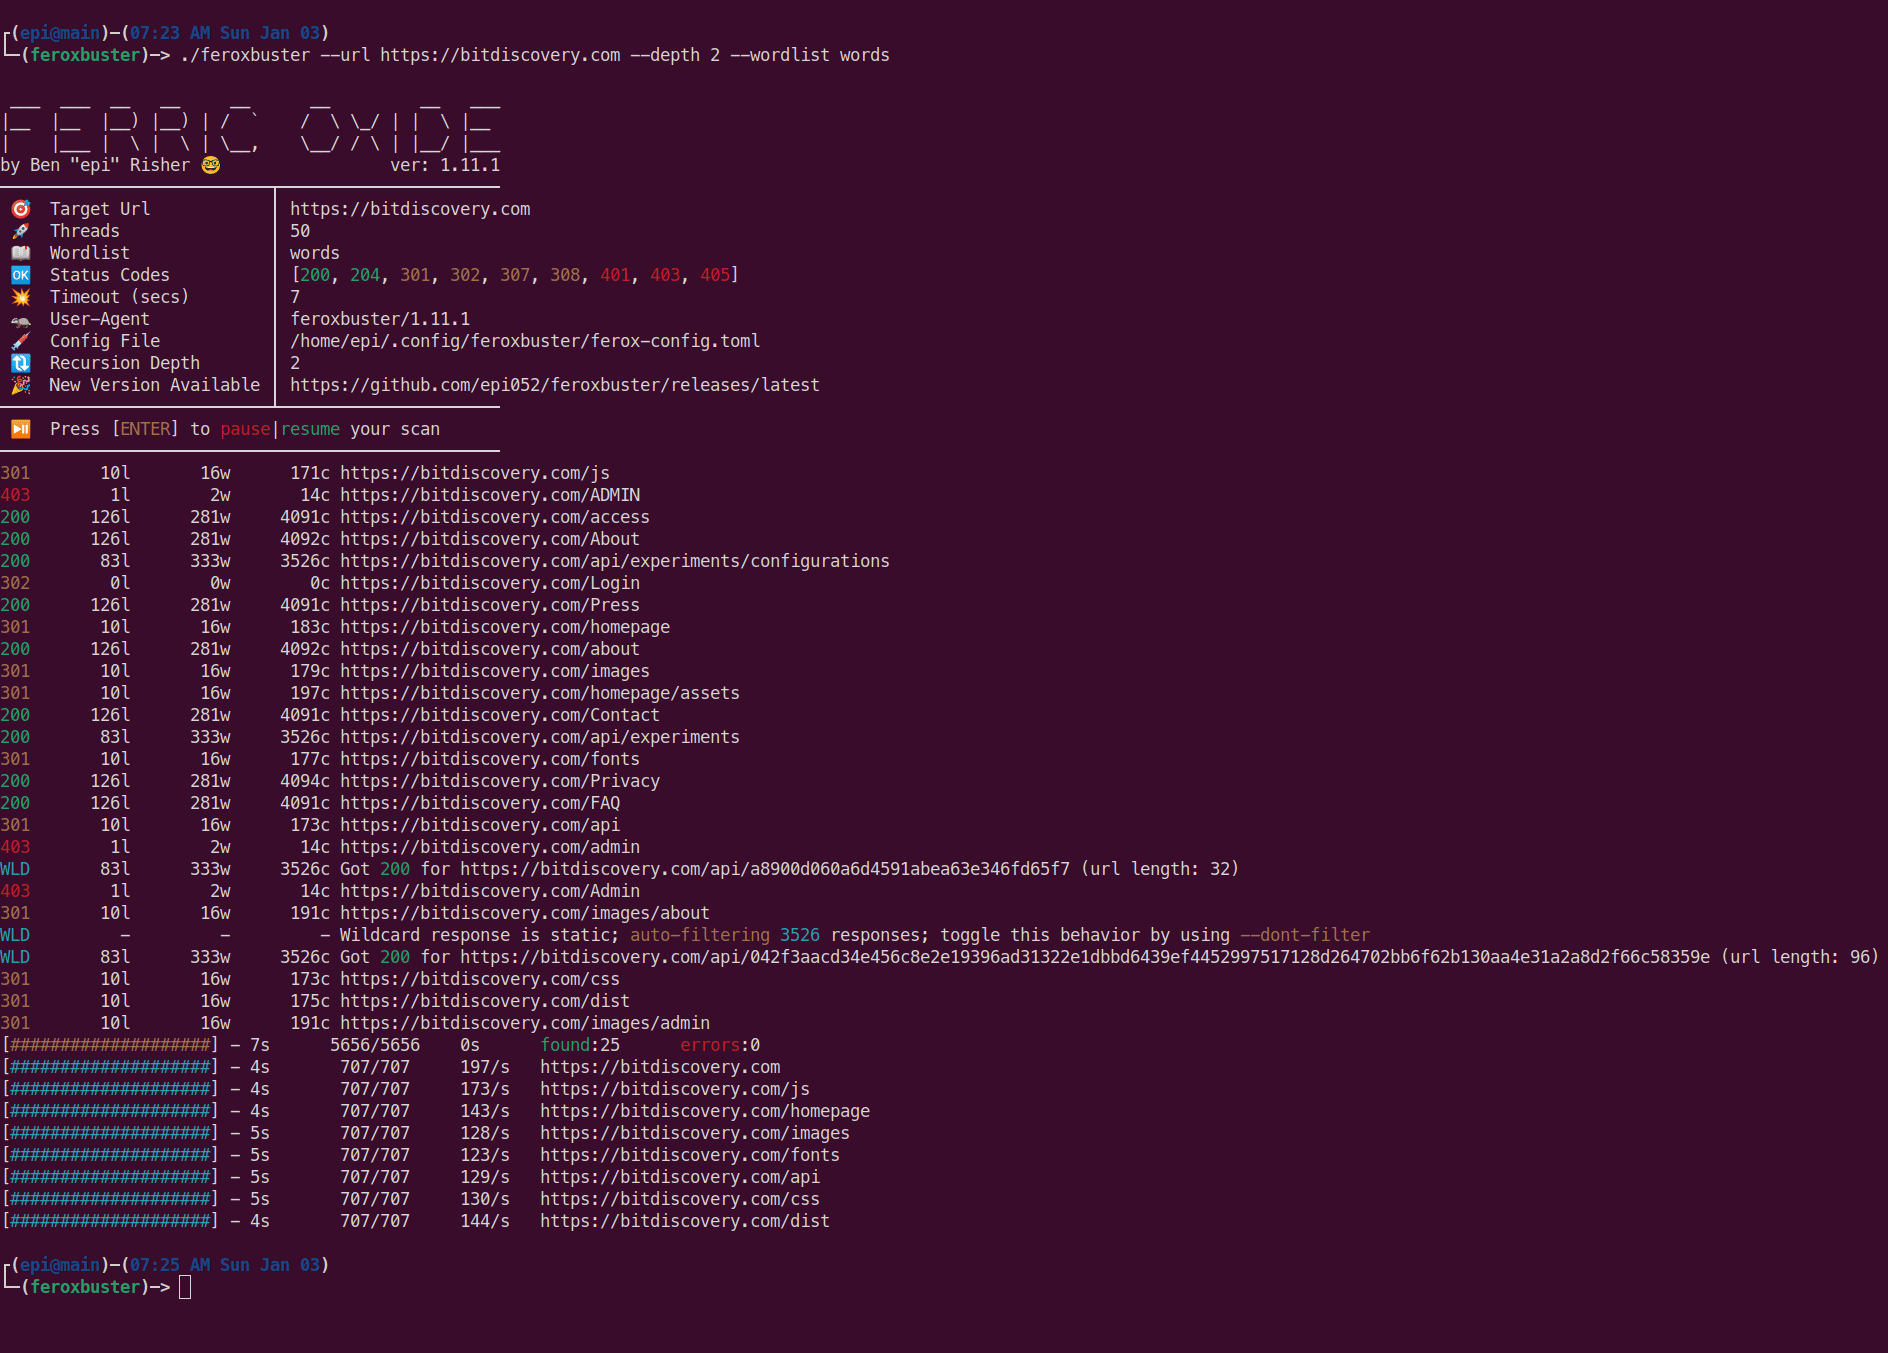 epi052/feroxbuster
A fast, simple, recursive content discovery tool written in Rust.
 go-delve/delve
Source-level debugger for Go with CLI, API, and headless modes; supports breakpoints, variable inspection, and execution tracing for efficient…
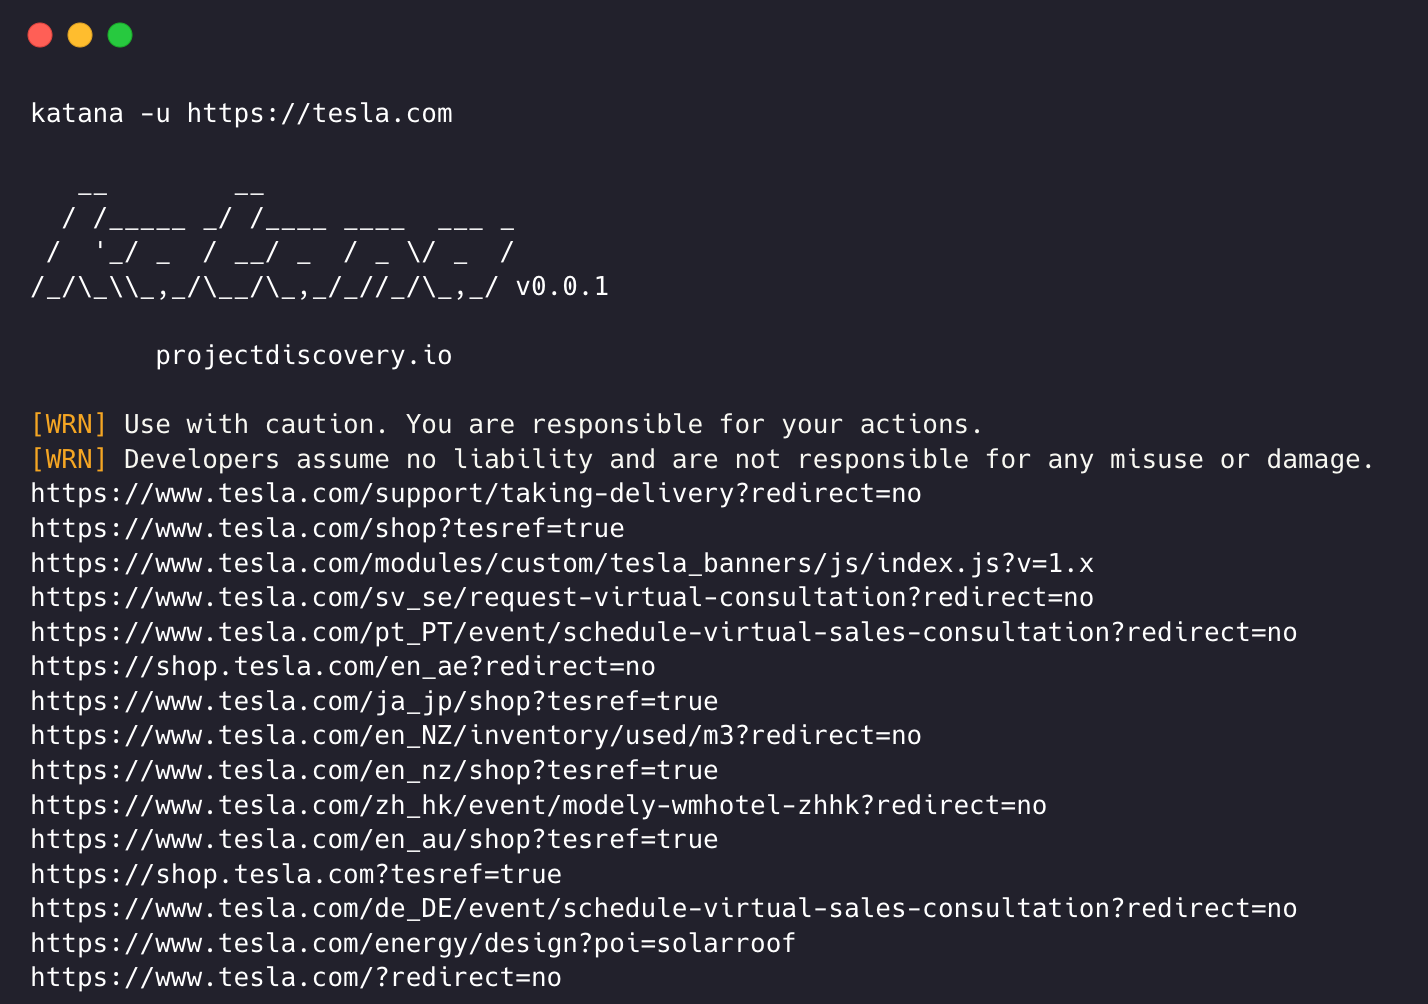 projectdiscovery/katana
A next-generation crawling and spidering framework.
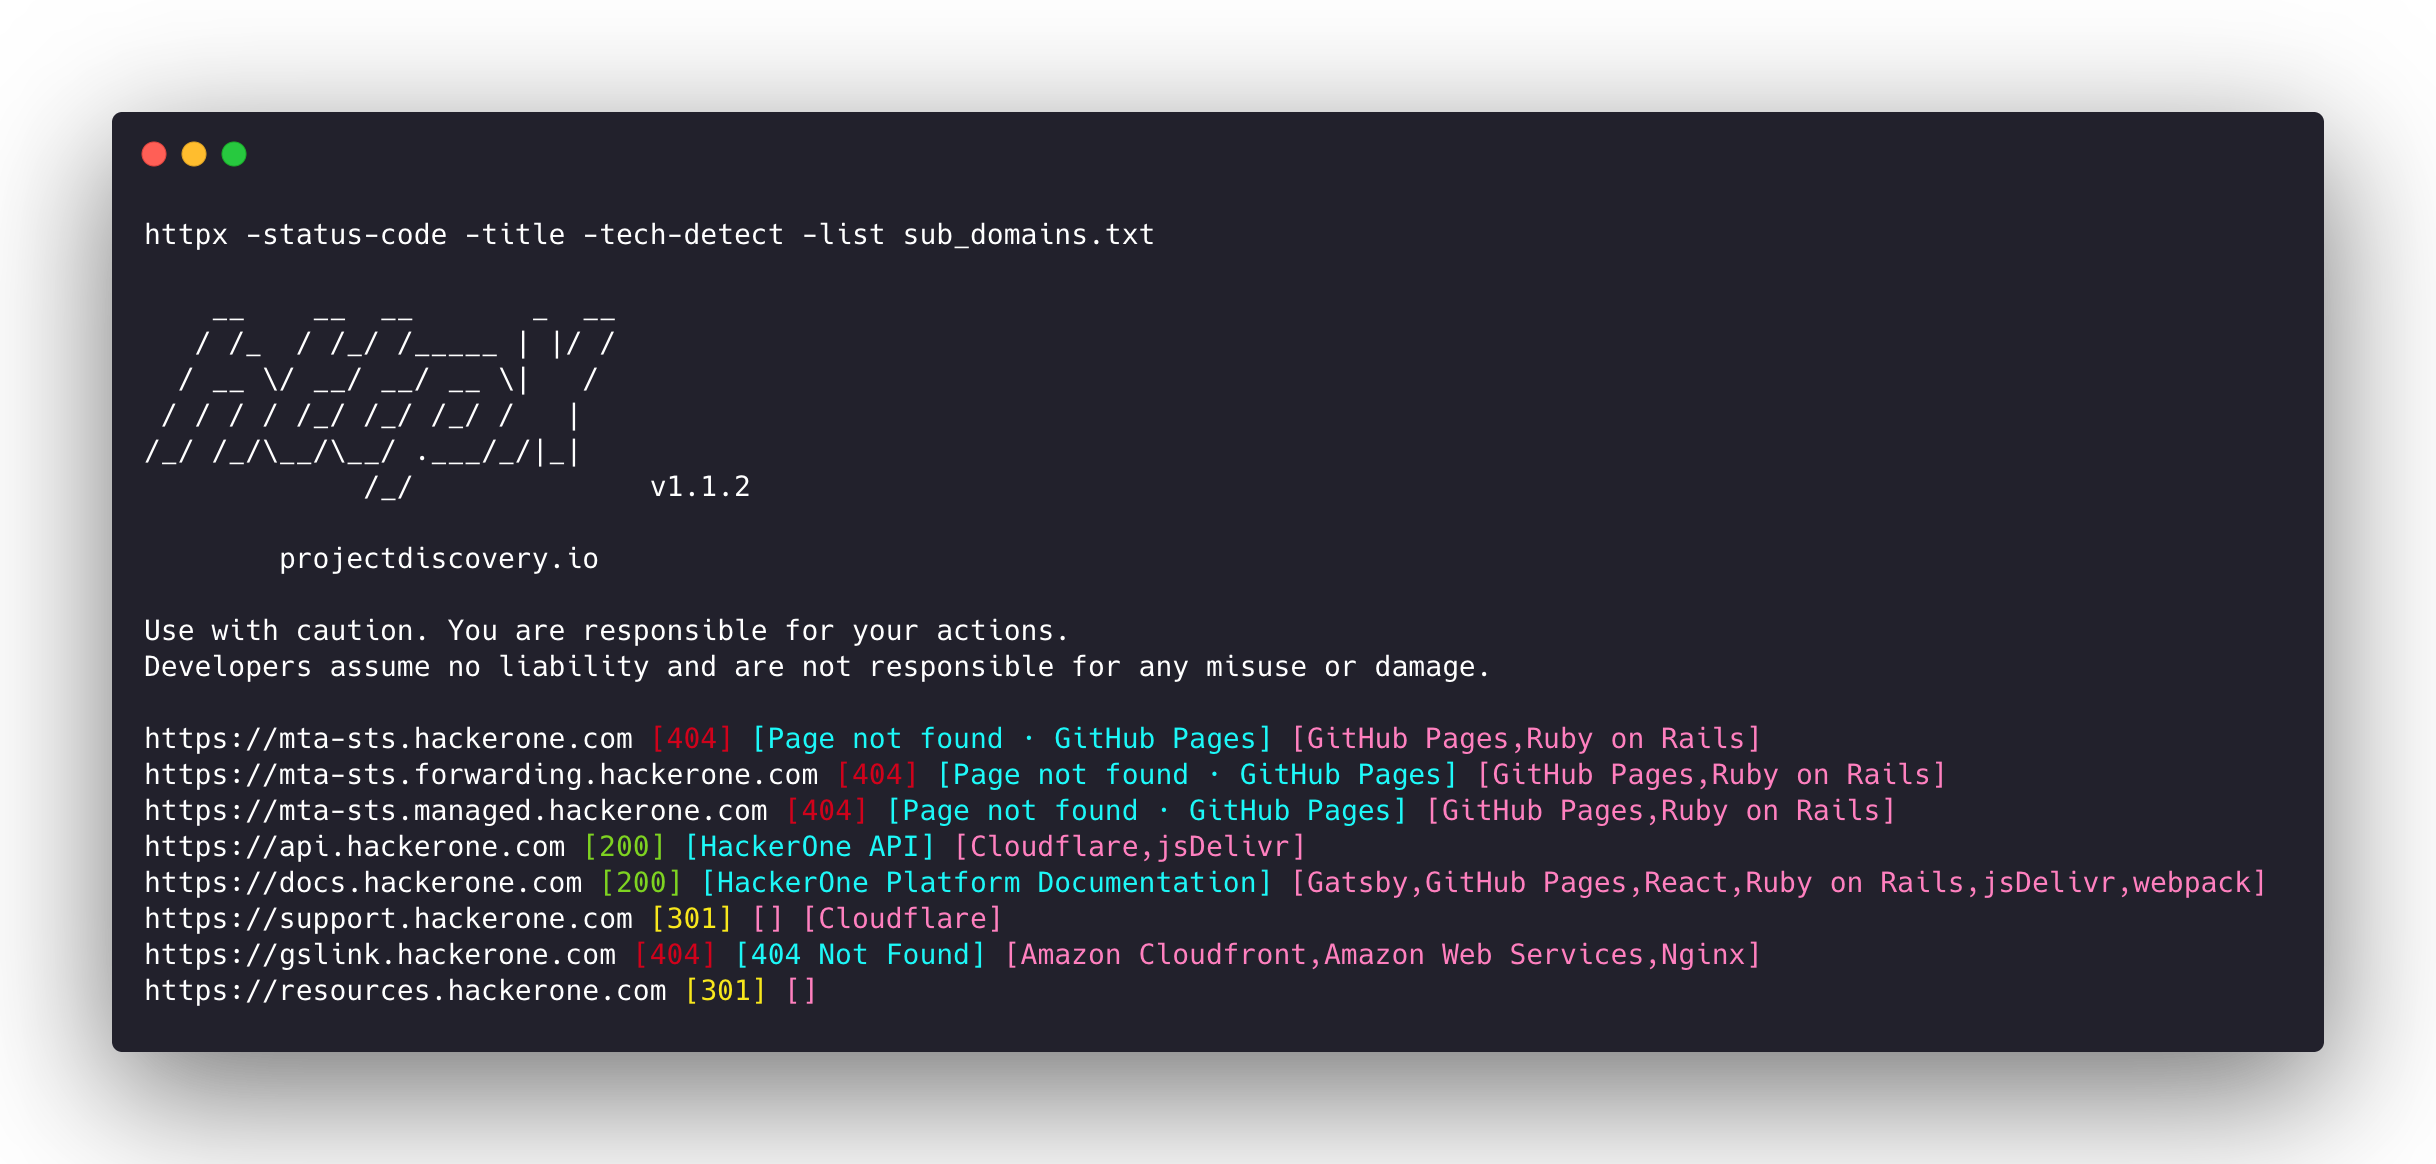 projectdiscovery/httpx
Fast, multi-probe HTTP toolkit for reconnaissance and information gathering. Probes TLS, CSP, headers, tech stack, and CDN. Supports matchers,…
 rr-debugger/rr
Record and replay framework for deterministic debugging of multi-threaded applications, enabling reverse execution, hardware watchpoints, and…
 owasp/nettacker
Automated Penetration Testing Framework - Open-Source Vulnerability Scanner - Vulnerability Management
 microsoft/detours
Runtime Windows API interception library for hooking, monitoring, and instrumenting function calls. Supports binary rewriting and DLL injection,…
 tanprathan/mobileapp-pentest-cheatsheet
The Mobile App Pentest cheat sheet was created to provide concise collection of high value information on specific mobile application penetration…
 pizlonator/fil-c
Fil-C: completely compatible memory safety for C and C++
 tomnomnom/gf
A wrapper around grep, to help you grep for things