
Frida-Labs
 dere-ad2001/frida-labs
The repo contains a series of challenges for learning Frida for Android Exploitation.
android-securitybinary-analysisctf+6
1.3k7 months ago
dere-ad2001/frida-labsThe repo contains a series of challenges for learning Frida for Android Exploitation.
 chichou/grapefruit
Open-source mobile security testing suite for iOS and Android. Previously Passionfruit
 narfindustries/http-garden
Differential testing framework for HTTP implementations
 byt3bl33d3r/offensivedlr
Toolbox containing research notes & PoC code for weaponizing .NET's DLR
 google/oss-fuzz-gen
LLM powered fuzzing via OSS-Fuzz.
 microsoft/windbg-samples
Sample extensions, scripts, and API uses for WinDbg.
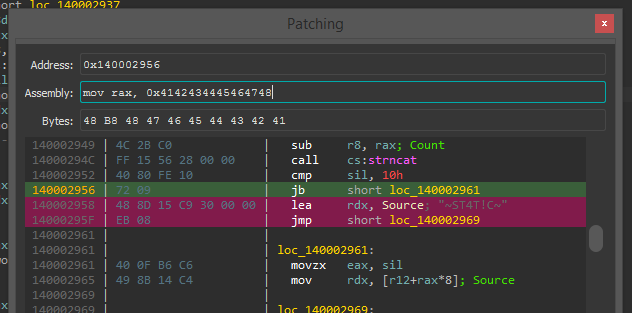 gaasedelen/patching
An Interactive Binary Patching Plugin for IDA Pro
 splx-ai/agentic-radar
A security scanner for your LLM agentic workflows
 steven-michaud/hookcase
Tool for reverse engineering macOS/OS X
 cc1a2b/jshunter
jshunter is a command-line tool designed for analyzing JavaScript files and extracting endpoints. This tool specializes in identifying sensitive…
 dolevf/graphw00f
GraphQL server engine fingerprinting tool that sends benign and malformed queries to identify backend technology and assess security defenses via the…
 smackers/smack
Modular software verification toolchain that translates LLVM IR into Boogie intermediate verification language for bounded and experimental unbounded…
 rogerorr/nttrace
An strace-like program for the Windows 'native' API
 trailofbits/polytracker
An LLVM-based instrumentation tool for universal taint tracking, dataflow analysis, and tracing.
 ghostvectoracademy/dllhijackhunter
Automated DLL Hijacking Discovery, Validation, and Confirmation. Turning local misconfigurations into weaponized, confirmed attack paths.
 chichou/vscode-frida
Unofficial frida extension for VSCode
 swdunlop/andbug
Scriptable debugger for Android Dalvik VM using JDWP/DDM interfaces to hook methods, inspect process state, and modify runtime behavior without…
 zer0condition/reversekit
x64 Dynamic Reverse Engineering Toolkit