
BurpSentinel
 dobin/burpsentinel
GUI Burp Plugin to ease discovering of security holes in web applications
dynamic-code-analysispenetration-testingvulnerability-analysis+3
153
dobin/burpsentinelGUI Burp Plugin to ease discovering of security holes in web applications
 we5ter/flerken
A Solution For Cross-Platform Obfuscated Commands Detection presented on CIS2019 China. 动静态Bash/CMD/PowerShell命令混淆检测框架 - CIS 2019大会
 nccgroup/dibf
Windows NT ioctl bruteforcer and modular fuzzer
 worksbutnottested/lightkeeper
Maps execution-coverage data onto Ghidra disassembly to highlight visited code paths and accelerate reverse-engineering workflows.
 r00tkitsmm/pishi
Pishi is a code coverage tool like kcov for macOS.
 robertdfrench/ifuncd-up
GNU IFUNC is the real culprit behind CVE-2024-3094
 tca-iscas/cooper-ndss-2022
A tool for effective testing the binding layer of scripting languages
 binsec/xyntia
Xyntia, the black-box deobfuscator
 1rhino2/fnprint
match functions in binaries by what they do, not what their bytes look like. behavioral function fingerprinting via microexecution.
 nccgroup/winstrument
Winstrument is a framework of modular scripts to aid in instrumenting Windows software using Frida for reverse engineering and attack surface…
 stealthcopter/wordpress-hacking
A collection of useful resources for hacking WordPress and it's plugins and themes
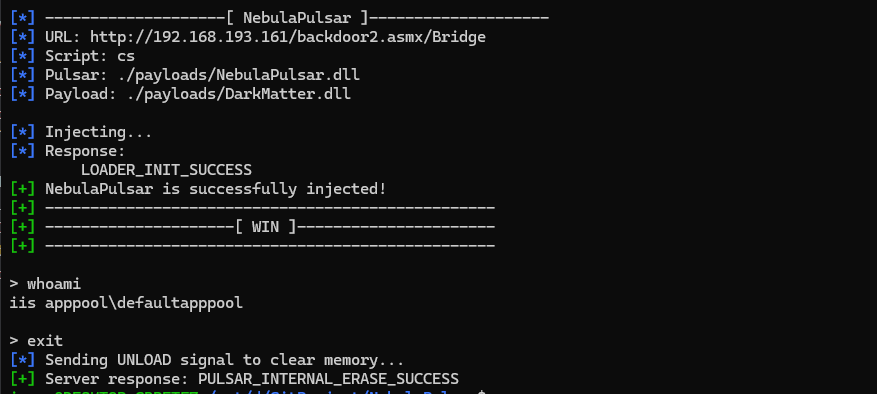 iss4cf0ng/nebulapulsar
NebulaPulsar is a proof-of-concept in-memory implant framework for Java (JSP) and ASP.NET (ASPX/ASHX/ASMX) webshells, originally developed as part of…
 dvyukov/centipede
Distributed coverage-guided fuzzing engine compatible with libFuzzer targets; scales to thousands of concurrent jobs, uses sanitizers and corpus…
 0x3c3e/slides
CodeQL + DTrace = Memory Disclosure Vulnerabilities in XNU
 momalab/icsfuzz
Instrumented fuzzer for PLC-based ICS control applications, targeting Codesys runtime on Wago controllers to uncover memory corruption and…
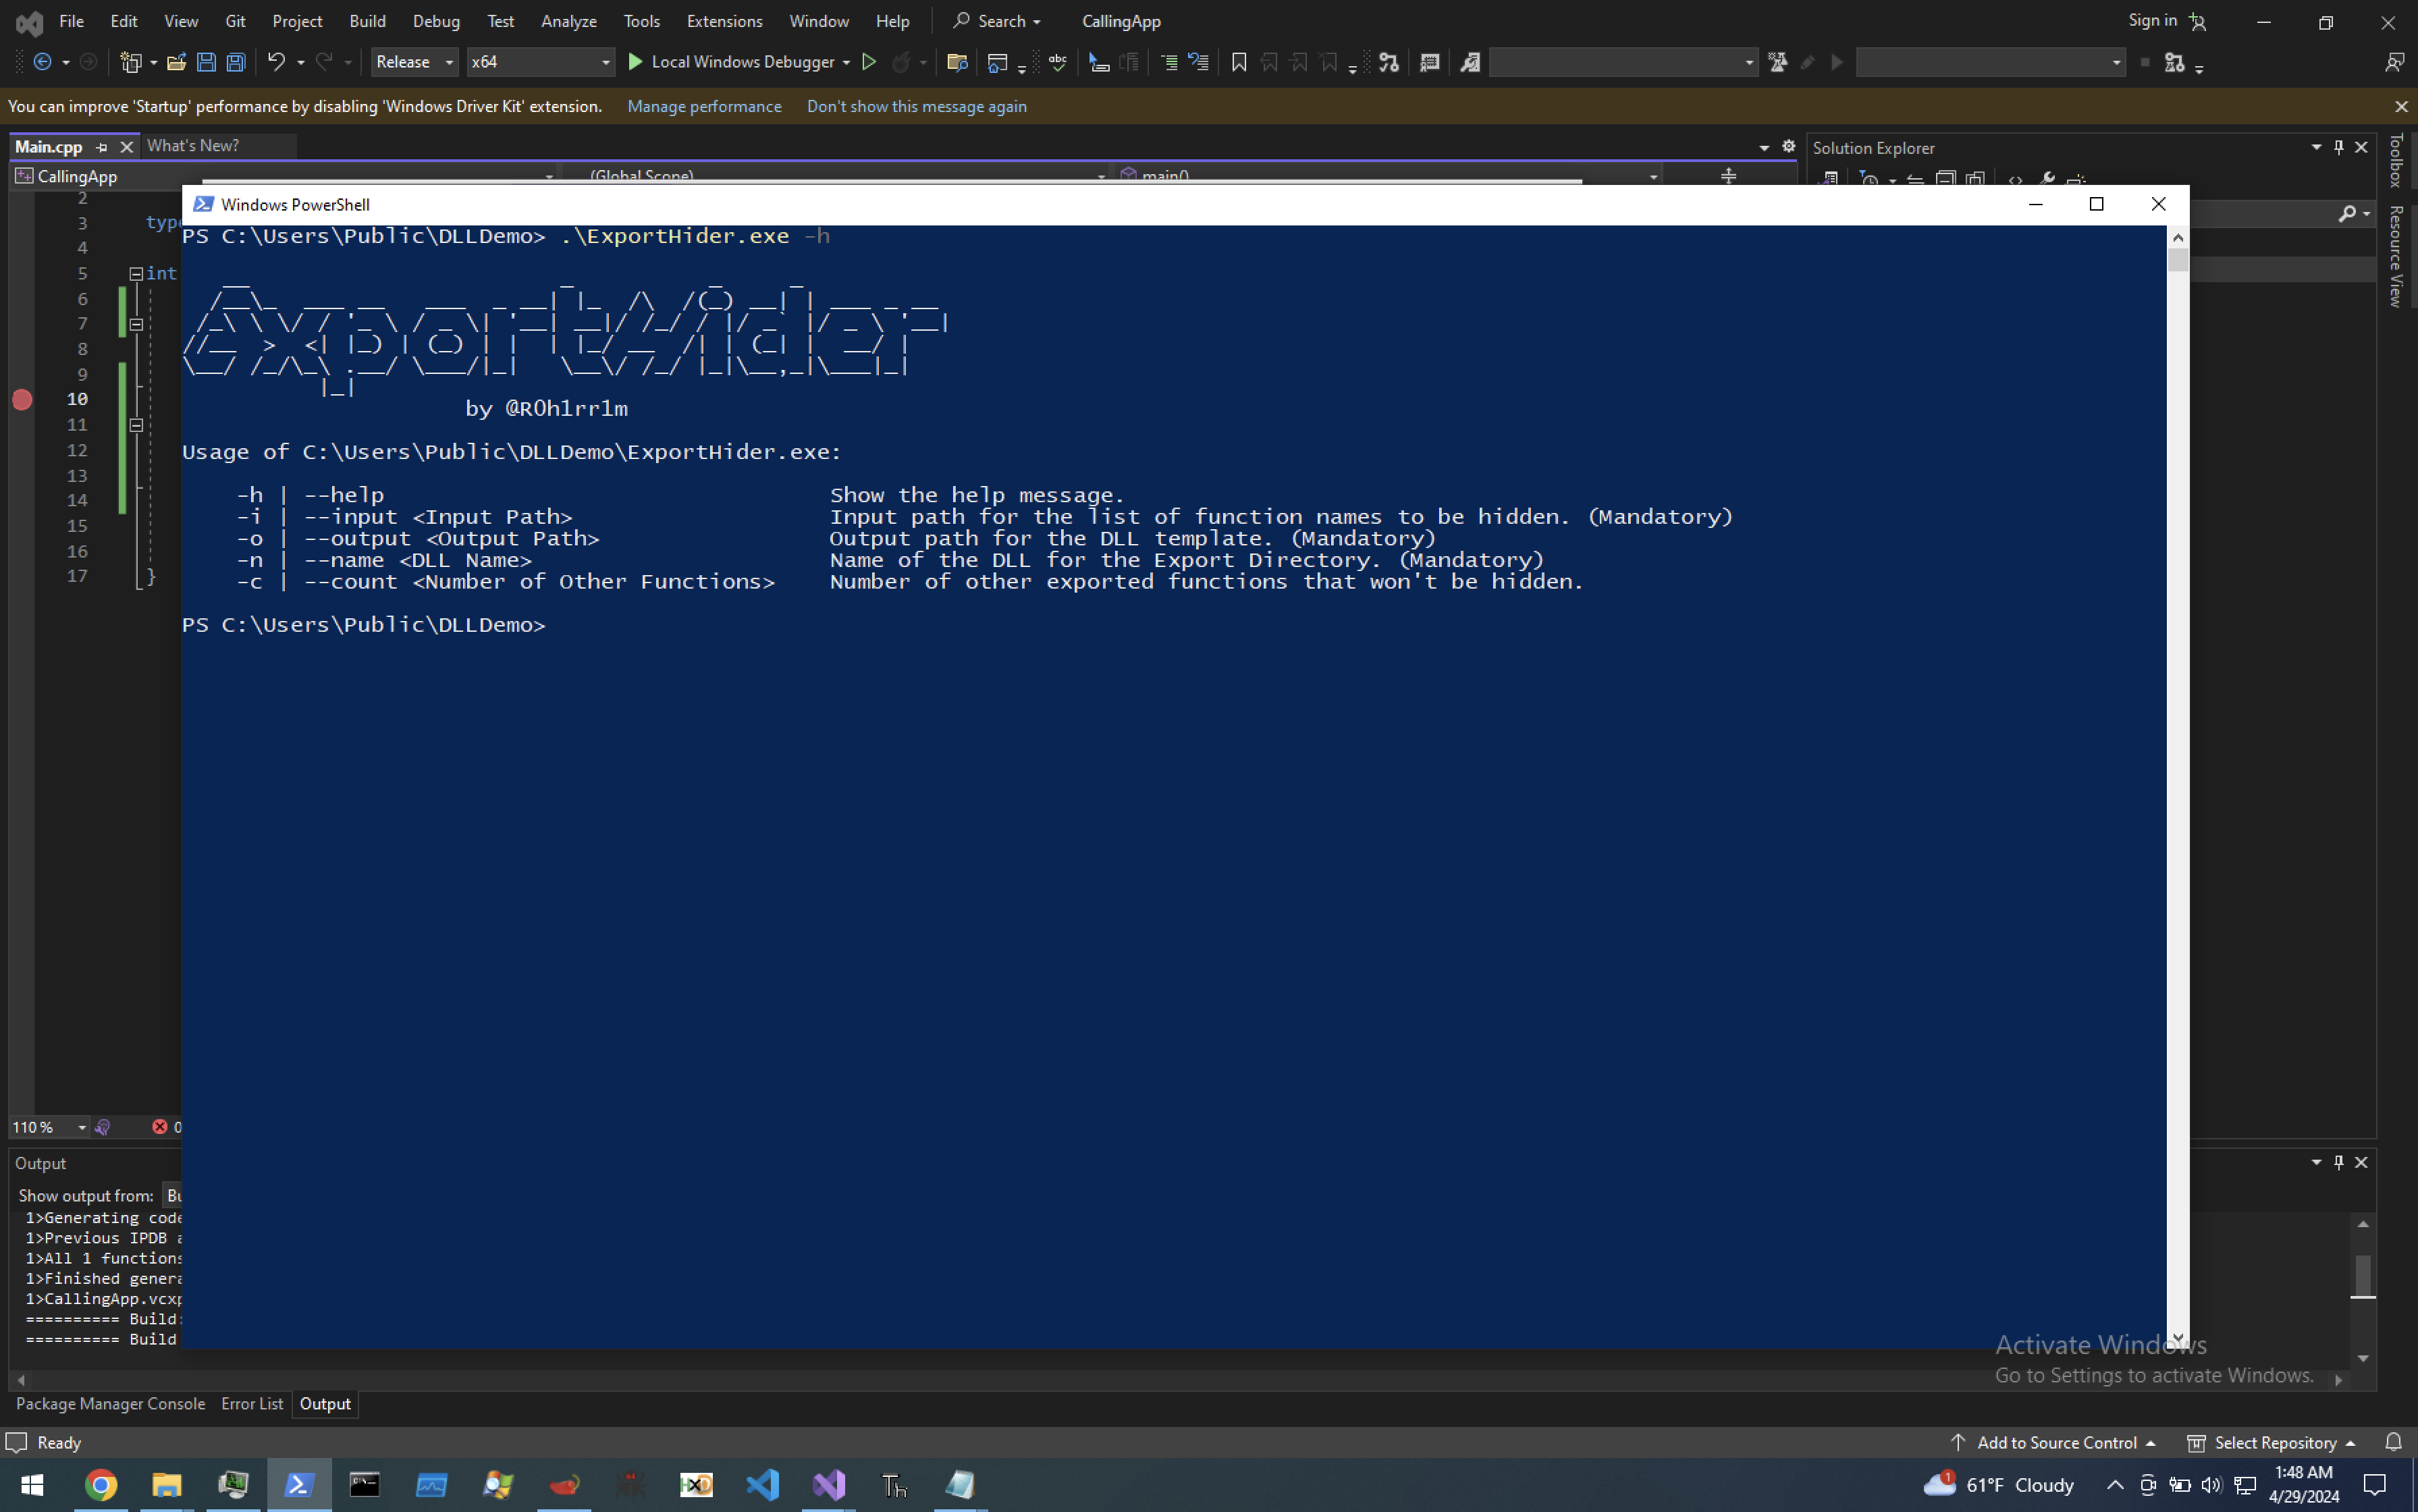 frkngksl/exporthider
ExportHider: Generating Export Table during Runtime to Hide the Exported Functions from the DLL File.
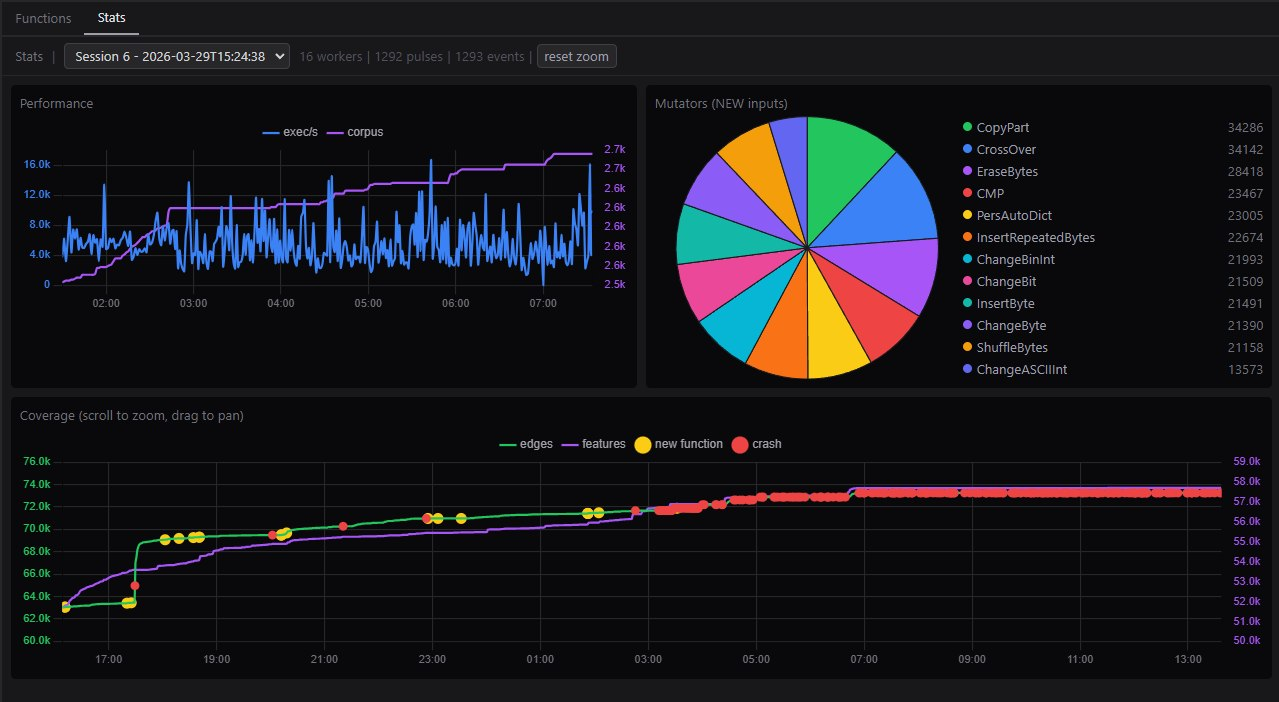 0xbigshaq/apatchy
Fuzzing Framework for Modules in Apache HTTPD Server
 zxgio/ghidra_stack_strings
A script to detect stack-strings by using emulation (leveraging Unicorn)