
polytracker
 trailofbits/polytracker
An LLVM-based instrumentation tool for universal taint tracking, dataflow analysis, and tracing.
binary-analysisdynamic-code-analysiseducation+4
599
trailofbits/polytrackerAn LLVM-based instrumentation tool for universal taint tracking, dataflow analysis, and tracing.
 chichou/vscode-frida
Unofficial frida extension for VSCode
 ghostvectoracademy/dllhijackhunter
Automated DLL Hijacking Discovery, Validation, and Confirmation. Turning local misconfigurations into weaponized, confirmed attack paths.
 fuzzysecurity/fermion
Fermion, an electron wrapper for Frida & Monaco.
 skylined/bugid
Detect, analyze and uniquely identify crashes in Windows applications
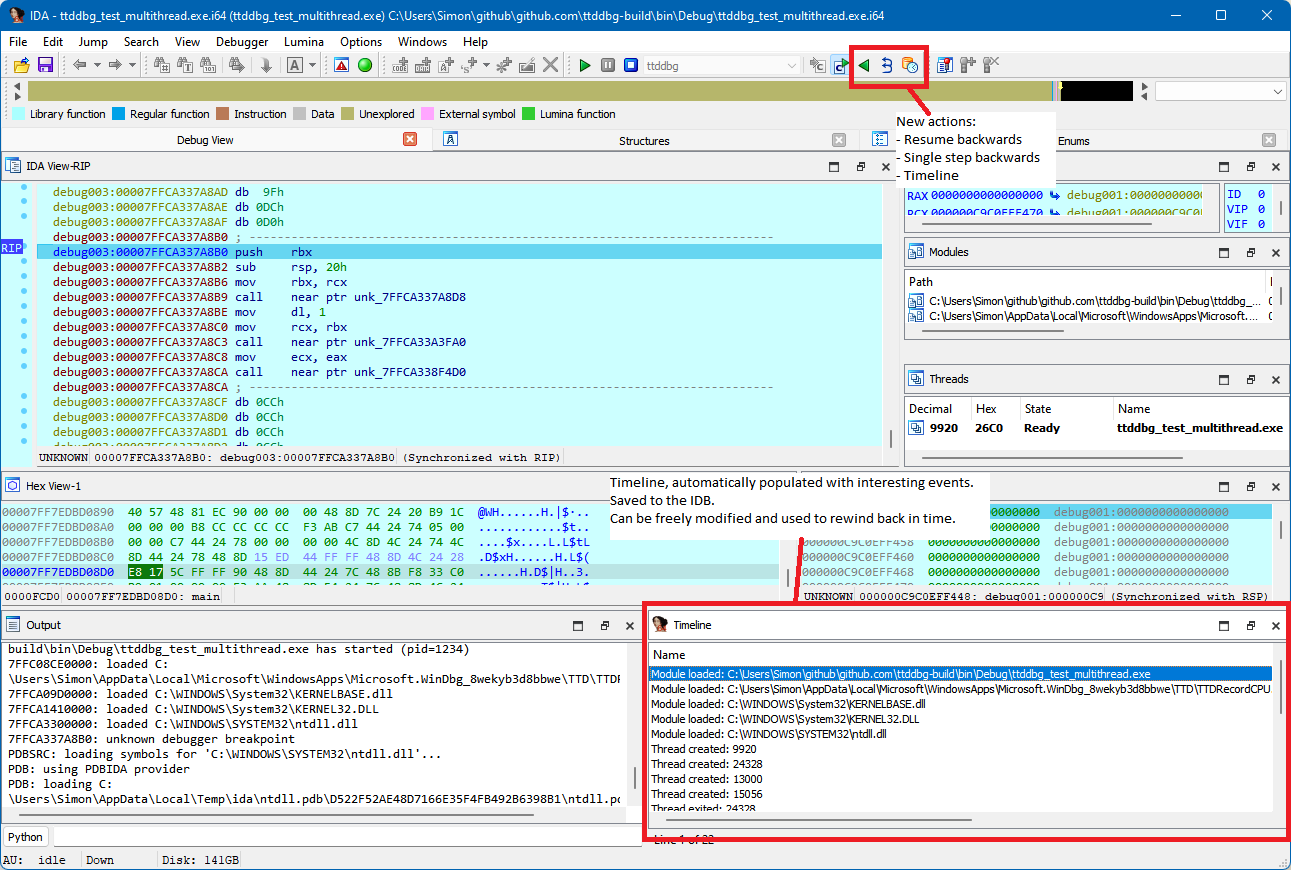 airbus-cert/ttddbg
Time Travel Debugging IDA plugin
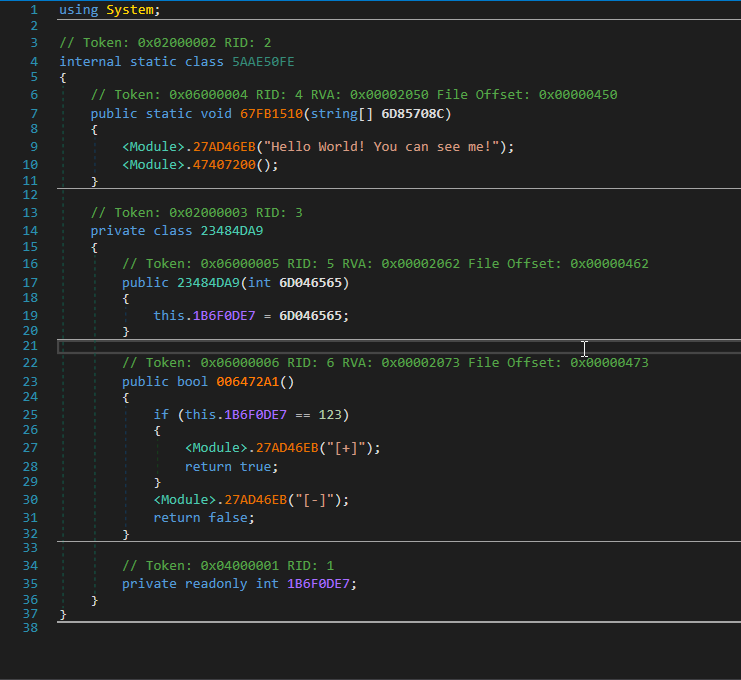 void-stack/vmunprotect.dumper
VMUnprotect.Dumper can dynamically untamper VMProtected Assembly.
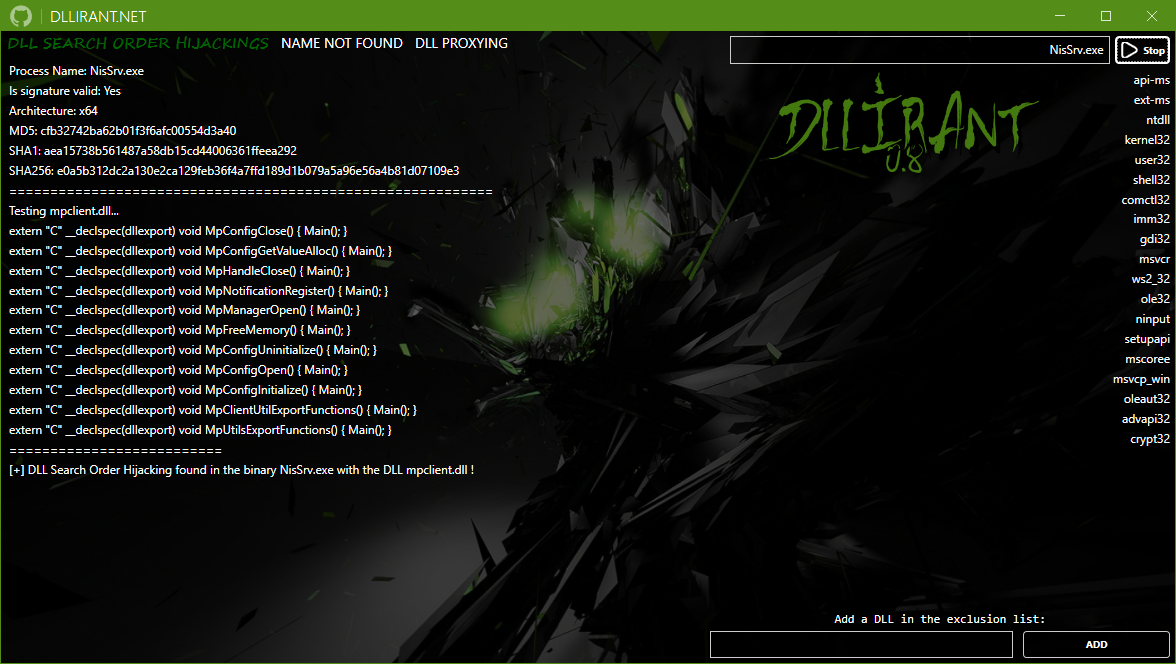 redteamsocietegenerale/dllirant
DLLirant is a tool to automatize the DLL Hijacking researches on a specified binary.
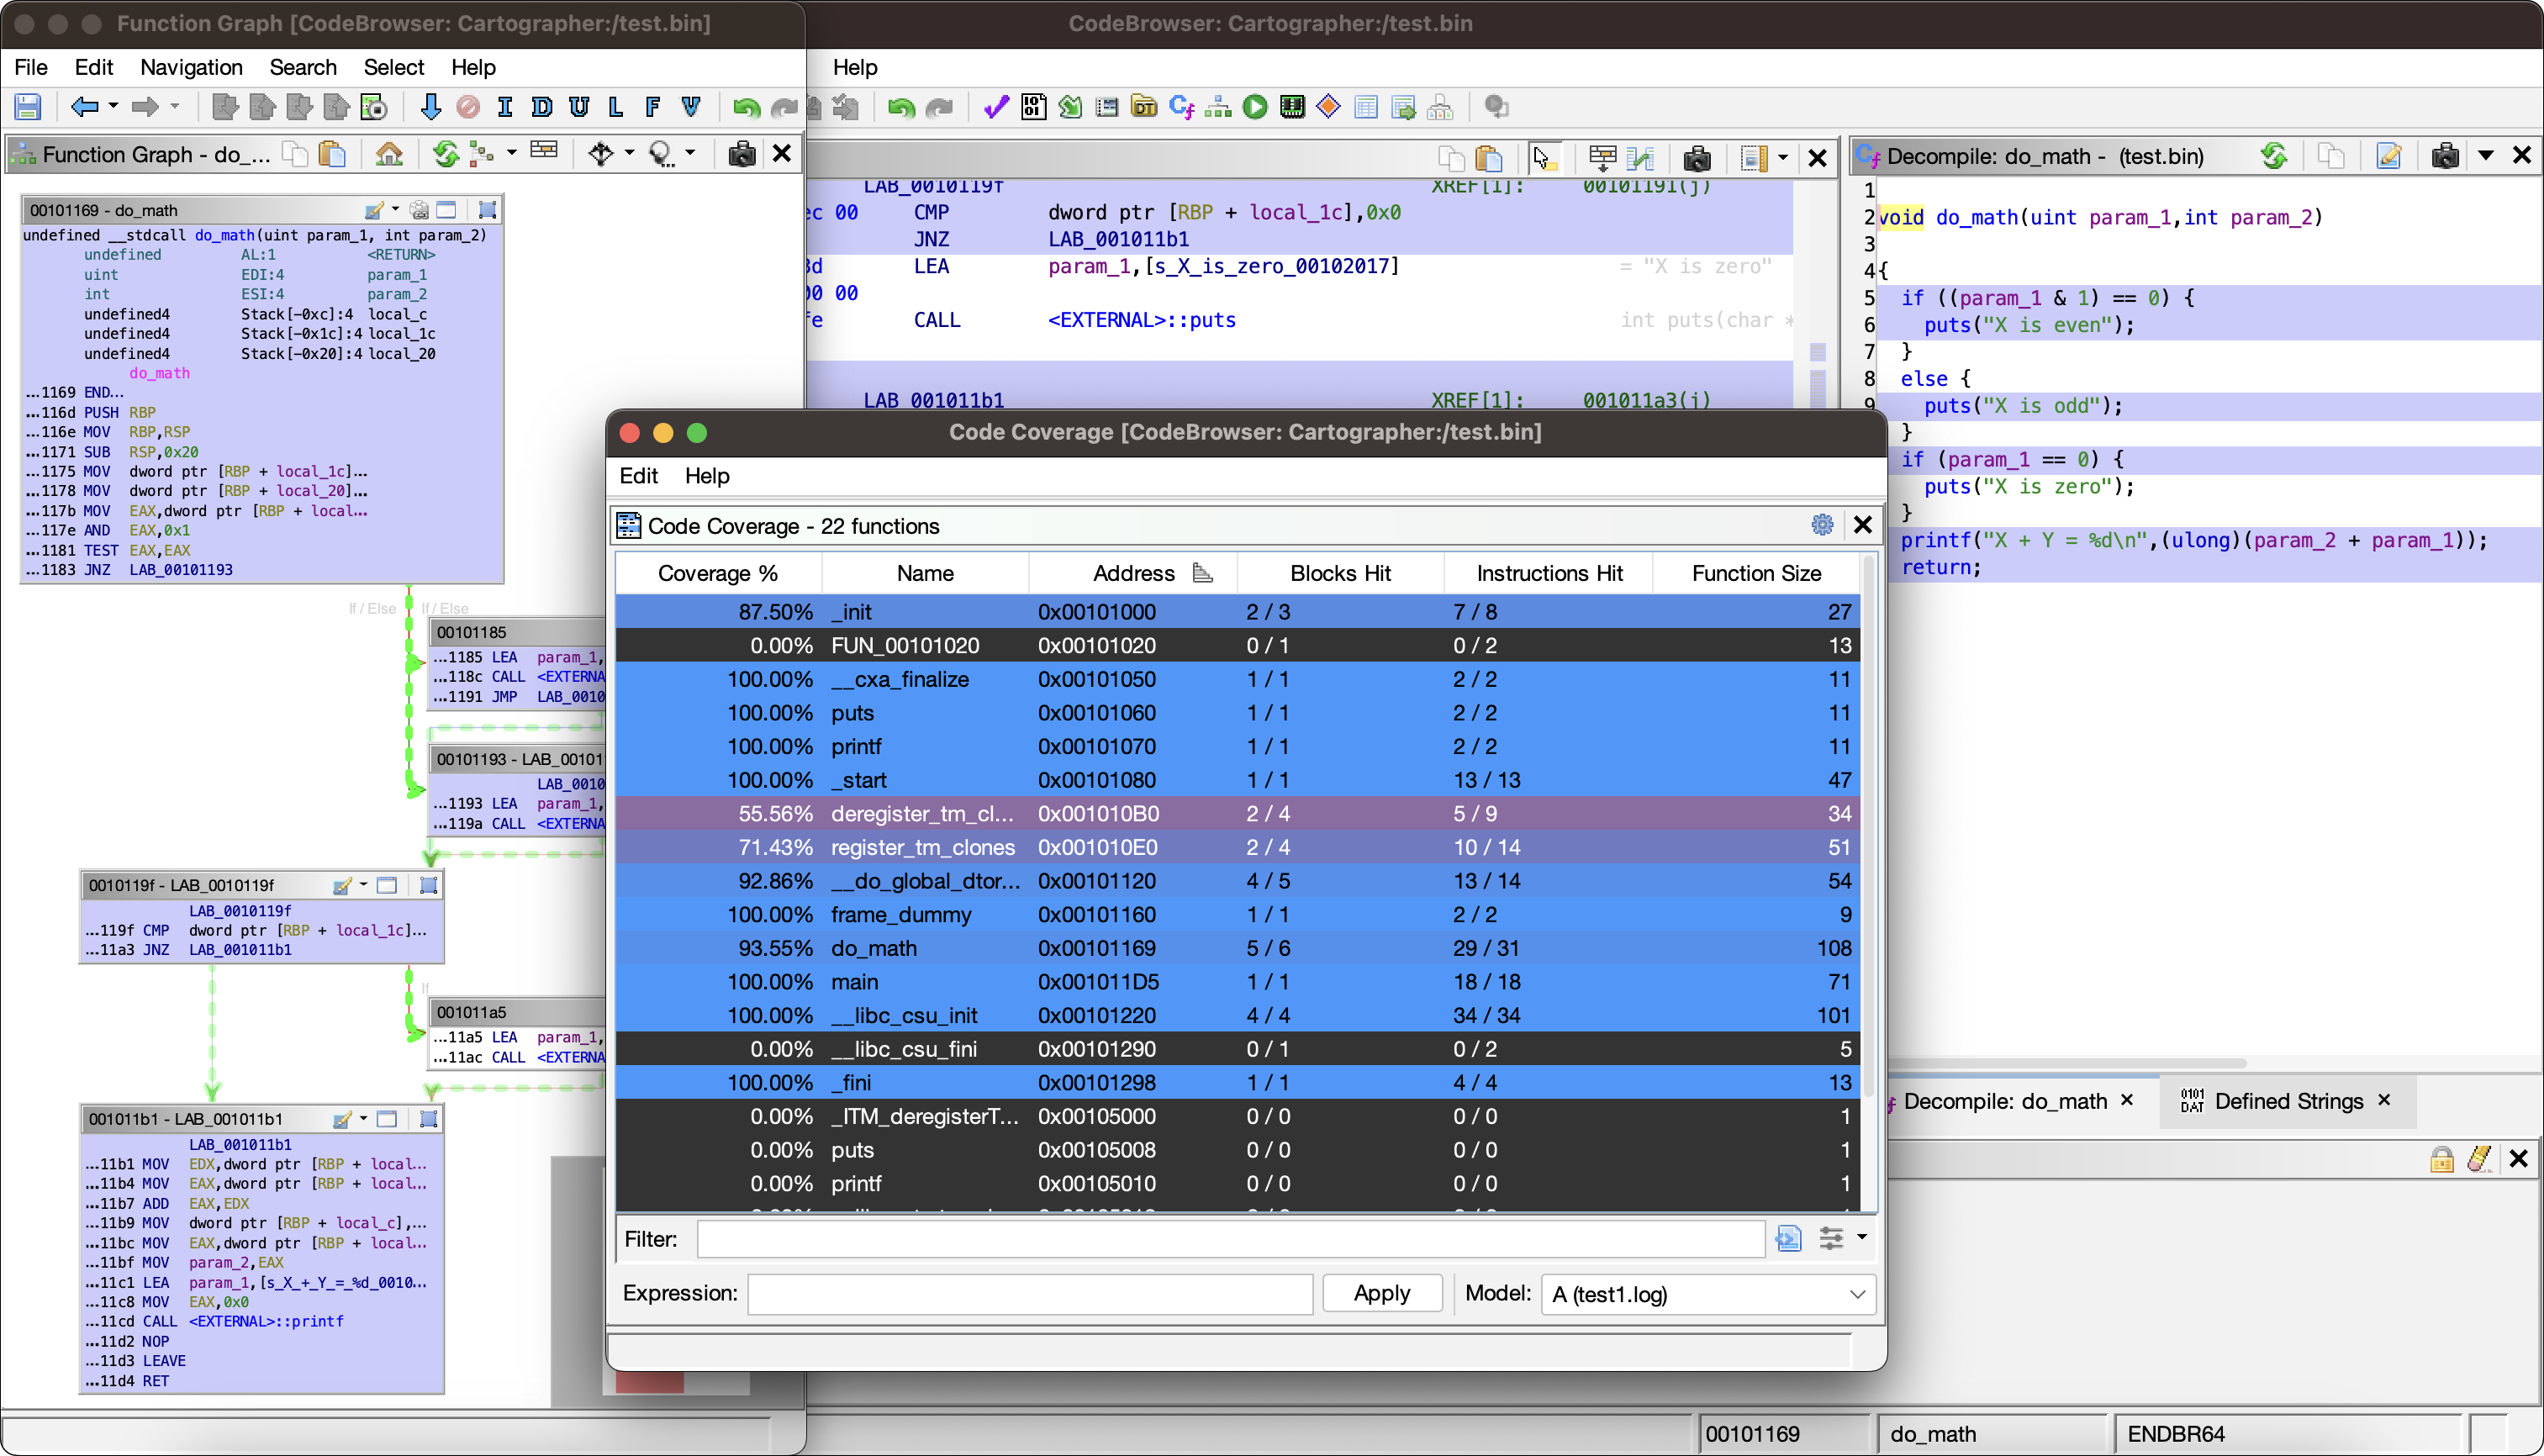 nccgroup/cartographer
Code Coverage Exploration Plugin for Ghidra
 hugsy/windbg_js_scripts
Toy scripts for playing with WinDbg JS API
 symbioticsec/hermes-decomp
A powerful decompiler that lets you reverse-engineer React Native mobile apps by converting their compiled Hermes bytecode (.hbc) files back into…
 lauriewired/artful
The ARTful library for dynamically modifying the Android Runtime
 rbmm/ntdetours
Detours implementation (x64/x86) which used only ntdll import
 r00tkitsmm/pishi
Pishi is a code coverage tool like kcov for macOS.
 binsec/xyntia
Xyntia, the black-box deobfuscator
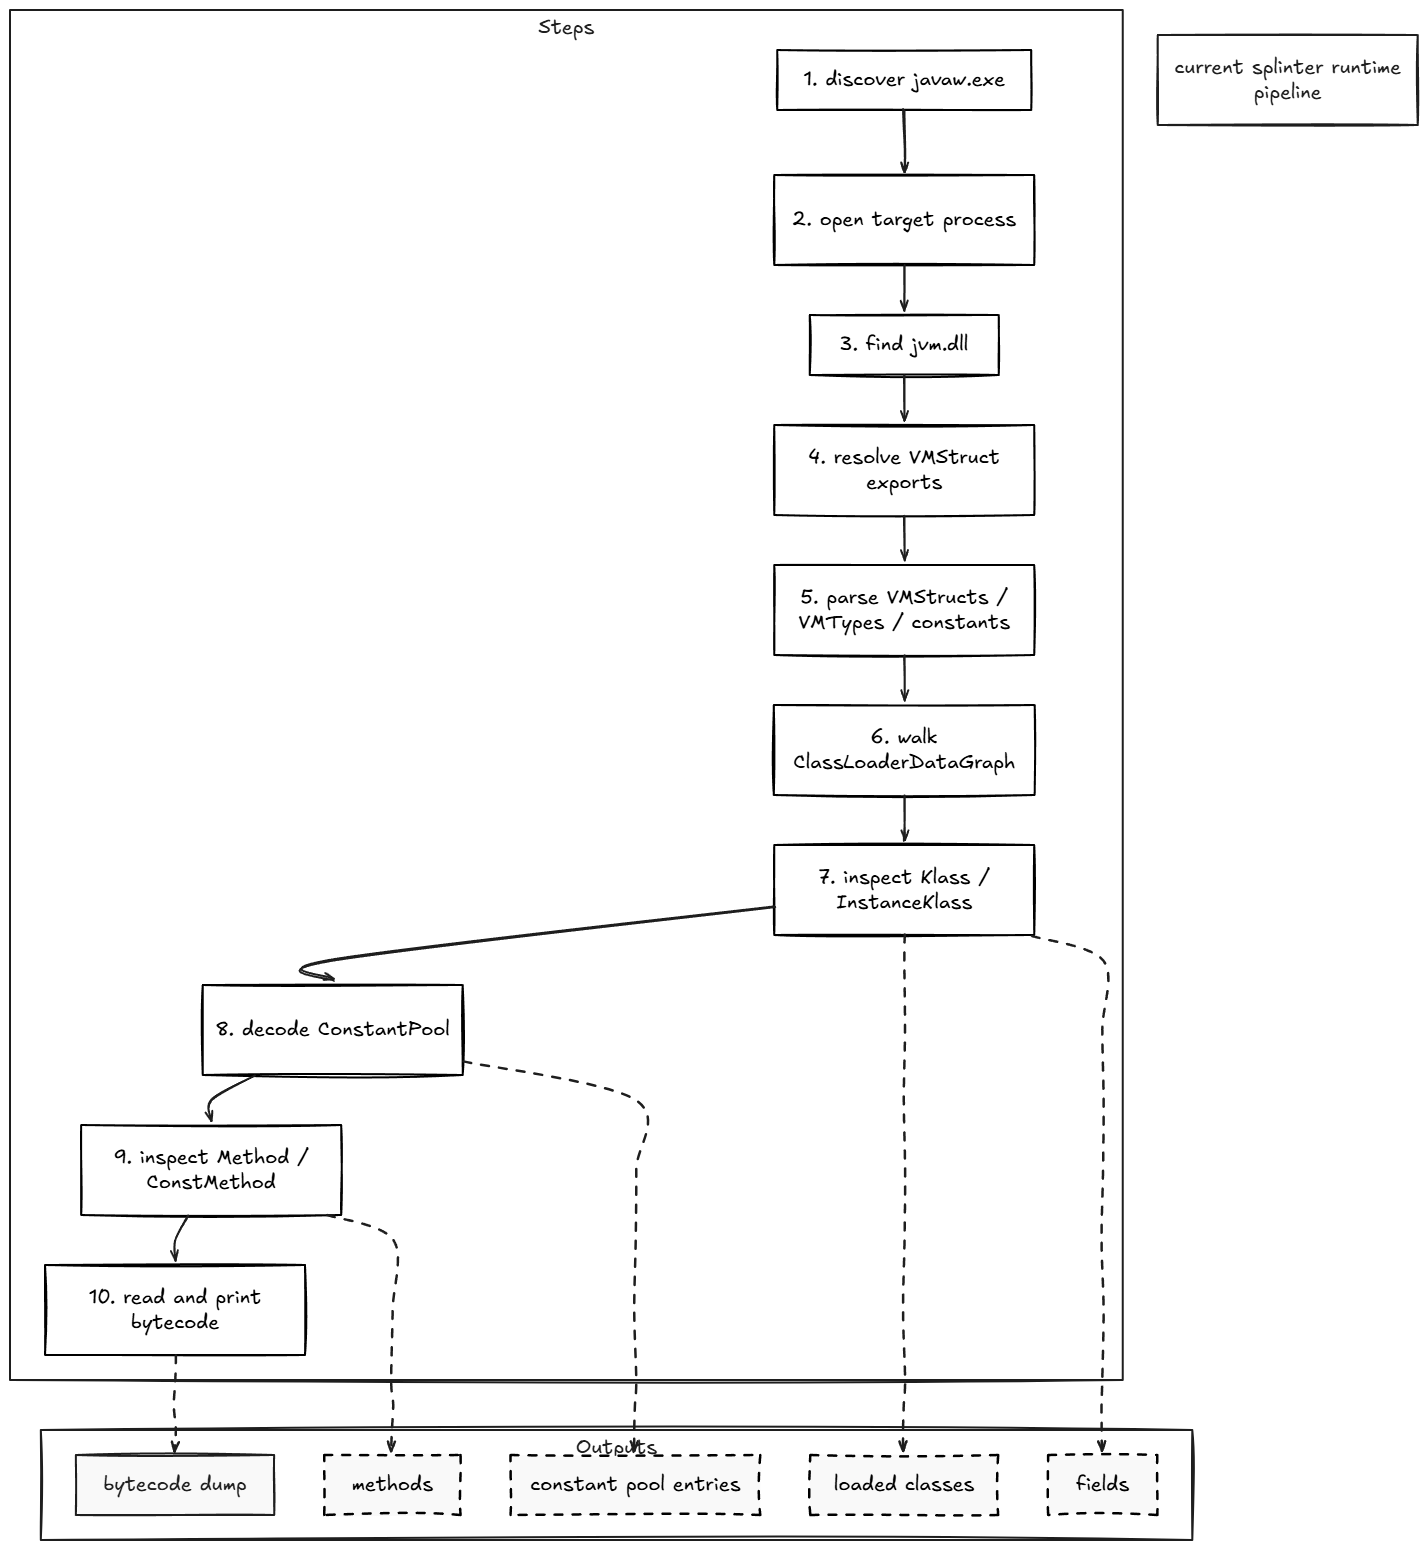 awrped/splinter
Runtime JVM analysis toolkit for inspecting classes, methods, fields, constant pool, and bytecode
 tca-iscas/cooper-ndss-2022
A tool for effective testing the binding layer of scripting languages