

HookCase
 steven-michaud/hookcase
Tool for reverse engineering macOS/OS X
binary-analysisdebuggersdynamic-code-analysis+1
steven-michaud/hookcaseTool for reverse engineering macOS/OS X
 angorafuzzer/angora
Coverage-guided fuzzer that uses taint tracking and scalar optimization to solve path constraints without symbolic execution, improving branch…
 byt3bl33d3r/offensivedlr
Toolbox containing research notes & PoC code for weaponizing .NET's DLR
 trailofbits/polytracker
An LLVM-based instrumentation tool for universal taint tracking, dataflow analysis, and tracing.
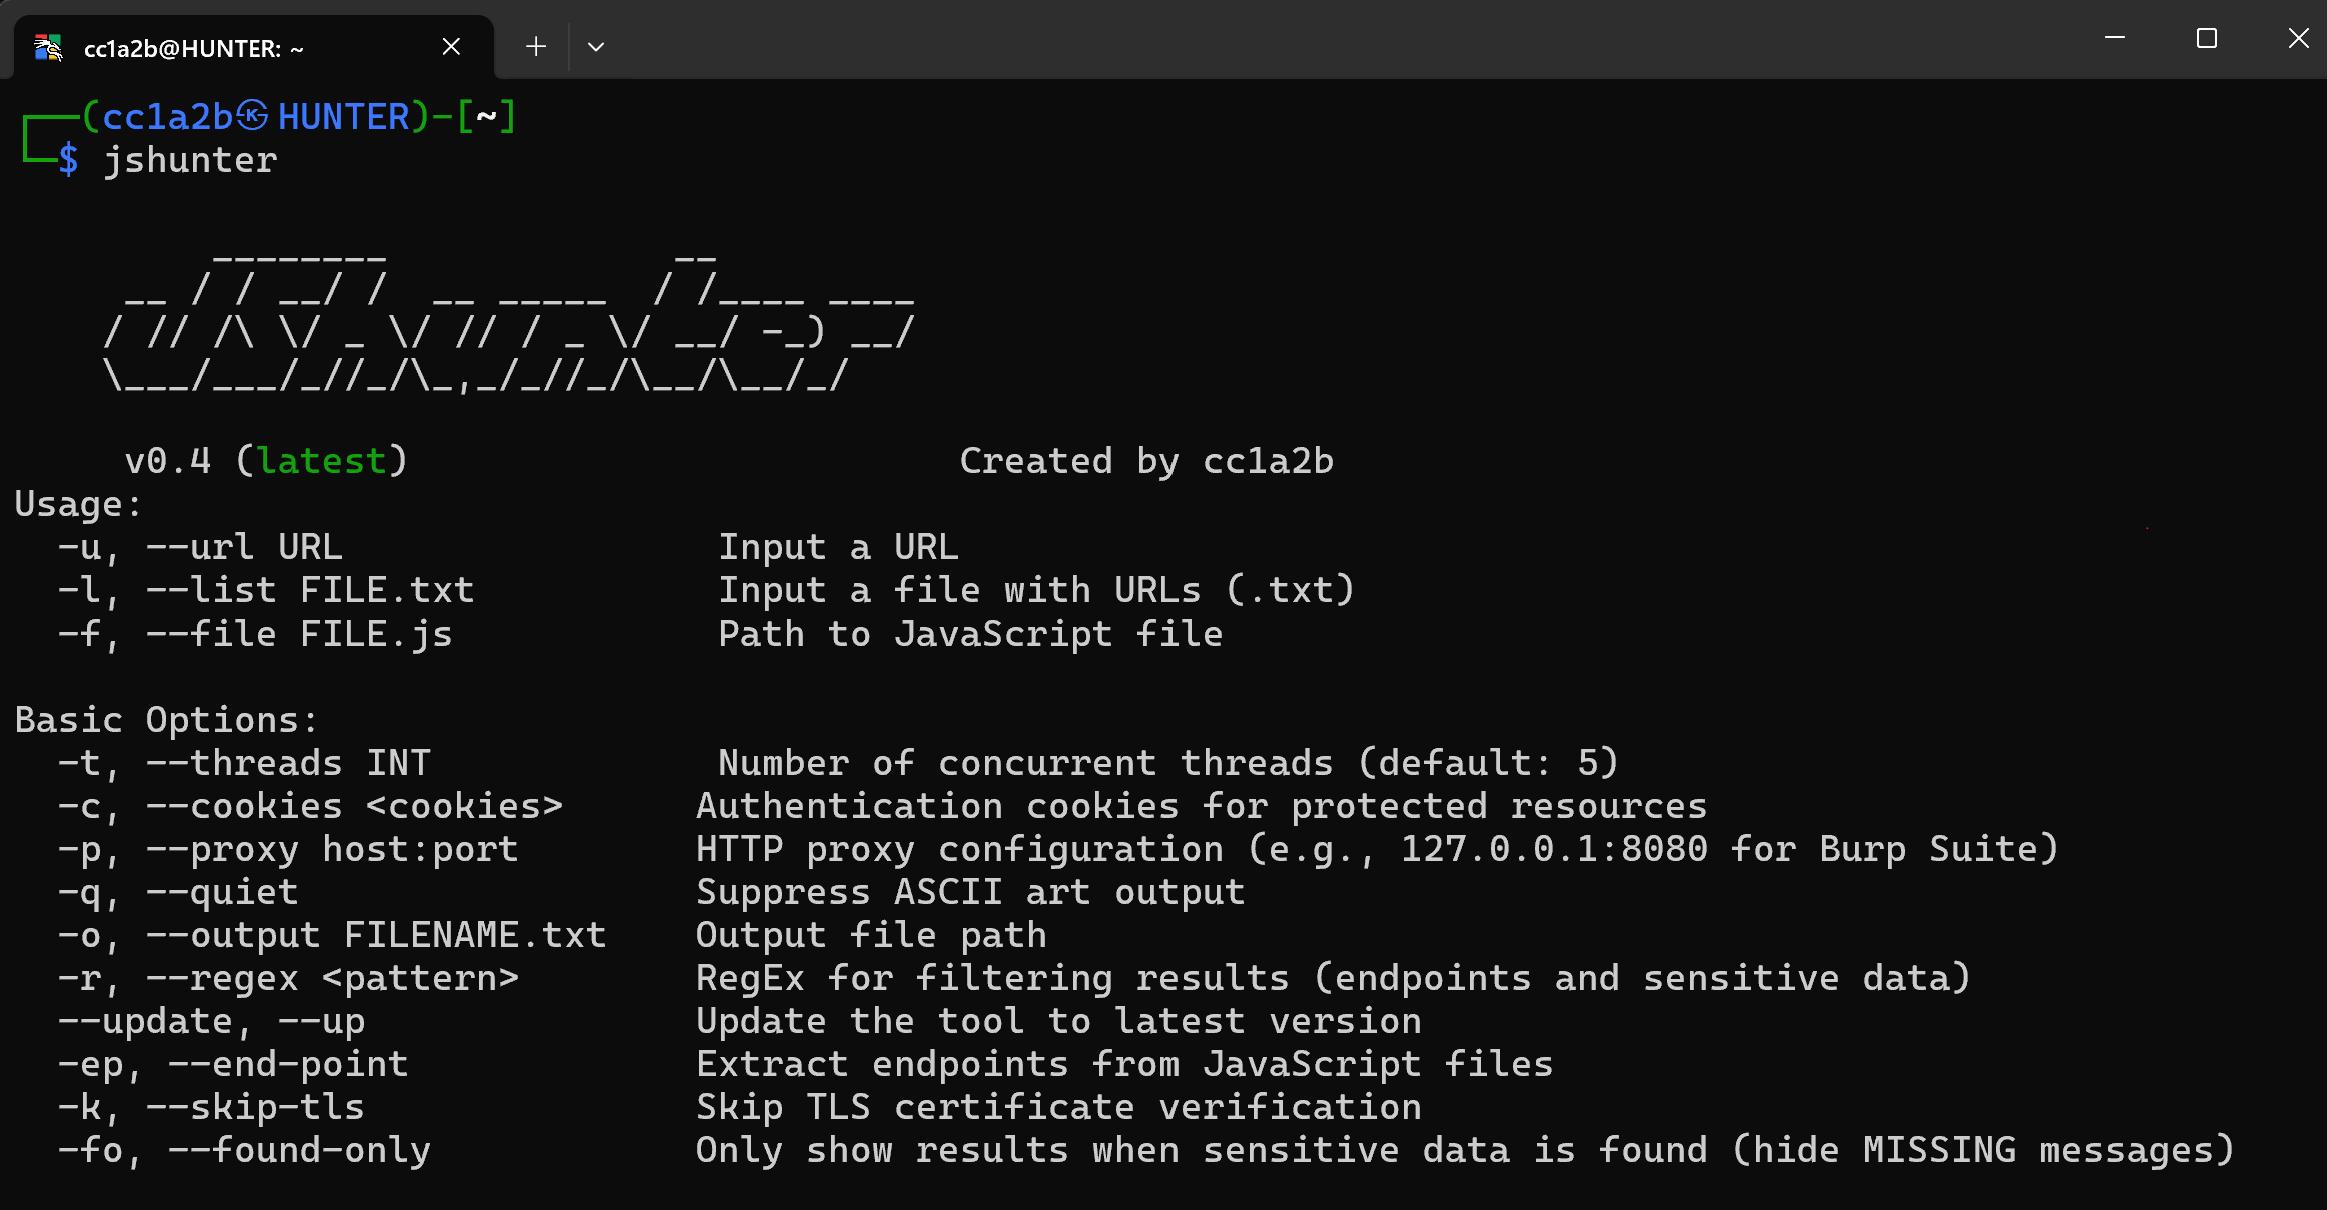 cc1a2b/jshunter
jshunter is a command-line tool designed for analyzing JavaScript files and extracting endpoints. This tool specializes in identifying sensitive…
 smackers/smack
Modular software verification toolchain that translates LLVM IR into Boogie intermediate verification language for bounded and experimental unbounded…
 google/buzzer
eBPF fuzzer toolchain for generating random eBPF programs and validating kernel verifier/runtime behavior. Supports coverage-guided fuzzing and…
 dolevf/graphql-cop
Lightweight Python utility for automated security auditing of GraphQL APIs. Detects misconfigurations, information leaks, and denial-of-service…
 rogerorr/nttrace
An strace-like program for the Windows 'native' API
 lifting-bits/sleigh
CMake build of Ghidra's SLEIGH processor specification library, providing standalone disassembly and p-code lifting engines for reverse engineering…
 mynameismeerkat/pyretic
pyREtic is an extensible framework for in-memory Python 2.x bytecode reverse engineering
 hackmanit/tinja
TInjA is a CLI tool for testing web pages for template injection vulnerabilities and supports 44 of the most relevant template engines for eight…
 atomdrift-project/scan
0-day malware detection for binaries, source & scripts (that doesn't suck)
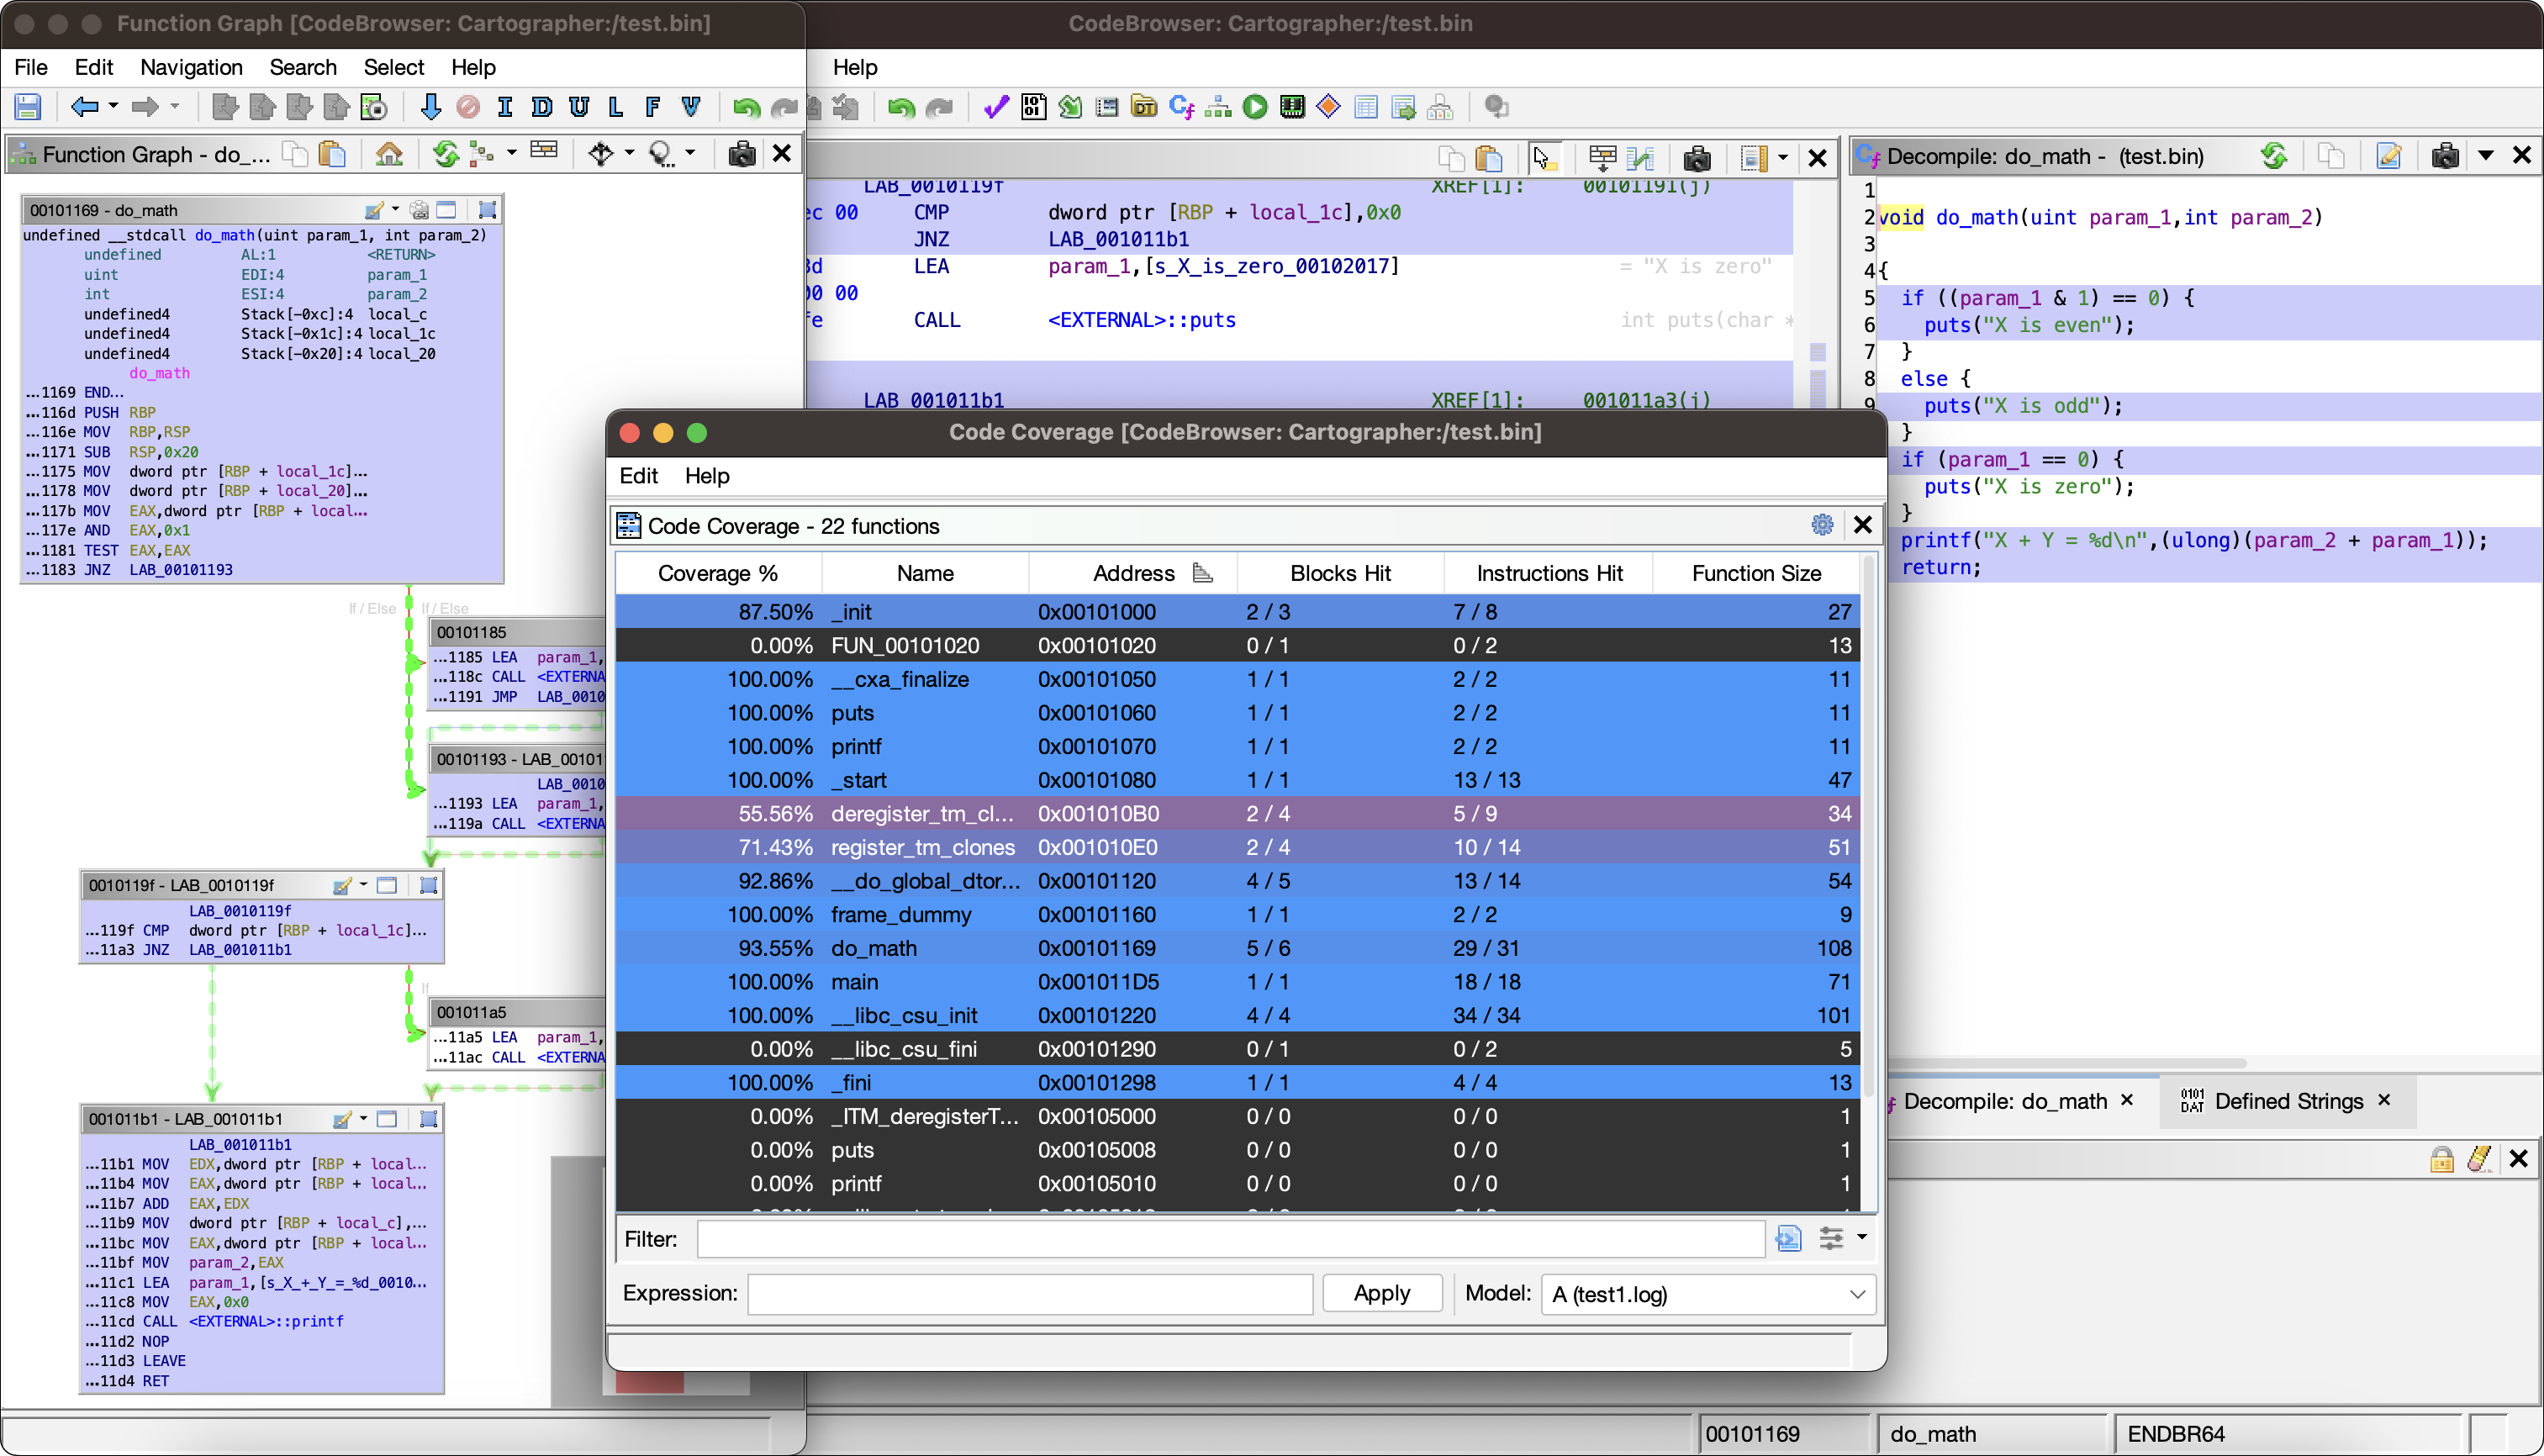 nccgroup/cartographer
Code Coverage Exploration Plugin for Ghidra
 pietroborrello/customprocessingunit
The first analysis framework for CPU microcode
 hugsy/windbg_js_scripts
Toy scripts for playing with WinDbg JS API
 cobbr/elite
Elite is the client-side component of the Covenant project. Covenant is a .NET command and control framework that aims to highlight the attack…
 advdebug/brovan
User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…