
Frida-Labs
 dere-ad2001/frida-labs
The repo contains a series of challenges for learning Frida for Android Exploitation.
android-securitybinary-analysisctf+6
1.3k8 months ago
dere-ad2001/frida-labsThe repo contains a series of challenges for learning Frida for Android Exploitation.
 chichou/vscode-frida
Unofficial frida extension for VSCode
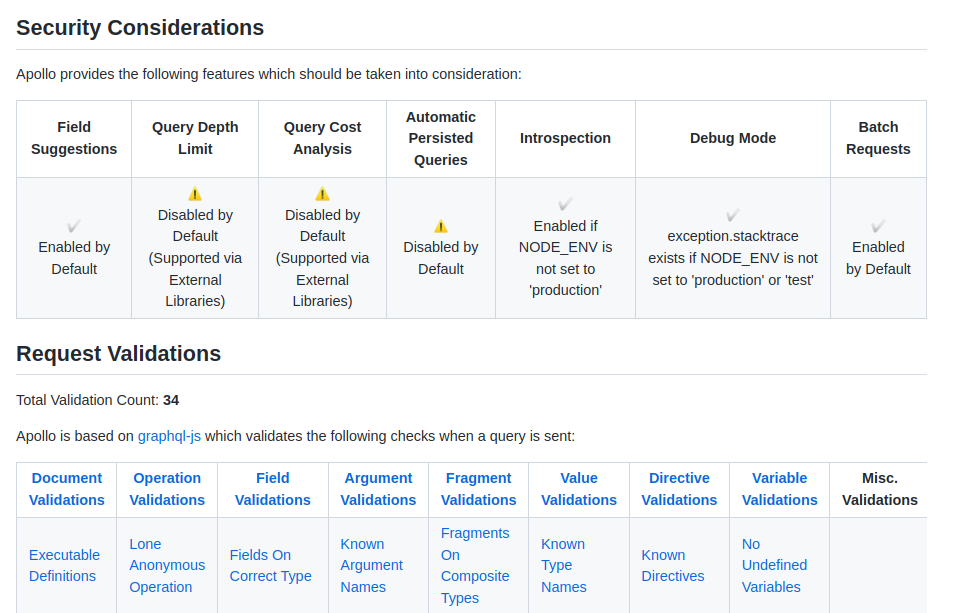 dolevf/graphw00f
GraphQL server engine fingerprinting tool that sends benign and malformed queries to identify backend technology and assess security defenses via the…
 ejfkdev/ddc
Android DEX → Java decompiler in Rust — quality-first: javac-verified output, exact semantic-preserving simplification (cure), full apps in seconds,…
 swdunlop/andbug
Scriptable debugger for Android Dalvik VM using JDWP/DDM interfaces to hook methods, inspect process state, and modify runtime behavior without…
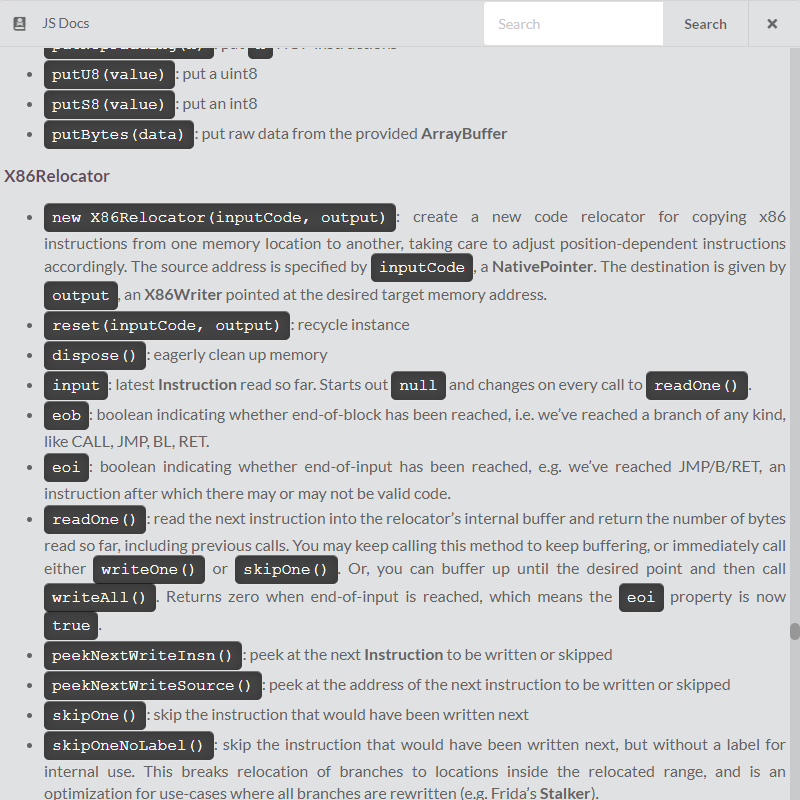 fuzzysecurity/fermion
Fermion, an electron wrapper for Frida & Monaco.
 dolevf/graphql-cop
Lightweight Python utility for automated security auditing of GraphQL APIs. Detects misconfigurations, information leaks, and denial-of-service…
 rogerorr/nttrace
An strace-like program for the Windows 'native' API
 yuatemycat/superghidra
Python toolkit accelerating Ghidra with a cached daemon, ARM64 P-code lifting, Z3 equivalence proofs, GPU-accelerated scanning, binary diffing, and…
 ch0pin/rdx
A native APK and DEX decompiler written in Rust
 lauriewired/artful
The ARTful library for dynamically modifying the Android Runtime
 symbioticsec/hermes-decomp
A powerful decompiler that lets you reverse-engineer React Native mobile apps by converting their compiled Hermes bytecode (.hbc) files back into…
 giveen/decomp.anything
decomp.wtf fork: Windows PE matching, MinGW/clang-cl toolchains, and an optional REA MCP bridge
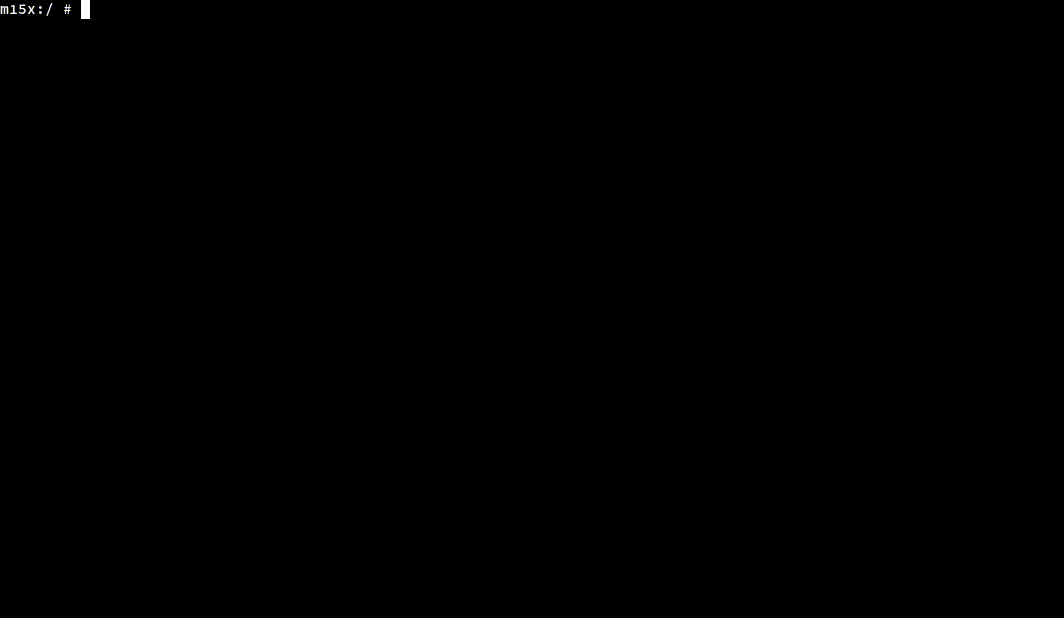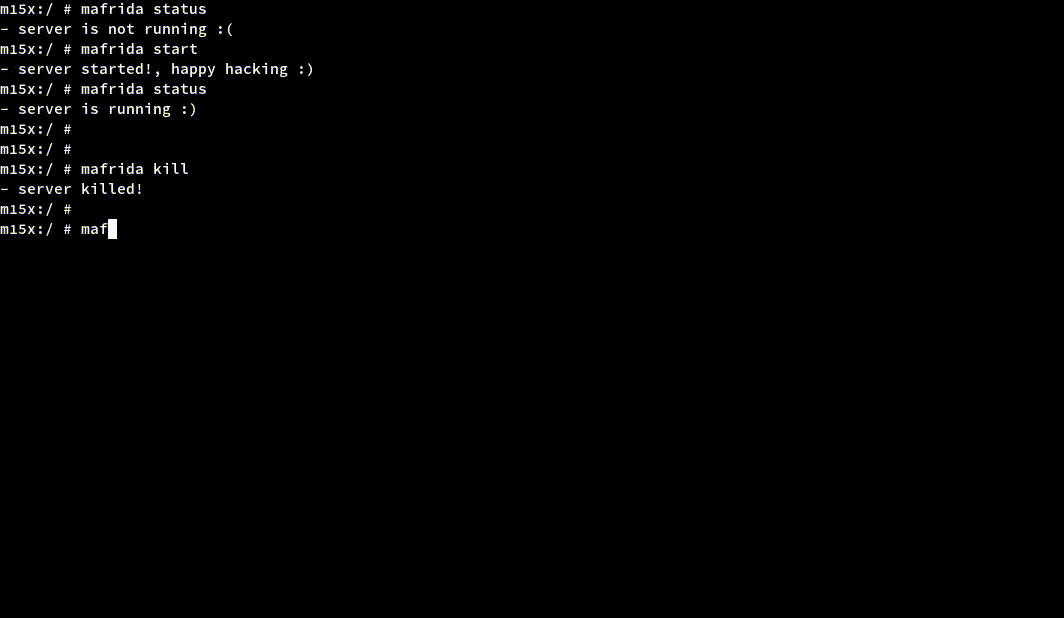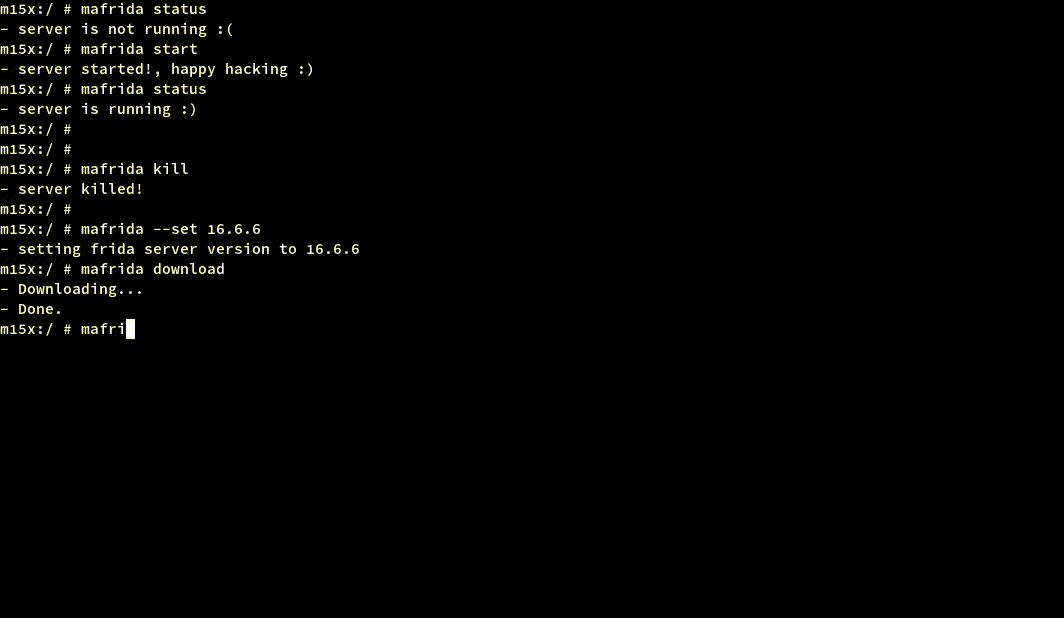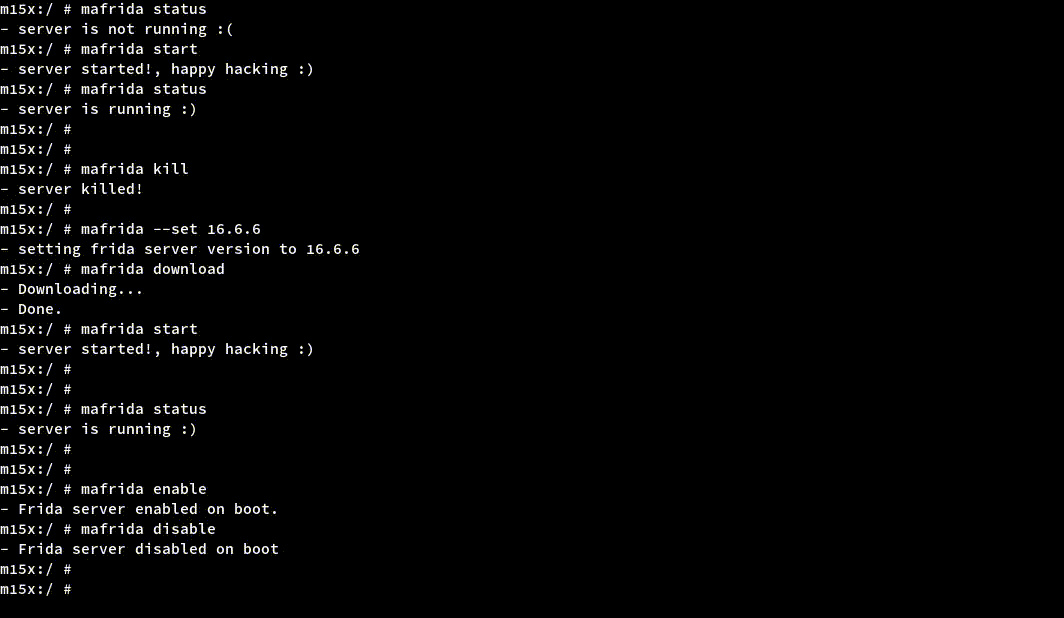 theshinigami/mafrida
A Magisk module that simplifies running the Frida server on Android, with easy management commands to download specific versions, enable or disable…
 kaisonox/apiscope
An API hooking framework for intercepting and monitoring Windows applications
 fkie-cad/sandroid_dexray-intercept
A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…
 xv4l3x/hermit
Inspects, decompiles and structurally patches Hermes bytecode (HBC) from React Native apps, with a GDB-style REPL, CFG, decompiler and re-serializing…