

cargo-fuzz
 rust-fuzz/cargo-fuzz
Cargo subcommand for coverage-guided Rust fuzzing with libFuzzer: create and run fuzz targets, minimize failures and corpora, and report coverage.
vulnerability-analysisdynamic-code-analysisfuzzing
rust-fuzz/cargo-fuzzCargo subcommand for coverage-guided Rust fuzzing with libFuzzer: create and run fuzz targets, minimize failures and corpora, and report coverage.
 narfindustries/http-garden
Differential testing framework for HTTP implementations
 google/oss-fuzz-gen
LLM powered fuzzing via OSS-Fuzz.
 gaasedelen/patching
An Interactive Binary Patching Plugin for IDA Pro
 splx-ai/agentic-radar
A security scanner for your LLM agentic workflows
 steven-michaud/hookcase
Tool for reverse engineering macOS/OS X
 chichou/vscode-frida
Unofficial frida extension for VSCode
 angorafuzzer/angora
Coverage-guided fuzzer that uses taint tracking and scalar optimization to solve path constraints without symbolic execution, improving branch…
 cc1a2b/jshunter
jshunter is a command-line tool designed for analyzing JavaScript files and extracting endpoints. This tool specializes in identifying sensitive…
 byt3bl33d3r/offensivedlr
Toolbox containing research notes & PoC code for weaponizing .NET's DLR
 dolevf/graphw00f
GraphQL server engine fingerprinting tool that sends benign and malformed queries to identify backend technology and assess security defenses via the…
 smackers/smack
Modular software verification toolchain that translates LLVM IR into Boogie intermediate verification language for bounded and experimental unbounded…
 trailofbits/polytracker
An LLVM-based instrumentation tool for universal taint tracking, dataflow analysis, and tracing.
 ghostvectoracademy/dllhijackhunter
Automated DLL Hijacking Discovery, Validation, and Confirmation. Turning local misconfigurations into weaponized, confirmed attack paths.
 swdunlop/andbug
Scriptable debugger for Android Dalvik VM using JDWP/DDM interfaces to hook methods, inspect process state, and modify runtime behavior without…
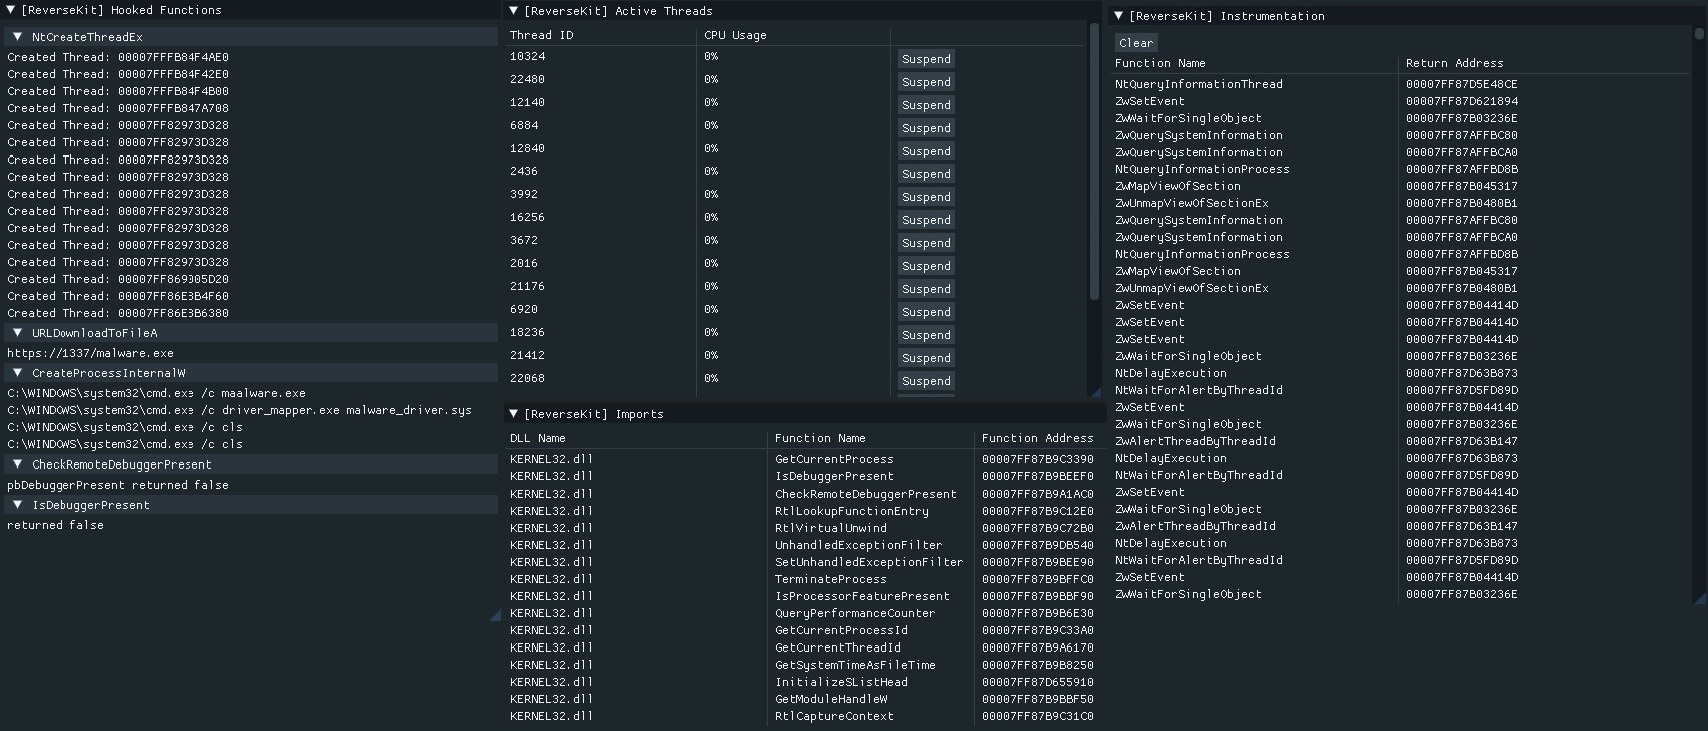 zer0condition/reversekit
x64 Dynamic Reverse Engineering Toolkit
 ejfkdev/ddc
Android DEX → Java decompiler in Rust, built for speed — full apps in seconds, queries in milliseconds. Progressive analysis, javac-verified output,…
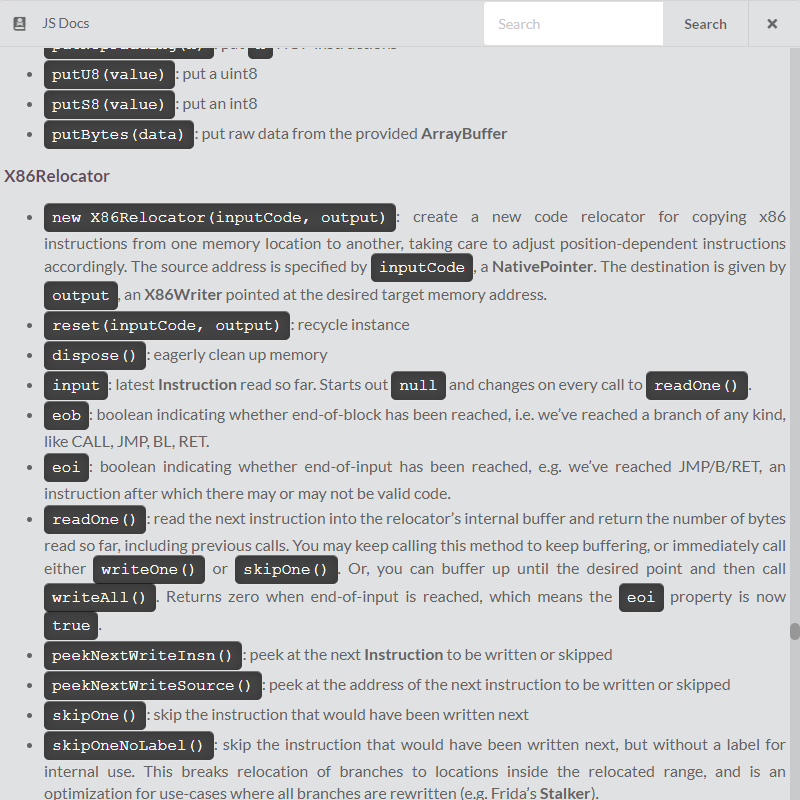 fuzzysecurity/fermion
Fermion, an electron wrapper for Frida & Monaco.