

Brovan
 advdebug/brovan
User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…
binary-analysisdebuggersdynamic-analysis-sandboxing+3
164
advdebug/brovanUser-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…
 ch0pin/rdx
A native APK and DEX decompiler written in Rust
 hahwul/dalfox
Fast XSS scanner with parameter analysis, WAF fingerprinting, and DOM/AST verification. Supports reflected, stored, and DOM-based XSS detection via…
 veridiff/veridiff
Dynamic branch-divergence finder for native code -- traces two Frida executions and finds the exact instruction where they diverge.

 ejfkdev/ddc
DEX → Java decompiler in Rust — fast, progressive analysis, bilingual CLI

 robertdfrench/ifuncd-up
GNU IFUNC is the real culprit behind CVE-2024-3094
 wapiti-scanner/wapiti
Web vulnerability scanner written in Python3
 cc1a2b/jshunter
jshunter is a command-line tool designed for analyzing JavaScript files and extracting endpoints. This tool specializes in identifying sensitive…
 1rhino2/fnprint
match functions in binaries by what they do, not what their bytes look like. behavioral function fingerprinting via microexecution.
 anonmoty/xxstrike
XSStrike based XSS scanner with custom features. Detects XSS vulnerabilities in web applications.
 epi052/feroxbuster
A fast, simple, recursive content discovery tool written in Rust.
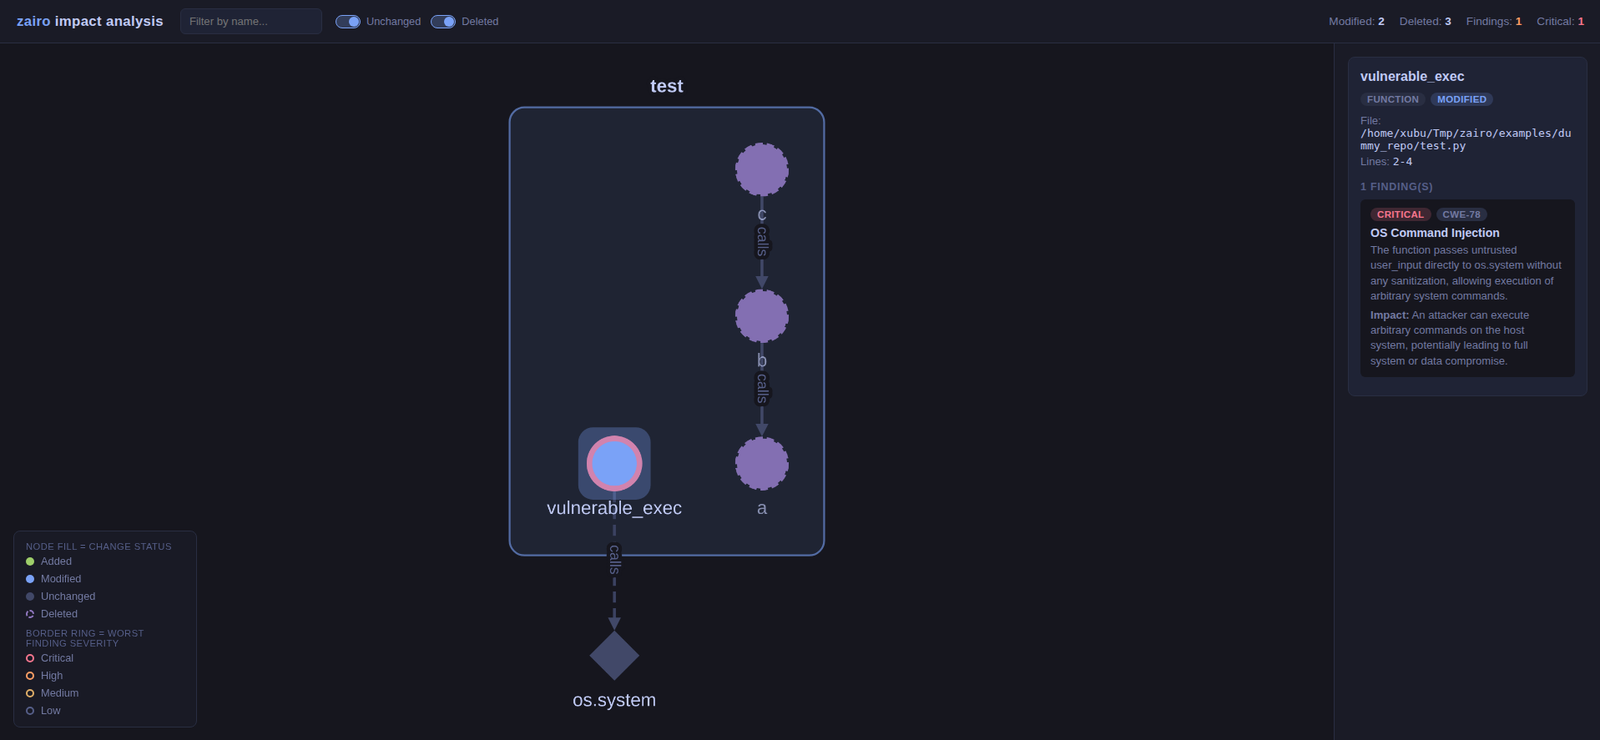 iamavu/zairo
Scans code diffs with context to build an impact graph and uses LLMs to find vulnerabilities, supporting multi-repo scans and CI gating with SARIF…
 open-flaw/cve-2026-56848
Exploit PoC for CVE-2026-56848, a Node.js HTTP/2 heap-use-after-free that allows remote unauthenticated DoS. Includes raw-socket trigger, ASan build…
 r00tkitsmm/pishi
Pishi is a code coverage tool like kcov for macOS.
 hunt-benito/one-multiply-too-many-cve-2026-70638-llama-cpp-android-jni-integer-overflow
Reproduces the CVE-2026-70638 integer overflow in llama.cpp Android JNI with a safe arithmetic demo, malicious GGUF generator, and Frida hook for…
 smackers/smack
Modular software verification toolchain that translates LLVM IR into Boogie intermediate verification language for bounded and experimental unbounded…