
fil-c
 pizlonator/fil-c
Fil-C: completely compatible memory safety for C and C++
defensive-toolsdynamic-code-analysisvulnerability-analysis
pizlonator/fil-cFil-C: completely compatible memory safety for C and C++
 advdebug/brovan
User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
 rr-debugger/rr
Record and replay framework for deterministic debugging of multi-threaded applications, enabling reverse execution, hardware watchpoints, and…
 anonmoty/xxstrike
XSStrike based XSS scanner with custom features. Detects XSS vulnerabilities in web applications.
 symbioticsec/hermes-decomp
A powerful decompiler that lets you reverse-engineer React Native mobile apps by converting their compiled Hermes bytecode (.hbc) files back into…
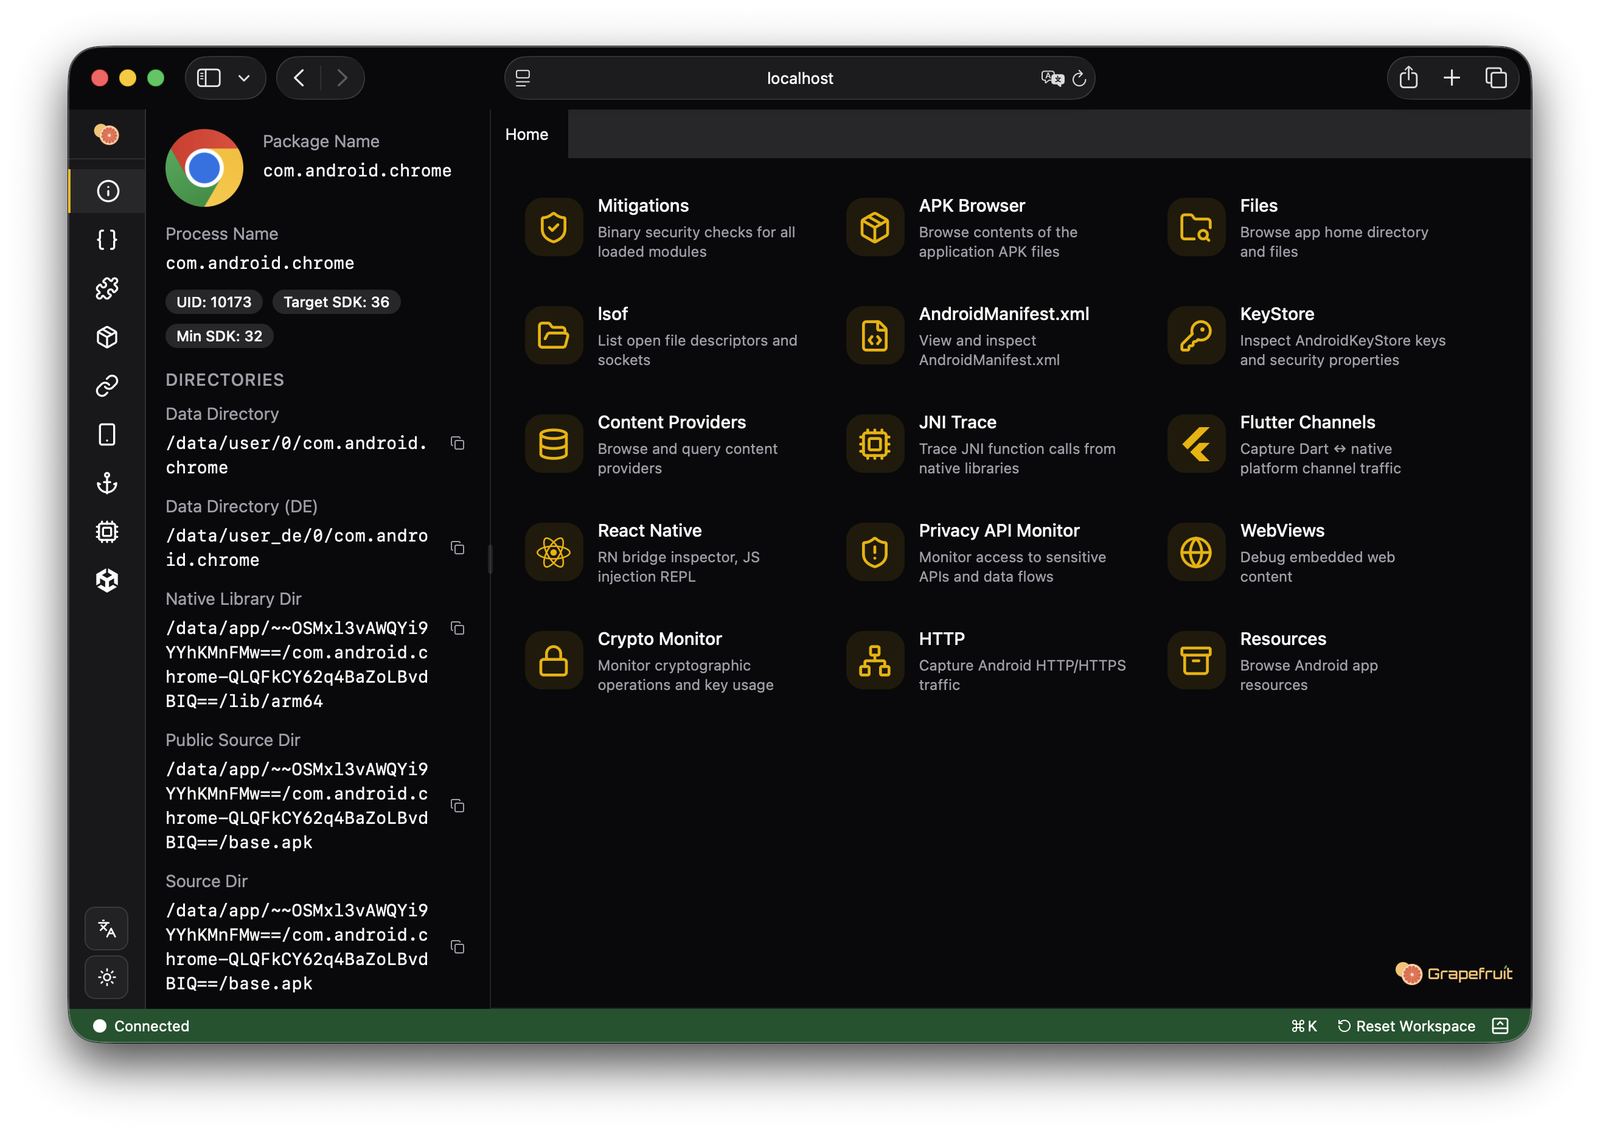 chichou/grapefruit
Open-source mobile security testing suite for iOS and Android. Previously Passionfruit
 0xdea/frida-scripts
A collection of my Frida instrumentation scripts to reverse engineer mobile apps and more.
 whatswrongandwhy/ptrace
Linux ptrace-based process tracing and debugging utility for inspecting system calls, memory, and program execution flow.
 google/honggfuzz
Security oriented software fuzzer. Supports evolutionary, feedback-driven fuzzing based on code coverage (SW and HW based)
 narfindustries/http-garden
Differential testing framework for HTTP implementations
 robertdfrench/ifuncd-up
GNU IFUNC is the real culprit behind CVE-2024-3094
 urbanadventurer/whatweb
Next generation web scanner
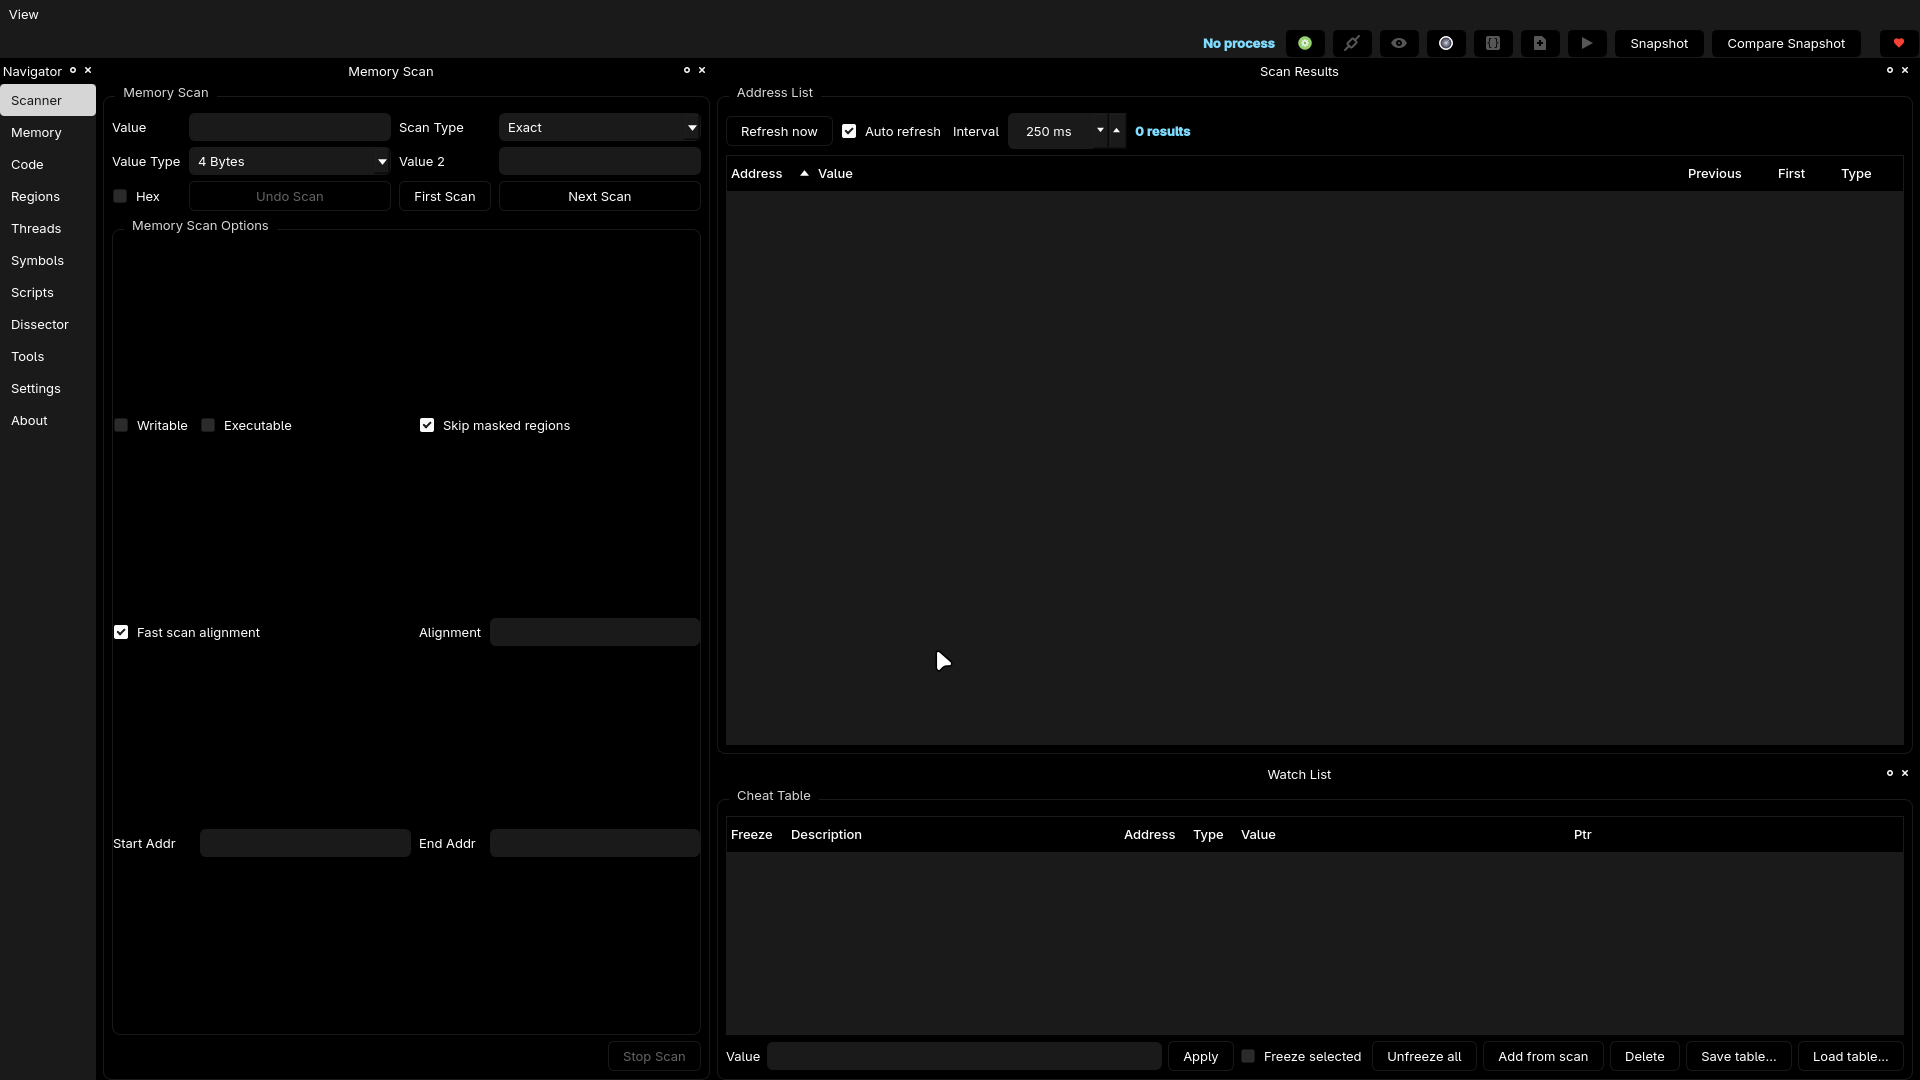 kashithecomfy/comfyengine
ComfyEngine is a memory exploration toolkit built for people who need to monitor, patch, and script a running process.
 abubakar-shahid/cve-2024-36886
Academic research on N-Day Linux kernel vulnerabilities, analyzing CVE-2024-36886 in the TIPC networking subsystem, lifecycle, impact, and mitigation…
 google/kernel-sanitizers
Linux Kernel Sanitizers, fast bug-detectors for the Linux kernel
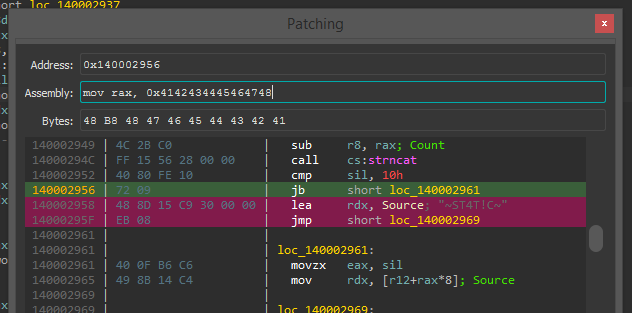 gaasedelen/patching
An Interactive Binary Patching Plugin for IDA Pro
 angorafuzzer/angora
Coverage-guided fuzzer that uses taint tracking and scalar optimization to solve path constraints without symbolic execution, improving branch…