reverse-engineering-browser

Local-first macOS research browser built on a custom Brave build that captures network traffic, fingerprints, scripts, and runtime evidence for…

Local-first macOS research browser built on a custom Brave build that captures network traffic, fingerprints, scripts, and runtime evidence for…

A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…

0-day malware detection for binaries, source & scripts (that doesn't suck)

A native APK and DEX decompiler written in Rust

Extract the managed (.NET) assemblies out of a MAUI Android assembly store.

frida-stalker based system call tracer on windows(x64).

Dynamic branch-divergence finder for native code -- traces two Frida executions and finds the exact instruction where they diverge.

Agent-native CLI wrapping IDA Pro IDALib for stateless, JSON-output binary analysis: disassembly, Hex-Rays decompilation, CFG, xrefs, strings, and…

XSStrike based XSS scanner with custom features. Detects XSS vulnerabilities in web applications.

C++ reimplementation of Ghidra's analytical core without JVM dependencies, providing embeddable binary analysis, Pcode/Sleigh foundations, and…

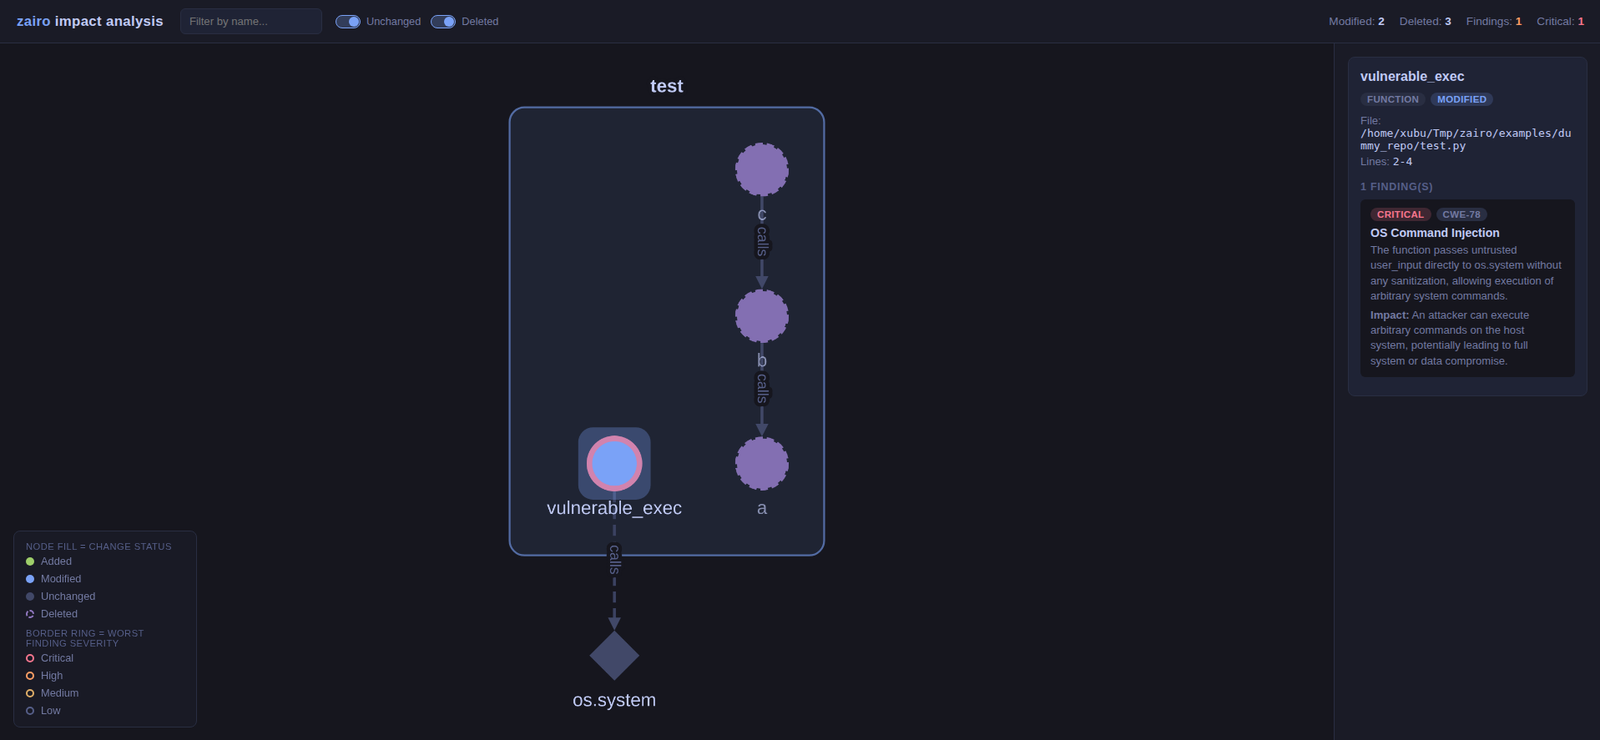
Scans code diffs with context to build an impact graph and uses LLMs to find vulnerabilities, supporting multi-repo scans and CI gating with SARIF…

An LLVM-based instrumentation tool for universal taint tracking, dataflow analysis, and tracing.

Instrumented fuzzer for PLC-based ICS control applications, targeting Codesys runtime on Wago controllers to uncover memory corruption and…

Coverage-guided fuzzer that uses taint tracking and scalar optimization to solve path constraints without symbolic execution, improving branch…

A security scanner for your LLM agentic workflows

A wrapper around grep, to help you grep for things

Security oriented software fuzzer. Supports evolutionary, feedback-driven fuzzing based on code coverage (SW and HW based)

Cargo subcommand for coverage-guided Rust fuzzing with libFuzzer: create and run fuzz targets, minimize failures and corpora, and report coverage.