

decomp.anything
 giveen/decomp.anything
decomp.wtf fork: Windows PE matching, MinGW/clang-cl toolchains, and an optional REA MCP bridge
ai-assisted-reversingai-securityandroid-security+7
6
giveen/decomp.anythingdecomp.wtf fork: Windows PE matching, MinGW/clang-cl toolchains, and an optional REA MCP bridge
 dragonjar/burpia
Extensión de Burp Suite que incorpora detección pasiva de vulnerabilidades mediante inteligencia artificial.
 gmh5225/ida-claude-code-plugins
Plugins integrating Claude Code with IDA Pro to assist reverse engineering and binary analysis workflows through AI-driven disassembly and code…
 gmh5225/enigma-
C++ reimplementation of Ghidra's analytical core without JVM dependencies, providing embeddable binary analysis, Pcode/Sleigh foundations, and…
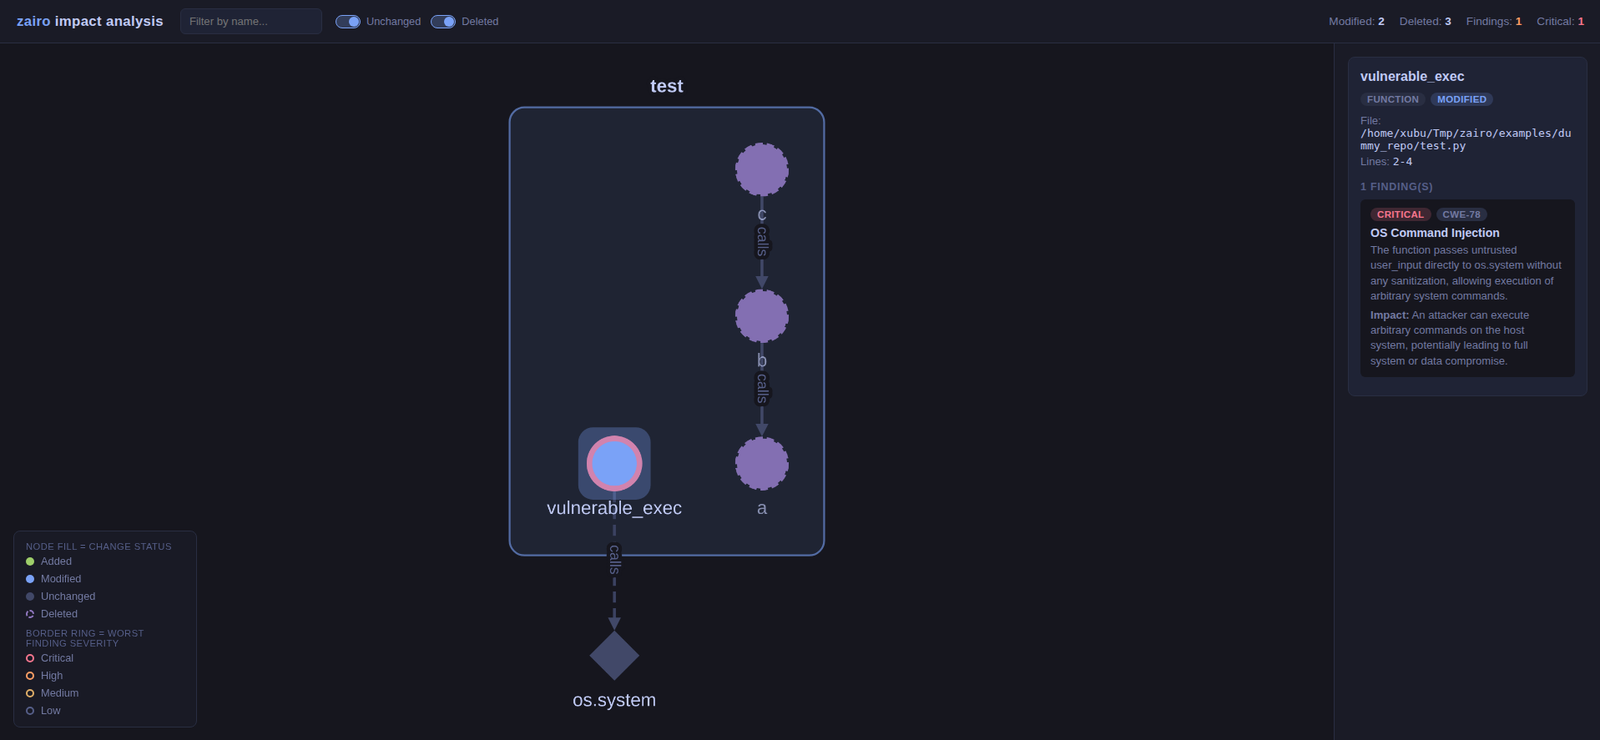 iamavu/zairo
Scans code diffs with context to build an impact graph and uses LLMs to find vulnerabilities, supporting multi-repo scans and CI gating with SARIF…
 splx-ai/agentic-radar
A security scanner for your LLM agentic workflows
 microsoft/detours
Runtime Windows API interception library for hooking, monitoring, and instrumenting function calls. Supports binary rewriting and DLL injection,…
 google/oss-fuzz-gen
LLM powered fuzzing via OSS-Fuzz.
 vladko312/sstimap
Automatic SSTI detection tool with interactive interface
 sqlmapproject/sqlmap
Automatic SQL injection and database takeover tool
 hackmanit/tinja
TInjA is a CLI tool for testing web pages for template injection vulnerabilities and supports 44 of the most relevant template engines for eight…
 chaitin/safeline
Self-hosted WAF and reverse proxy that filters malicious HTTP traffic, blocks SQL injection, XSS, and bot attacks, with rate limiting and dynamic…