

wpscan
 wpscanteam/wpscan
WordPress security scanner that detects vulnerabilities, enumerates plugins/themes/users, and checks for weak passwords. Integrates with the WPScan…
crawlerdynamic-code-analysisinformation-gathering+7
9.7k
wpscanteam/wpscanWordPress security scanner that detects vulnerabilities, enumerates plugins/themes/users, and checks for weak passwords. Integrates with the WPScan…
 vladko312/sstimap
Automatic SSTI detection tool with interactive interface
 cloudflare/security-audit-skill
A coding-agent skill for multi-phase security audits with independently verified, machine-readable findings

 hahwul/dalfox
Fast XSS scanner with parameter analysis, WAF fingerprinting, and DOM/AST verification. Supports reflected, stored, and DOM-based XSS detection via…
 lifting-bits/sleigh
CMake build of Ghidra's SLEIGH processor specification library, providing standalone disassembly and p-code lifting engines for reverse engineering…
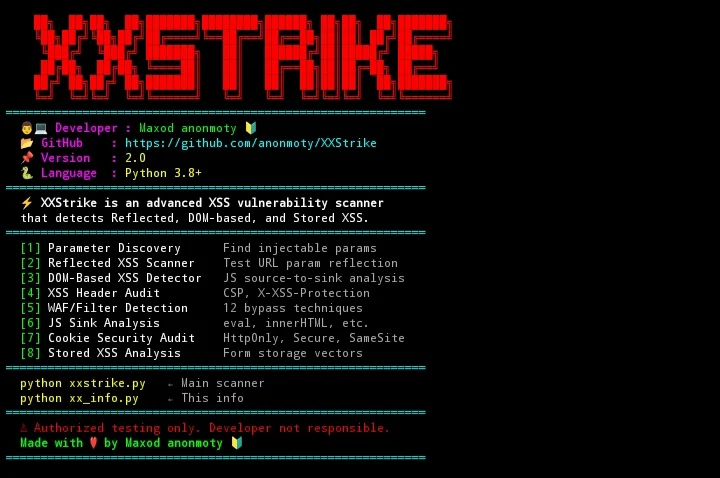 anonmoty/xxstrike
XSStrike based XSS scanner with custom features. Detects XSS vulnerabilities in web applications.
 google/oss-fuzz-gen
LLM powered fuzzing via OSS-Fuzz.
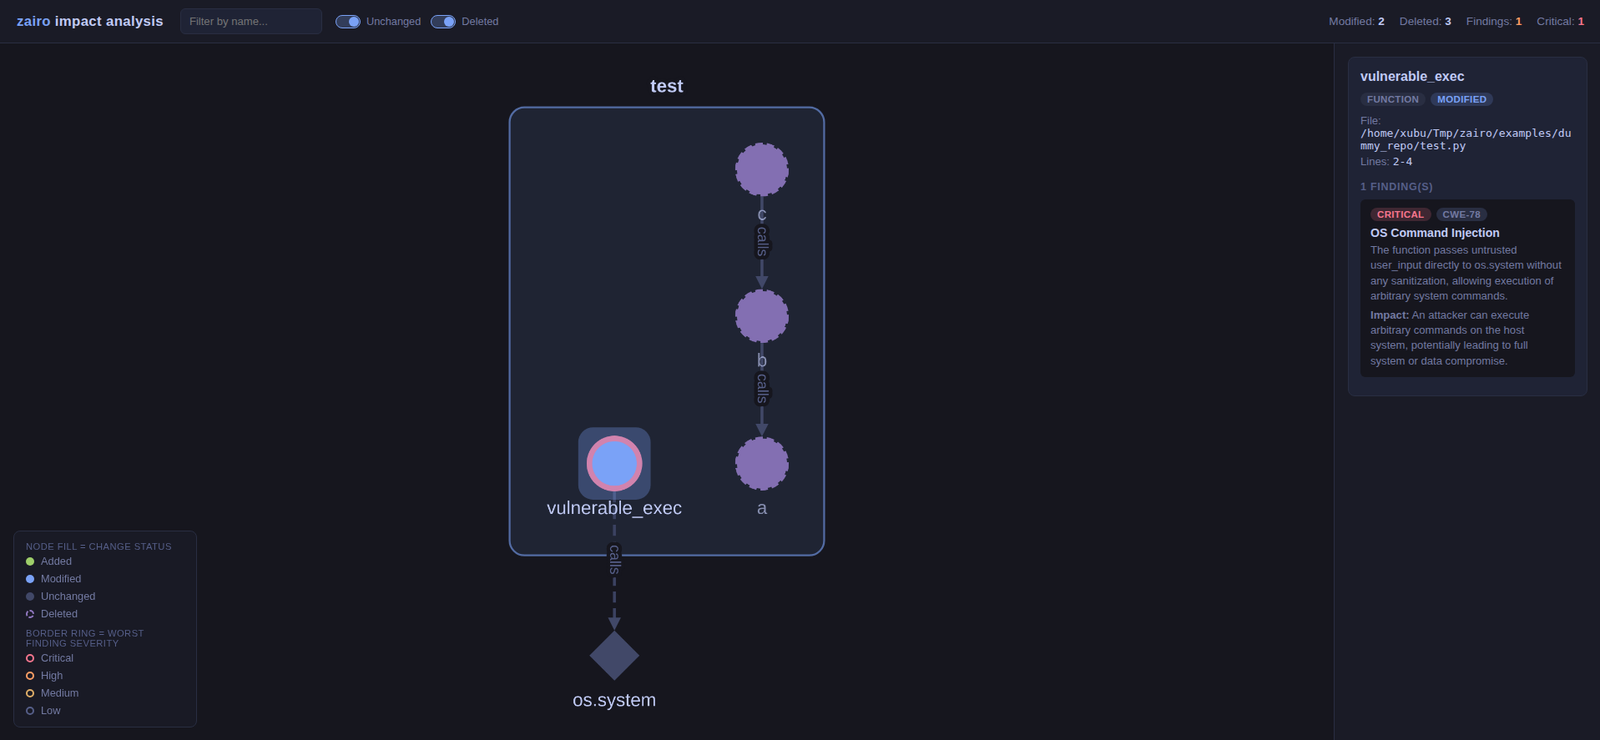 iamavu/zairo
Scans code diffs with context to build an impact graph and uses LLMs to find vulnerabilities, supporting multi-repo scans and CI gating with SARIF…
 aftermathlabs/vmp2
Unpack and deobfuscate VMProtect 2 protected binaries with an emulation-based VM explorer, handler profiler, and experimental LLVM recompiler for…
 tomnomnom/gf
A wrapper around grep, to help you grep for things
 rust-fuzz/cargo-fuzz
Cargo subcommand for coverage-guided Rust fuzzing with libFuzzer: create and run fuzz targets, minimize failures and corpora, and report coverage.
 stealthcopter/wordpress-hacking
A collection of useful resources for hacking WordPress and it's plugins and themes
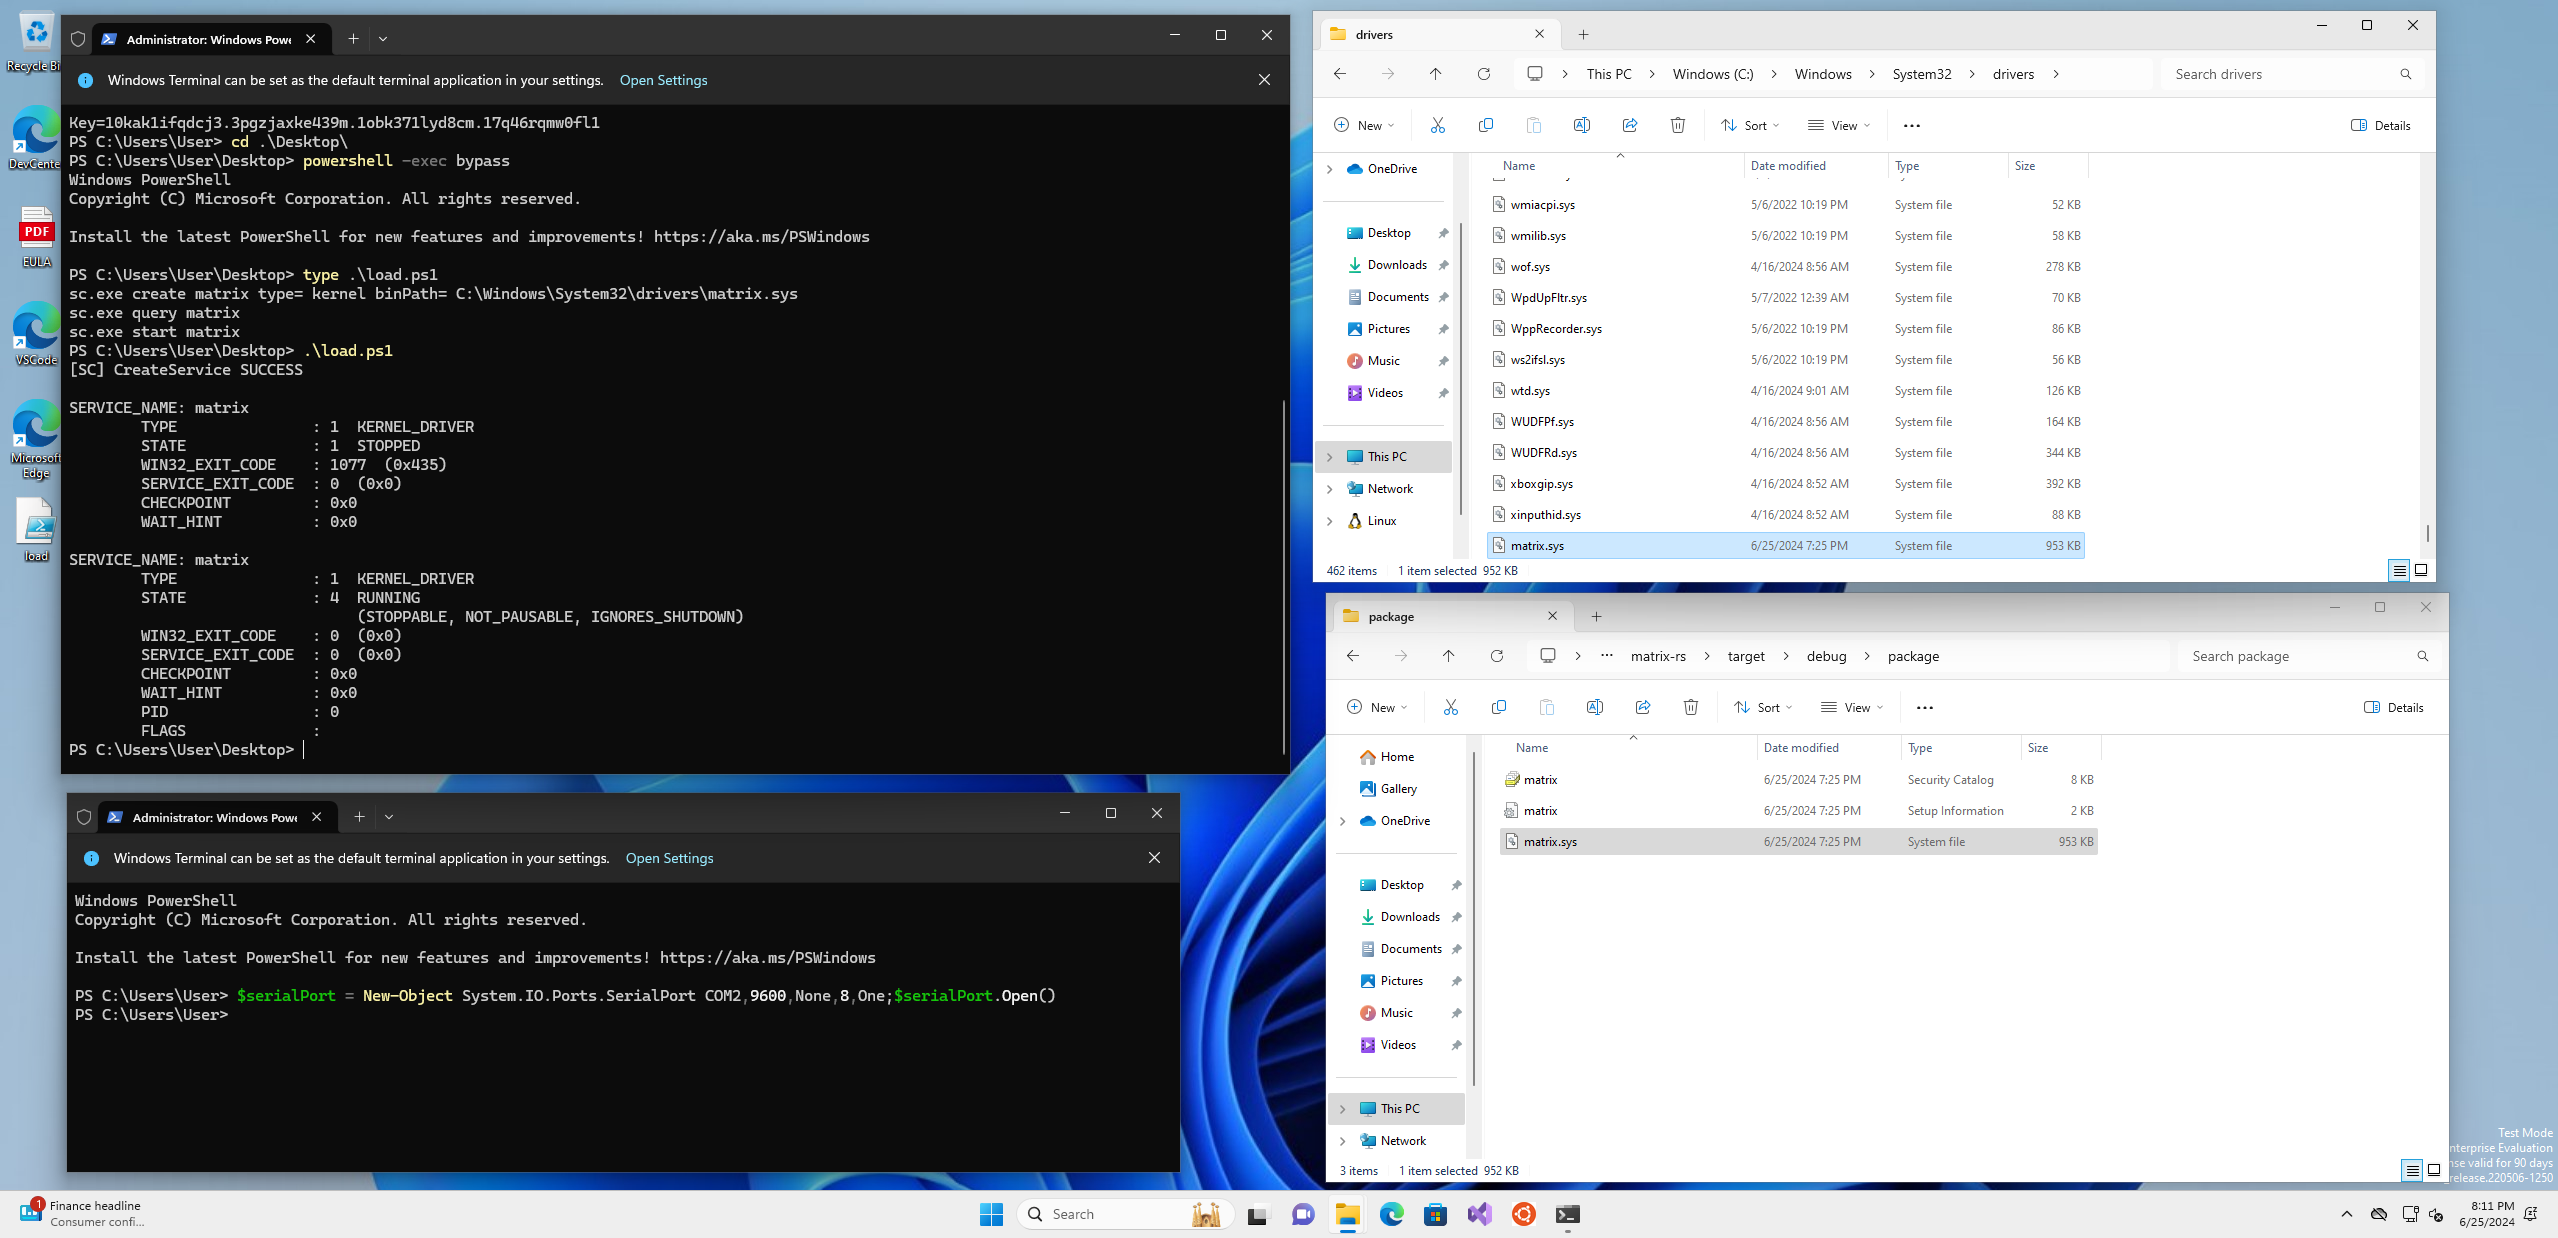 memn0ps/matrix-rs
Rusty Hypervisor - Windows Kernel Blue Pill Type-2 Hypervisor in Rust (Codename: Matrix)
 dvyukov/centipede
Distributed coverage-guided fuzzing engine compatible with libFuzzer targets; scales to thousands of concurrent jobs, uses sanitizers and corpus…
 trailofbits/umberto
Library and CLI for mutating structured data (JSON, XML, X.509) to support grammar-based fuzzing, with multiple mutation strategies and integration…
 narfindustries/http-garden
Differential testing framework for HTTP implementations
 dwisiswant0/findom-xss
A fast DOM based XSS vulnerability scanner with simplicity.