sandbox-runtime
A lightweight sandboxing tool for enforcing filesystem and network restrictions on arbitrary processes at the OS level, without requiring a container.

A lightweight sandboxing tool for enforcing filesystem and network restrictions on arbitrary processes at the OS level, without requiring a container.

Windows malware emulation framework that executes binaries, drivers, and shellcode in a modeled runtime, emulating APIs, process/thread behavior,…

FakeNet-NG - Next Generation Dynamic Network Analysis Tool

eBPF-based packet analyzer that captures network traffic with automatic process, container, and Kubernetes pod metadata annotation, supporting…

Imaginary C2 is a python tool which aims to help in the behavioral (network) analysis of malware. Imaginary C2 hosts a HTTP server which captures…

Secure multithreaded packet sniffer

Dynamic analysis sandbox for Android apps that monitors network traffic, file operations, cryptographic API usage, permission circumvention, and…

Lightweight, container-free sandbox for running commands with network and filesystem restrictions

Lightweight, cross-platform process sandboxing powered by OpenAI Codex's runtime. Sandbox any command with file, network, and credential controls.

User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…

eBPF-based toolkit for sniffing network traffic, extracting OpenSSL TLS keys, and intercepting/decrypting TLS 1.2 connections in real time using…

Standalone Windows VM malware sandbox running capemon, with GUI triage viewer, YARA signatures, IOC extraction, network analysis, and…

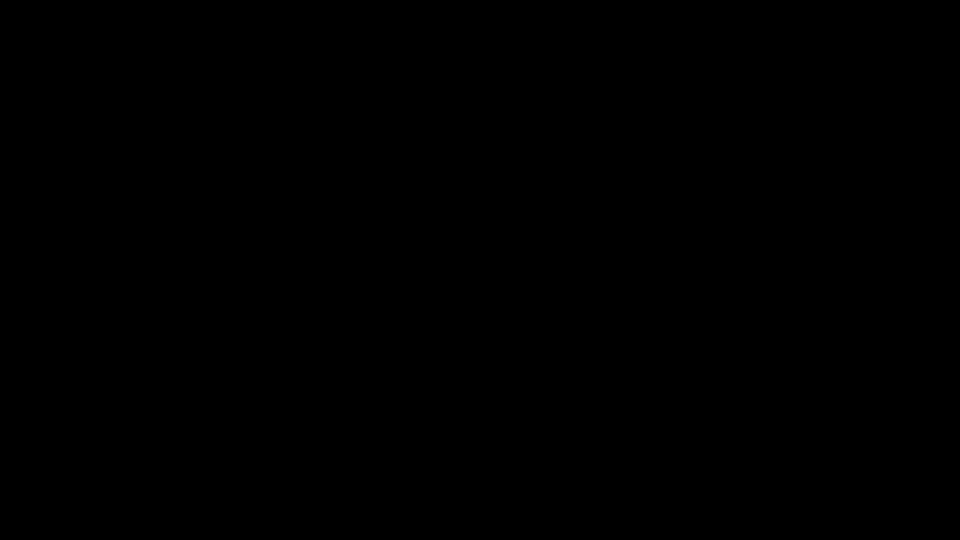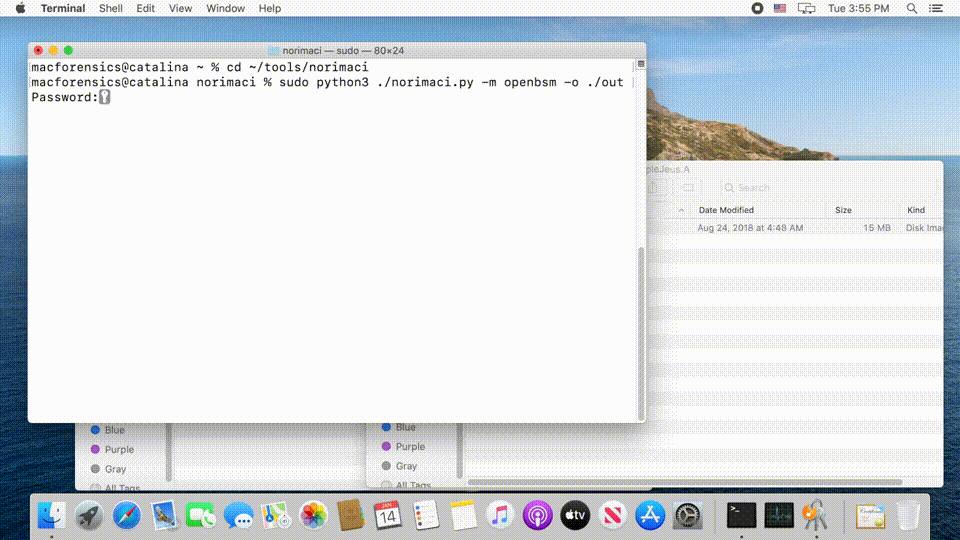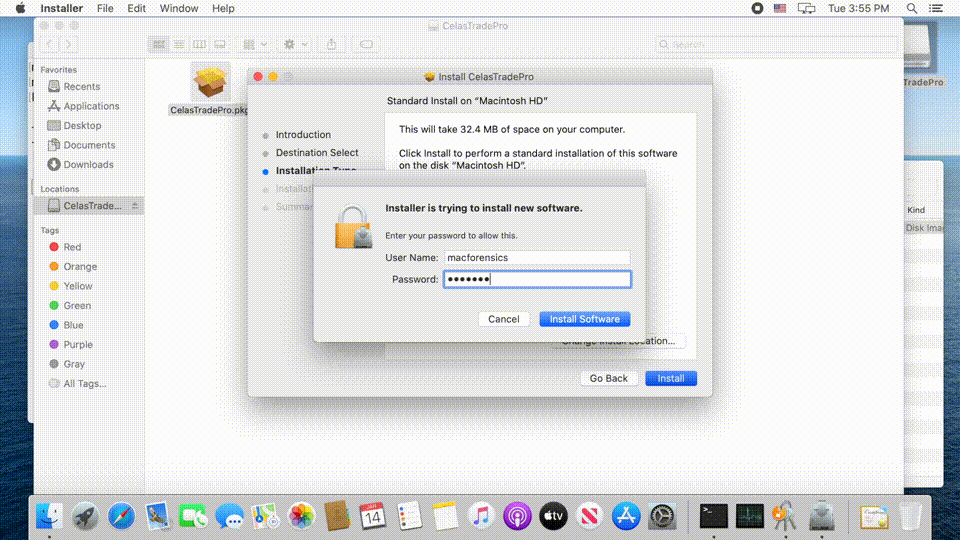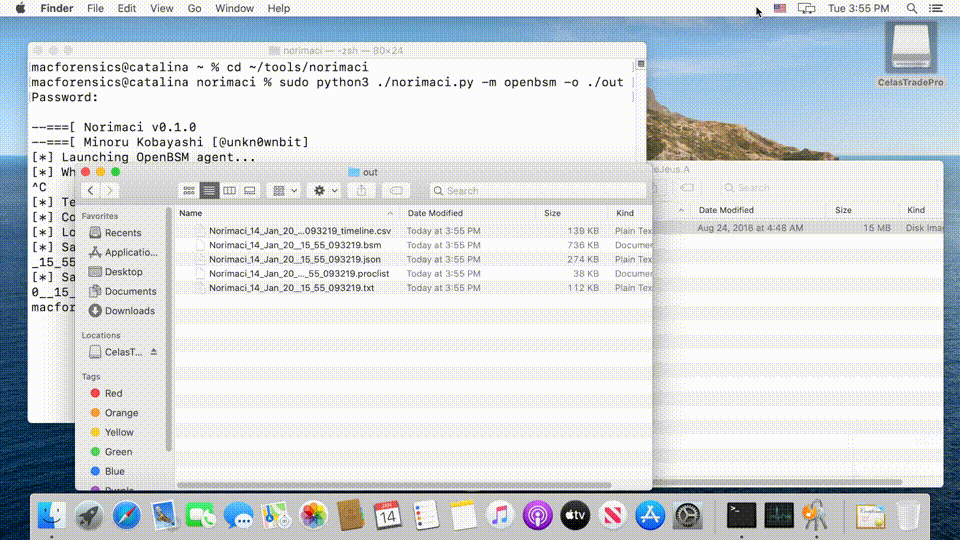
Lightweight macOS malware analysis sandbox that monitors system activity via OpenBSM or Monitor.app, generating detailed reports and timelines of…

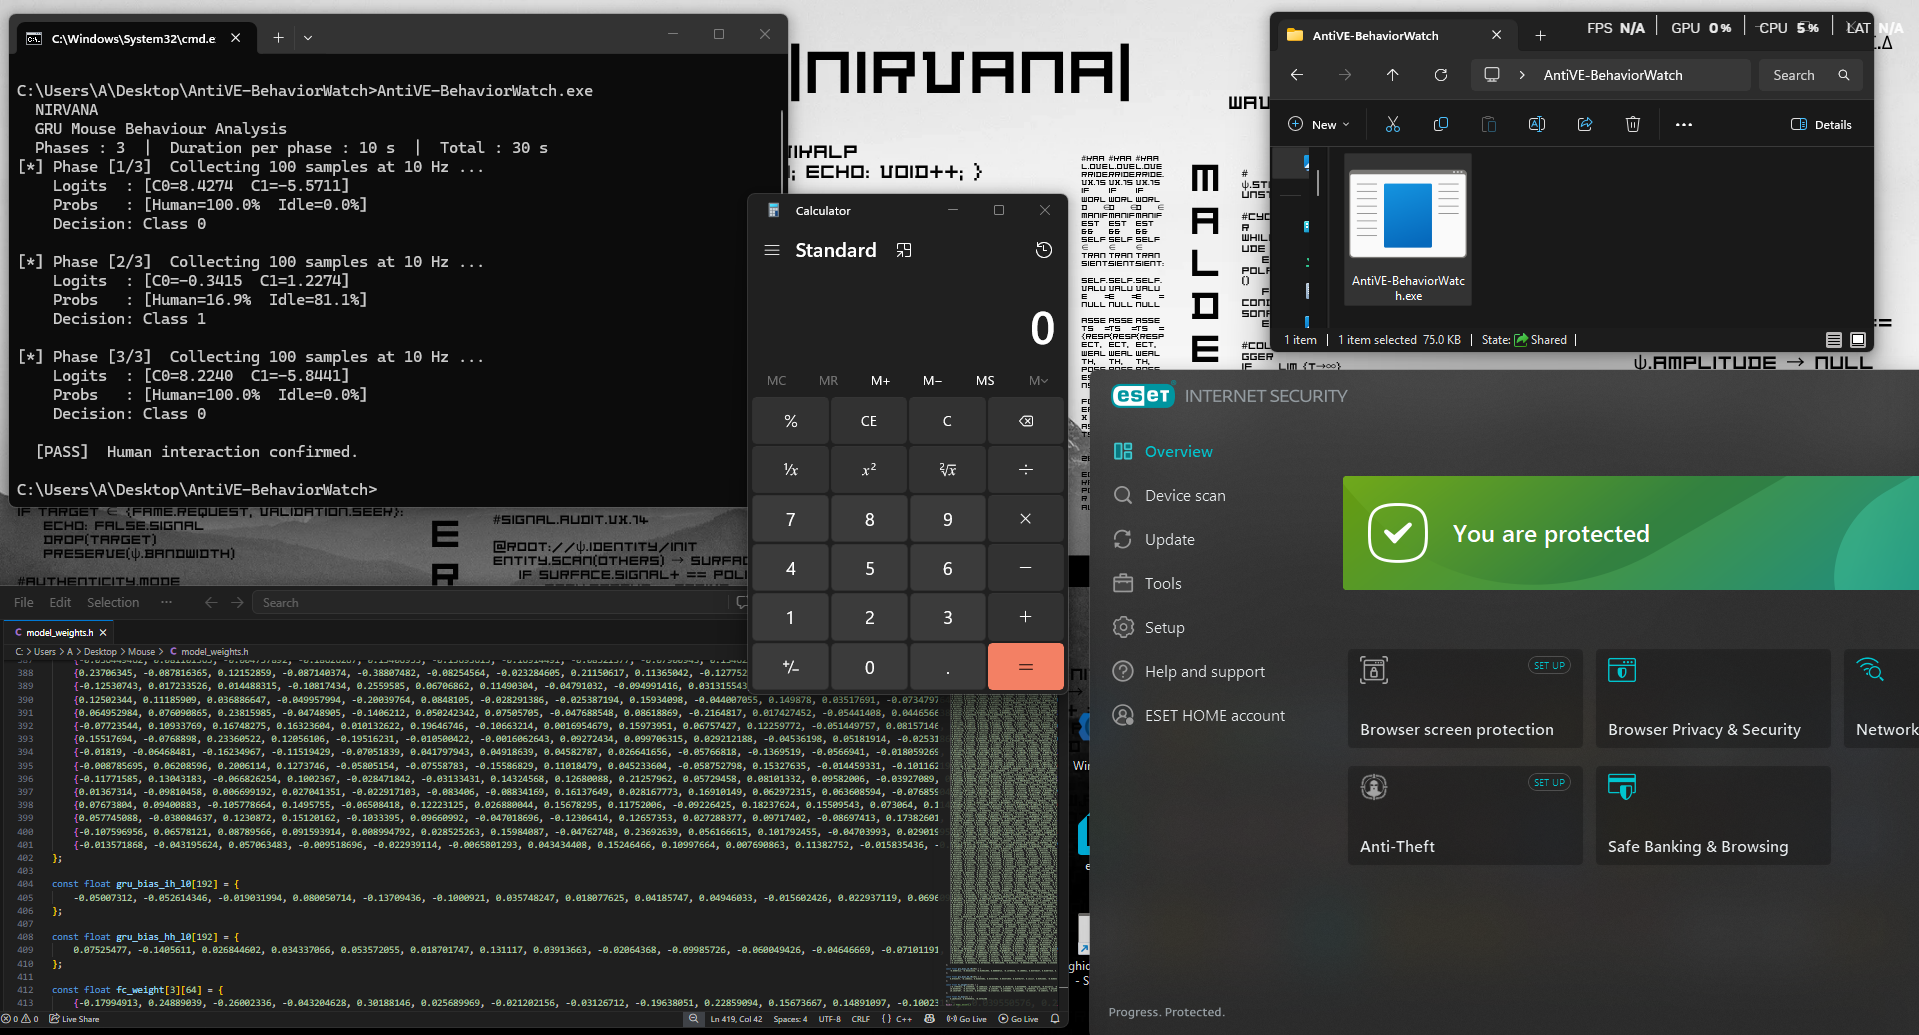
Embedded GRU neural network for real-time human behavior verification via mouse movement analysis, detecting automated analysis systems, sandboxes,…

Linux system-call monitor using ptrace to trace file, process, network, and memory activity, with namespace isolation and machine learning…

ltm is a machine-history debugger for Linux. It records process, file, network, memory, and block-I/O metadata via eBPF, then lets you query the…

A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…

Local-first macOS research browser built on a custom Brave build that captures network traffic, fingerprints, scripts, and runtime evidence for…