
antidbg
 notrequiem/antidbg
A stealthy, fully syscalled C/C++ userland anti-debugging library for Windows, designed to protect software from reverse engineering
anti-botbinary-analysisdefensive-tools+4
333
notrequiem/antidbgA stealthy, fully syscalled C/C++ userland anti-debugging library for Windows, designed to protect software from reverse engineering
 mandiant/flare-vm
A collection of software installations scripts for Windows systems that allows you to easily setup and maintain a reverse engineering environment on…
 mxmssh/drltrace
Drltrace is a library calls tracer for Windows and Linux applications.
 yarox24/attack_monitor
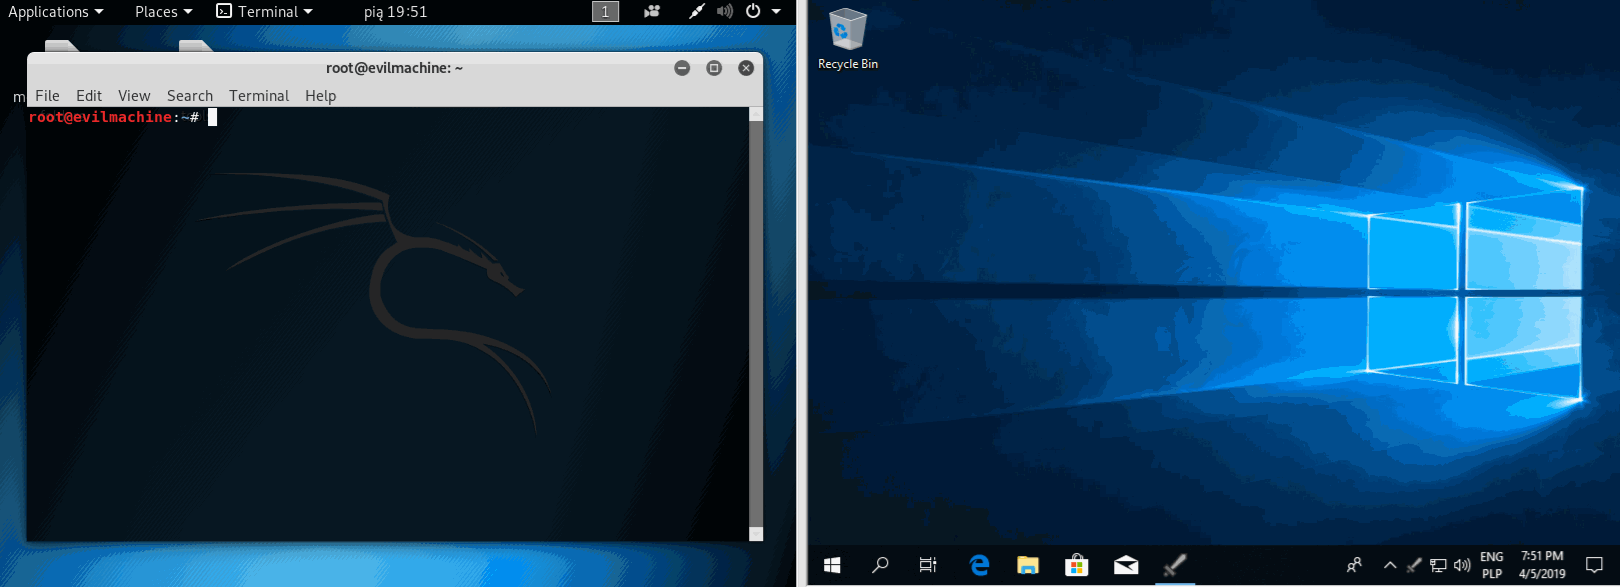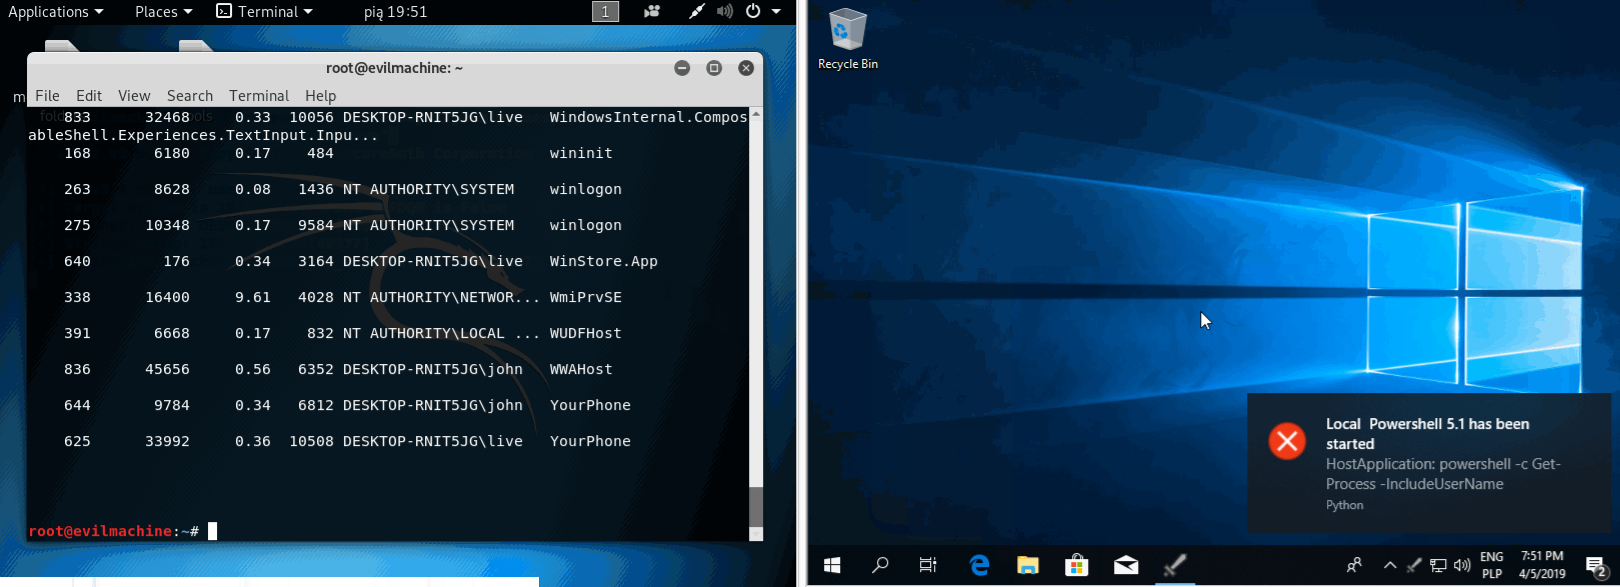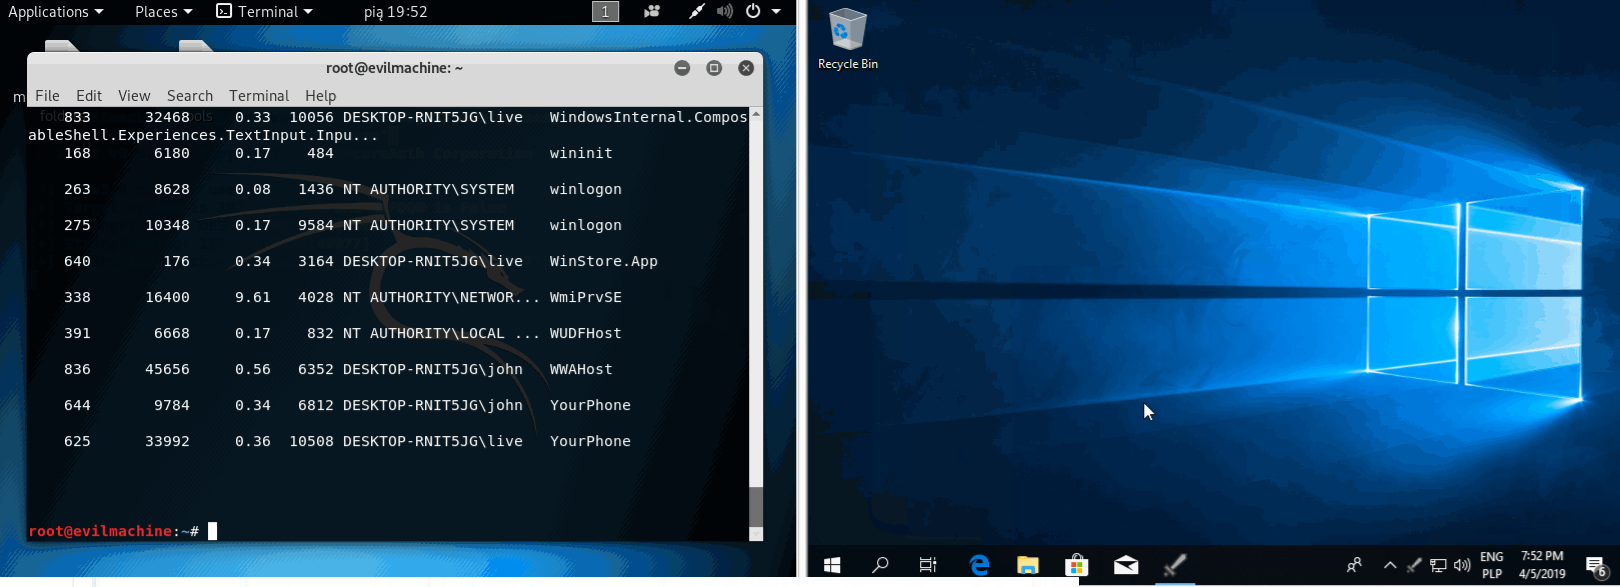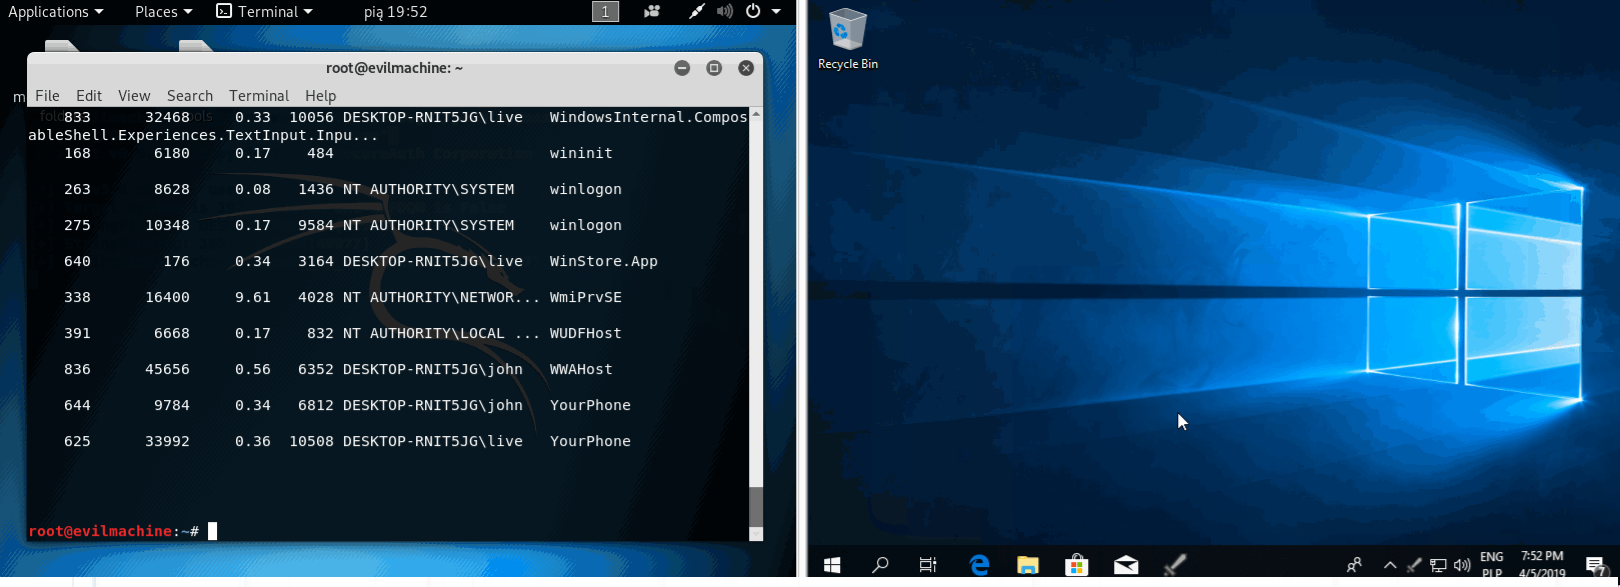
Endpoint detection & Malware analysis software
 microsoft/onefuzz
A self-hosted Fuzzing-As-A-Service platform
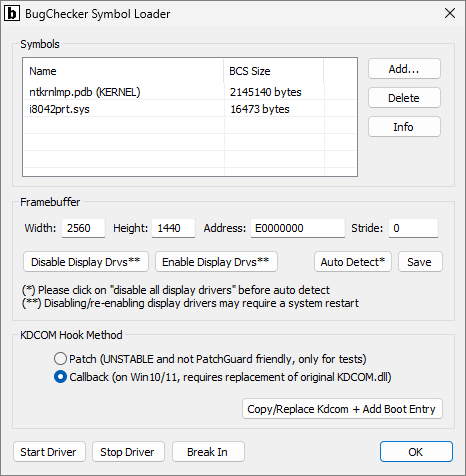 vitoplantamura/bugchecker
SoftICE-like kernel debugger for Windows 11
 googleprojectzero/sandbox-attacksurface-analysis-tools
Set of tools to analyze Windows sandboxes for exposed attack surface.
 cyb3rmx/qu1cksc0pe
All-in-One malware analysis tool.
 last-emo-boy/rikune
MCP server for reverse engineering Windows executables and binary formats. Combines static triage, Ghidra-assisted function recovery, plugin-driven…
 nccgroup/psr
Pointer Sequence Reverser - enable you to see how Windows C++ application is accessing a particular data member or object.
 mandiant/flare-qdb
Command-line and Python debugger for instrumenting and modifying native software behavior on Windows and Linux.
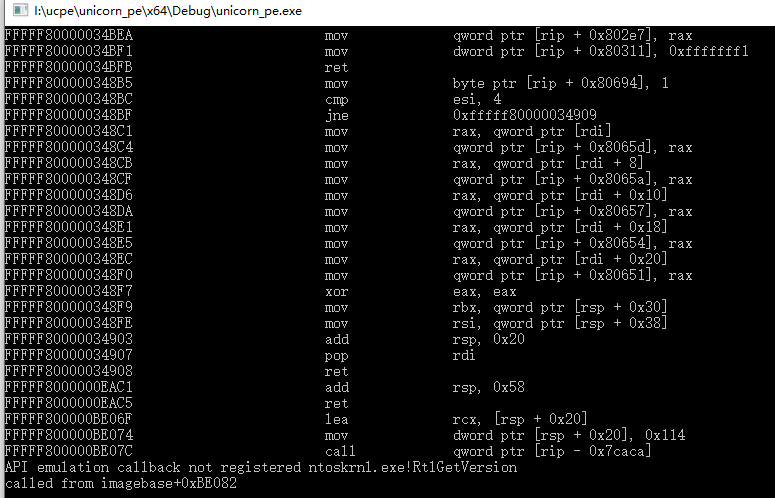 hzqst/unicorn_pe
Emulates Windows PE execution using Unicorn engine for malware analysis, unpacking packed binaries, and decrypting VMProtect strings and imports.
 mandiant/flare-ida
IDA Pro utilities from FLARE team
 akatorich/kernelflirt
Windows kernel-level debugger with OllyDbg/IDA-style UI, software and hardware breakpoints, PDB symbols, decompiler, and 17 plugins for reverse…
 zeze-zeze/ioctlance
A tool that is used to hunt vulnerabilities in x64 WDM drivers
 corelight/zeek-xor-exe-plugin
Zeek plugin to detect and decrypt XOR-encrypted EXEs
 d4rksystem/vmwarecloak
A PowerShell script that attempts to help malware analysts hide their VMware Windows VM's from malware that may be trying to evade analysis.
 lloydlabs/wsb-detect
wsb-detect enables you to detect if you are running in Windows Sandbox ("WSB")